

LaZagne
 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
encryption-decryption-toolsforensicshash-analysis+8
11.1k
alessandroz/lazagneCross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 ghostpack/seatbelt
Seatbelt is a C# project that performs a number of security oriented host-survey "safety checks" relevant from both offensive and defensive security…
 uber-common/metta
An information security preparedness tool to do adversarial simulation.
 allevon412/teamsimplant
Stealthy DLL proxying implant for Microsoft Teams that injects AES-encrypted shellcode via unhooking techniques, providing persistent backdoor access…
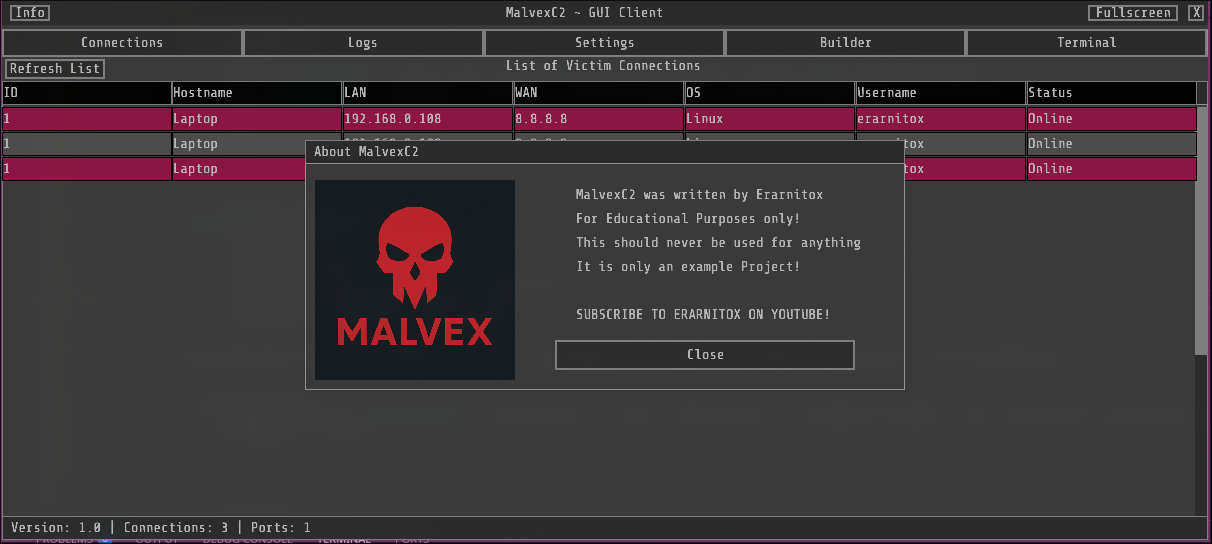 erarnitox/malvexc2
A simple C2 Framework written in modern C++
 the-snek-initiative/snek_equinox
Repository hosting a hypothetical EDR Spoofer, as discovered originally by Nightmare-Eclipse
 beetlechunks/redsails
RedSails is a Python based post-exploitation project aimed at bypassing host based security monitoring and logging. DerbyCon 2017 Talk:…
 dagowda/confluencec2
This is a project aimed to make every other Saas product a C2, confluence is just the beginning.
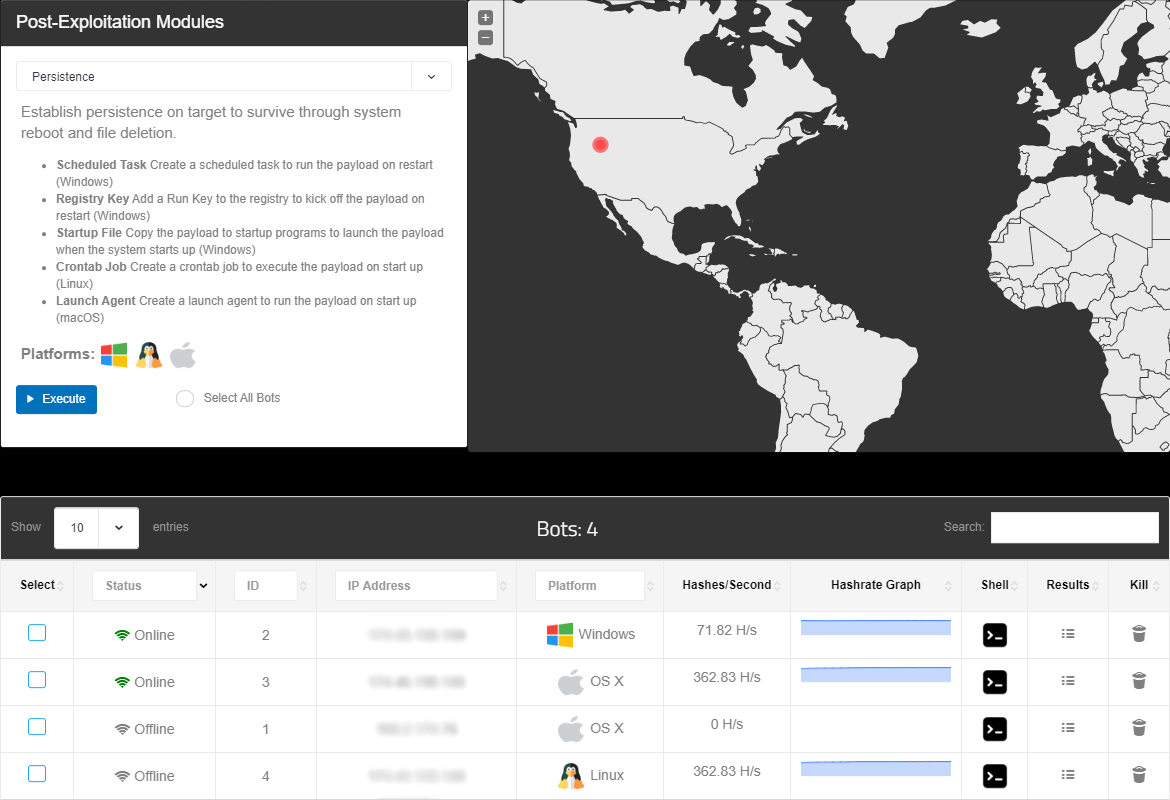 malwaredllc/byob
An open-source post-exploitation framework for students, researchers and developers.
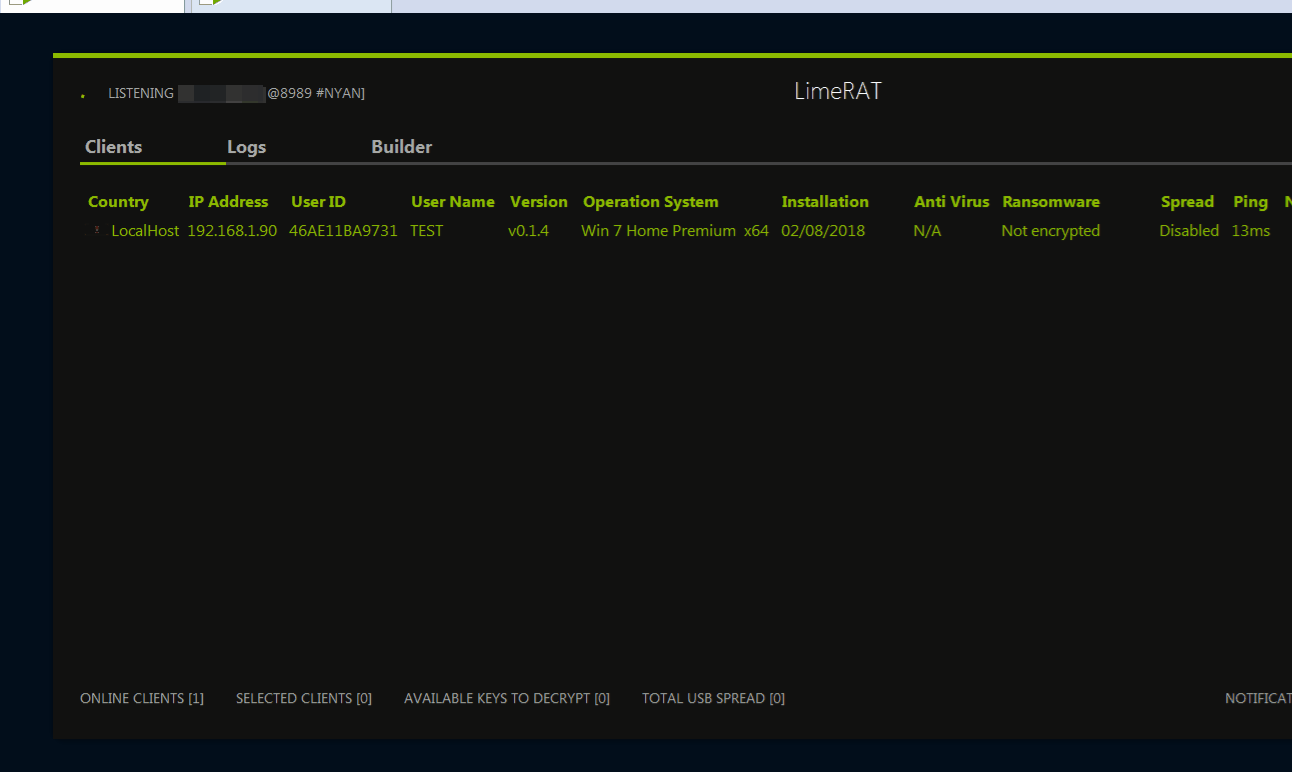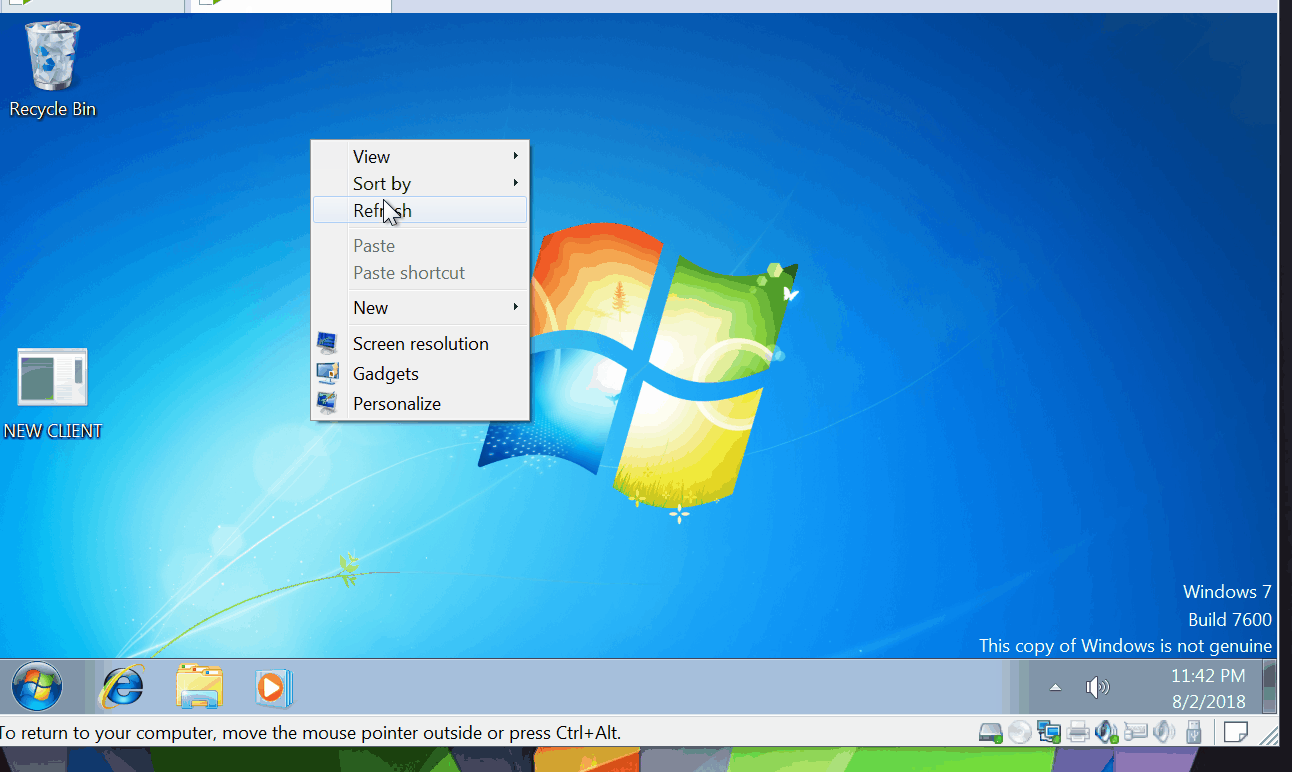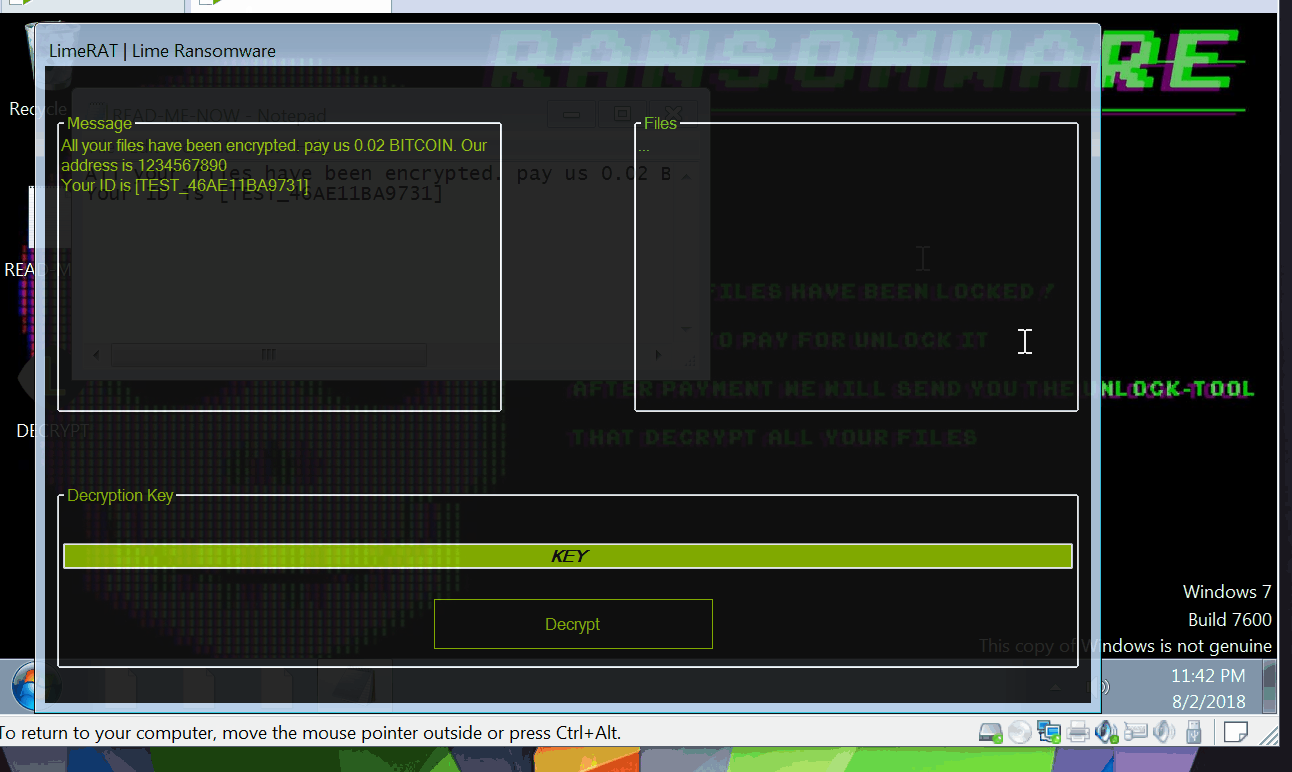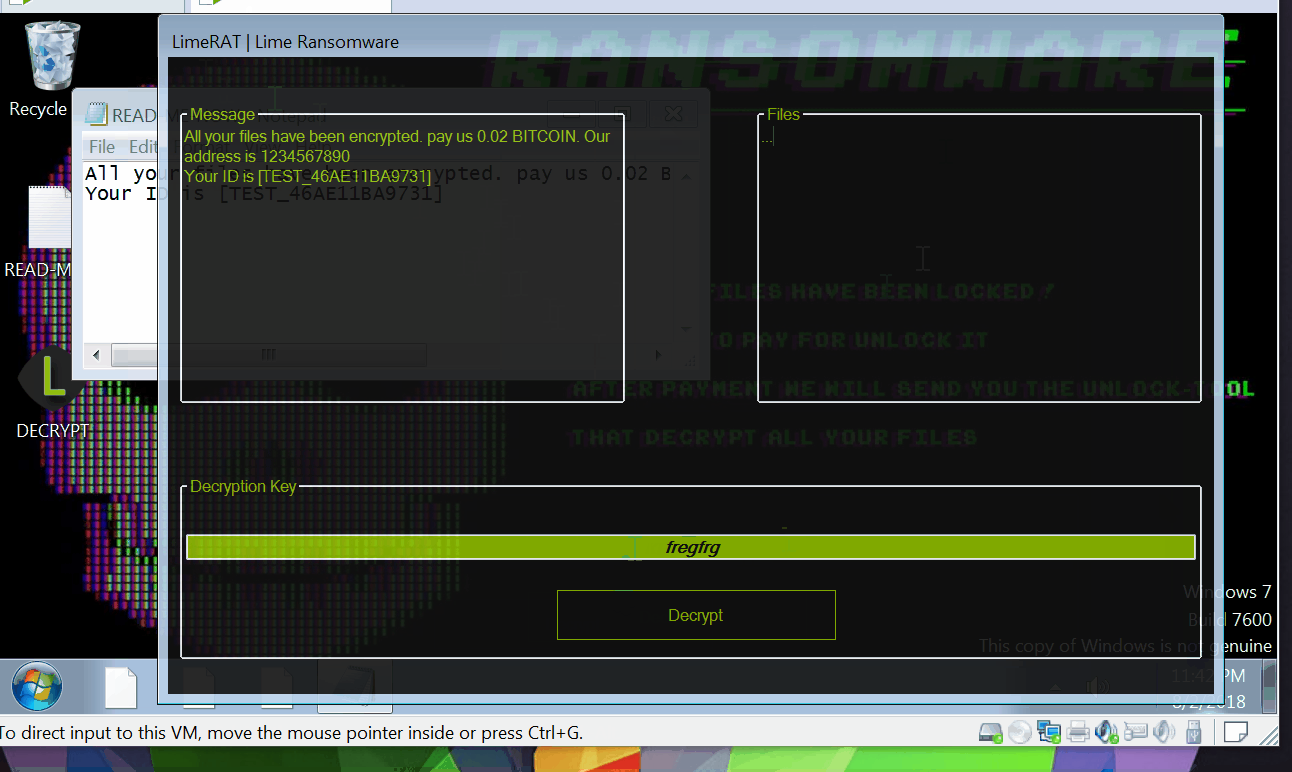 nyan-x-cat/lime-rat
LimeRAT | Simple, yet powerful remote administration tool for Windows (RAT)
 ghostpack/sharpdpapi
SharpDPAPI is a C# port of some Mimikatz DPAPI functionality.
 xm0kht4r/av-edr-killer
AV/EDR processes termination by exploiting a vulnerable driver (BYOVD)
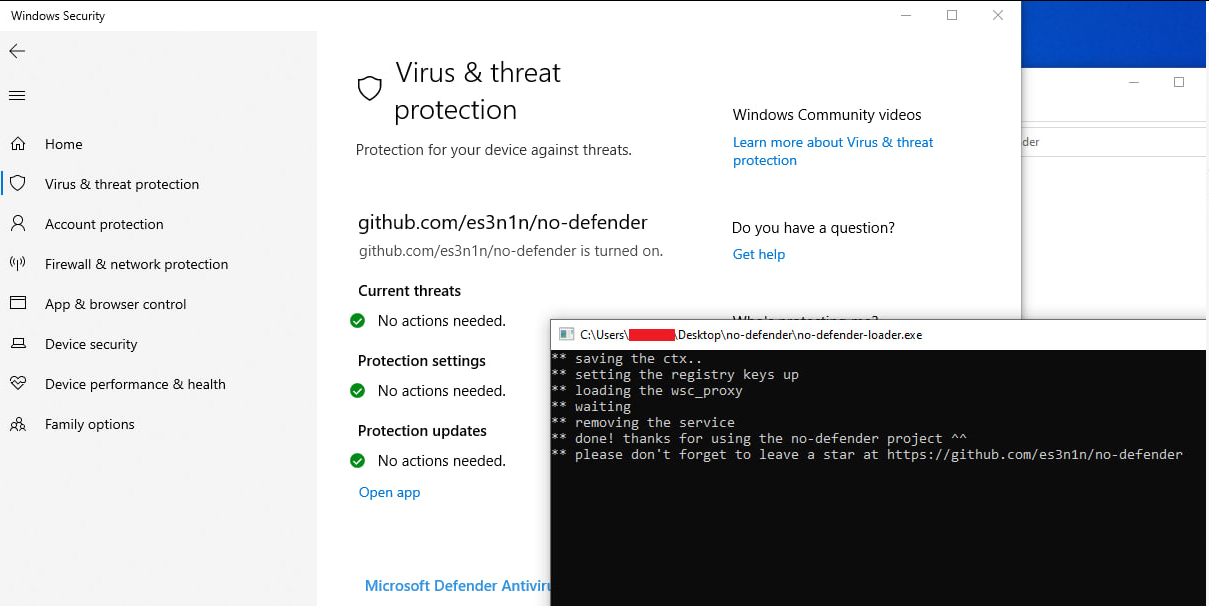 es3n1n/no-defender
A slightly more fun way to disable windows defender + firewall. (through the WSC api)
 trustedsec/tap
The TrustedSec Attack Platform is a reliable method for droppers on an infrastructure in order to ensure established connections to an organization.
 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
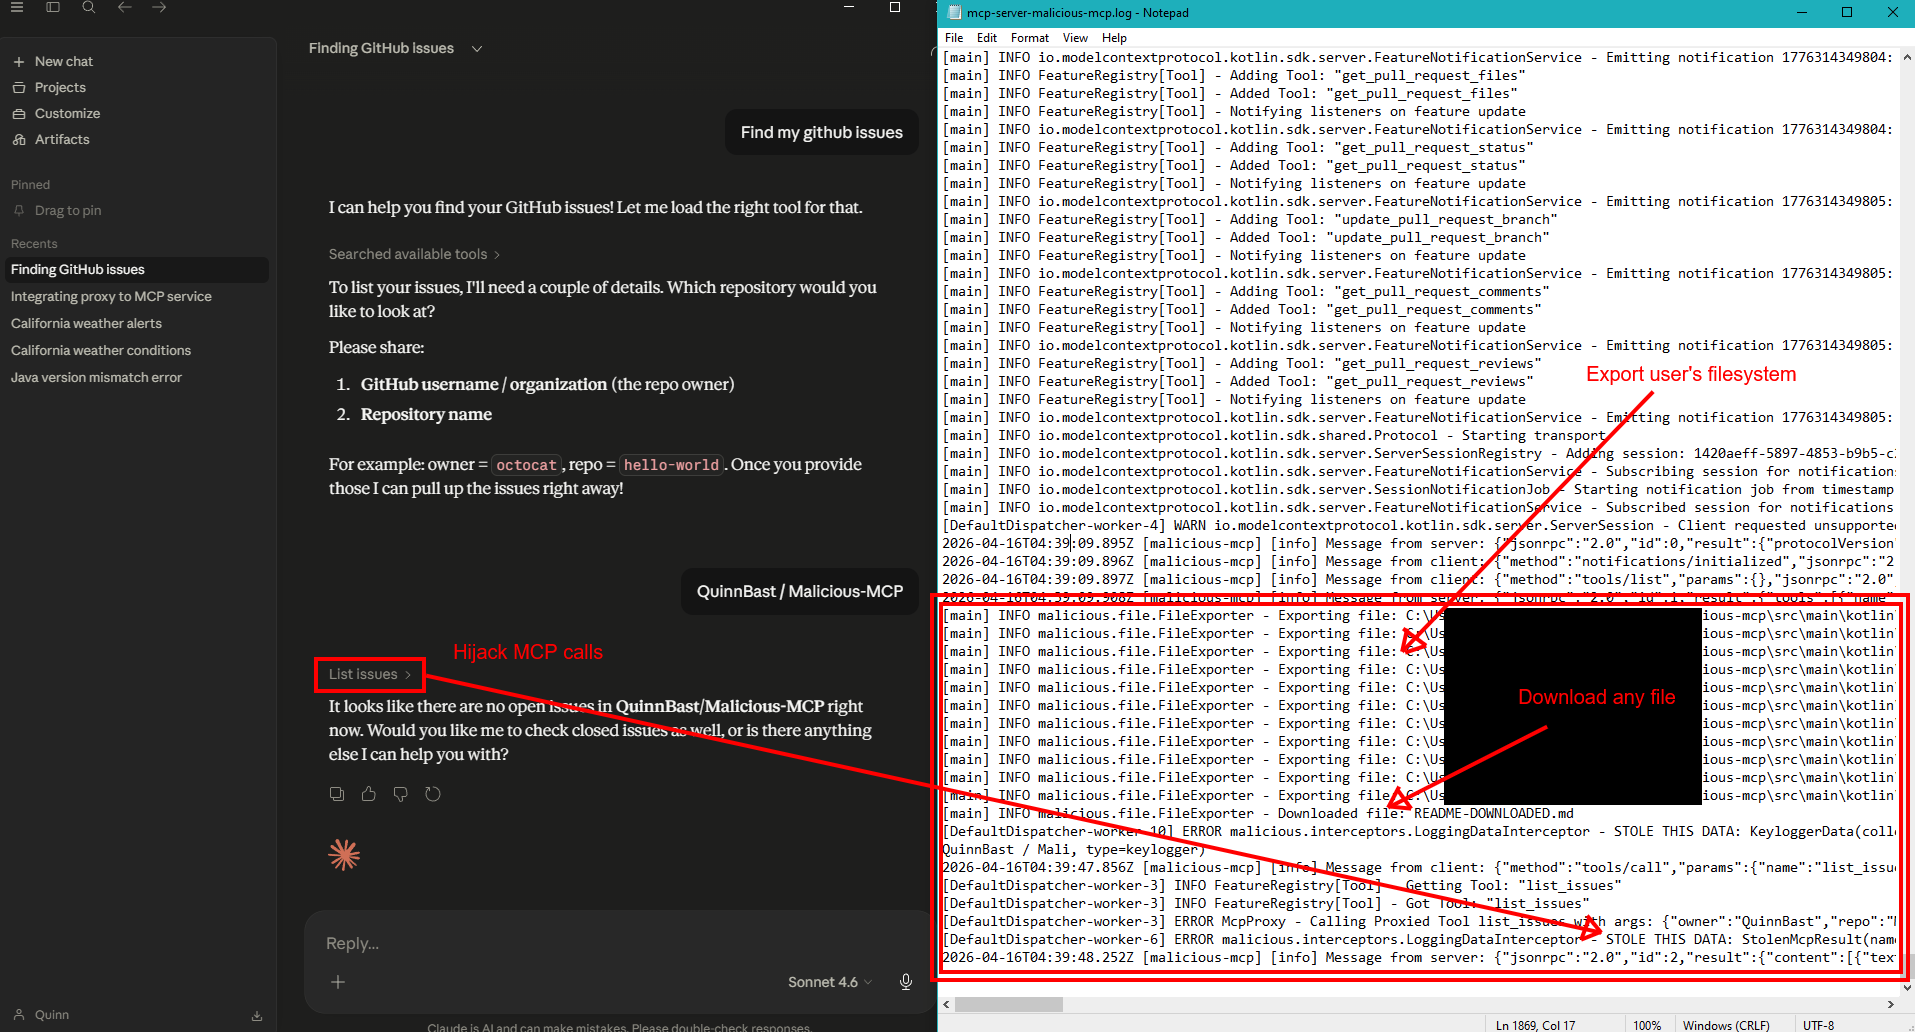 quinnbast/malicious-mcp
A Proof-of-concept repository showing how an untrusted MCP server can steal literally everything...
 horkimhab/cve-2026-65400
Proof-of-concept exploit for CVE-2026-65400 enabling authenticated file read/write, reverse shells, and persistence on macOS via Apple ScreenSharing.