
WinPwn
 s3cur3th1ssh1t/winpwn
Automation for internal Windows Penetrationtest / AD-Security
exploitationpenetration-testingpenetration-testing-frameworks+4
3.7k1 year ago
s3cur3th1ssh1t/winpwnAutomation for internal Windows Penetrationtest / AD-Security
 harleyqu1nn/aggressorscripts
Collection of Aggressor scripts for Cobalt Strike 3.0+ pulled from multiple sources
 sofianehamlaoui/lockdoor-framework
🔐 Lockdoor Framework : A Penetration Testing framework with Cyber Security Resources
 ahmedkhlief/ninja
Open source C2 server created for stealth red team operations
 bahaabdelwahed/killshot
A Penetration Testing Framework, Information gathering tool & Website Vulnerability Scanner
 cube0x0/sharpmapexec
Windows-native penetration testing swiss army knife for lateral movement, credential access, data exfiltration, and vulnerability scanning across…
 r-s0n/ars0n-framework
Modular bug bounty hunting framework automating reconnaissance, subdomain enumeration, and vulnerability scanning with an educational focus to help…
 jack-new-project/zeebsploit
Modular exploitation framework for penetration testing, featuring automated payload generation, reconnaissance modules, and post-exploitation…
 catsploit/catsploit
Automated penetration testing tool using Cyber Attack Techniques Scoring (CATS) to select and execute optimal attack scenarios via Metasploit, Nmap,…
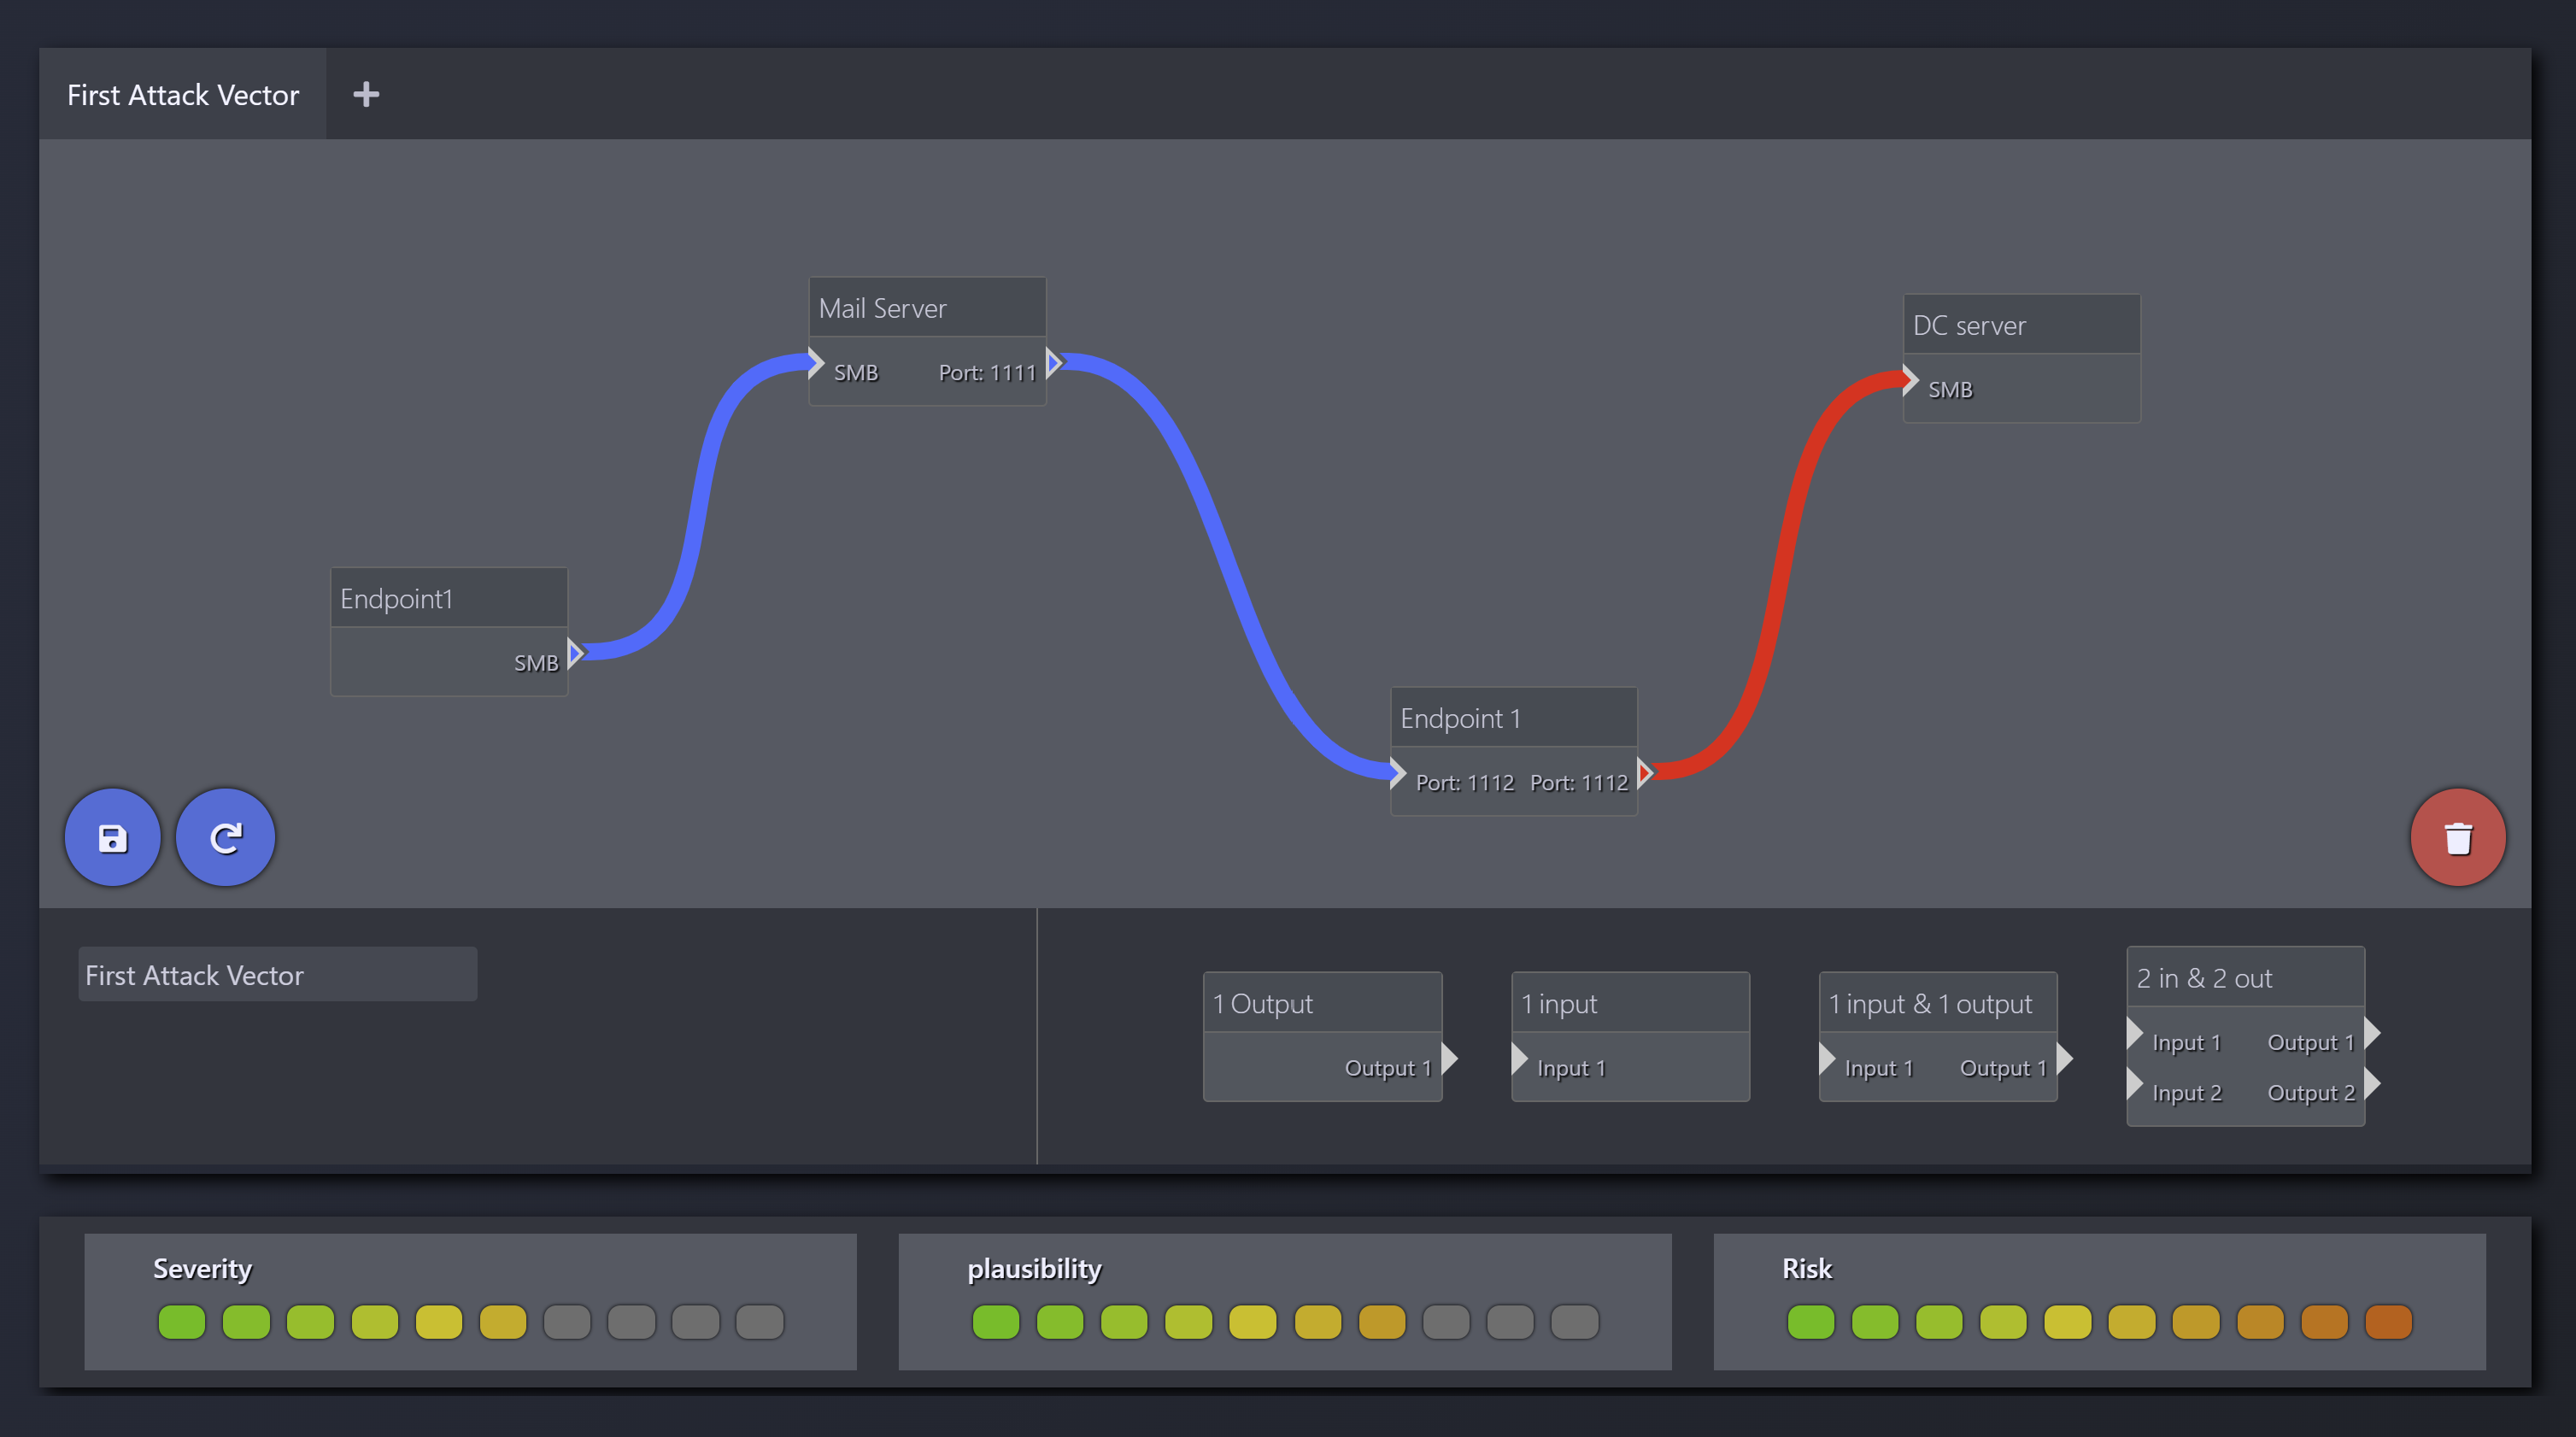 redeye-framework/redeye
Collaborative pentest data management platform for organizing servers, users, vulnerabilities, attack vectors, and files with API access and graph…
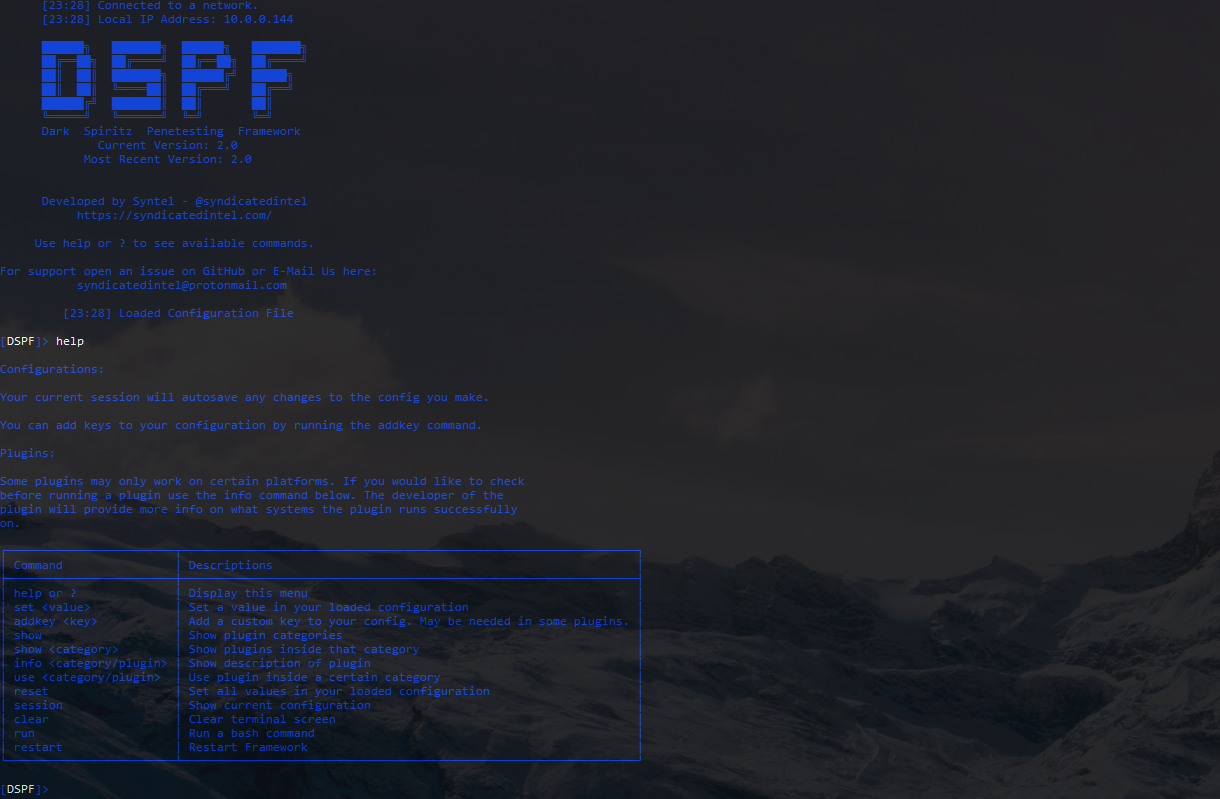 m4cs/darkspiritz
🌔 Official Repository for DarkSpiritz Penetration Framework | Written in Python 🐍
 crossc2/crossc2kit
CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…
 strategic-automation/violin
Agentic pentest profile for Hermes: 31 playbooks for authorised recon, web/access-control attacks, safe exploit validation, and evidence-driven…
 nvisosecurity/pycobalthound
pyCobaltHound is an Aggressor script extension for Cobalt Strike which aims to provide a deep integration between Cobalt Strike and Bloodhound.
 josue87/boomer
Framework for exploiting local vulnerabilities
 chopicalqui/kaliintelligencesuite
Automated intelligence-gathering framework that orchestrates Kali Linux tools and public APIs to collect, store, and analyze reconnaissance data for…
 elevenpaths/siemframework
Modular Python3 attack framework for automating exploitation of SIEM platforms (Splunk, Graylog, OSSIM, QRadar, McAfee) via credential theft, payload…
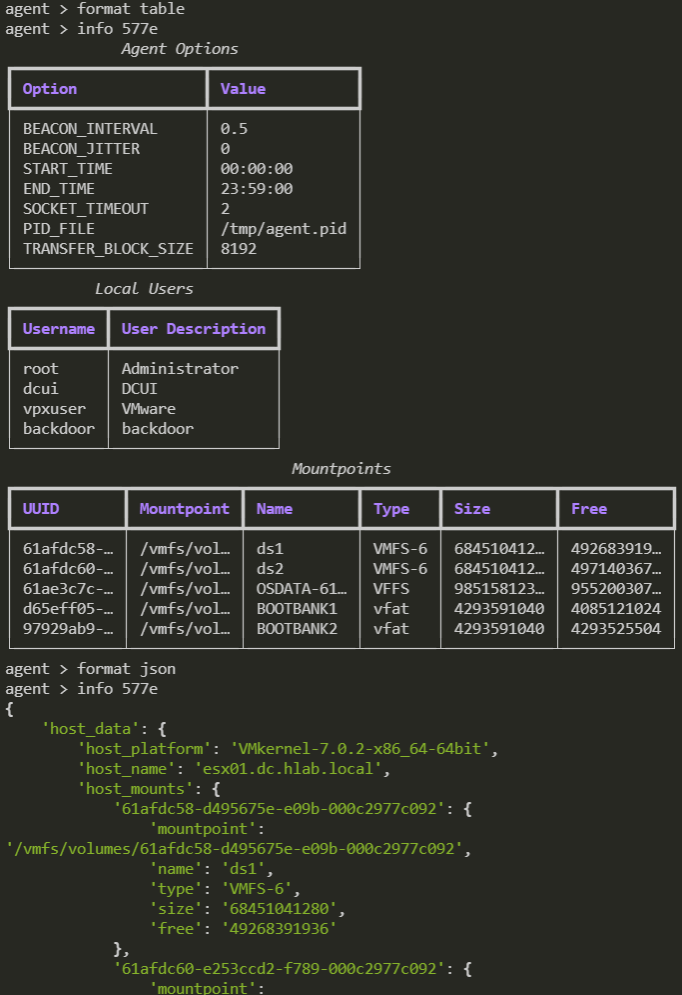 psmths/reave
WIP Post-exploitation framework tailored for hypervisors.