
powerview.py
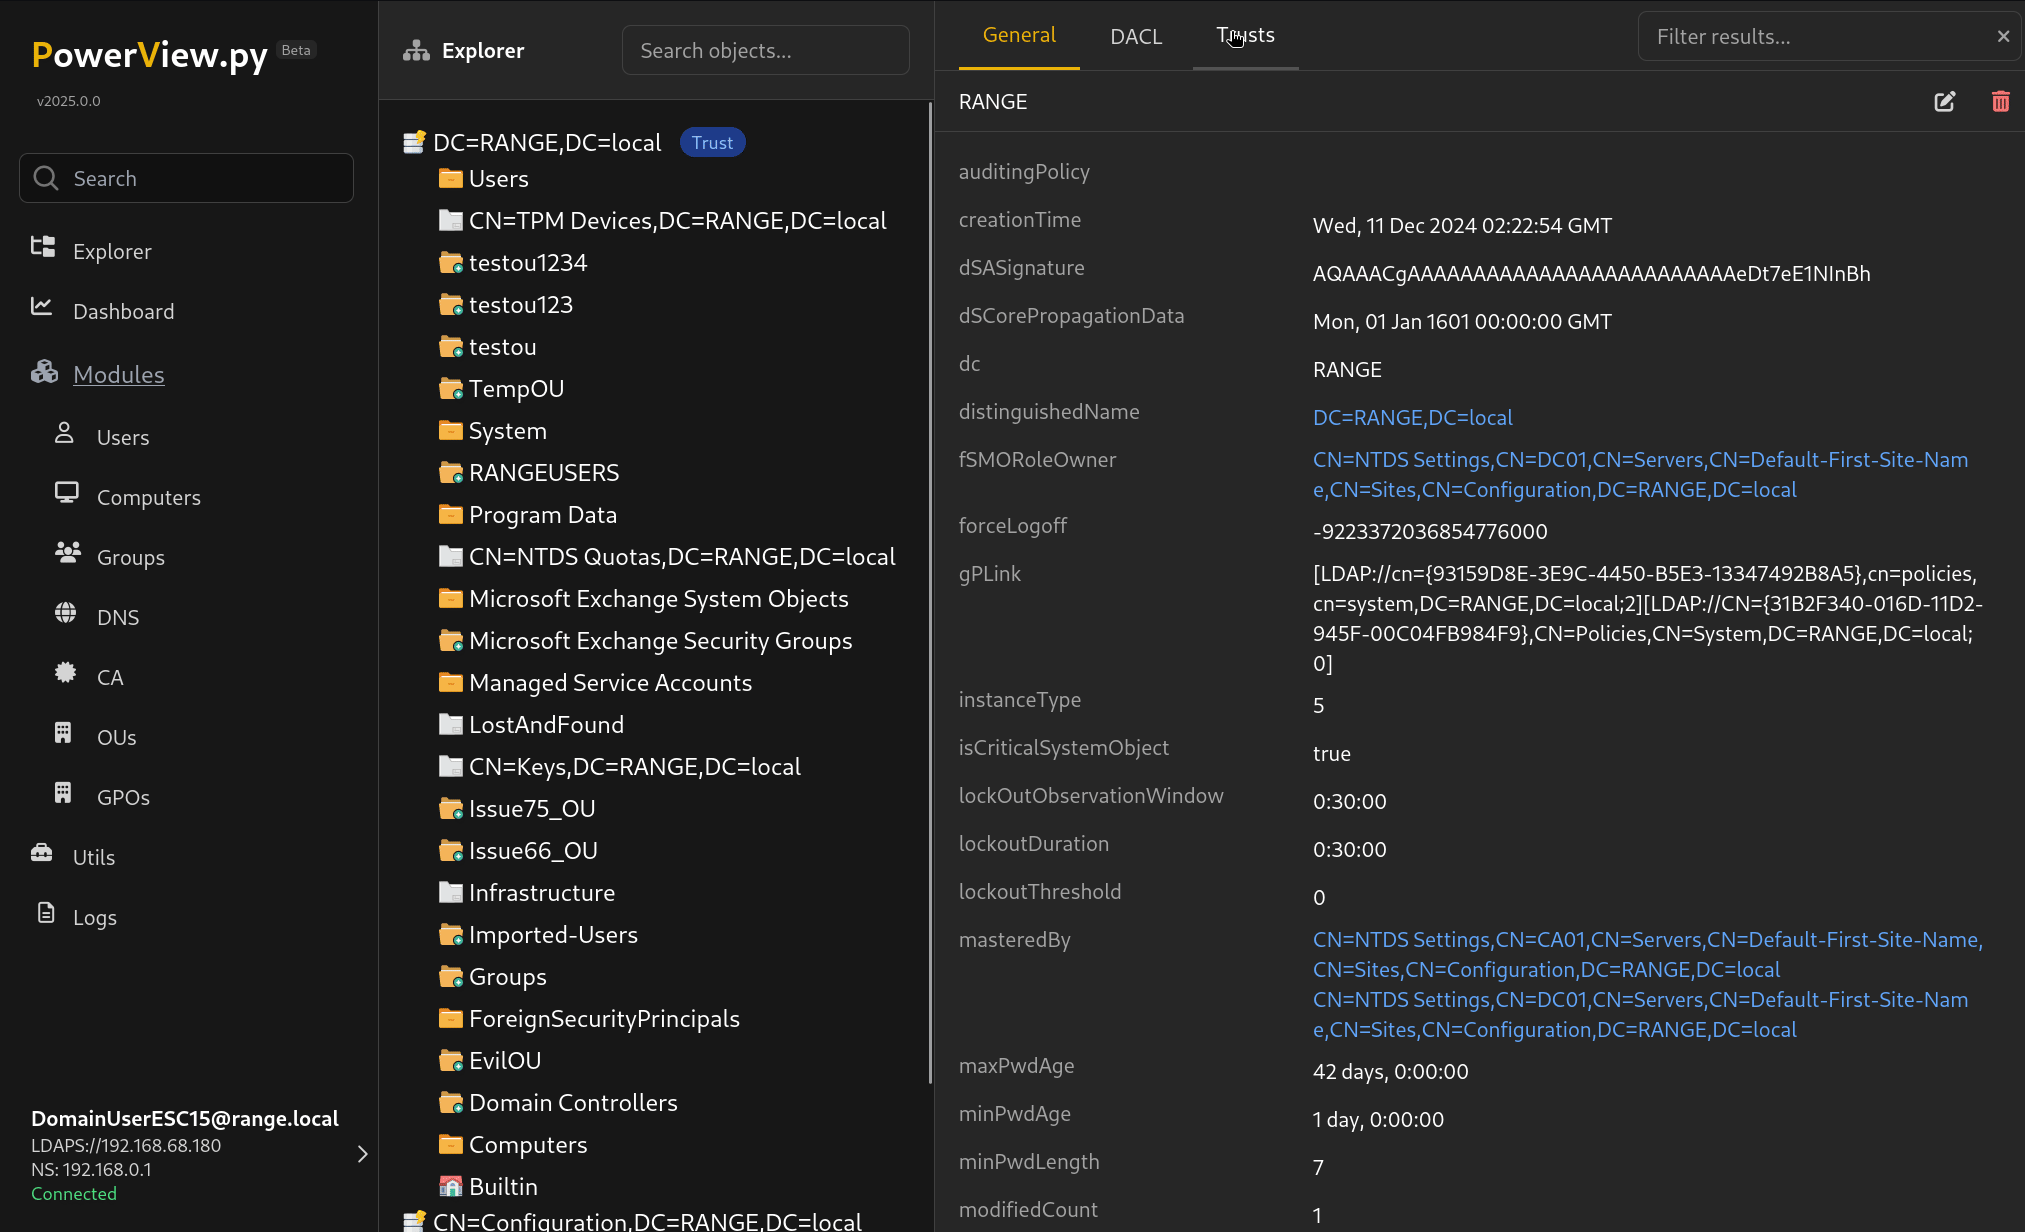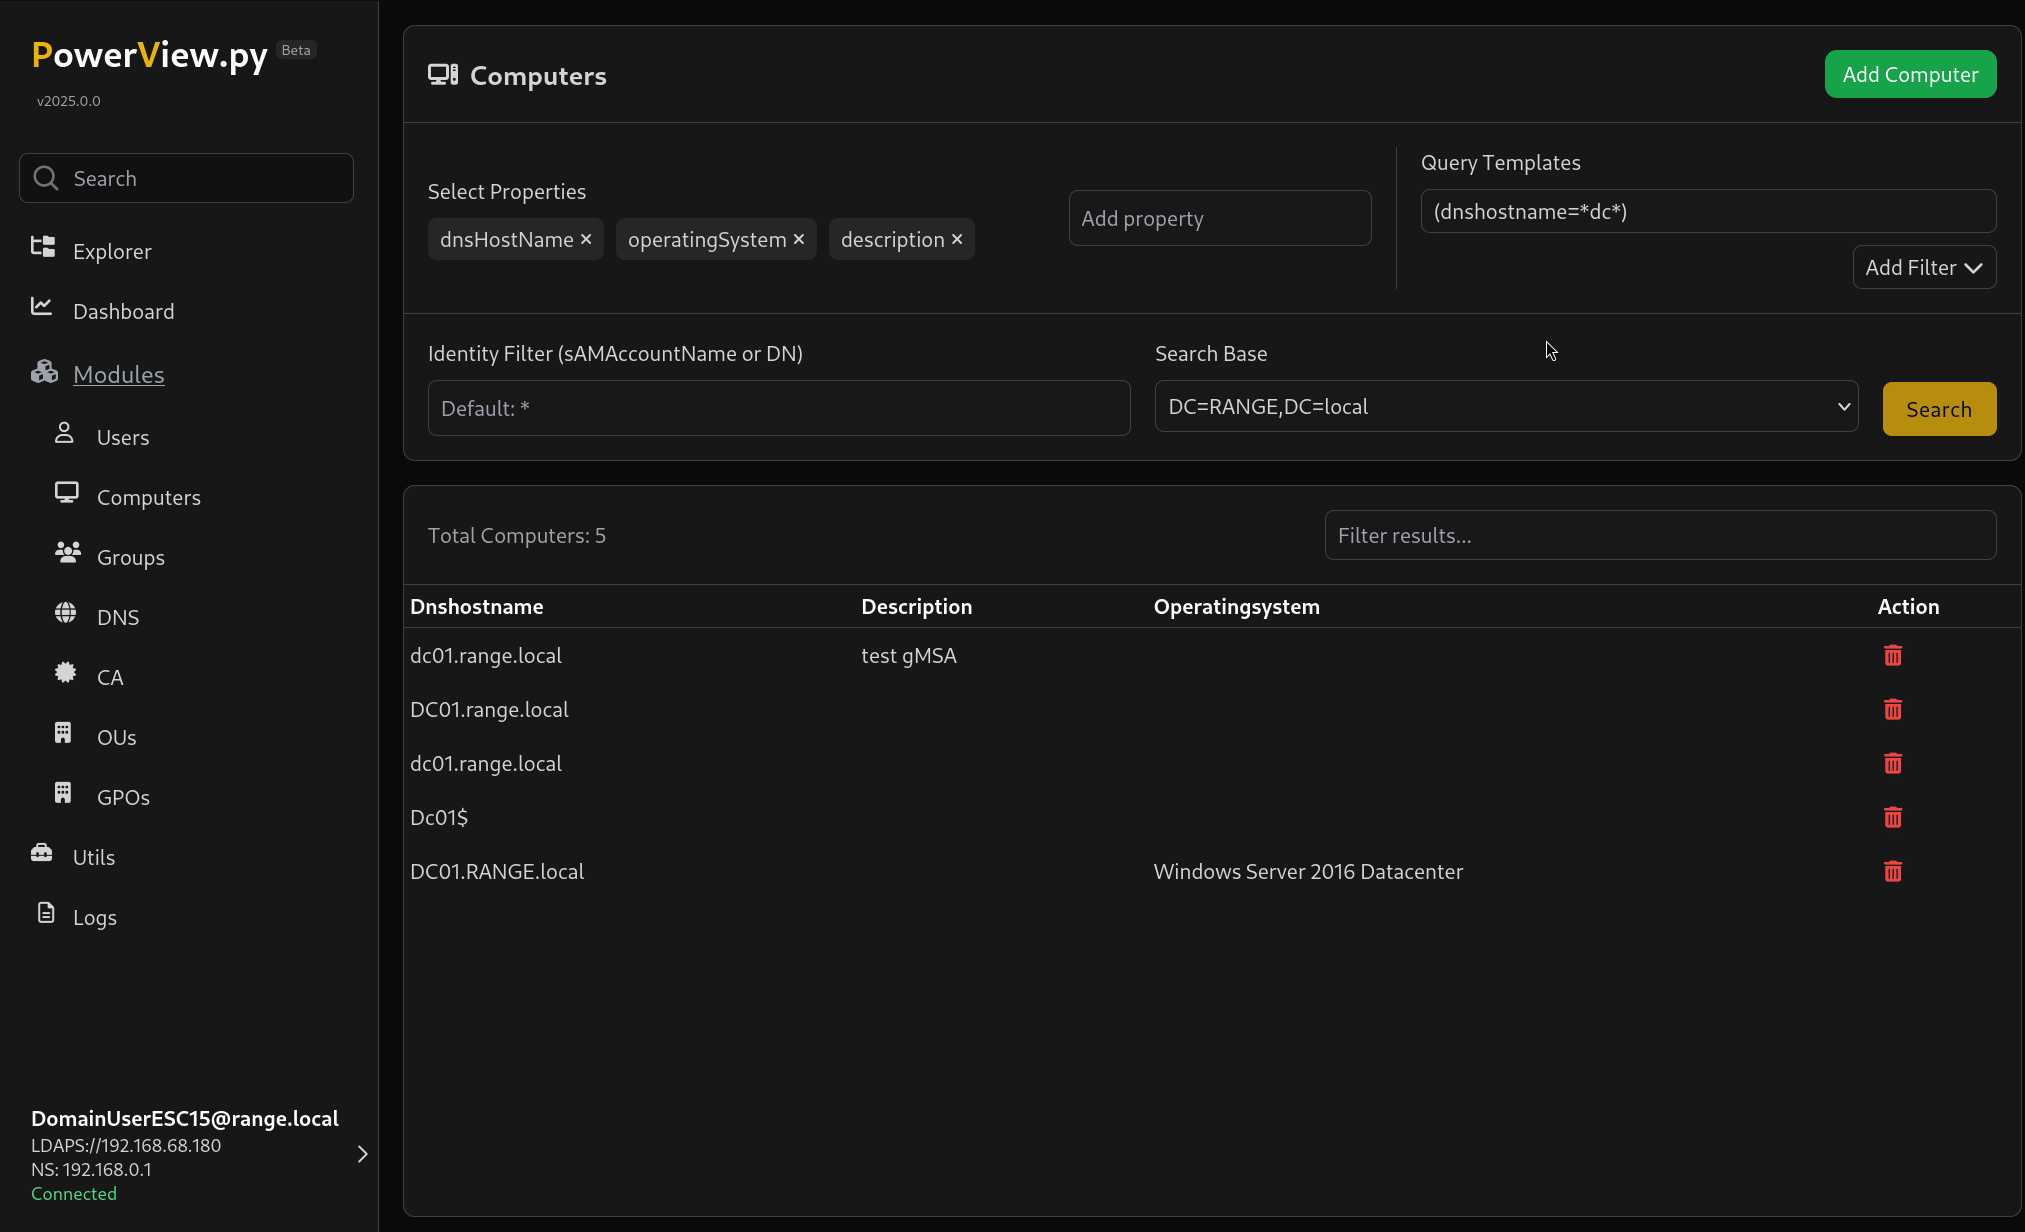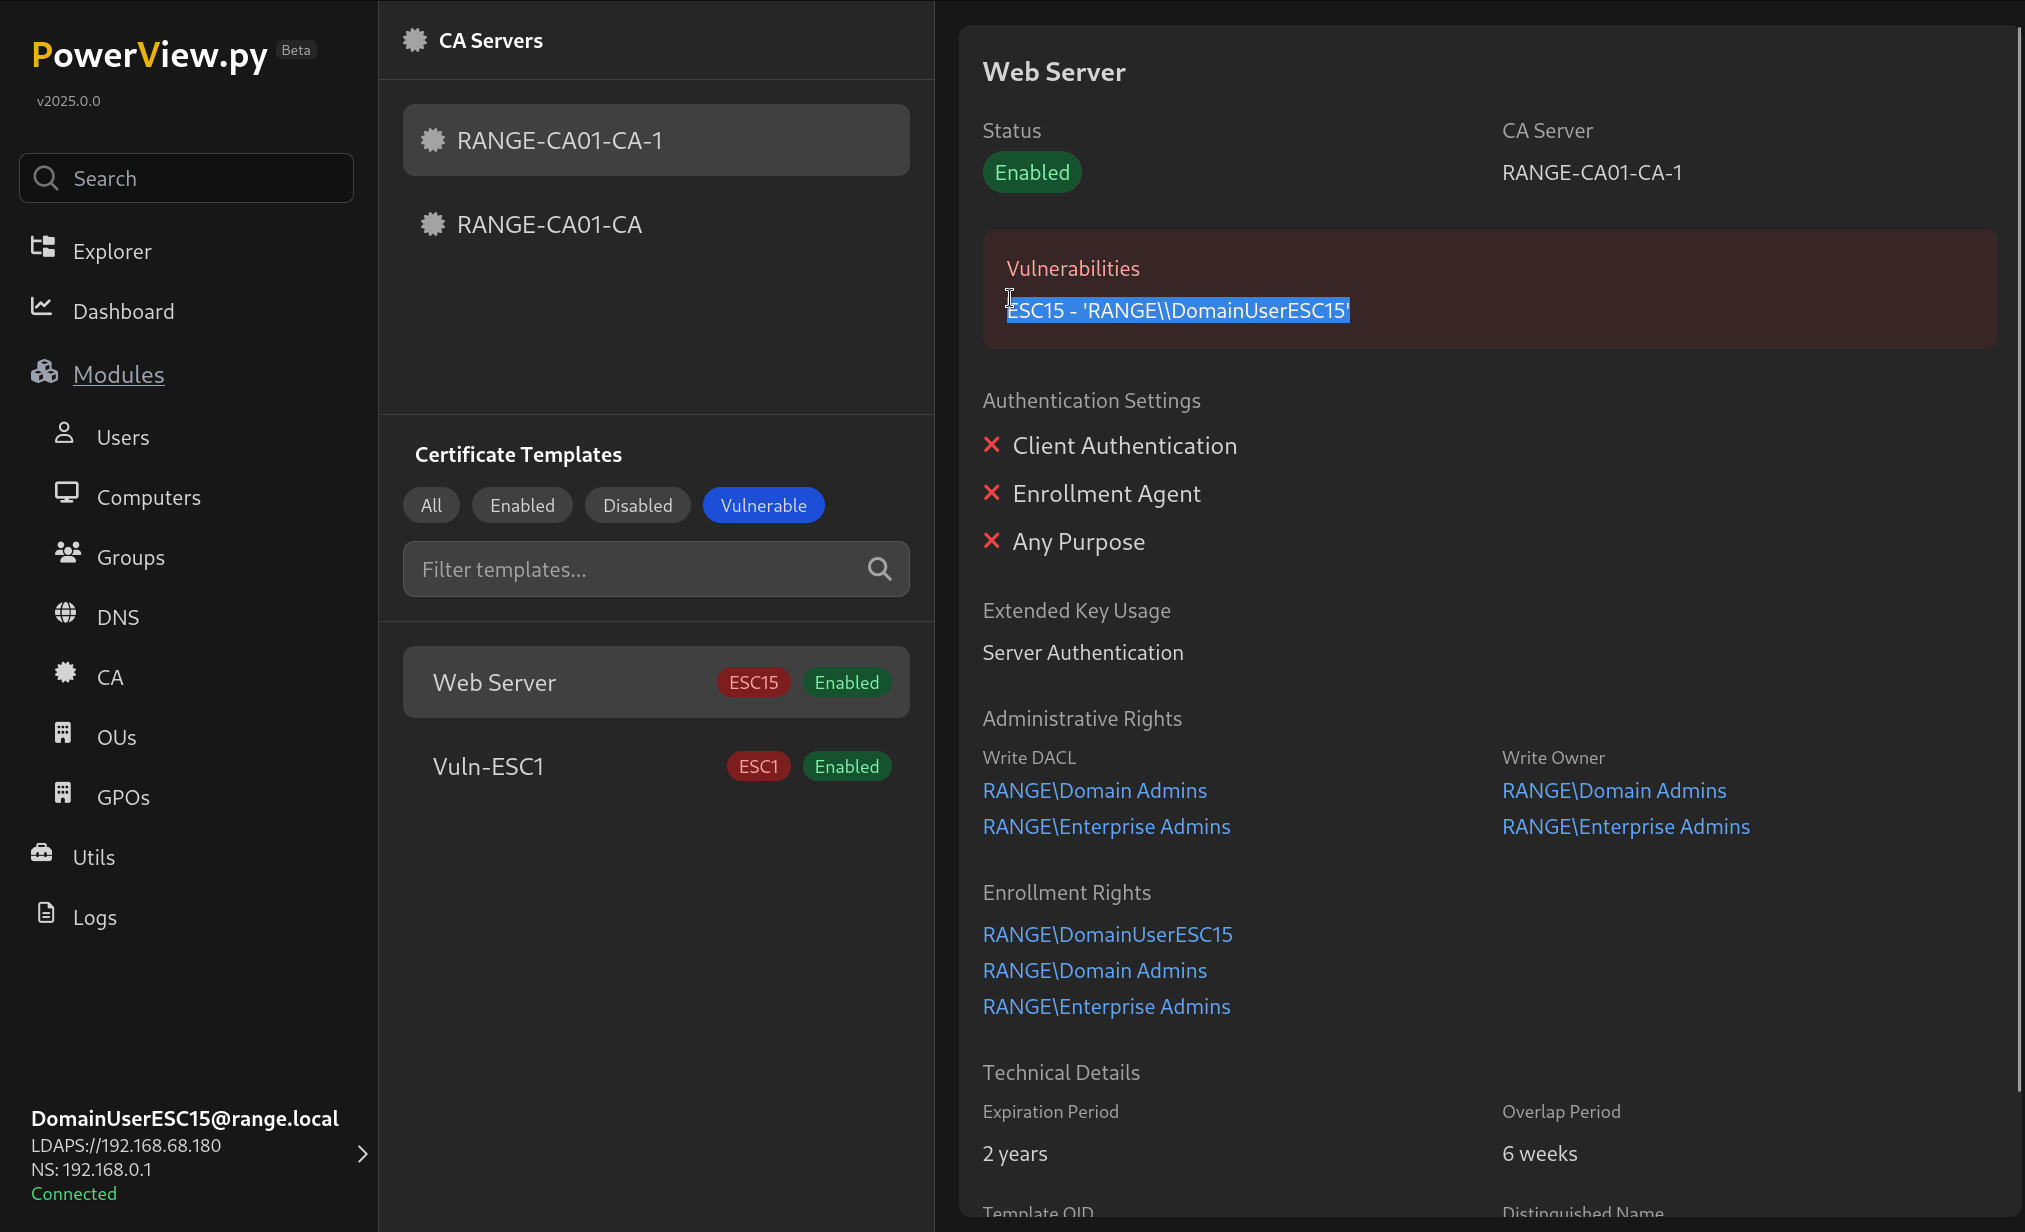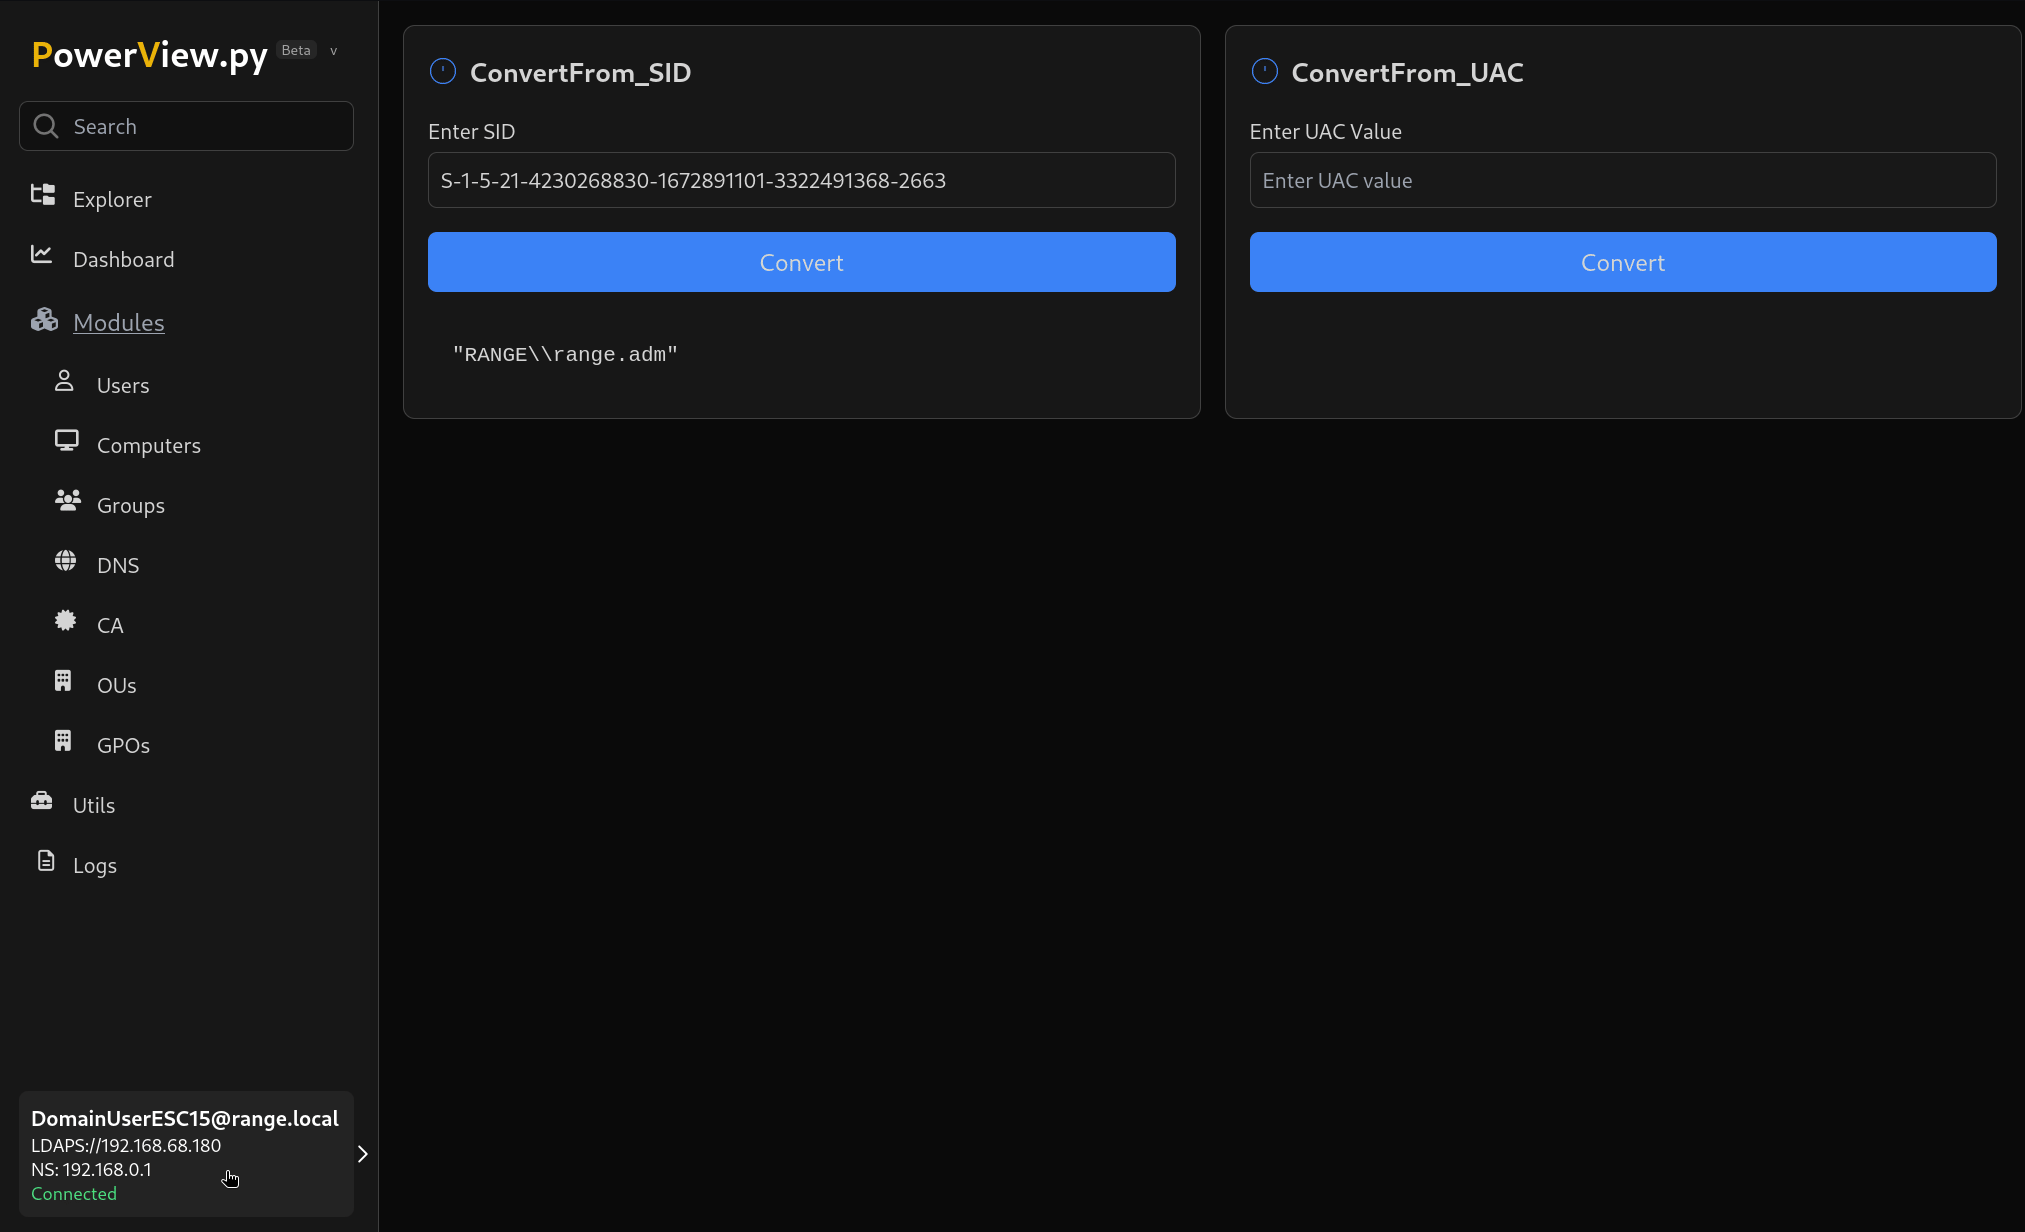
 aniqfakhrul/powerview.py
Powerview on steroids
dns-analysisexploitationinformation-gathering+7
aniqfakhrul/powerview.pyPowerview on steroids
 sia-iotechnology/kittysploit-framework
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
 aaaguirrep/offensive-docker
Offensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 gl4ssesbo1/nebula
Nebula is a cloud C2 Framework, which at the moment offers reconnaissance, enumeration, exploitation, post exploitation on AWS, but still working to…
 mazen160/shennina
Automating Host Exploitation with AI
 luemmelsec/apex
Azure Post Exploitation Framework
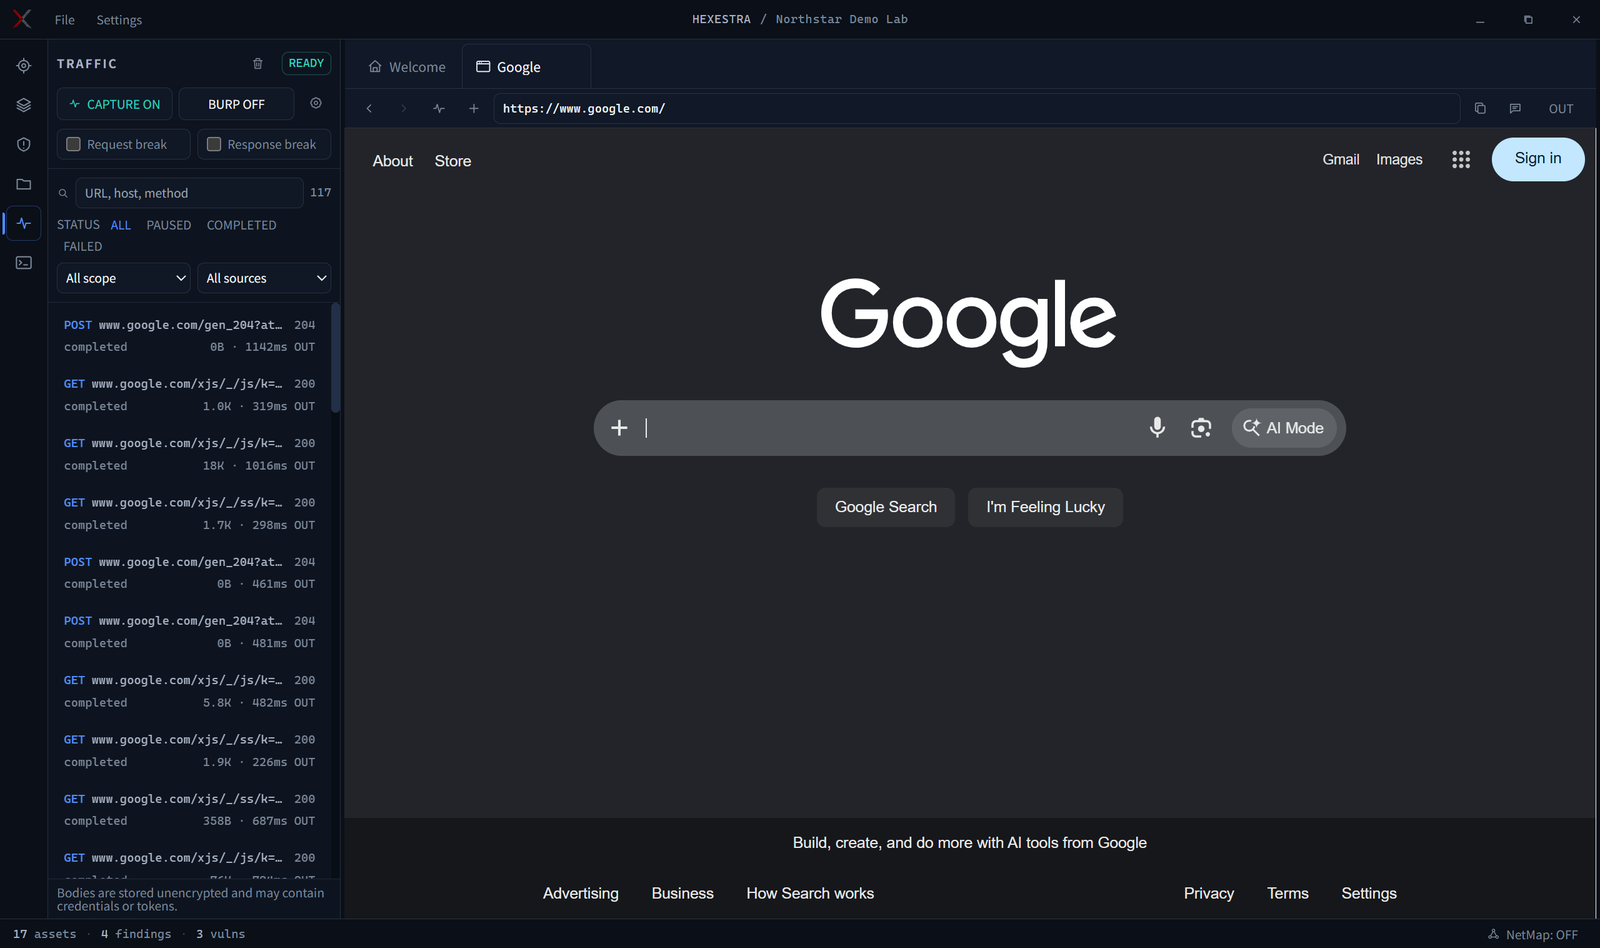 absllk/hexestra
AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
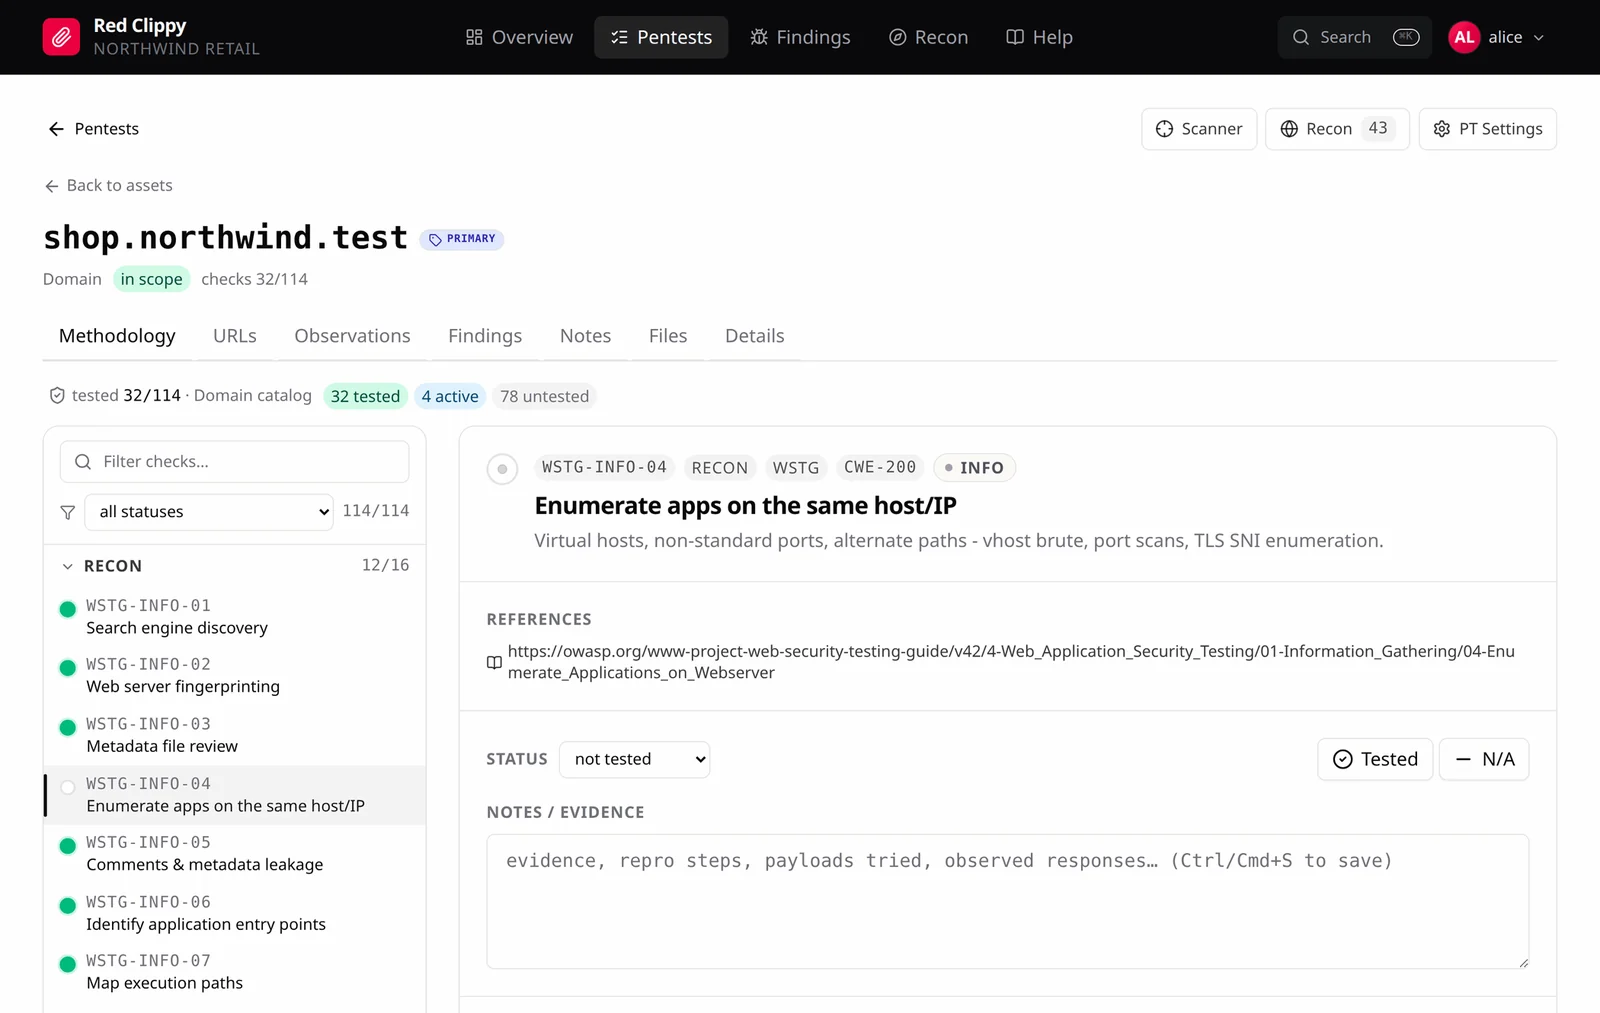 cspf-founder/red-clippy
open-source pentest management built to be operated by an AI agent
 wavestone-cdt/abaddon
Red team operations management platform automating infrastructure deployment, C2 setup, phishing campaigns, and reconnaissance with integrated tool…
 dmontgomery40/pentest-mcp
NOT for educational purposes: An MCP server for professional penetration testers including STDIO/HTTP/SSE support, nmap, go/dirbuster, nikto, JtR,…
 r00ts3c/ddos-rootsec
Explore RootSec's DDOS Archive, featuring top-tier scanners, powerful botnets (Mirai & QBot) and other variants, high-impact exploits, advanced…
 cervantessec/cervantes
Open-source collaborative platform for pentesters and red teams to manage projects, clients, vulnerabilities, and generate OWASP-compliant reports…
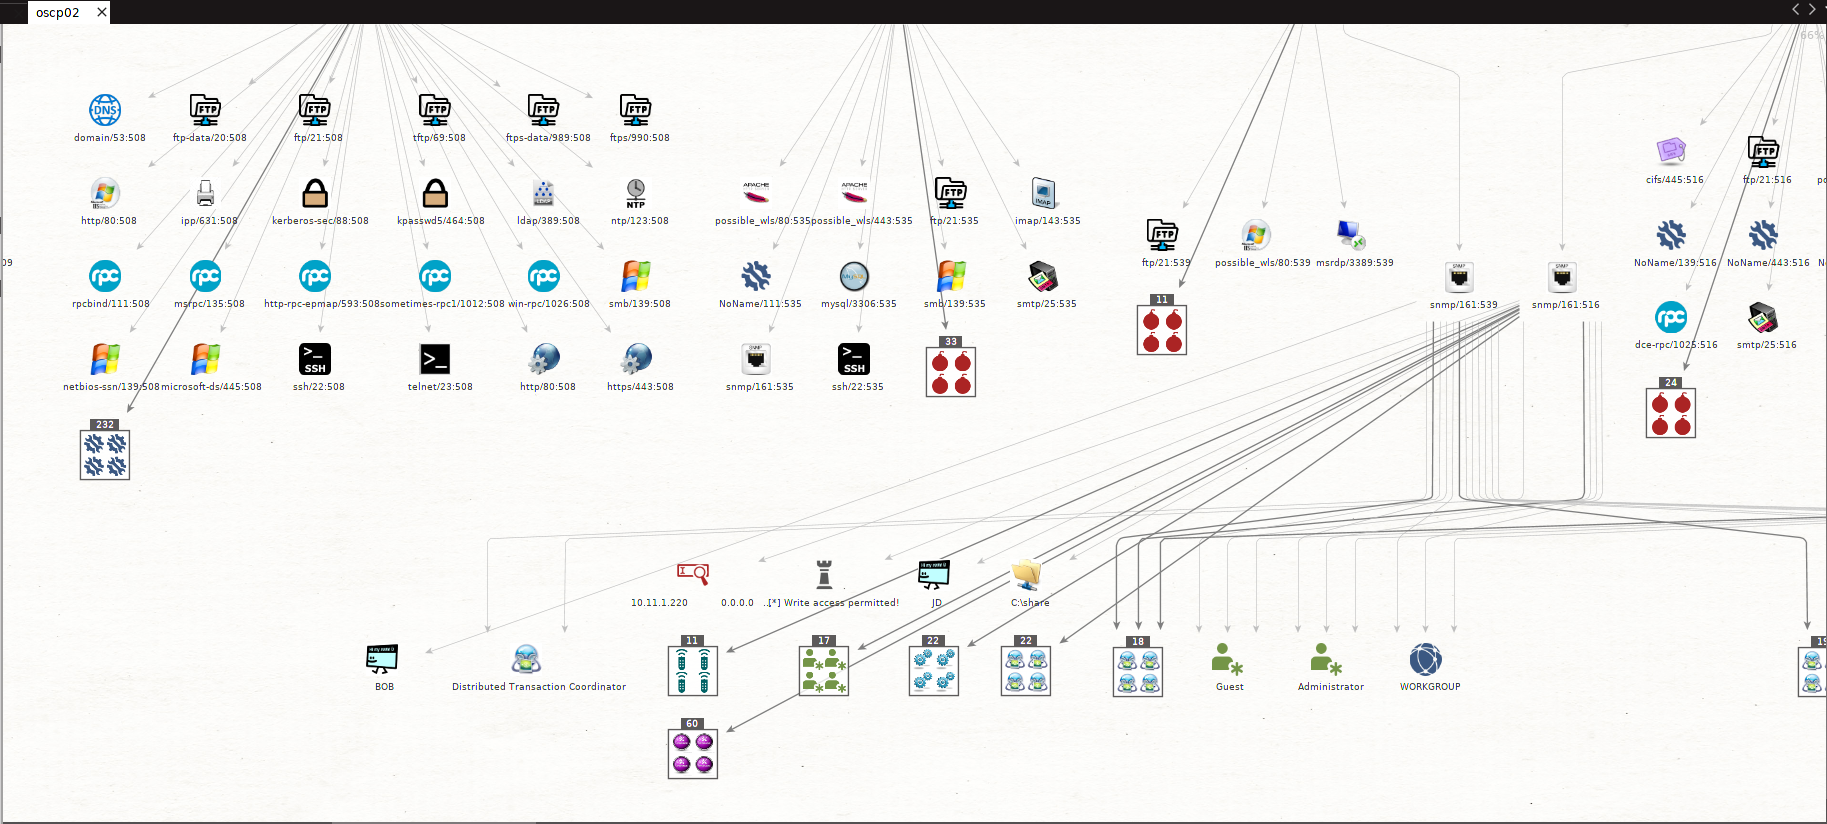 shizzz477/msploitego
Pentesting suite for Maltego based on data in a Metasploit database
 mr-rizwan-syed/chomtesh
CHOMTE.SH is a powerful shell script designed to automate reconnaissance tasks during penetration testing. It utilizes various Go-based tools to…
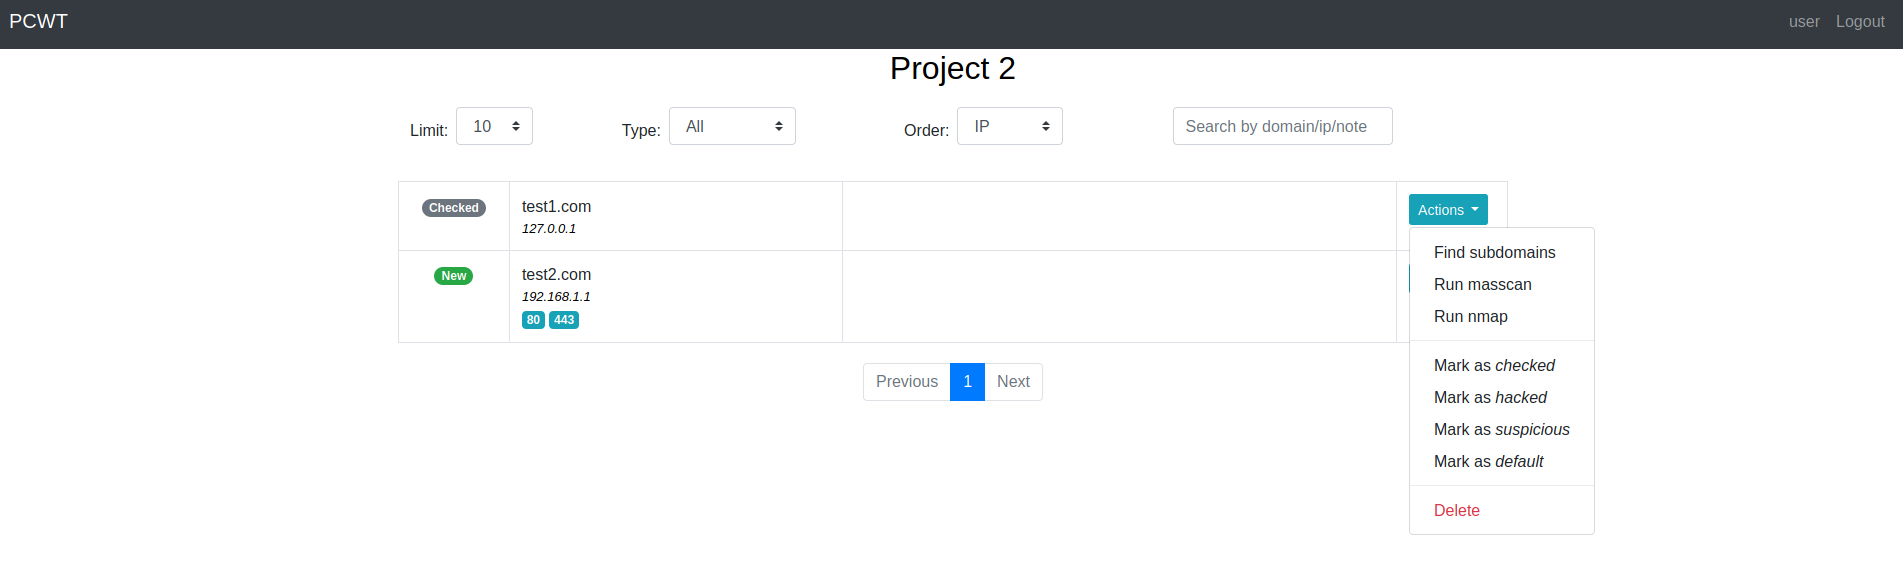 ascr0b/pcwt
Web-based project management interface for penetration testing and bug bounty workflows, automating port scanning with Nmap/Masscan and subdomain…
 sabri-zaki/easy_hack
Hack the World using Termux
 bugbasesecurity/pentest-copilot
AI-driven penetration testing agent that connects to a Kali box, autonomously runs security tools, analyzes results, and iterates through…