
Viper
 funnywolf/viper
Adversary simulation and Red teaming platform with AI
adversarial-attackai-securitycommand-and-control+5
funnywolf/viperAdversary simulation and Red teaming platform with AI
 klezvirus/inceptor
Template-Driven AV/EDR Evasion Framework

 nettitude/poshc2
A proxy aware C2 framework used to aid red teamers with post-exploitation and lateral movement.
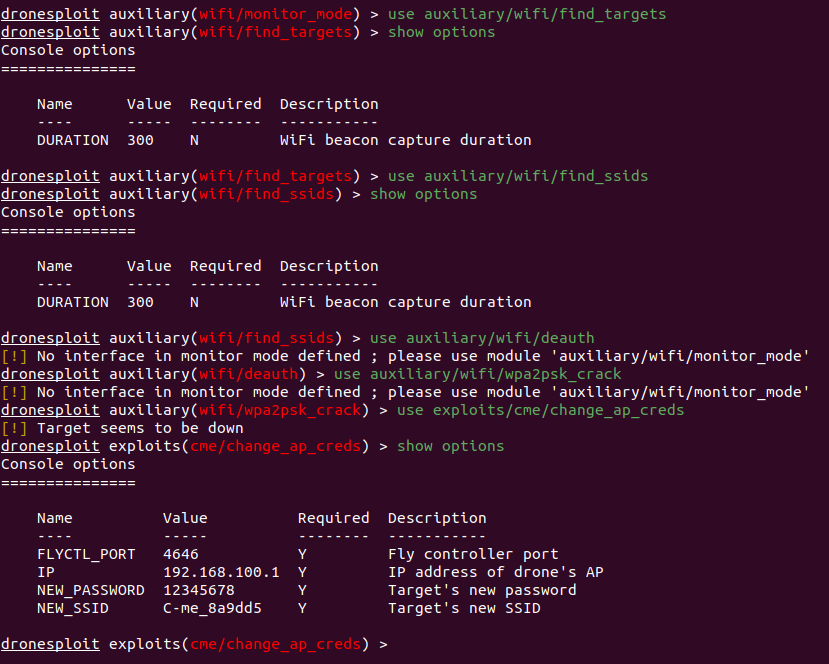 dronesploit/dronesploit
Metasploit-style console framework for pentesting commercial drones, featuring modular exploits for wireless attacks, SSID/password manipulation, and…
 redsiege/c2concealer
Generates randomized, lint-validated C2 malleable profiles for Cobalt Strike, automating HTTP/S, DNS, SMB, and SSH beacon configuration with…
 khast3x/redcloud
Automated Red Team Infrastructure deployement using Docker
 mythicagents/thanatos
Mythic C2 agent targeting Linux and Windows hosts written in Rust
 mythicagents/medusa
Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
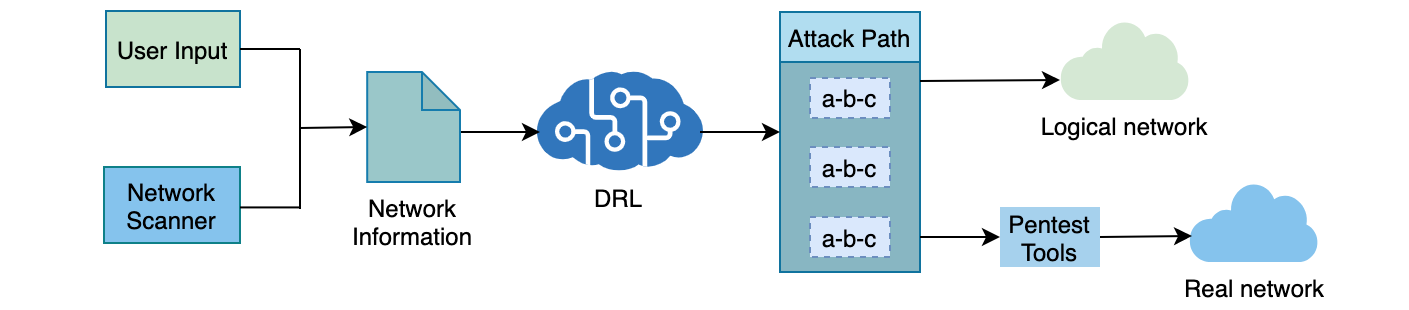 crond-jaist/autopentest-drl
AutoPentest-DRL: Automated Penetration Testing Using Deep Reinforcement Learning
 und3rf10w/external_c2_framework
Python api for usage with cobalt strike's External C2 specification
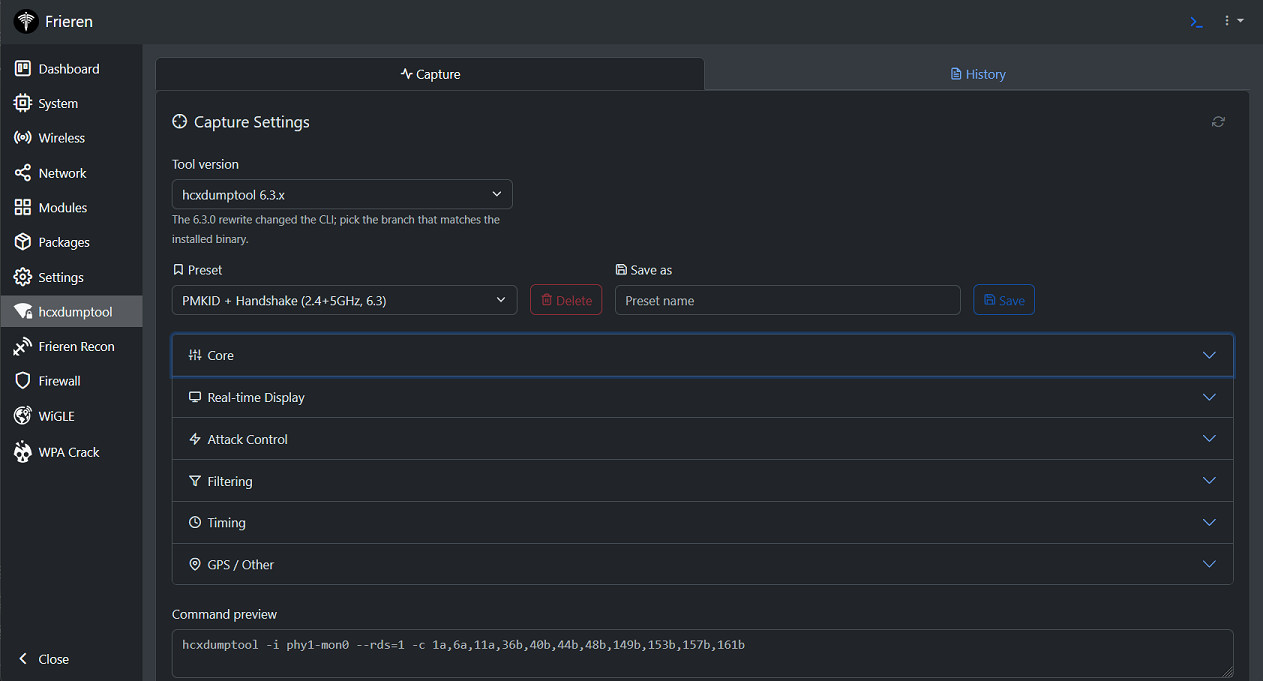 xchwarze/frieren
Frieren is a micro-framework designed for use in routers and Single Board Computers (SBCs). This framework is built to be lightweight, efficient, and…
 fraunhofer-aisec/gallia
Extendable pentesting framework for automotive UDS interfaces, enabling reproducible scans, diagnostic trouble code reading, and post-processing via…
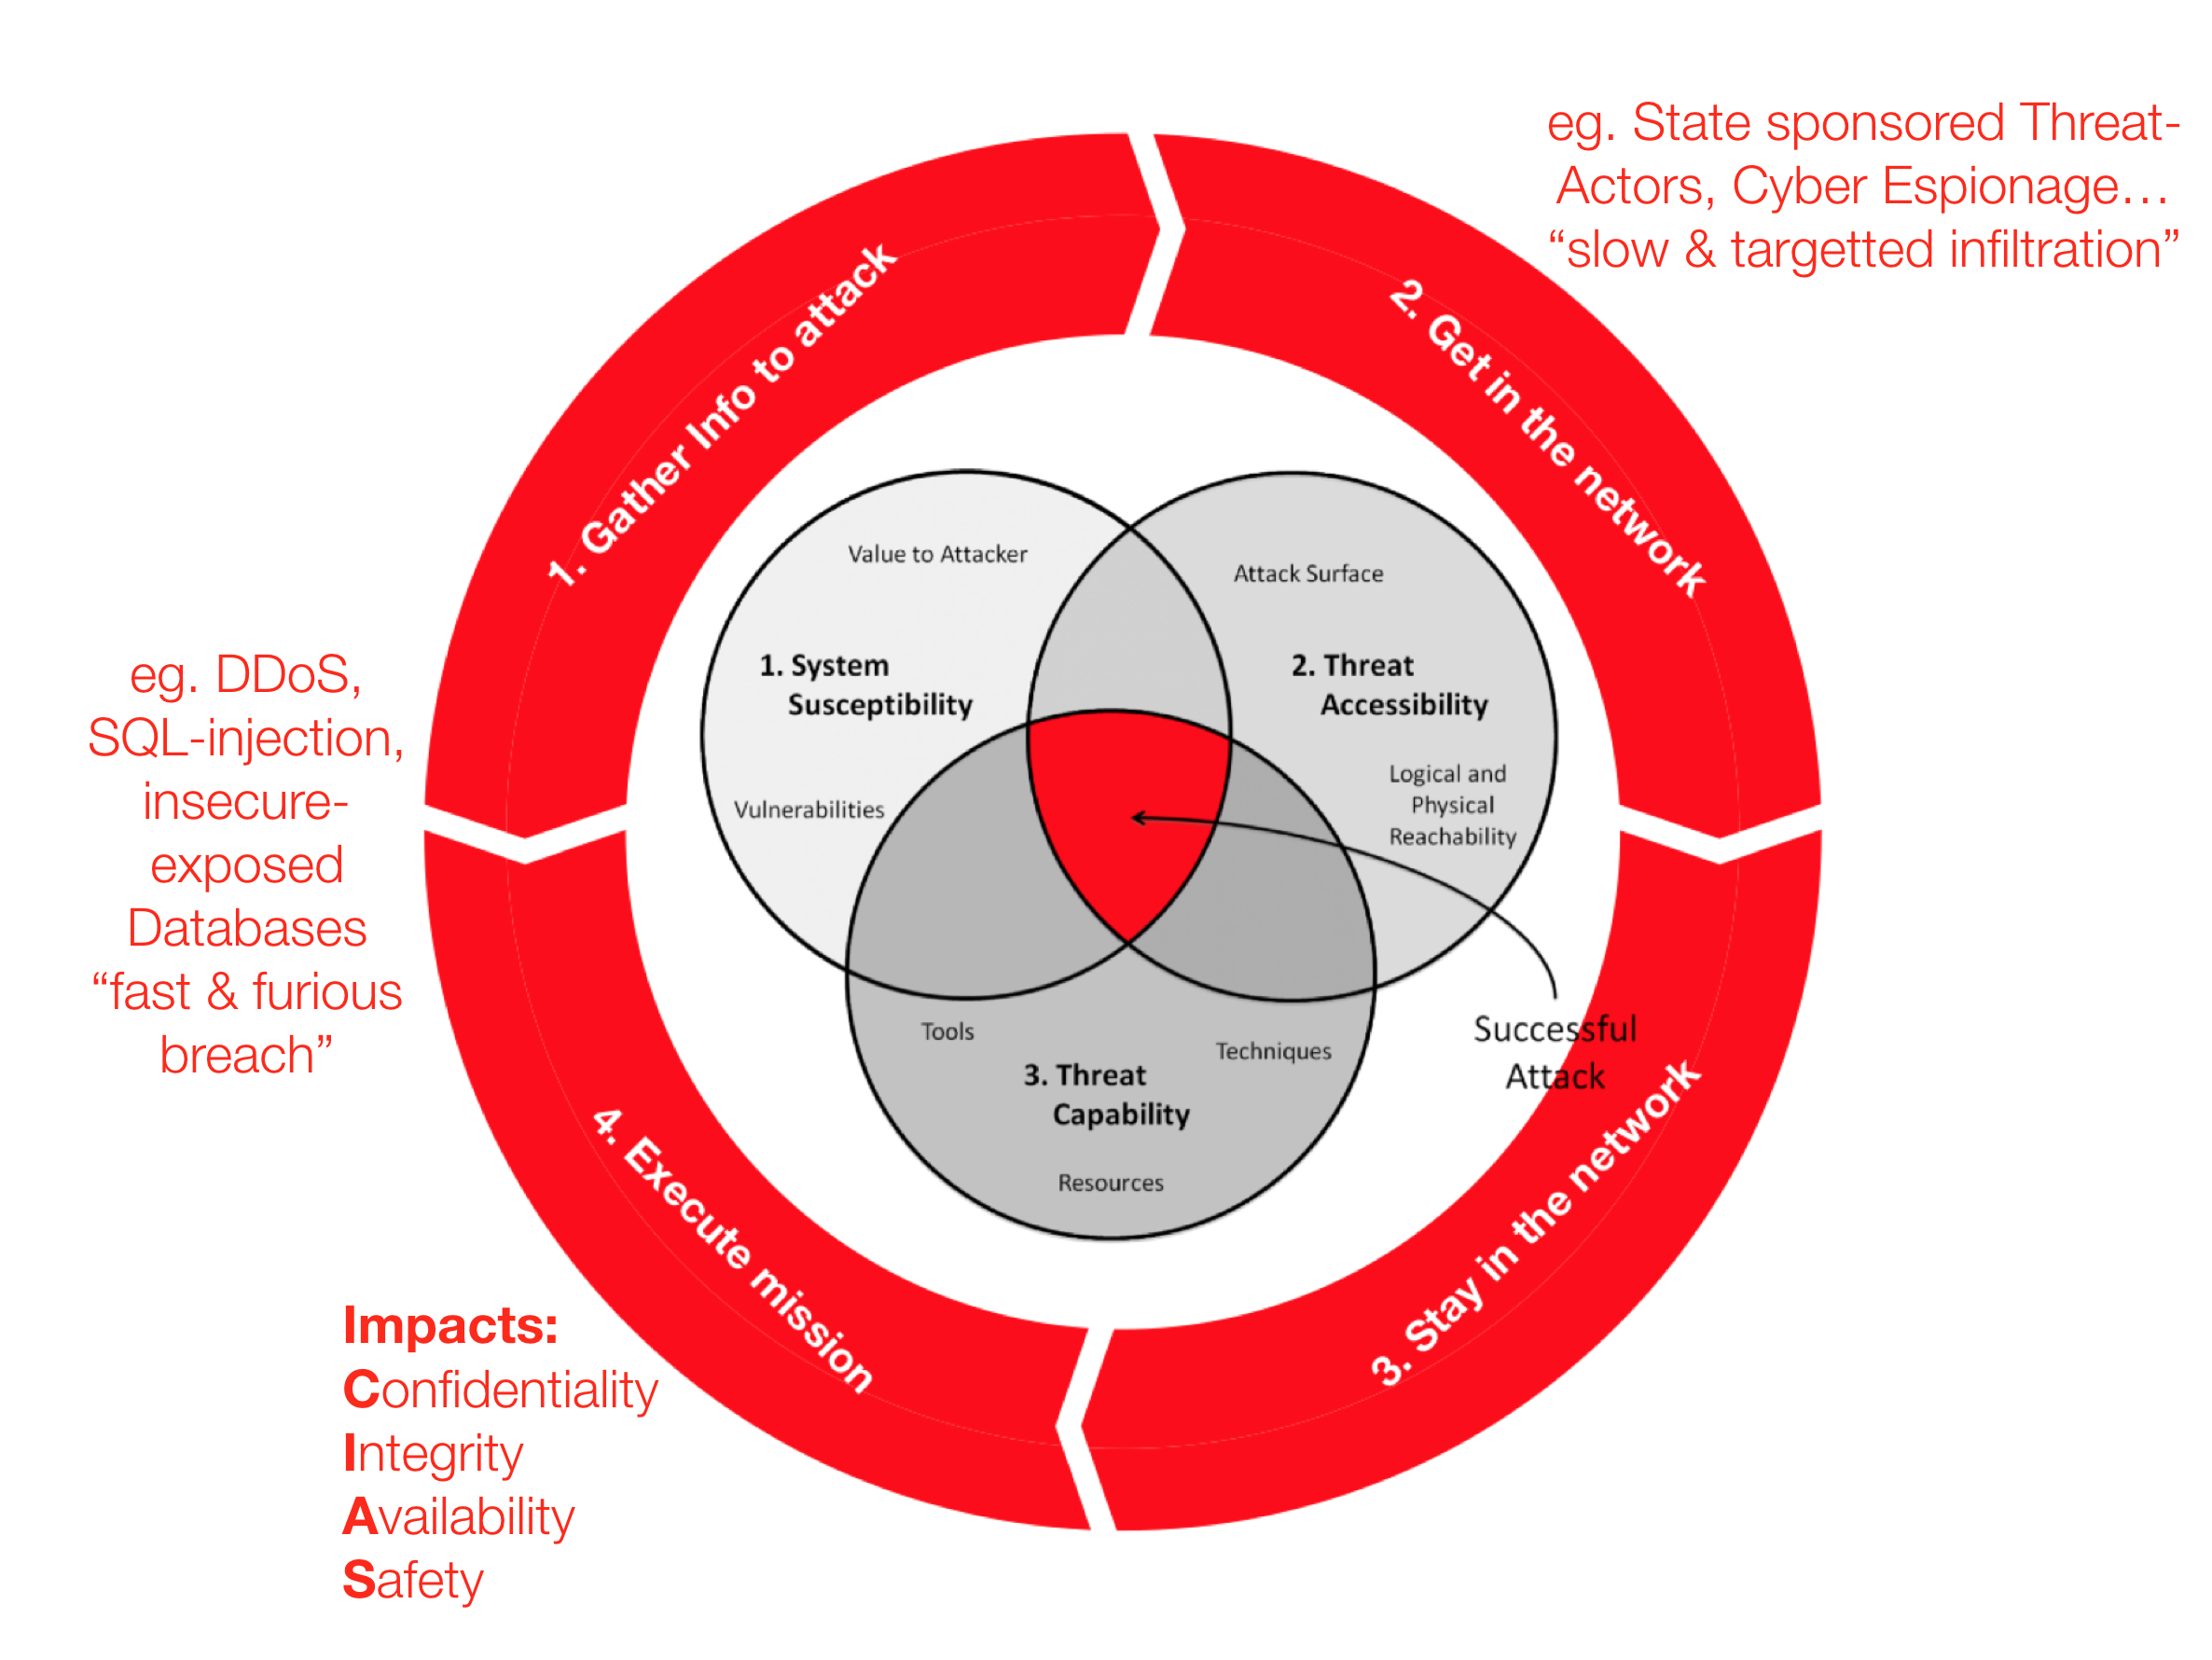 jymcheong/autottp
Automated Tactics Techniques & Procedures
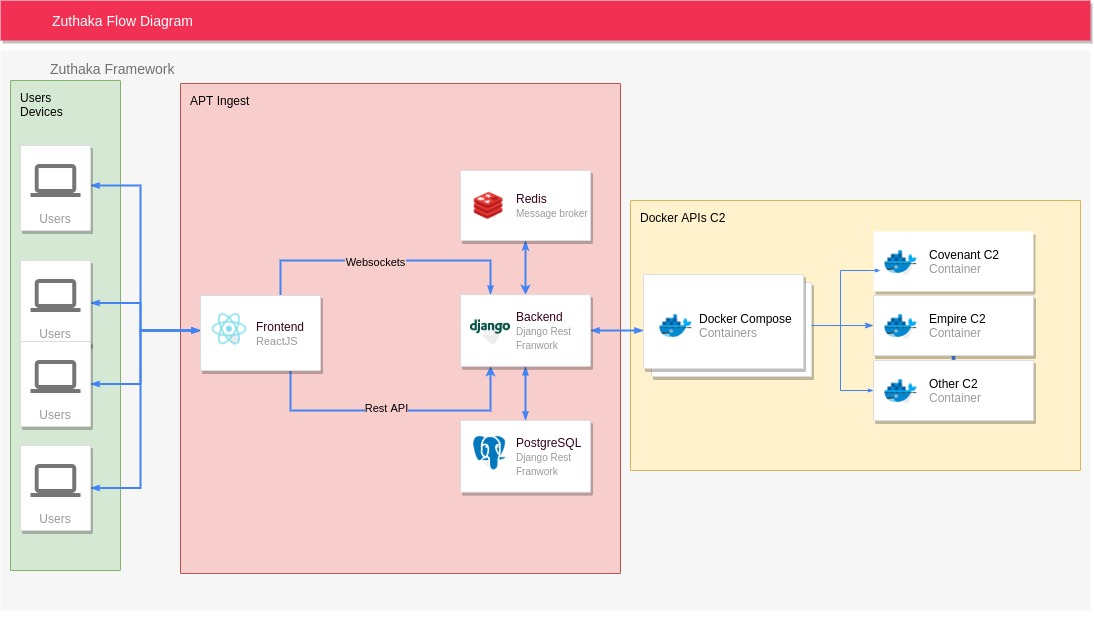 pucarasec/zuthaka
Open-source C2 integration framework providing a unified web interface for managing multiple command-and-control instances, listeners, agents, and…
 trustedsec/specula
Modular command-and-control framework abusing Microsoft Outlook's Home Page feature for stealthy persistence, remote access, and post-exploitation.
 mythicagents/nimplant
A cross-platform implant written in Nim
 bhavsec/autopentest-ai
Agentic Pentesting MCP server that discovers, exploits, and reports web application vulnerabilities.