docker-lab-cve-2017-5638-cve-2021-41773

Docker-based multi-stage attack emulation lab demonstrating CVE-2017-5638 and CVE-2021-41773 exploitation, lateral movement, and Suricata IDS…

Docker-based multi-stage attack emulation lab demonstrating CVE-2017-5638 and CVE-2021-41773 exploitation, lateral movement, and Suricata IDS…

Python-based exploit for WSO2 RCE (CVE-2022-29464) supporting multi-target scanning via URL list input.

A curated list of awesome Hacking tutorials, tools and resources

红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool

Autonomous AI penetration testing agent that orchestrates multi-agent recon, exploitation, post-exploitation, and reporting with persistent…

Multi-architecture Linux privilege escalation toolkit with 24 pre-built and runtime-compilable exploits. Auto-detects kernel version, filters patched…

OSINT & recon toolkit // 100+ tools, one-command installer, SOCMINT, GEOINT, network recon, dark web, forensics & more.

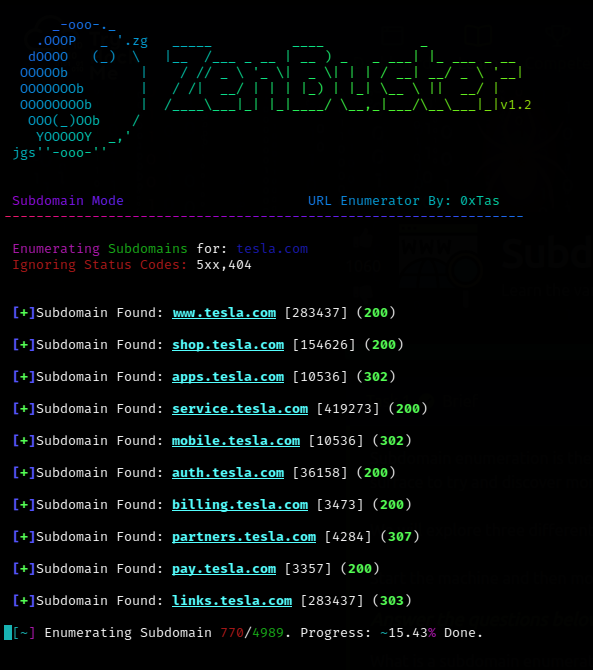
Multi-threaded URL enumeration/content-discovery tool in Python.

Reproduction pack and PoC script for CVE-2026-87796, an unauthenticated arbitrary file upload RCE in Multi Uploader for Gravity Forms <= 1.1.9, with…

Agentic Pentesting MCP server that discovers, exploits, and reports web application vulnerabilities.

Multi-threaded Telnet vulnerability scanner that exploits CVE-2026-24061 via environment variable injection, verifies root access, and provides an…

This is a multi-use bash script for Linux systems to audit wireless networks.

🔥 React2Shell Toolkit - CVE-2025-55182 & CVE-2025-66478

CVE-2026-43284 - CVE-2026-43500 - CVE-2026-46300 Variant of dirtyfrag exploit

POC for CVE-2025-29384

CVE-2026-8181: Burst Statistics Auth Bypass → REST API takeover & admin creation. Python 2.7. Educational use only.

A clean, interactive multi-step Local Privilege Escalation (LPE) exploit for Ubuntu OverlayFS (GameOver(lay)) that escapes the user namespace sandbox…

WordPress HTMega Unauthenticated PII Disclosure Exploit (CVE-2026-4106)