
BlackStone
 micro-joan/blackstone
Automated pentesting report generator with vulnerability database, severity classification, and client information gathering via subdomain and email…
information-gatheringpenetration-testingvulnerability-analysis
micro-joan/blackstoneAutomated pentesting report generator with vulnerability database, severity classification, and client information gathering via subdomain and email…
 ritvikb99/dark-fantasy-hack-tool
DDOS Tool: To take down small websites with HTTP FLOOD. Port scanner: To know the open ports of a site. FTP Password Cracker: To hack file system of…
 smicallef/spiderfoot
Automates OSINT data collection and analysis for threat intelligence, attack surface mapping, and reconnaissance. Integrates 200+ modules for DNS,…
 0x09al/raven
raven is a Linkedin information gathering tool that can be used by pentesters to gather information about an organization employees using Linkedin.
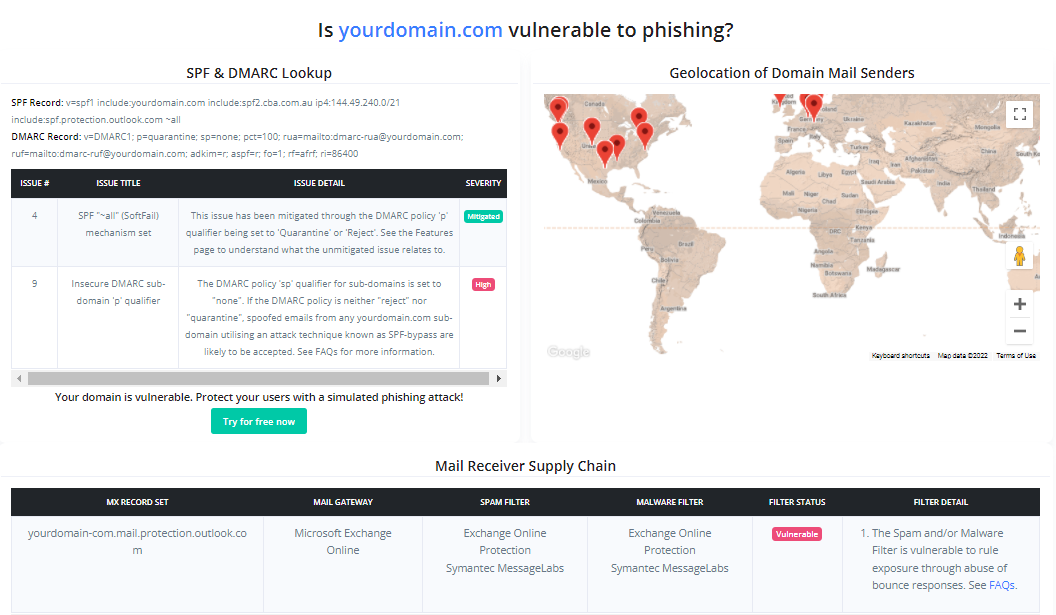 caniphish/phishious
An open-source Secure Email Gateway (SEG) evaluation toolkit designed for red-teamers.
 h4md153v63n/cve-2022-40347_intern-record-system-phone-v1.0-sql-injection-vulnerability-unauthenticated
CVE-2022-40347: Intern Record System - 'phone', 'email', 'deptType' and 'name' SQL Injection (Unauthenticated)
 blue-chocolates/cve-2016-10033
Exploit for CVE-2016-10033, a remote code execution vulnerability in PHPMailer, enabling unauthenticated attackers to execute arbitrary code via…
 rootxsushant/cve-2023-5561-poc-updated
Updated POC for Unauth Post Author Email Disclosures WordPress CVE-2023-5561
 jeanback1/cve-2019-9053-exploit
Automated exploit for CVE-2019-9053, a time-based blind SQL injection in CMS Made Simple ≤2.2.9. Extracts admin credentials (username, email,…
 networksecure/cve-2020-14065
Exploit for CVE-2020-14065: unlimited file upload vulnerability in Icewarp Email Server 12.3.0.1, enabling remote code execution via crafted upload…
 randomrobbiebf/cve-2021-24959
WP Email Users <= 1.7.6 - SQL Injection
 7h30th3r0n3/cve-2025-51586-prestashop-poc
PrestaShop AdminLogin Email Enumeration PoC - CVE-2025-51586. This repository provides an ethical Proof-of-Concept (PoC) for the PrestaShop…
 networksecure/cve-2020-14064
Proof-of-concept exploit for CVE-2020-14064, an incorrect access control vulnerability in Icewarp Email Server 12.3.0.1, enabling unauthorized access.
 thewoodenbench/cve-2025-66955
Local File Inclusion in Contact Plan, E-Mail, SMS and Fax components in Asseco SEE Live 2.0 allows remote authenticated users to access files on the…
 tghook/cve-2024-4295-poc
CVE-2024-4295 Email Subscribers by Icegram Express <= 5.7.20 - Unauthenticated SQL Injection via hash
 rasyidfox/cve-2019-18818
Exploit for CVE-2019-18818 allowing password reset of admin accounts via email. Useful for penetration testing and vulnerability verification of…
 hf3cyber/cms-made-simple-2.2.9-unauthenticated-sql-injection-exploit-cve-2019-9053-
Time-based blind SQL injection exploit for CMS Made Simple <= 2.2.9 (CVE-2019-9053) that extracts username, email, password hash, and salt, with…
 nxploited/cve-2024-0235-poc
The EventON WordPress plugin before 4.5.5, EventON WordPress plugin before 2.2.7 do not have authorisation in an AJAX action, allowing…