
CVE-1999-0678
 lto7777777/cve-1999-0678
CVE-1999-0678- /doc directory browsable
configuration-auditingeducationintrusion-detection+4
lto7777777/cve-1999-0678CVE-1999-0678- /doc directory browsable
 fengjixuchui/cve-2021-40444-docx-generate
Generates .docx files exploiting CVE-2021-40444 for Microsoft Office Word Remote Code Execution via malicious bitmap image objects.
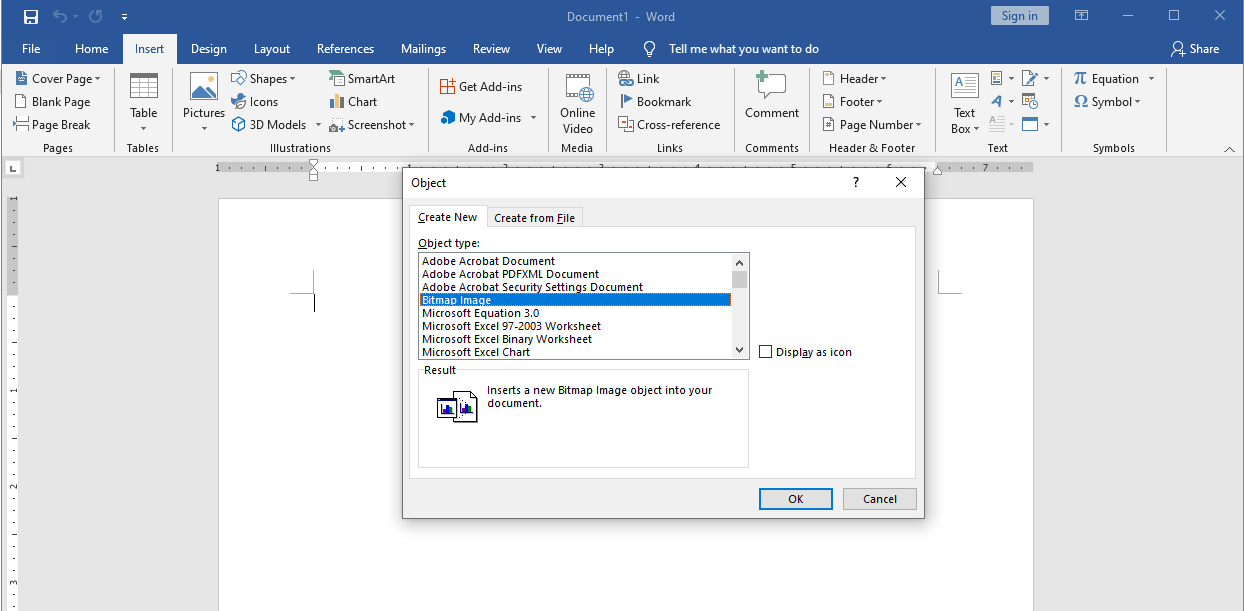 knooow/cve-2021-40444-docx-generate
Generates malicious .docx files exploiting CVE-2021-40444 (Microsoft Office Word RCE) with embedded HTML and CAB payloads for penetration testing.
 hqdat809/cve-2021-40444
Malicious DOCX generator exploiting CVE-2021-40444 for remote code execution via crafted Office documents, with integrated hosting server for payload…
 sudoaza/cve-2022-30190
MS-MSDT Follina CVE-2022-30190 PoC document generator
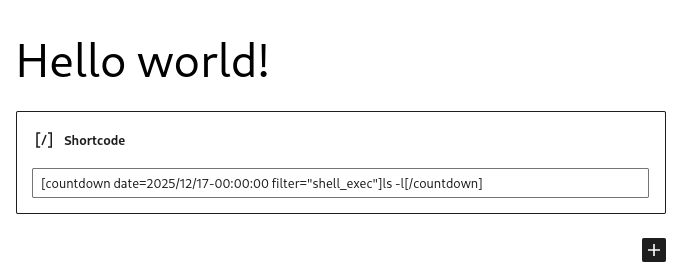 nimisha17/poc-cve-2025-9519
Proof-of-concept exploit for CVE-2025-9519, demonstrating remote code execution in WordPress Easy Timer plugin via a crafted shortcode filter, with…
 febinrev/deepin-linux_reader_rce-exploit
CVE-2023-50254: PoC Exploit for Deepin-reader RCE that affects unpatched Deepin Linux Desktops. Deepin Linux's default document reader…
 hscorpion/cve-2022-30190
Proof-of-concept exploit for CVE-2022-30190 (Follina). Generates malicious docx files and hosts a server to trigger remote code execution via…
 ceramicskate0/sharpexchange
C# Tool to interact with MS Exchange based on MS docs
 karazajac/dirtyfail
Detector + PoC for Linux page-cache write vulnerabilities: Copy Fail (CVE-2026-31431) and Dirty Frag (CVE-2026-43284/43500). Authorized security…
 qasimshahbaz21/cve-exploit-research-development
SSH Exploit Tool (Educational Use Only) 📌 Description This tool demonstrates exploitation of: CVE-2008-0166 CVE-2008-1657 It connects to vulnerable…
 tiagob0b/cve-2021-40444
Malicious DOCX generator exploiting CVE-2021-40444 (Microsoft Office Word RCE) with CAB-based DLL side-loading and CAB-less RAR/WSF attack chains for…
 caido/caido
Lightweight web proxy for intercepting, inspecting, and modifying HTTP traffic to audit web applications during penetration testing and bug bounty…
 infamoussyn/rogue
An extensible toolkit providing penetration testers an easy-to-use platform to deploy Access Points during penetration testing and red team…
 rolix44/kubestroyer
Go-based Kubernetes exploitation tool that scans for exposed ports and exploits cluster misconfigurations, including anonymous Kubelet RCE and etcd…
 komomon/cve-2022-30190-follina-office-msdt-fixed
Modified CVE-2022-30190 exploit tool for MS-MSDT Office RCE with custom docx template support, binary/command execution modes, and embedded HTTP…