
slinger
 emo-crab/slinger
An HTTP client specifically developed for security researchers
api-security-testingpenetration-testingvulnerability-analysis+2
29
emo-crab/slingerAn HTTP client specifically developed for security researchers
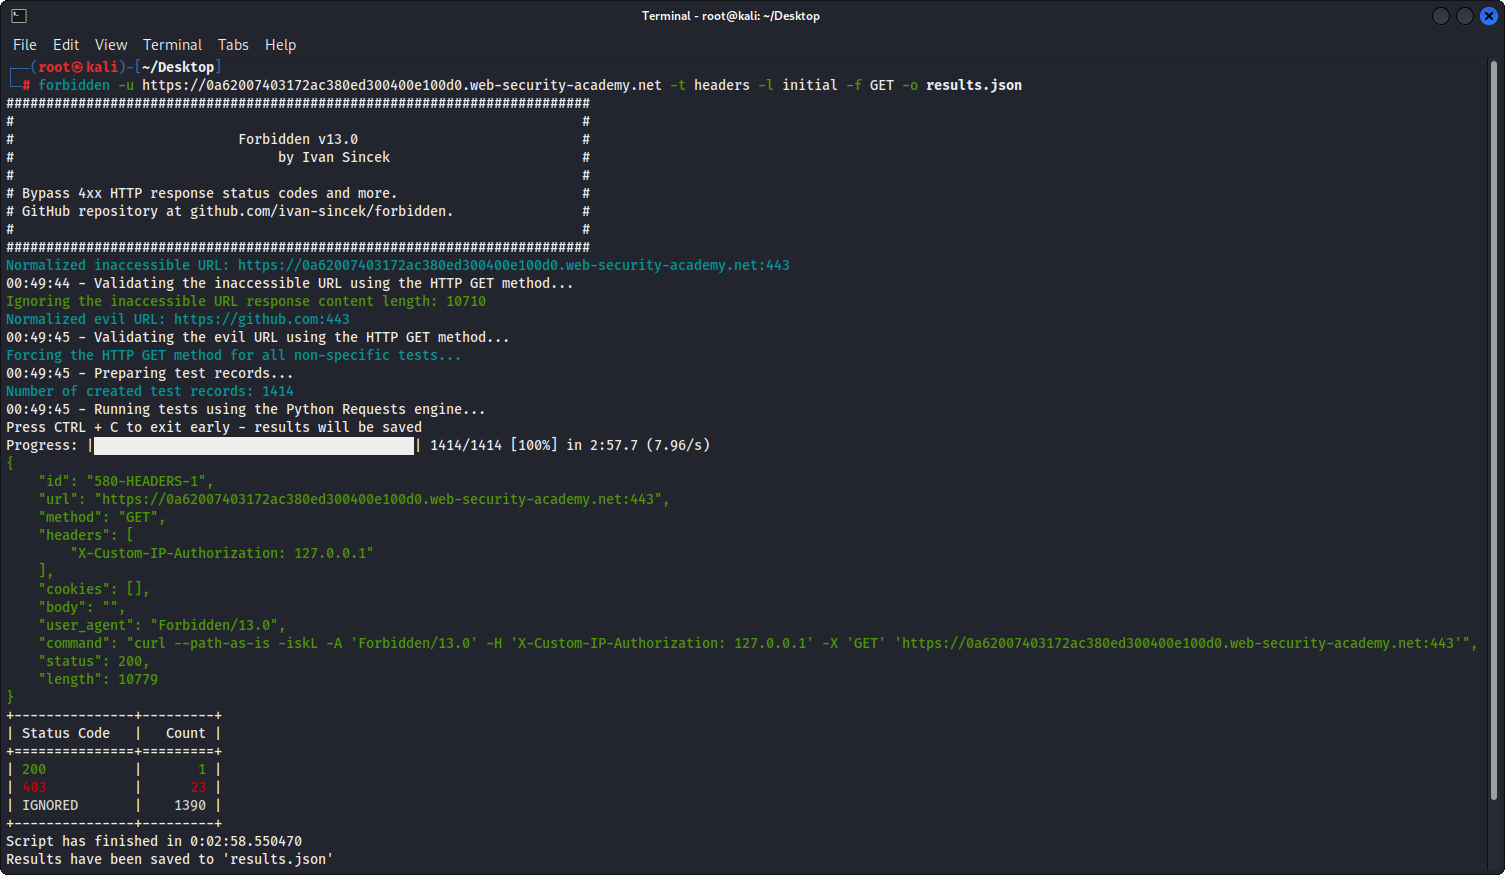 ivan-sincek/forbidden
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
 oscerd/cve-2026-49365
PoC reproducer for CVE-2026-49365 (Apache Camel camel-netty-http / camel-undertow): muteException defaults to false, so an uncaught exception's full…
 d0rb/rusttlsx
🦀 Stealth HTTP client for Rust . mimics real browser TLS fingerprints for undetectable requests. Fast, type-safe, and built for precision networking.
 davidblakecoe/axios-cve-2025-27152-poc
Proof-of-concept exploit for CVE-2025-27152 in Axios, demonstrating a server-side request forgery vulnerability in the popular HTTP client library.
 forse01/cve-2019-17638-jetty
Exploit for CVE-2019-17638 targeting Jetty Java HTTP server, enabling remote code execution via crafted HTTP requests for security testing and…
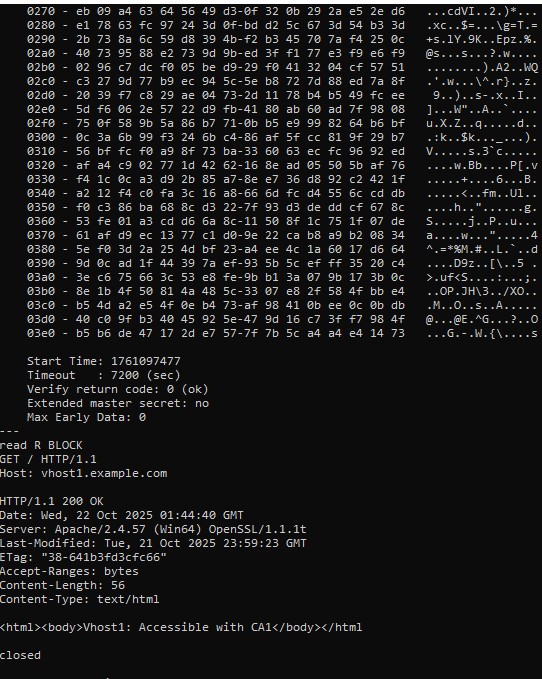 absholi7ly/cve-2025-23048-poc
Apache HTTP Server versions 2.4.35 – 2.4.63 are vulnerable to a client certificate authentication bypass when TLS 1.3 session resumption is used…
 coana-tech/cve-2022-0155-poc
Proof-of-concept demonstrating CVE-2022-0155 cookie theft via HTTP redirect in follow-redirects npm package, including Express server and client…
 jpillora/chisel
Fast TCP/UDP tunnel over HTTP with SSH encryption, supporting reverse port forwarding, SOCKS5 proxy, and client authentication for secure network…
 ozozuz/qlik-view-12.60-including-sr-stored-cross-site-scripting-cve-2022-42248
Proof-of-concept exploit for CVE-2022-42248, a stored cross-site scripting vulnerability in QlikView Ajax Client allowing remote attackers to execute…
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 theopaid/cve-2026-66746-http-response-splitting-via-unvalidated-response-header-values-rouille-
Security Advisory: HTTP Response Splitting via Unvalidated Response Header Values (rouille)
 nccgroup/abptts
TCP tunneling over HTTP/HTTPS for web application servers
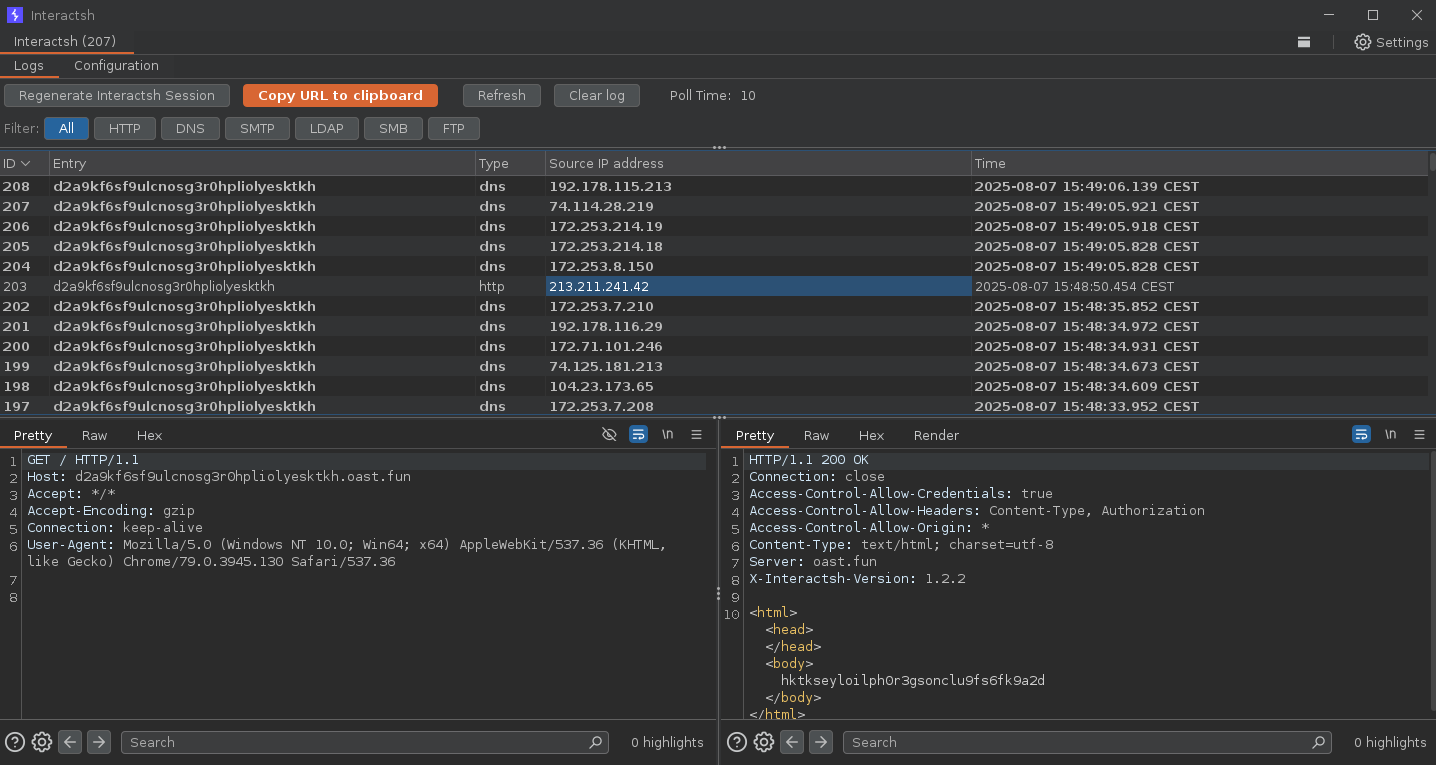 projectdiscovery/interactsh
An OOB interaction gathering server and client library
 nccgroup/wssip
Application for capturing, modifying and sending custom WebSocket data from client to server and vice versa.