
CVE-2026-82222
 ghostlyrootb2h/cve-2026-82222
Exploit framework for CVE-2026-82222, an unauthenticated RCE in GiveWP WordPress plugin. Supports mass scanning, auto-detection, multi-threading,…
command-and-controlexploitationinformation-gathering+5
ghostlyrootb2h/cve-2026-82222Exploit framework for CVE-2026-82222, an unauthenticated RCE in GiveWP WordPress plugin. Supports mass scanning, auto-detection, multi-threading,…
 cerberusmrxi/discuz-x5.0-authentication-bypass-exploit-framework
Discuz! X5.0 Authentication Bypass Exploit Framework (CVE-2026-49952) - Critical vulnerability allowing unauthenticated database backup access via…
 epsilonpoint88-glitch/epsilonpoint-
Modular exploit framework targeting CVE-2026-23550 in WordPress, featuring mass exploitation, obfuscation, post-exploitation, and Docker-based C2…
 ermensonx/cve-2024-38077-madlicense-exploit
Modular exploit framework for CVE-2024-38077 (Windows RDL heap overflow) with ASLR bypass, heap grooming, ROP chain generation, and DLL injection…
 trinadh465/frameworks_base_cve-2023-20943
Android framework base exploit for CVE-2023-20943, enabling privilege escalation testing on vulnerable Android devices.
 timwr/cve-2019-5825
Chrome V8 exploit for CVE-2019-5825 targeting version 73.0.3683.86 with --no-sandbox. Includes proof-of-concept code and integration with Metasploit…
 moften/cve-2024-51996
CVE-2024-51996 es una vulnerabilidad crítica que afecta al componente security-http del framework Symfony.
 voraka/cve-2017-8760
Python toolkit that generates malicious RTF files exploiting CVE-2017-8759 to deliver Metasploit payloads, enabling remote code execution on…
 sgxgsx/bluetoolkit
Modular Bluetooth Classic (BR/EDR) vulnerability testing framework with reconnaissance, exploit modules for 43 public attacks/CVEs, and structured…
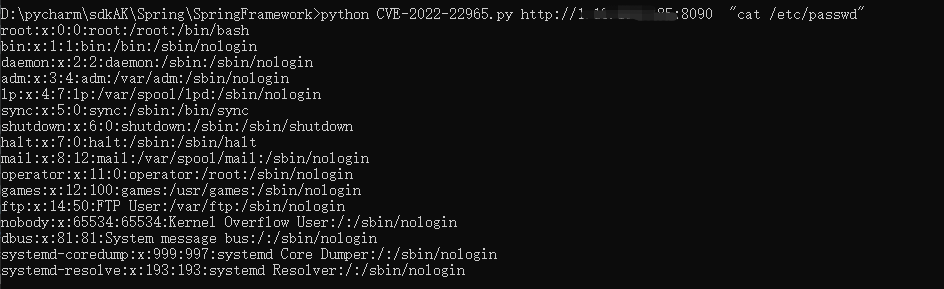 xsxtw/springframework_cve-2022-22965_rce
Python exploit for Spring Framework CVE-2022-22965 remote code execution with webshell deployment and Burp payload support for penetration testing.
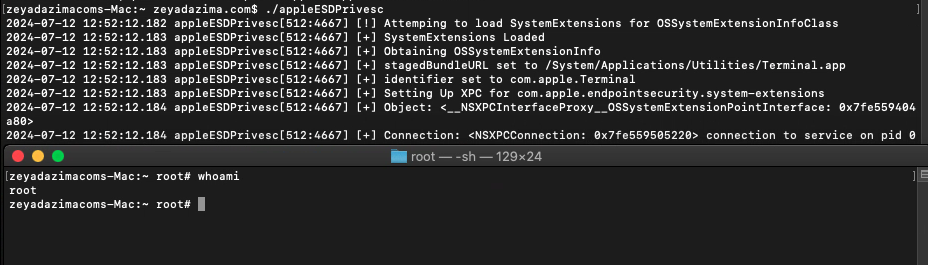 securelayer7/cve-2019-8805
Exploit for CVE-2019-8805 Apple EndpointSecurity framework Privilege Escalation
 c0ff33b34n/cve-2021-38314
Python exploit for CVE-2021-38314 targeting unauthenticated sensitive information disclosure in WordPress Gutenberg Template Library & Redux…
 rubensuxo-eh/react2shell-exploit
React2Shell-Exploit — Complete exploitation framework for CVE-2025-55182, including Python exploit, Docker vulnerable lab, Burp Suite manual and…
 tom4t0/cve-2018-1270_exp
Proof-of-concept exploit for CVE-2018-1270, a Spring Framework remote code execution vulnerability, demonstrating exploitation in Java.
 limo520/cve-2023-20860
Educational proof-of-concept exploit for CVE-2023-20860, a Spring Framework security bypass via un-prefixed double wildcard pattern, with links to…
 shoucheng3/spring-projects__spring-framework_cve-2022-22965_5-2-19-release
Exploit for CVE-2022-22965 (Spring4Shell) targeting Spring Framework versions vulnerable to remote code execution via classLoader manipulation.
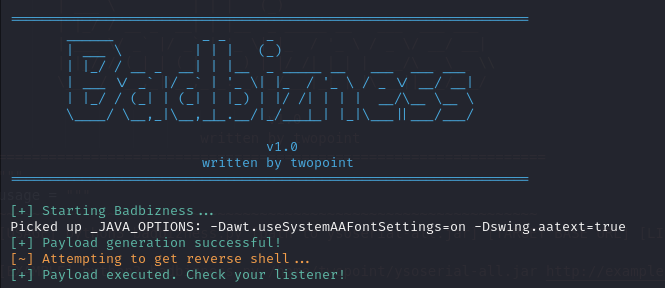 jakeotte/badbizness-cve-2023-51467
Auto exploit script for the Java web framework OF Biz under CVE-2023-51467.
 dorkerdevil/remote-desktop-services-remote-code-execution-vulnerability-cve-2019-0708-
Remote code execution exploit for CVE-2019-0708 (BlueKeep) in Windows Remote Desktop Services, designed to integrate with the pocsuite3 framework for…