
BreakEscape
 cliffe/breakescape
Mountable Rails engine providing 24+ cybersecurity escape room scenarios with randomized passwords, JIT-compiled NPC dialogue, and RESTful API for…
ctfeducationlabs-practice+3
cliffe/breakescapeMountable Rails engine providing 24+ cybersecurity escape room scenarios with randomized passwords, JIT-compiled NPC dialogue, and RESTful API for…
 adversarial-detection-engineering/adversarial-detection-engineering-framework
A framework and taxonomy for identifying, classifying, and reasoning about detection logic bugs in SIEM, EDR, and XDR rules, with concrete examples…
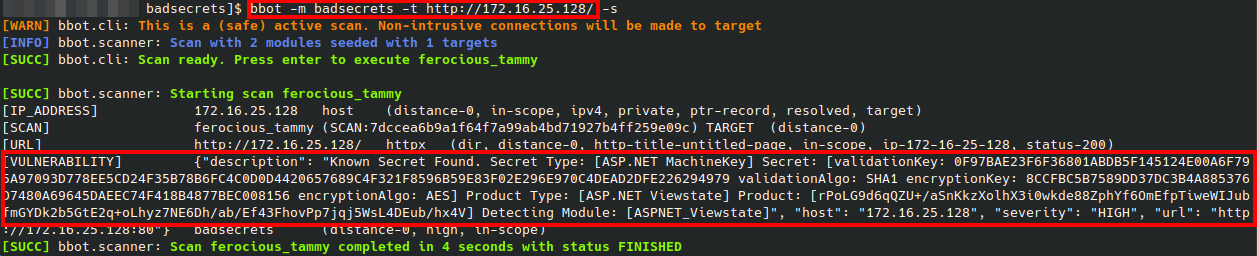 blacklanternsecurity/badsecrets
A library for detecting known secrets across many web frameworks
 ffffffff0x/f8x
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool
 duriantaco/ravage
Evidence first autonomous web security testing for controlled, authorized targets. With reproducible labs, audit trails, reports, and XBEN…
 owasp/railsgoat
A vulnerable version of Rails that follows the OWASP Top 10
 hackspeak/cve-2026-66066
CVE-2026-66066 (KindaRails2Shell) PoC - Rails Active Storage/libvips arbitrary file read to RCE; for authorized security testing
 shinthink/cve-2026-66066
CVE-2026-66066 — KindaRails2Shell: Rails Active Storage/libvips Arbitrary File Read → RCE. MATLAB/HDF5 dual-identity file → SECRET_KEY_BASE theft →…
 0xsha/kindarails2shell
Single-file PoC for Rails CVE-2026-66066: arbitrary file read, secret recovery, threaded scanning, and conditional RCE via signed image variations.
 oscerd/cve-2026-53913
PoC reproducer for CVE-2026-53913 (Apache Camel camel-keycloak): KeycloakSecurityPolicy fails open in the Basic Setup — with no required…
 wildwestcybersecurity/cve-2019-5420-poc
cve-2019-5420 POC simple ruby script
 caginkyr/cve-2026-5203
Exploit for CVE-2026-5203 in CMS Made Simple, leveraging path traversal and arbitrary file upload to achieve remote code execution with an…
 w4r10ck423/envvisualizer
Parse and visualize /proc/self/environ on compromised Linux boxes — categorizes env vars by tech stack (AWS, Django, Rails, NodeJS, MySQL, K8s,…
 cyfare/cve-2026-23918-apache-http-server-doublefree-poc
Proof-of-concept exploit for CVE-2026-23918, a double-free vulnerability in Apache HTTP Server, demonstrating remote crash via crafted requests.
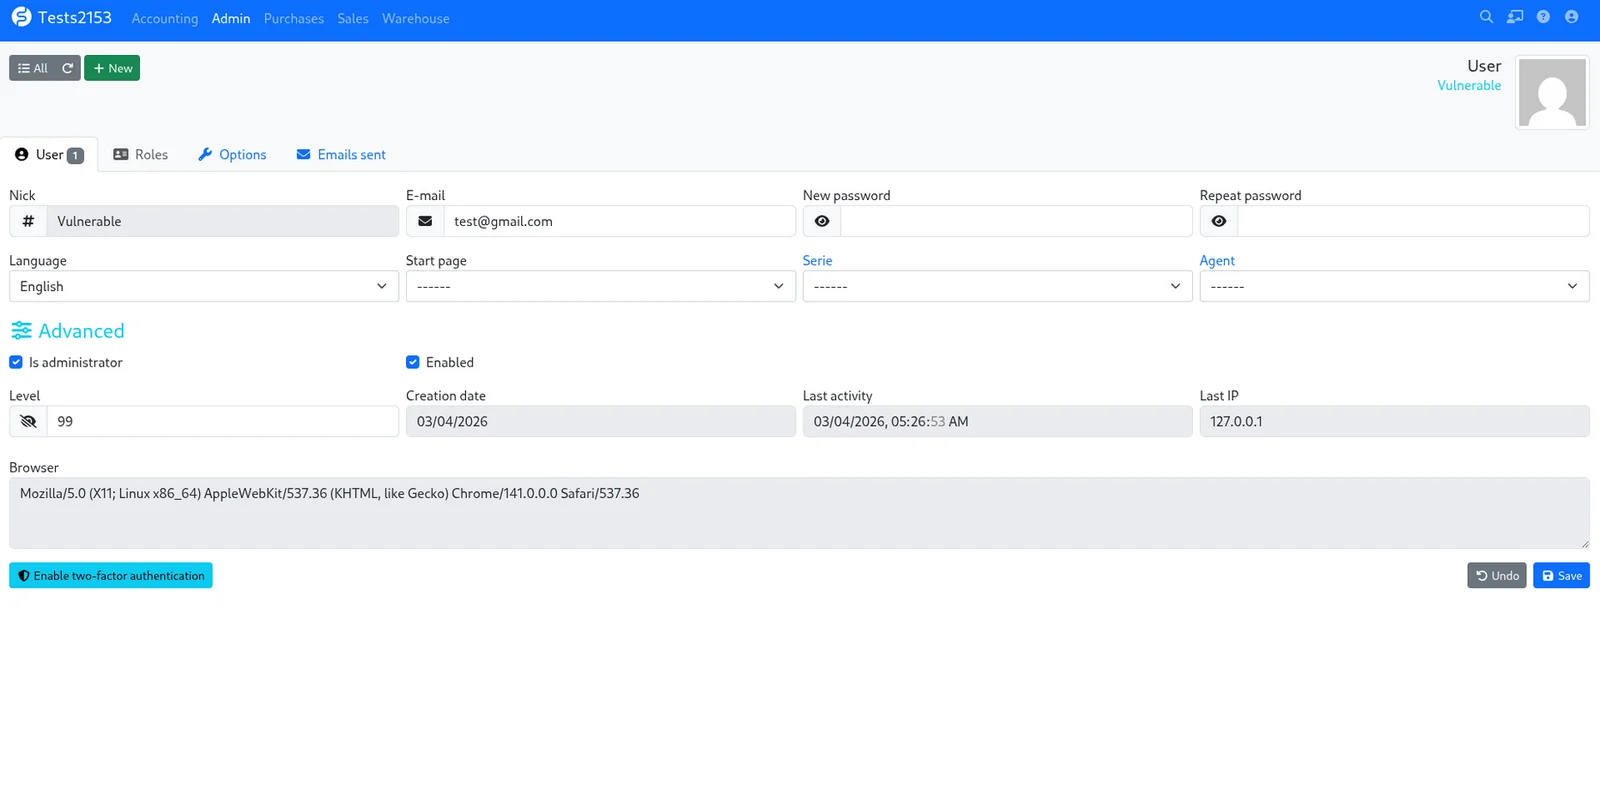 turkios/cve-2026-32699-facturascripts-nick-bypass
Broken Access Control in FacturaScripts EditUser controller allows authenticated users to rename any account (including admin) by modifying the…
 lu3ky13/alternative-approach-reverse-shell-callback-test-invokeai-rce
This repository contains alternative payload approaches for the InvokeAI RCE vulnerability (CVE-2024-12029) when SSH key injection fails. The…
 404-src/cve-2026-34486
Exploit for Apache Tomcat EncryptInterceptor bypass leading to unauthenticated RCE via Java deserialization on port 4000. Includes lab setup,…
