
signal-server-dropwizard-admin
 abraxas/signal-server-dropwizard-admin
Signal-Server v20261007.0.0 - High - Remote - Privilege leftover - unauth Dropwizard admin :8081
configuration-auditingdefensive-toolsinformation-gathering+5
7
abraxas/signal-server-dropwizard-adminSignal-Server v20261007.0.0 - High - Remote - Privilege leftover - unauth Dropwizard admin :8081
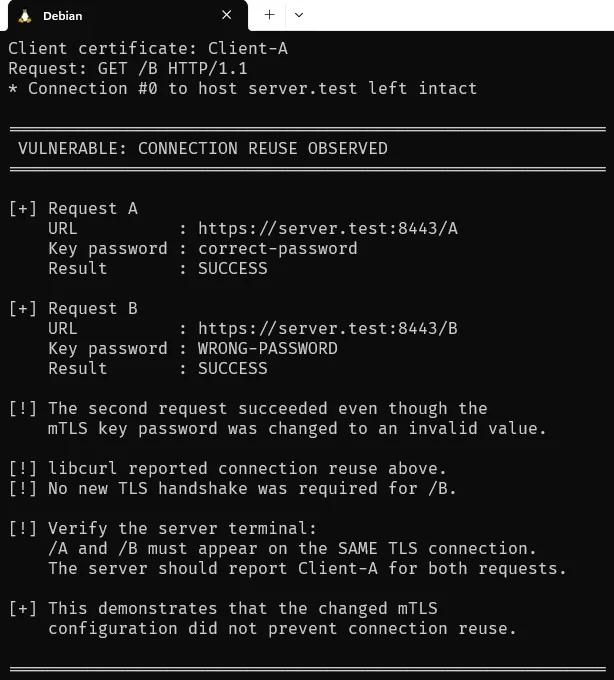 nimaarek/cve-2026-8932-poc
Proof-of-concept reproducing CVE-2026-8932, an incomplete mTLS configuration matching flaw in libcurl connection reuse, with a local lab server and C…
 virtualsamuraii/flyphish
Deploy a phishing infrastructure on the fly.
 baba01hacker666/cve-2026-33032
Python proof-of-concept for CVE-2026-33032 that inspects nginx status and configs, then demonstrates unauthorized config write with reload to deploy…
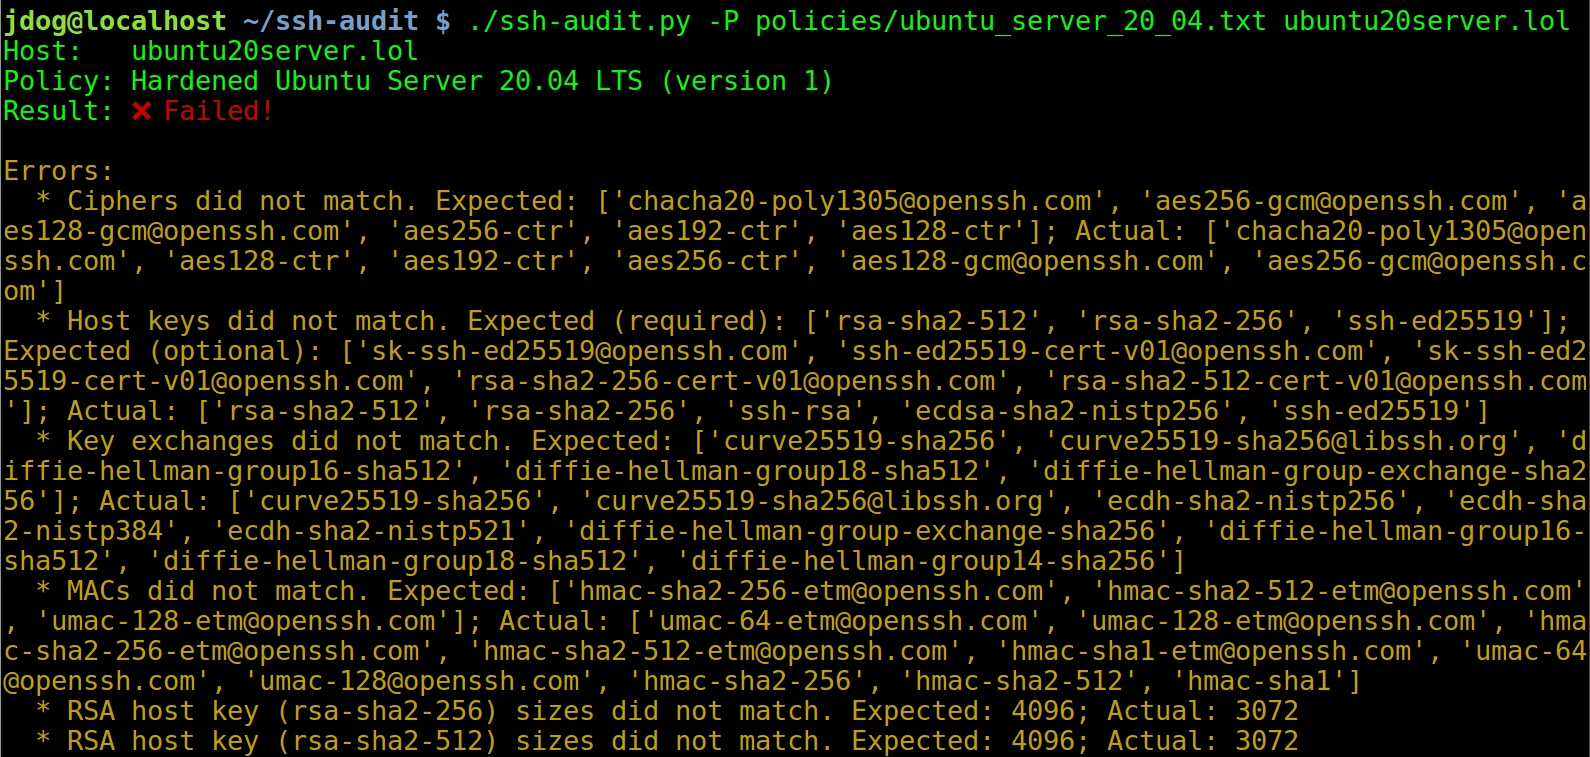 jtesta/ssh-audit
SSH server & client security auditing (banner, key exchange, encryption, mac, compression, compatibility, security, etc)
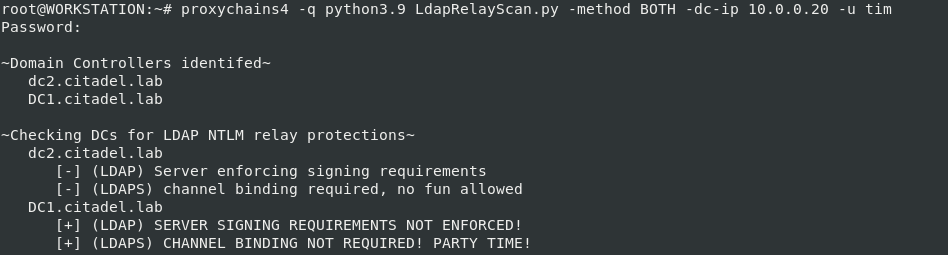 zyn3rgy/ldaprelayscan
Check for LDAP protections regarding the relay of NTLM authentication
 george0papasotiriou/cve-2026-22007-ntp-monlist-amplification-over-ipv6
Python PoC for CVE-2026-22007: NTP monlist amplification over IPv6, including a simulated vulnerable server and spoofed UDP reflection attack.
 blue0x1/sqlwinds
SQLWinds - SQL Server Security Assessment & Post-Exploitation Toolkit
 tevora-threat/rt_redirectors
Ansible role to configure redirectors for red team C2
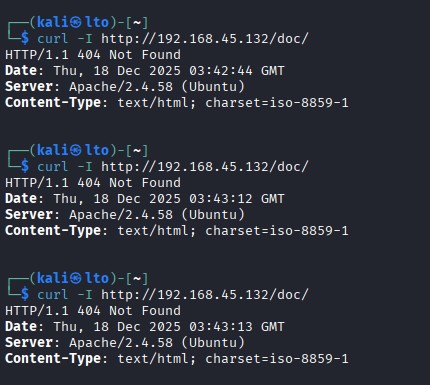 lto7777777/cve-1999-0678
CVE-1999-0678- /doc directory browsable
 slicingmelon/haproxy-cve-2023-45539-poc
HAProxy-CVE-2023-45539-PoC
 theorzr/ensimag-secu3a-cve-2024-22416
CVE-2024-22416 exploit experiments
 oscerd/cve-2026-40022
Reproducer for CVE-2026-40022: Apache Camel camel-platform-http-main authentication bypass on non-root context paths
 deepsecurityresearch/cve-2026-2586
Authenticated EL injection exploit for GlassFish/Payara admin console enabling remote command execution via crafted parameters in the virtual server…
 dahalsamir/cve-2026-23744-mcpjam-rce-exploit
This Python proof-of-concept targets a vulnerable MCP (Model Context Protocol) service exposed by the target application. The vulnerability allows an…
 xiaoxiaoranxxx/cve-2025-56815
Datart 1.0.0-rc.3 is vulnerable to Directory Traversal in the POST /viz/image interface, since the server directly uses MultipartFile.transferTo() to…
 nickguitar/drag-and-drop-multiple-file-uploader-pro-path-traversal
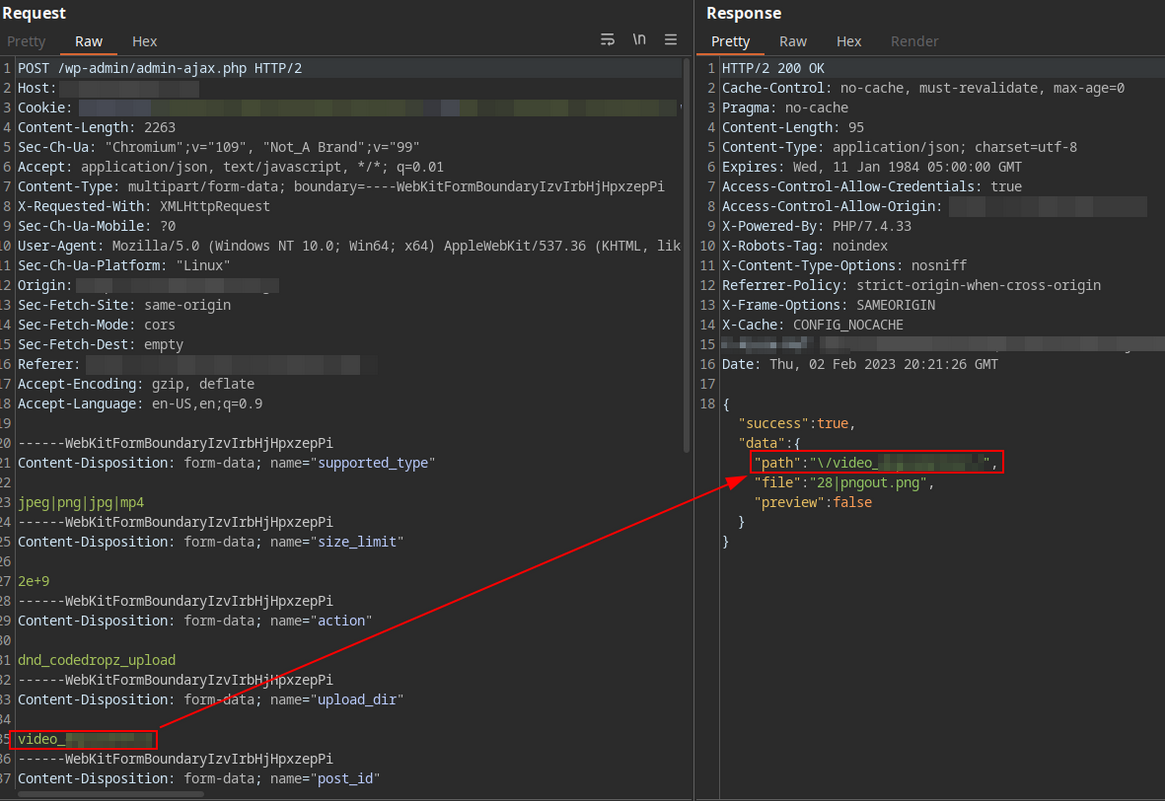
Drag and Drop Multiple File Uploader PRO - Contact Form 7 v5.0.6.1 Path Traversal (CVE-2023-1112)