
openmeetings-chat-user-idor
 abraxas/openmeetings-chat-user-idor
Apache OpenMeetings 9.1.0 - High - Remote - IDOR - dashboard chatTab-u{id} exports another users private chat
exploitationlabs-practicepenetration-testing+3
abraxas/openmeetings-chat-user-idorApache OpenMeetings 9.1.0 - High - Remote - IDOR - dashboard chatTab-u{id} exports another users private chat
 bignerd95/chimay-red
Working POC of Mikrotik exploit from Vault 7 CIA Leaks
 rushikesh-a-bhujbal/cve-2010-2075
UnrealIRCd 3.2.8.1 backdoor exploit — reverse shell via AB; trigger, built from scratch in Python using raw sockets. No Metasploit.
 anonmoty/xxstrike
XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.
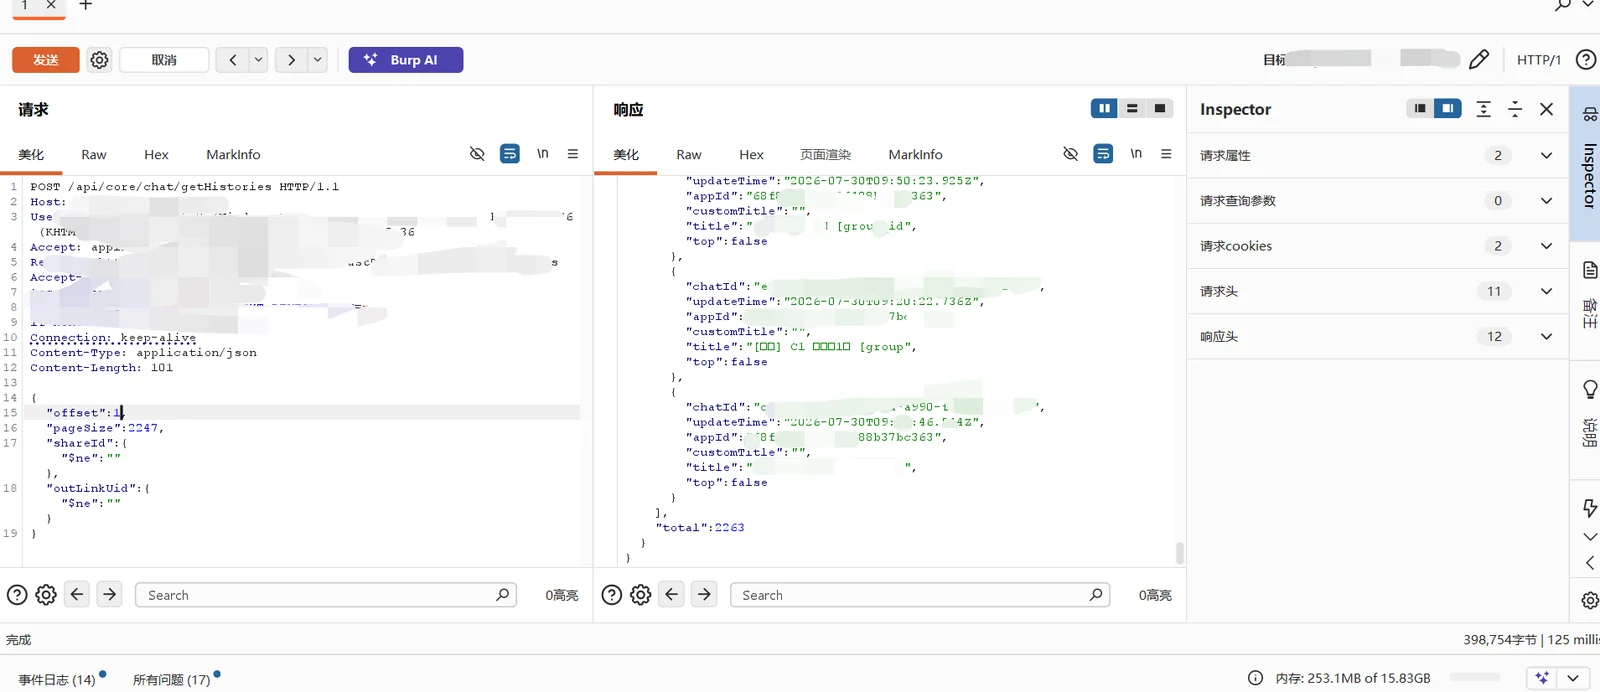 exploreio/cve-2026-79483-fastgpt-nosql-injection
Proof-of-concept for CVE-2026-79483, a NoSQL injection in FastGPT Community Edition allowing unauthenticated access to chat history titles. Includes…
 rudsarkar/cve-2026-42228
Proof-of-concept exploit for CVE-2026-42228, an unauthenticated chat execution hijacking vulnerability in n8n, with automated scanning and attack…
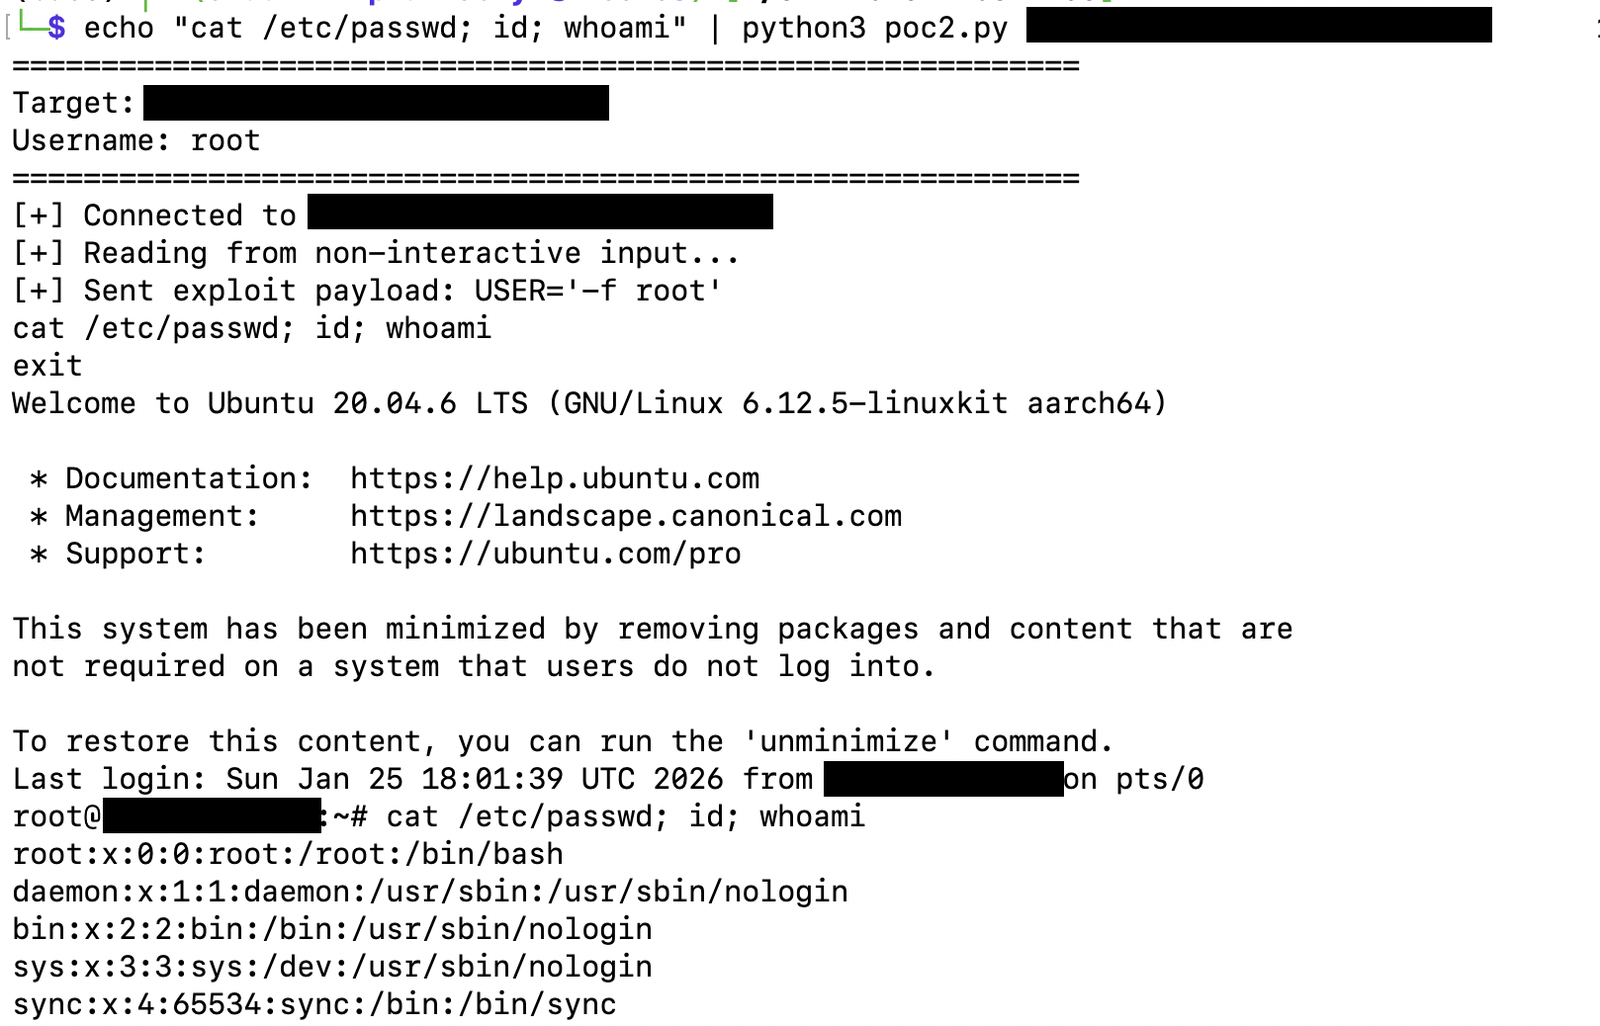 ms0x08-dev/cve-2026-24061-poc
Proof-of-concept exploit for CVE-2026-24061 providing an interactive remote shell session with configurable timeouts for reliable exploitation.
 wattocyber/lm-fingerprint
Fingerprint OpenAI-compatible LLMs from tokenizer and behavior signals.
 randomrobbiebf/woo
Exploit woocommerce SQLI and grab user and password hash
 theopaid/cve-2026-66749-unchecked-room-lookup-leads-to-server-crash-let-s-chat-
Security Advisory: Unchecked Room Lookup Leads to Server Crash (Let's Chat)
 shenhui35/redarrow
RedArrow3.2 是一款用于渗透测试ThinkPHP 5.0.23 远程命令执行漏洞(CVE-2018-20062)的图形化工具。
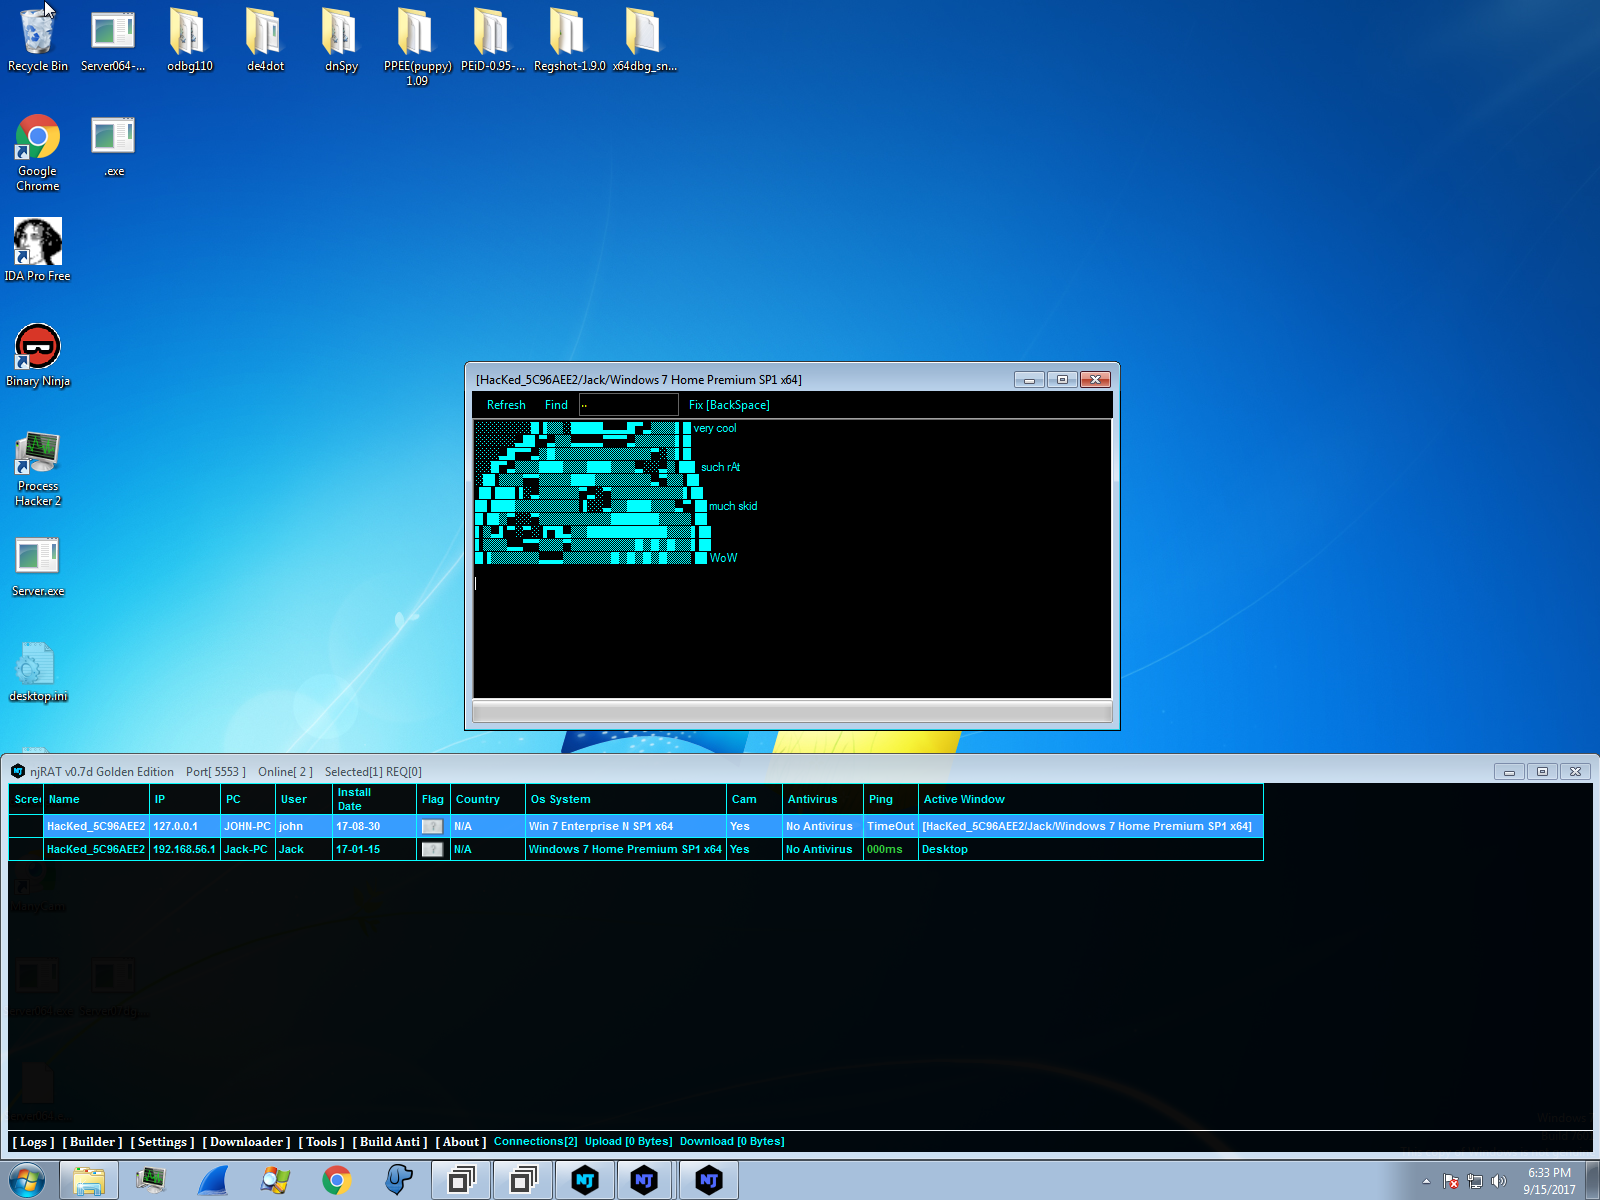 seep1959/njutils
A client and chat program for njrat 0.6.4, 0.7d, and 0.7d golden edition.
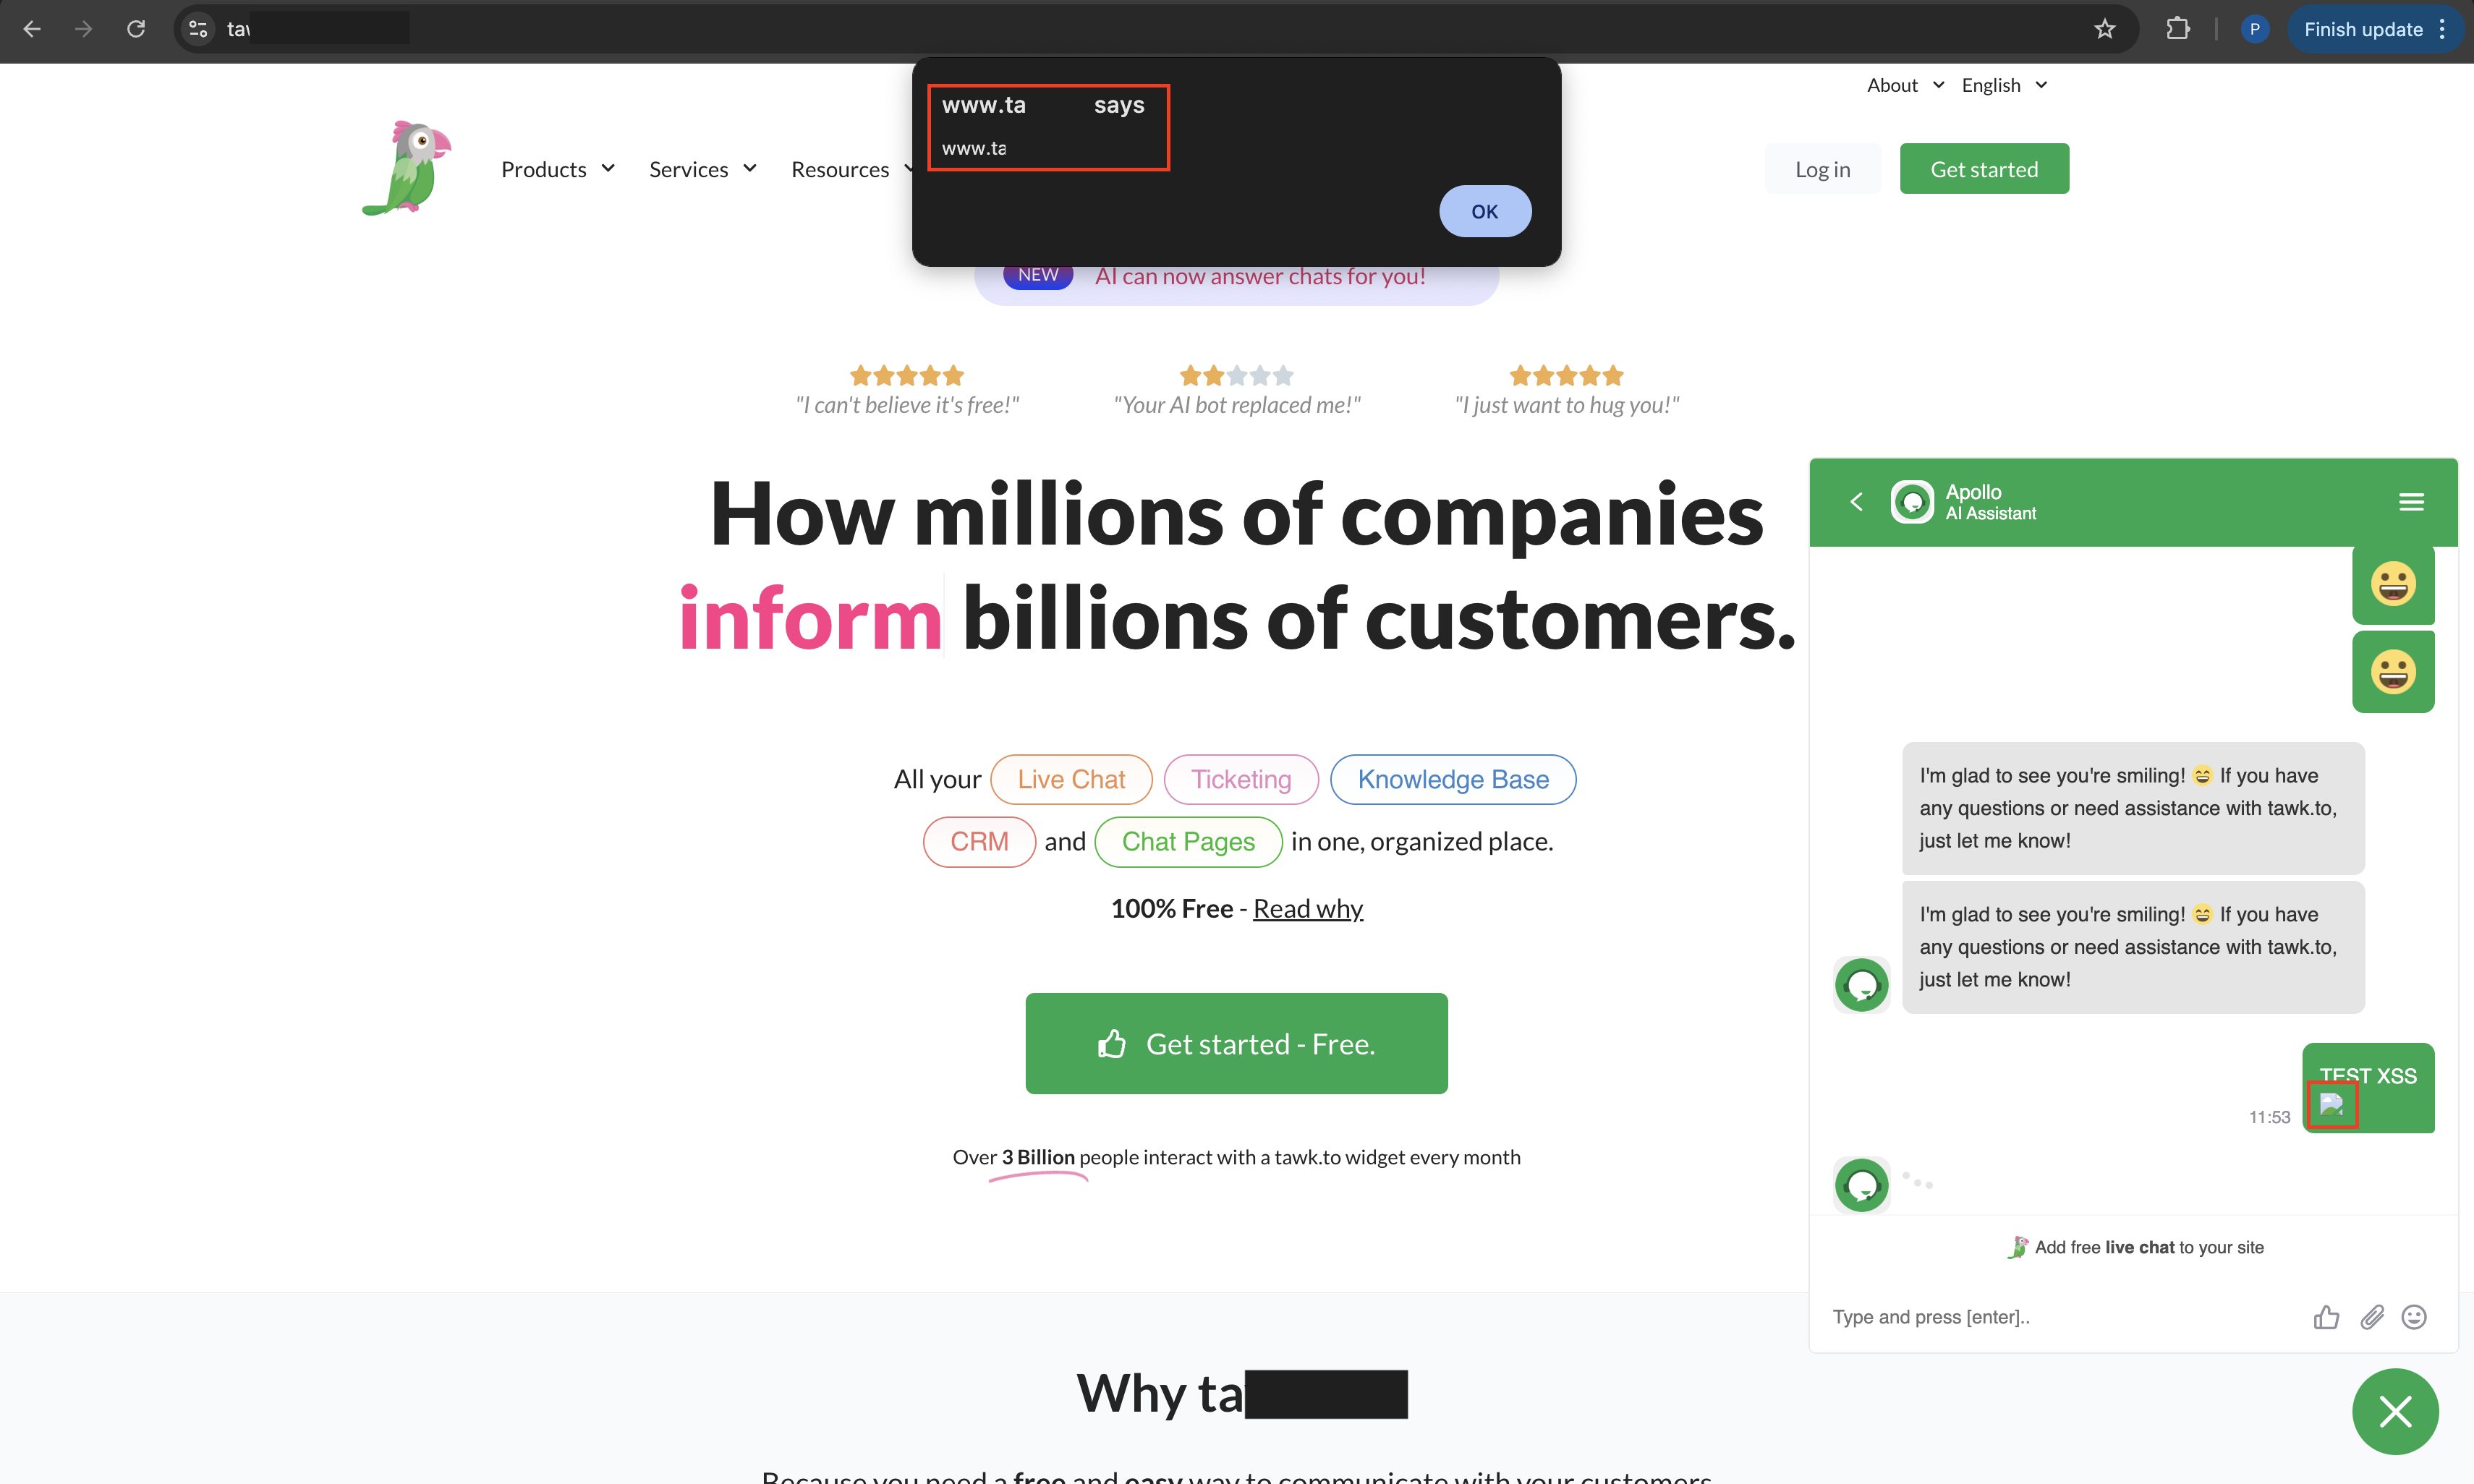 pracharapol/cve-2025-45960
Proof-of-concept for a stored cross-site scripting (XSS) vulnerability in tawk.to Live Chat 1.6.1, demonstrating JavaScript injection via unsanitized…
 nullbyte8080/cve-2026-36228
Proof-of-concept for CVE-2026-36228 demonstrating a denial-of-service vulnerability in Easy Chat Server 3.1 via oversized mtowho parameter. Dry-run…
 nullbyte8080/cve-2026-36227
Benign proof-of-concept for CVE-2026-36227, a path traversal vulnerability in Easy Chat Server 3.1 user registration. Demonstrates unauthorized file…
 kov404/cve-2025-56515
Cross-Site Scripting (XSS) Vulnerability in Fiora Chat Application
 kov404/cve-2025-56514
Cross Site Scripting (XSS) Vulnerability in Fiora Chat Application
 vulncheck-oss/cve-2025-0364
CVE-2025-0364: BigAnt Server RCE Exploit