

DakshSCRA
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
code-analysisdevsecopseducation+7
45
coffeeandsecurity/dakshscraFramework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
 fankh/vulnerability-poc
CVE proof-of-concept labs, exploit scripts, and detection/prevention rules (Nginx, Apache, Snort, YARA) for high-severity CVEs. Authorized security…
 praetorian-inc/titus
High-performance secrets scanner. CLI, Go library, Burp Suite extension, and Chrome extension. 487 detection rules with live credential validation.
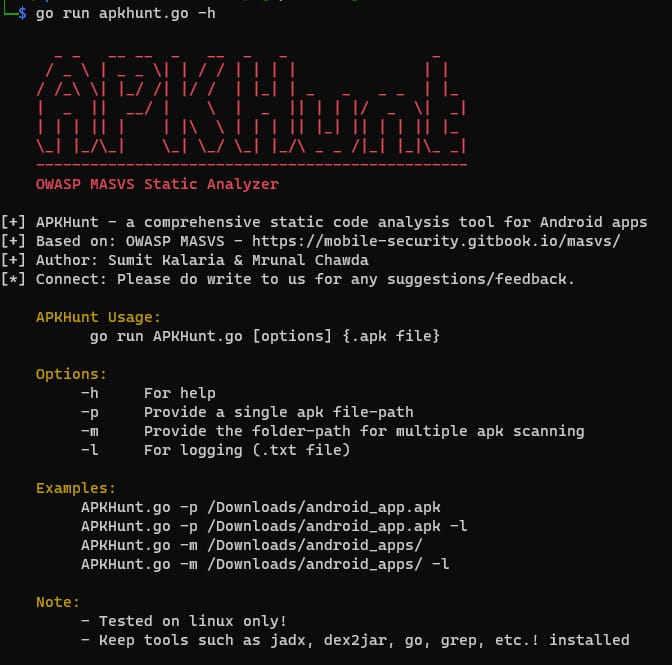 cyber-buddy/apkhunt
Static code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…
 jhatchi/nexacorp-dfir-inc-2026-001
DFIR investigation + 7 Suricata rules on a simulated NexaCorp intrusion (vsftpd 2.3.4 CVE-2011-2523 + MITRE Caldera C2). 4-day solo engagement…
 vulncheck-oss/initial-access-community
Go-based exploits for unauthenticated network vulnerabilities in routers, VPNs, appliances, and IoT, bundled with PCAPs, Suricata/Snort/YARA/Sigma…
 luemmelsec/cve-2023-29357
C# proof-of-concept exploit for CVE-2023-29357 targeting SharePoint, with YARA detection rules and detailed usage instructions for security testing.