
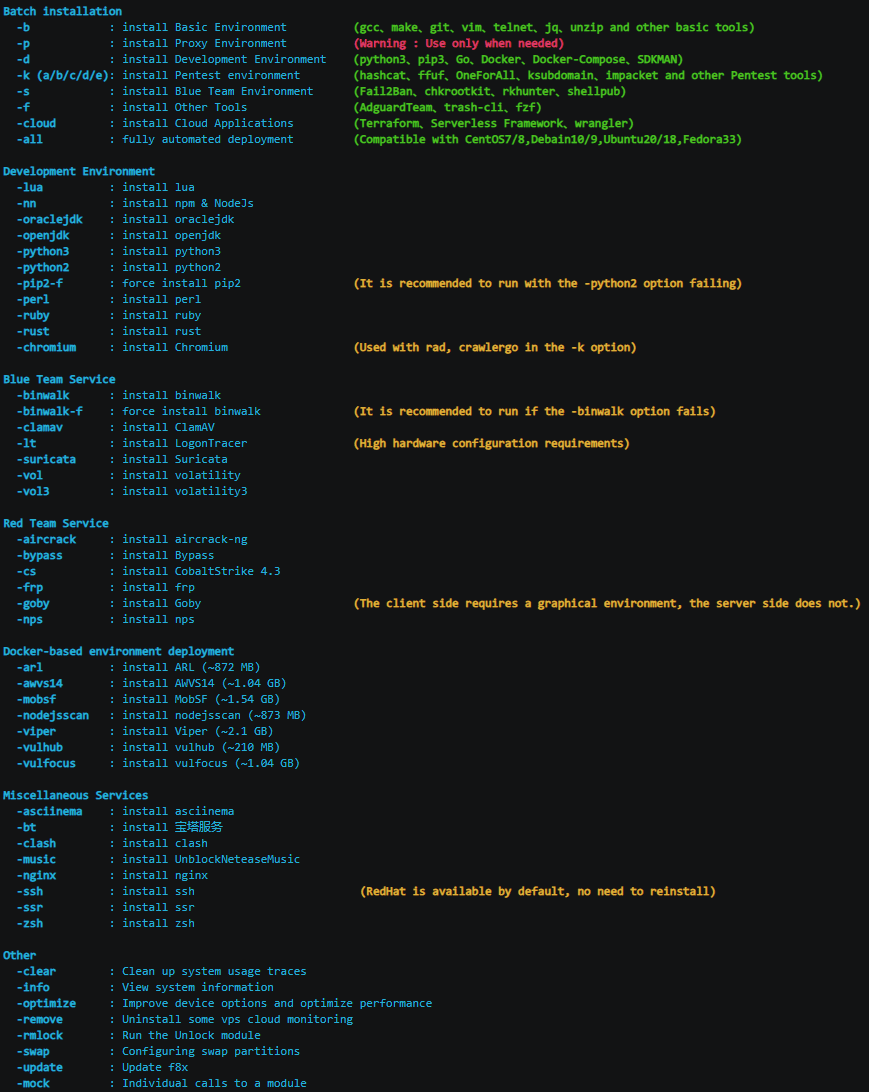
f8x
 ffffffff0x/f8x
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool
cloud-securityctfdevsecops+7
ffffffff0x/f8x红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool
 w4r10ck423/envvisualizer
Parse and visualize /proc/self/environ on compromised Linux boxes — categorizes env vars by tech stack (AWS, Django, Rails, NodeJS, MySQL, K8s,…
 owasp/railsgoat
A vulnerable version of Rails that follows the OWASP Top 10
 duriantaco/ravage
Evidence first autonomous web security testing for controlled, authorized targets. With reproducible labs, audit trails, reports, and XBEN…
 pentestgeek/phishing-frenzy
Ruby on Rails Phishing Framework
 0x00-0x00/cve-2015-3224
Modification of Metasploit module for RCE in Ruby-On-Rails Console CVE-2015-3224
 adversarial-detection-engineering/adversarial-detection-engineering-framework
A framework and taxonomy for identifying, classifying, and reasoning about detection logic bugs in SIEM, EDR, and XDR rules, with concrete examples…
 cliffe/breakescape
Mountable Rails engine providing 24+ cybersecurity escape room scenarios with randomized passwords, JIT-compiled NPC dialogue, and RESTful API for…
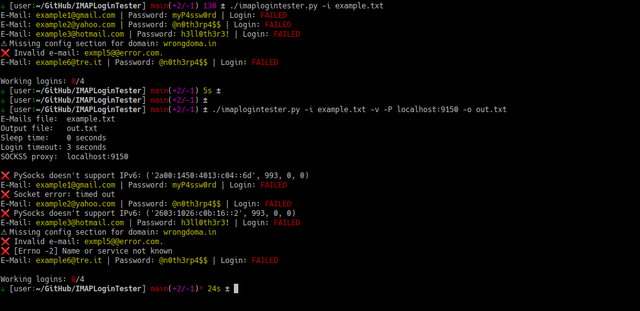 rm1984/imaplogintester
A simple Python script that reads a text file with lots of e-mails and passwords, and tries to check if those credentials are valid by trying to…
 cherrling/cve-2025-56499
Proof-of-concept exploit for CVE-2025-56499, demonstrating arbitrary file read via missing path validation in mihomo's rule-provider configuration,…
 decoder-it/printerbugnew
The DCERPC only printerbug.py version
 mrtiz/cve-2020-0688
Remote Code Execution on Microsoft Exchange Server through fixed cryptographic keys
 remenis/cve-2025-67158
Revotech I6032W-FHW IP camera firmware fails to validate authentication fields in API requests, allowing attackers to bypass authentication and…
 hackspeak/cve-2026-66066
CVE-2026-66066 (KindaRails2Shell) PoC - Rails Active Storage/libvips arbitrary file read to RCE; for authorized security testing
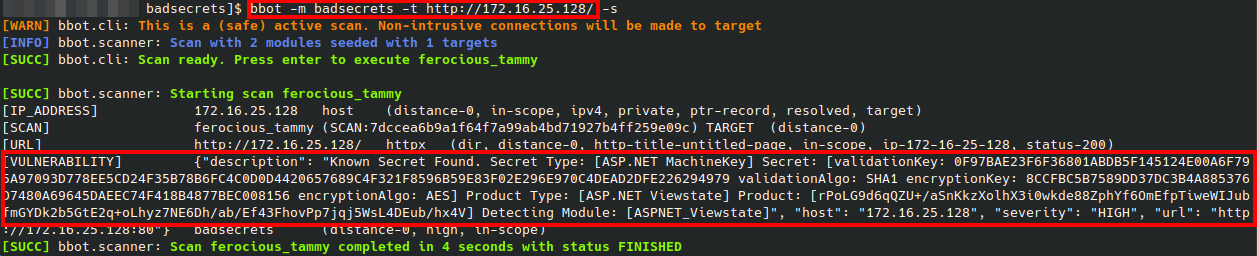 blacklanternsecurity/badsecrets
A library for detecting known secrets across many web frameworks
 shinthink/cve-2026-66066
CVE-2026-66066 — KindaRails2Shell: Rails Active Storage/libvips Arbitrary File Read → RCE. MATLAB/HDF5 dual-identity file → SECRET_KEY_BASE theft →…
 sharma19d/cve-2025-61148
The vulnerability exists in the Student Payment API. The application fails to properly validate whether the user requesting a receipt is authorized…
