

MSSQLand
 n3rada/mssqland
In-target C# post-exploitation and exploitation tool for Microsoft SQL Server (MS SQL / MSSQL) traversing linked-server chains of any depth with…
configuration-auditingdatabase-securityimpersonation-tools+6
75
n3rada/mssqlandIn-target C# post-exploitation and exploitation tool for Microsoft SQL Server (MS SQL / MSSQL) traversing linked-server chains of any depth with…
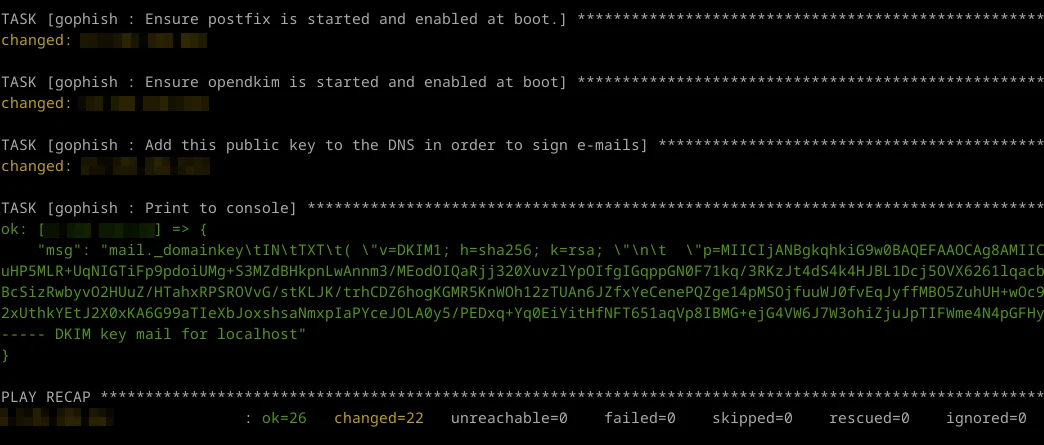 virtualsamuraii/flyphish
Deploy a phishing infrastructure on the fly.
 netspi/powerupsql
PowerUpSQL: A PowerShell Toolkit for Attacking SQL Server
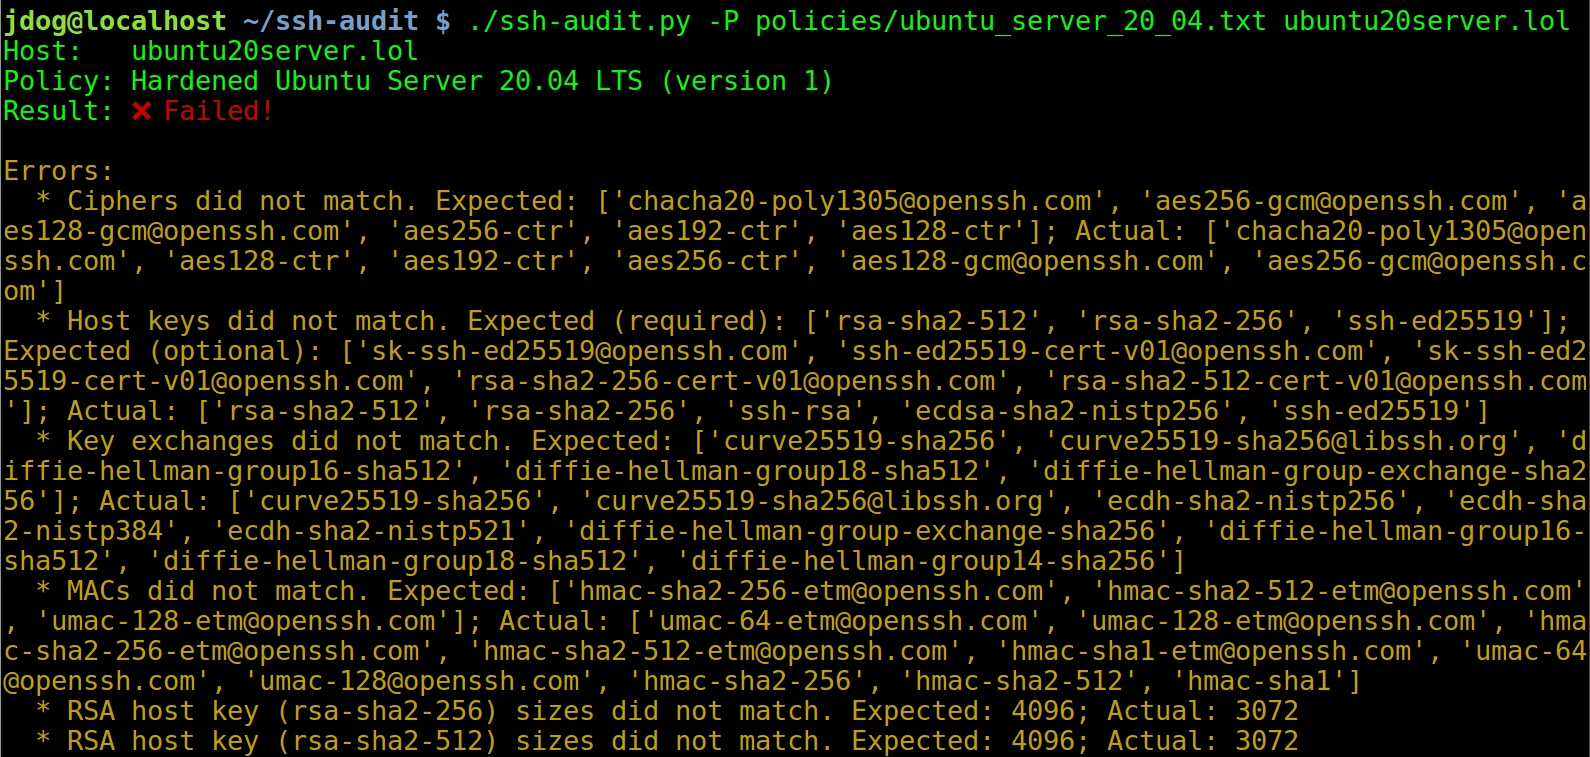 jtesta/ssh-audit
SSH server & client security auditing (banner, key exchange, encryption, mac, compression, compatibility, security, etc)
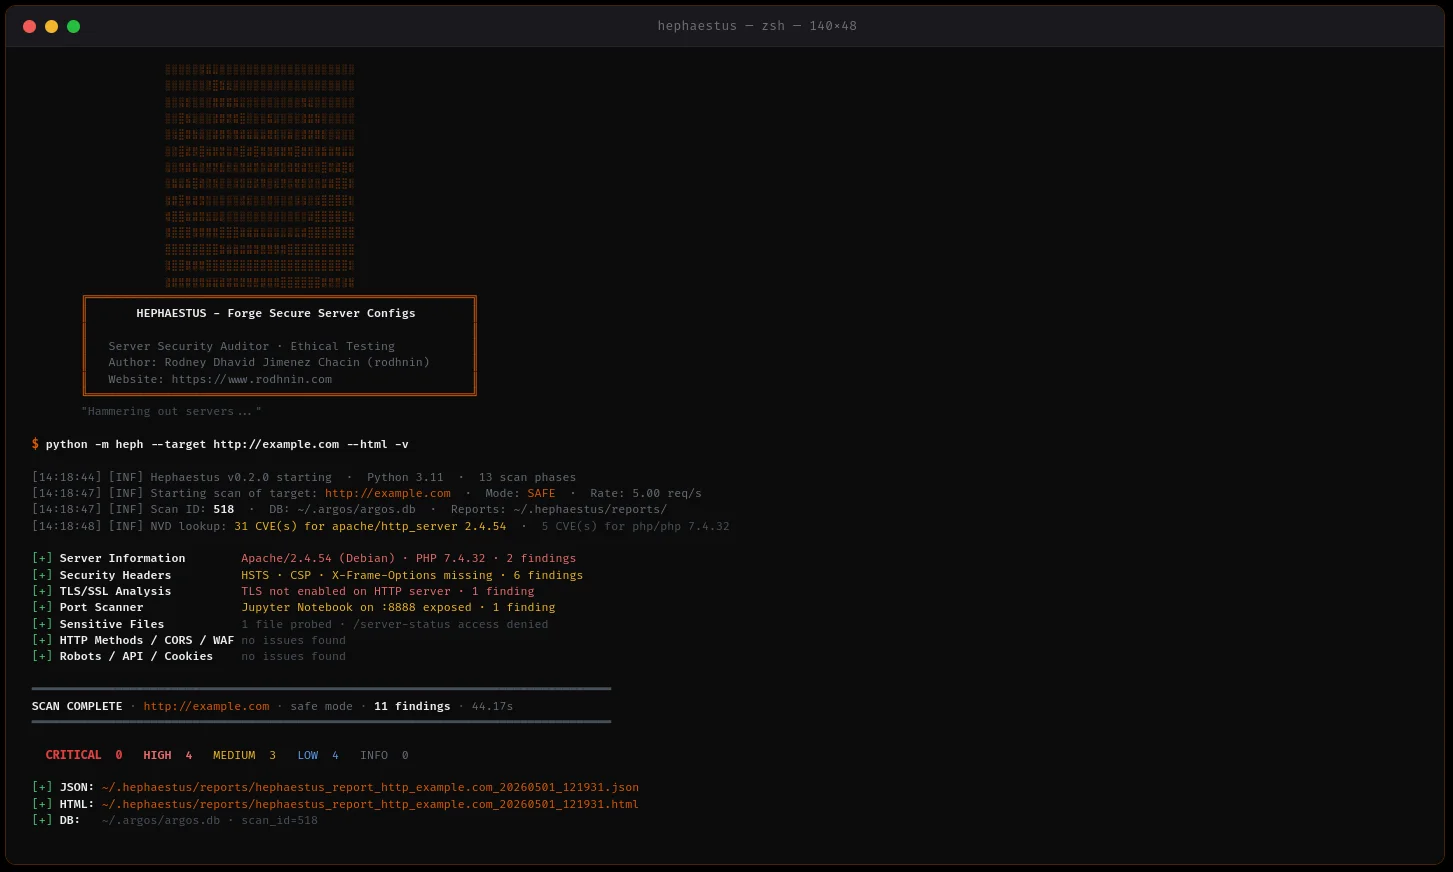 rodhnin/hephaestus-server-forger
server security auditor scanning Apache, Nginx, and IIS configurations with AI-powered hardening guides and professional reporting.
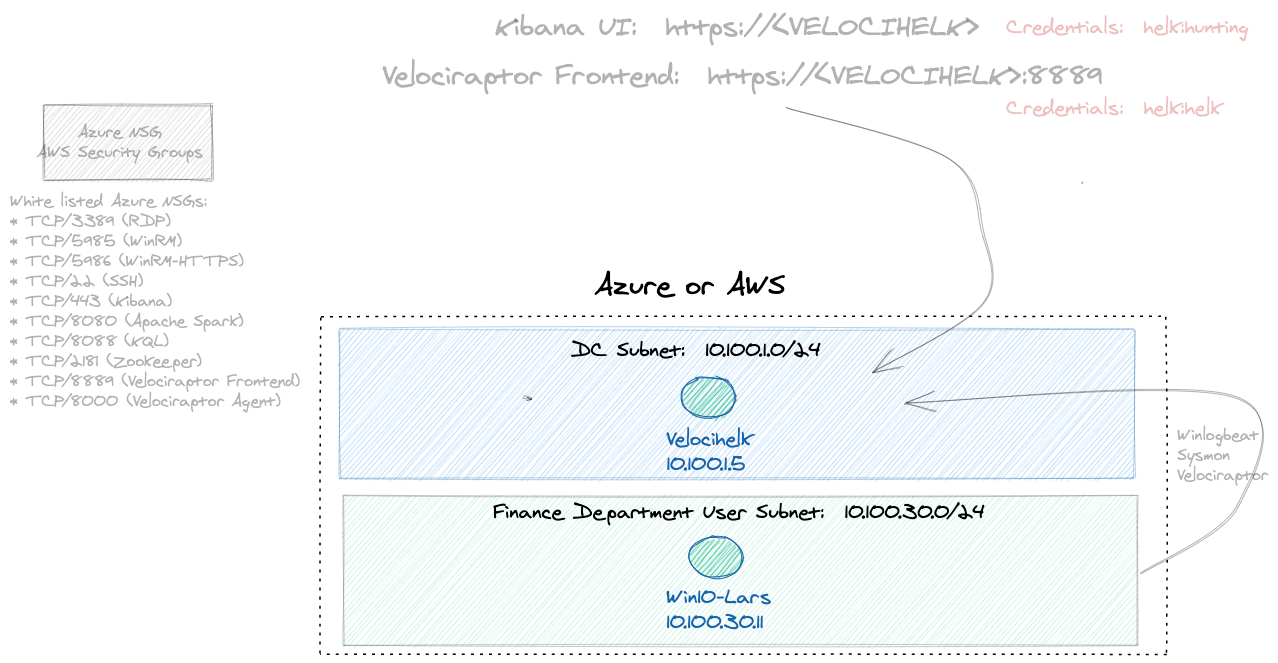 iknowjason/bluecloud
Cyber Range including Velociraptor + HELK system with a Windows VM for security testing and R&D. Azure and AWS terraform support.
 tls-attacker/tls-scanner
Automated TLS server and client configuration scanner for pentesters and researchers. Evaluates cipher suites, protocol versions, and security…
 baba01hacker666/cve-2026-33032
Python proof-of-concept for CVE-2026-33032 that inspects nginx status and configs, then demonstrates unauthorized config write with reload to deploy…
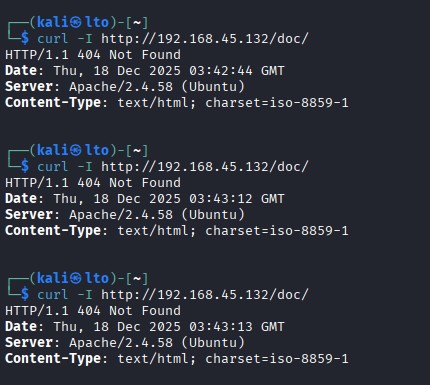 lto7777777/cve-1999-0678
CVE-1999-0678- /doc directory browsable
 blue0x1/sqlwinds
SQLWinds - SQL Server Security Assessment & Post-Exploitation Toolkit
 george0papasotiriou/cve-2026-22007-ntp-monlist-amplification-over-ipv6
Python PoC for CVE-2026-22007: NTP monlist amplification over IPv6, including a simulated vulnerable server and spoofed UDP reflection attack.
 oscerd/cve-2026-40022
Reproducer for CVE-2026-40022: Apache Camel camel-platform-http-main authentication bypass on non-root context paths
 12345qwert123456/cve-2021-41773
Vulnerable configuration Apache HTTP Server version 2.4.49
 immunit/cve-2018-11759
Proof-of-concept exploit for CVE-2018-11759 demonstrating Apache mod_jk access bypass via specially crafted requests to bypass reverse proxy…
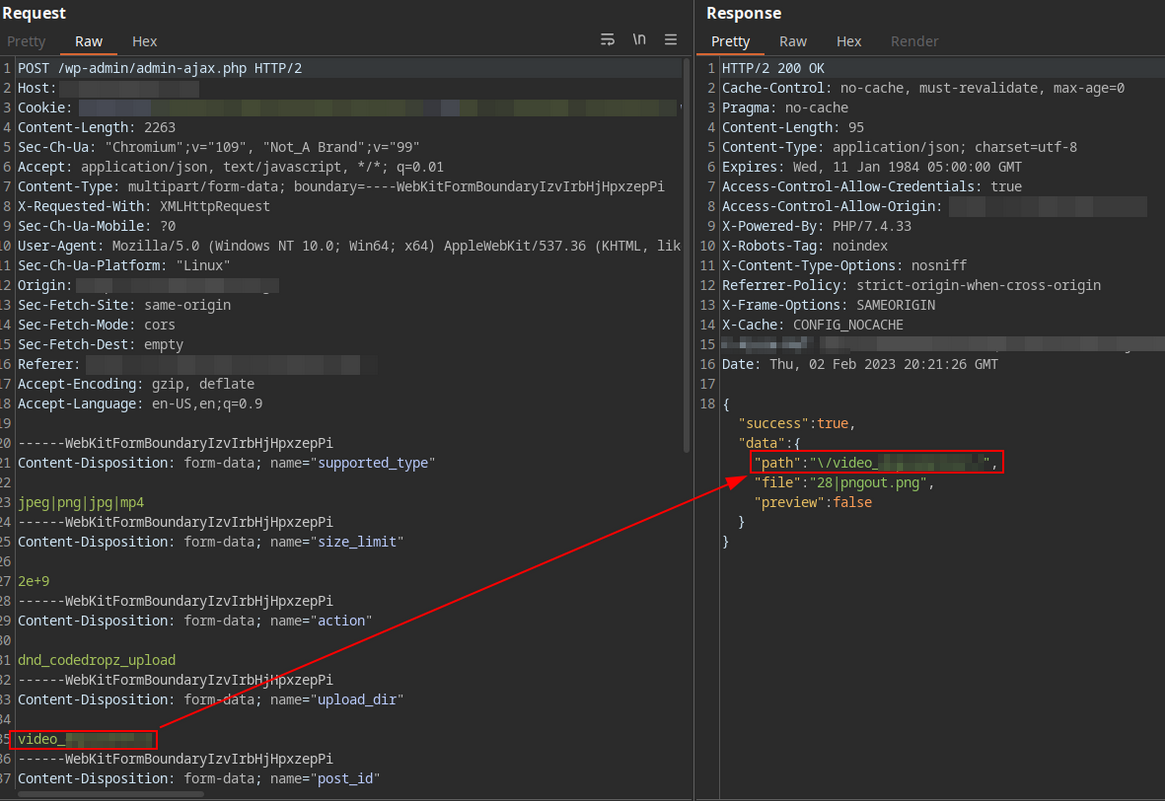 nickguitar/drag-and-drop-multiple-file-uploader-pro-path-traversal
Drag and Drop Multiple File Uploader PRO - Contact Form 7 v5.0.6.1 Path Traversal (CVE-2023-1112)
 deepsecurityresearch/cve-2026-2586
Authenticated EL injection exploit for GlassFish/Payara admin console enabling remote command execution via crafted parameters in the virtual server…
 jdormannn/secureops-lab
Performed a live cybersecurity assessment on a university Linux server. During analysis, active attack activity was identified, including brute-force…