

SecretSifter
 owasp/secretsifter
OWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).
ai-securityapi-securitydefensive-tools+7
5
owasp/secretsifterOWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).
 qeeqbox/social-analyzer
API, CLI, and Web App for analyzing and finding a person's profile in 1000 social media \ websites
 juice-shop/juice-shop
Intentionally vulnerable web application covering OWASP Top 10 vulnerabilities for security training, CTF competitions, and penetration testing…
 ahmadhassan-bted/silentsniffer
A professional, high-fidelity de-anonymization and vulnerability diagnostic framework. Features a zero-coupling modular architecture for…
 hilmiazizi/oorecon
Terminal UI for attack surface discovery: DNS recon, subdomain enumeration, port scanning, reverse IP, leaked login URLs, and JavaScript secret…
 ambitsecurity/jshound
Find every API request a web app makes, from the JavaScript it ships: method, URL, body, headers and GraphQL operations. One command.
 bfdfhdsfdd-crypto/cve-2026-22444
Exploit for Apache Solr CVE-2026-22444, leveraging UNC path injection and SMB server to achieve remote code execution via malicious configset and…
 learningdisordercapital35/cve_2025_24257----not-mine
Demonstrate CVE-2025-24257 with a public PoC for IOGPUFamily kernel heap OOB read/write and panic analysis
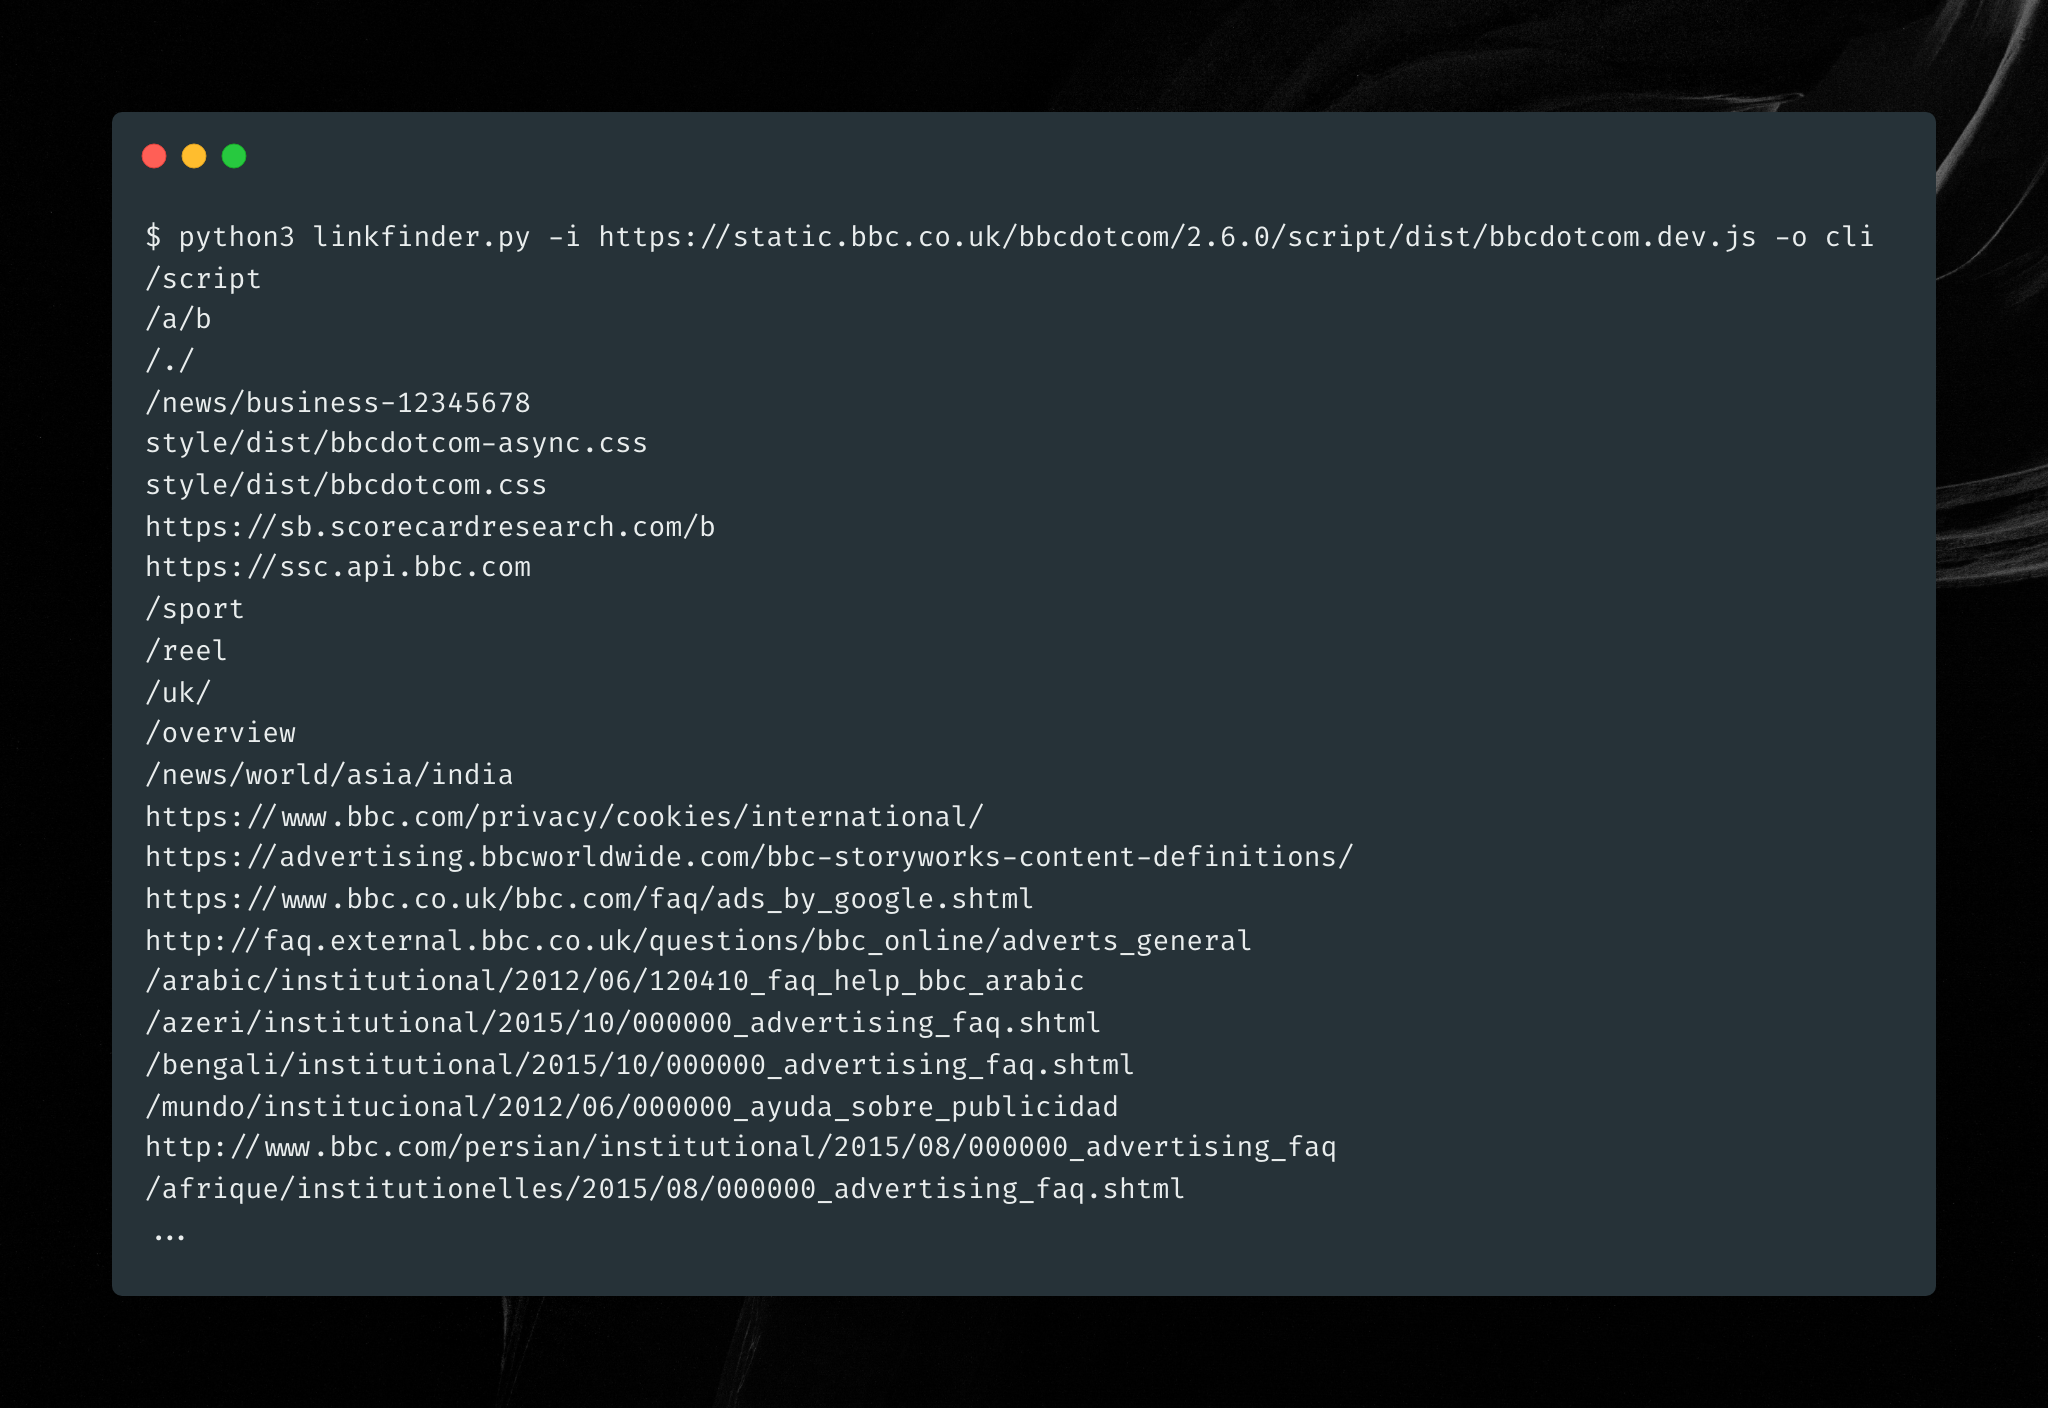 gerbenjavado/linkfinder
A python script that finds endpoints in JavaScript files
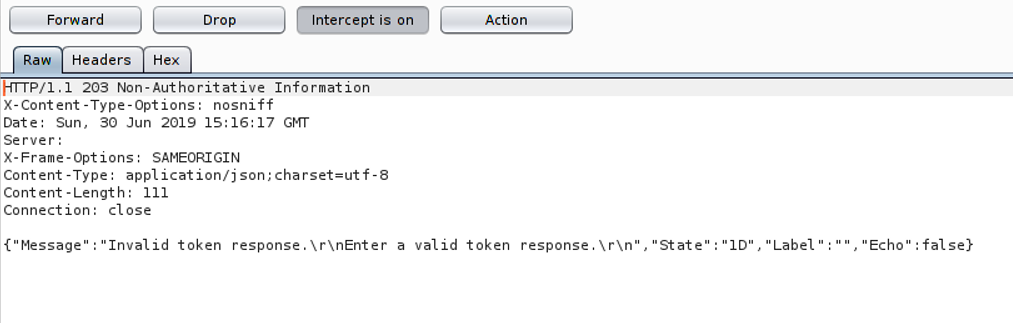 furqankhan1/cve-2019-13496
Proof-of-concept exploit demonstrating OTP bypass in One Identity Cloud Access Manager 8.1.3 via MITM/SSL-strip, SAML response replay, and injected…
 hakluke/hakrawler
Simple, fast web crawler designed for easy, quick discovery of endpoints and assets within a web application
 ahrixia/cve-2024-57428
CVE-2024-57428: PHPJabbers Cinema Booking System v2.0 suffers from stored XSS, enabling persistent JavaScript injection for phishing and malware…
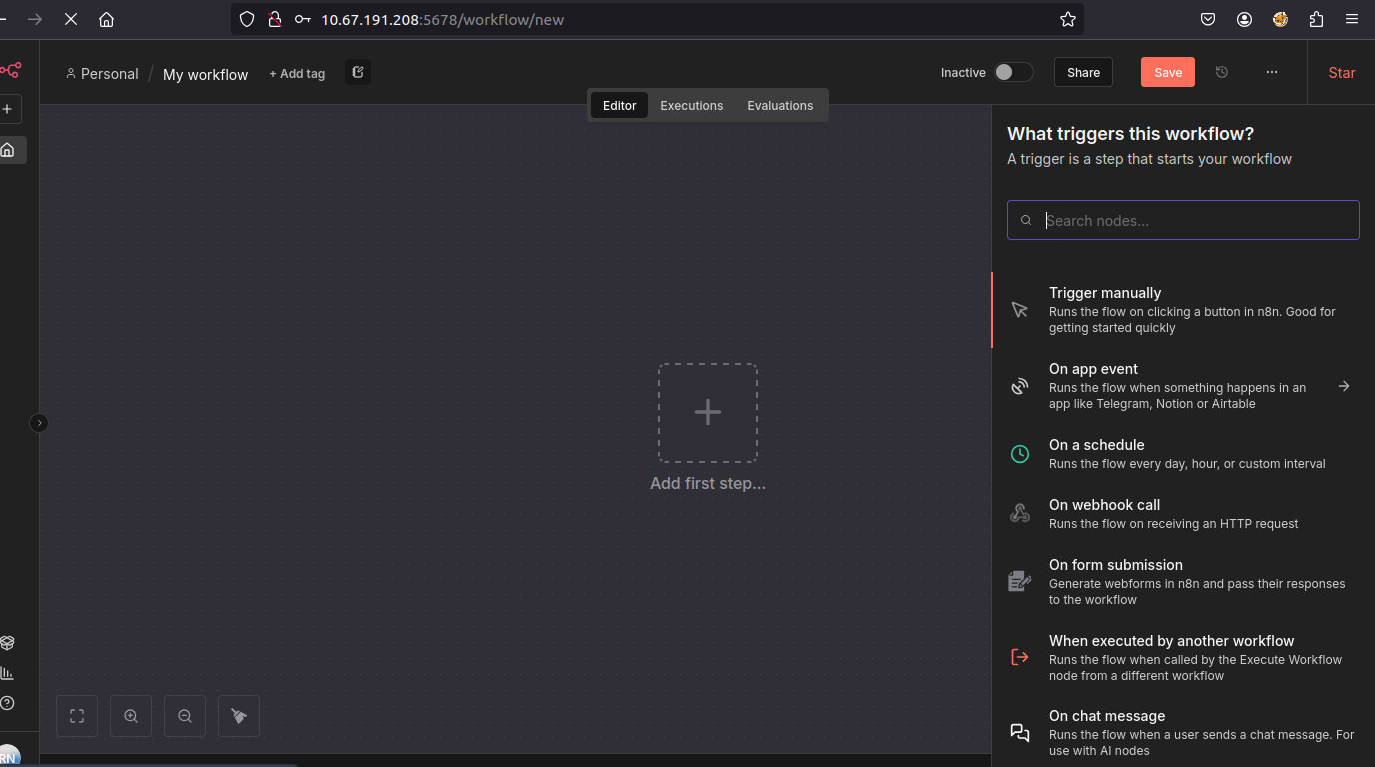 rianjuniorsf/analysis-and-poc-n8n-cve-2025-68613
Technical study of the CVE-2025-68613 vulnerability in n8n, covering affected versions, laboratory exploration scenario, offensive and defensive…
 arachni/arachni
Web Application Security Scanner Framework
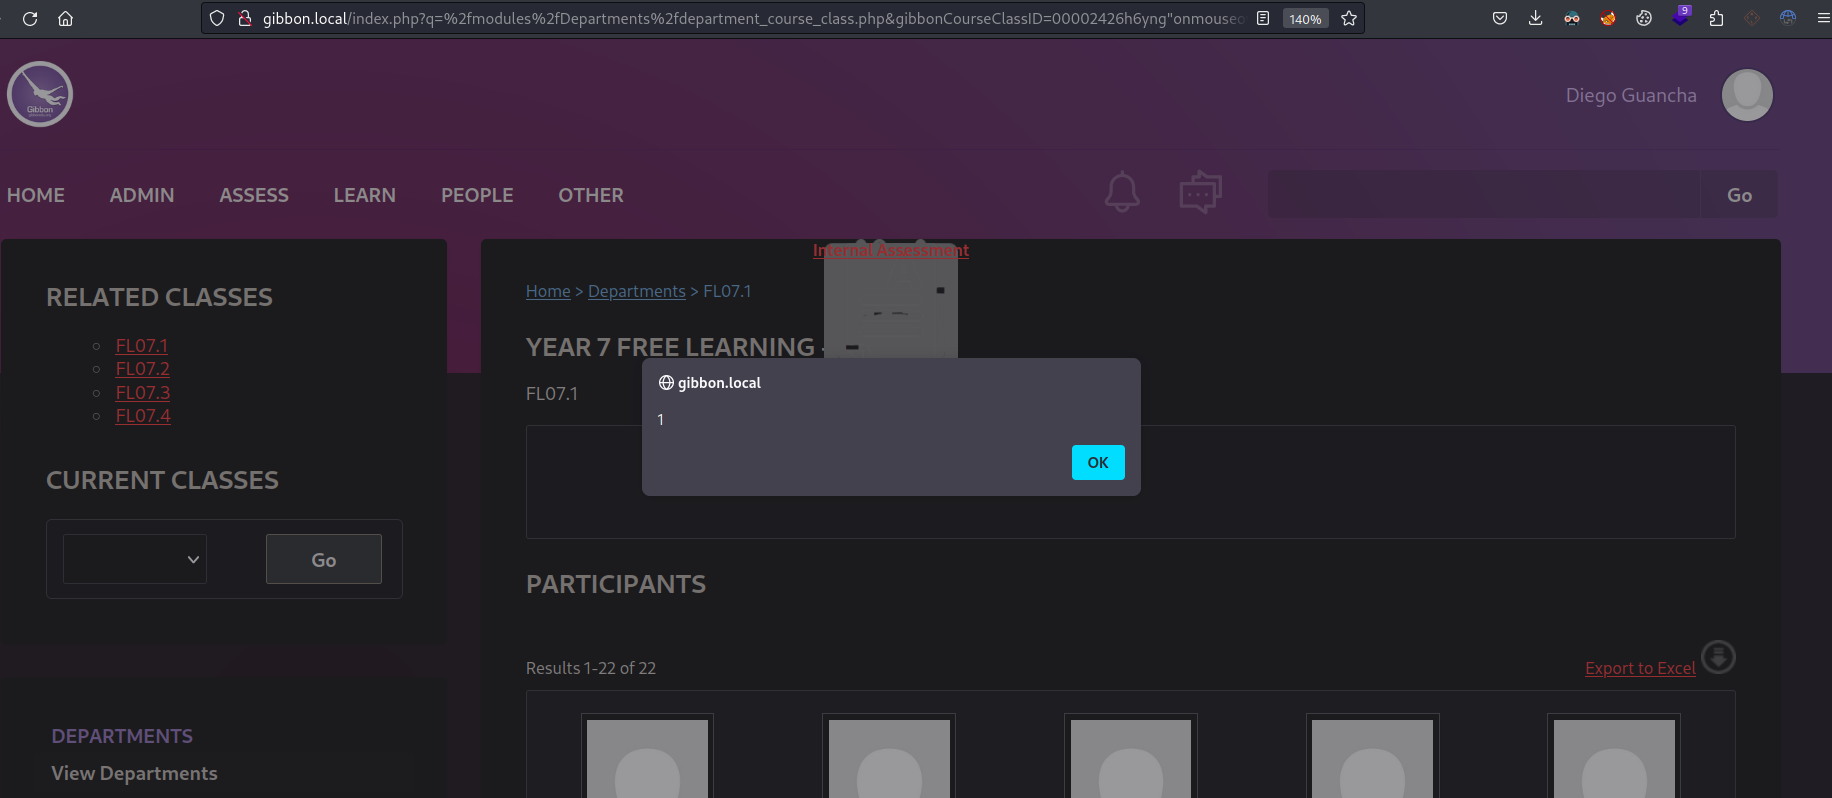 maddsec/cve-2023-34599
Multiple Cross-Site Scripting (XSS) vulnerabilities have been identified in Gibbon v25.0.0, which enable attackers to execute arbitrary Javascript…
 alt3kx/cve-2019-10685
A Reflected Cross Site Scripting (XSS) Vulnerability was discovered in Print Archive System v2015 release 2.6
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 soy-oreocato/cve-2023-46998
Proof-of-concept exploit for a stored/reflected Cross-Site Scripting (XSS) vulnerability in Bootbox.js versions 3.2 through 6.0, allowing remote…