
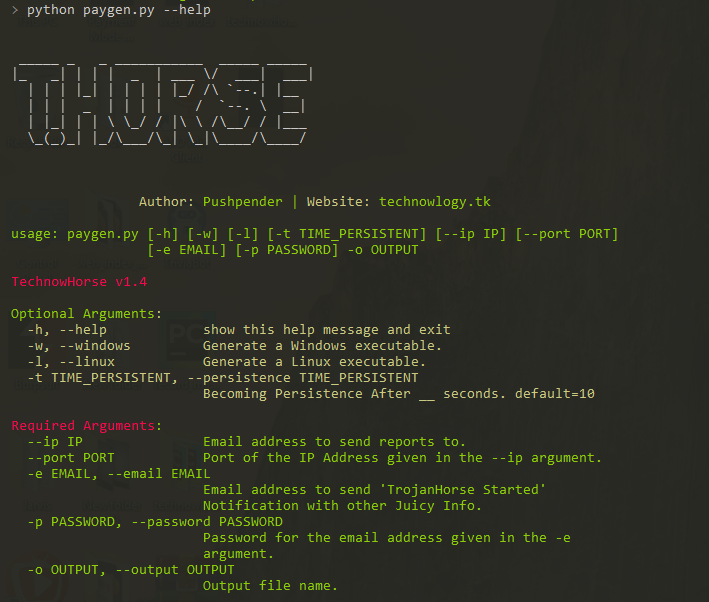
thorse
 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
anti-botcommand-and-controlexploit-frameworks+6
614
pushpenderindia/thorseTHorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
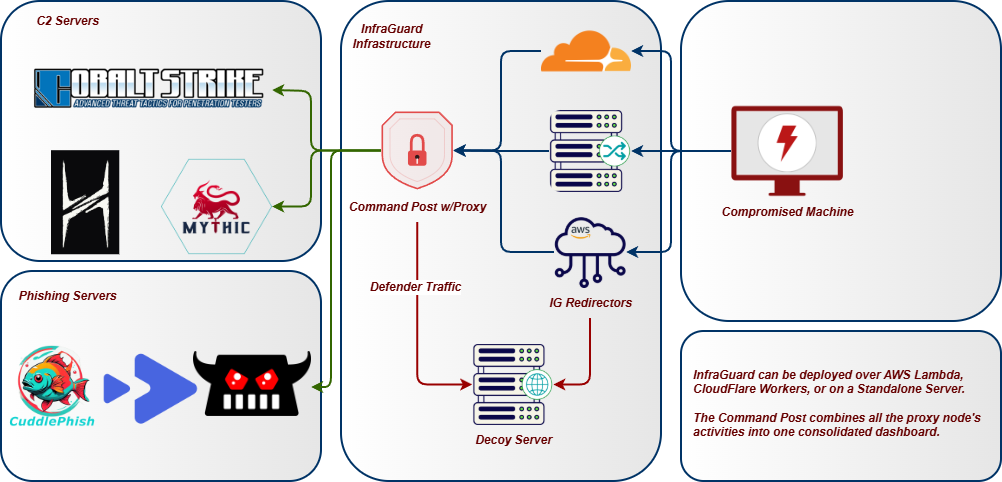 whispergate/infraguard
InfraGuard is a Command & Control Redirection Proxy and Manager which protects your Red Team Infrastructure against threat attribution
 aaaddress1/skrull
Generates anti-copy malware launchers using Process Ghosting to bypass AV/EDR signature scanning and prevent automatic sample submission. Supports…
 longwayhomie/polyengine
PolyEngine is an evasive PE packer designed for CTF challenges and low-level Windows security education. It focuses on bypassing EDR and AV…
 cryst4linqq/turkorat
Fully undetected grabber (grabs wallets, passwords, cookies, modifies discord client etc.)
 secretsquirrel/recomposer
Randomly changes Win32/64 PE Files for 'safer' uploading to malware and sandbox sites.
 billythegoat356/kramer
The next level 100% Python obfuscator.
 rek7/postshell
PostShell - Post Exploitation Bind/Backconnect Shell
 rek7/ddoor
DDoor - cross platform backdoor using dns txt records
 mephistolist/soviet
A Runtime Crypter in C for Linux ELF binaries.
 d4vinci/dr0p1t-framework
A framework that create an advanced stealthy dropper that bypass most AVs and have a lot of tricks
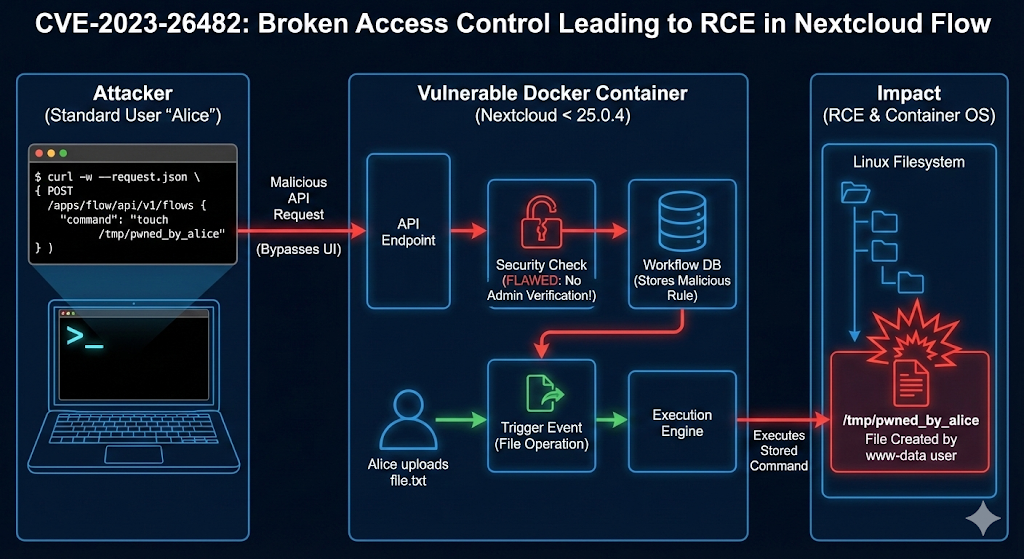 isabbii/poc---cve-2023-26482-rce-lab-nextcloud
Docker-based lab reproducing CVE-2023-26482 (Nextcloud RCE) with automated exploit script for educational vulnerability analysis and exploitation…
 theinterception/log4j-simulation-tool
Vulnerability analysis, patch management and exploitation tool forCVE-2021-44228 / CVE-2021-45046 / CVE-2021-4104
 nullarray/autosploit
Automated Mass Exploiter
 jonathansalwan/ropgadget
Search for ROP gadgets in ELF, PE, Mach-O, and Raw binaries across x86, ARM, MIPS, and RISC-V architectures. Supports automated ROP chain generation…
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
 jack-new-project/zeebsploit
Modular exploitation framework for penetration testing, featuring automated payload generation, reconnaissance modules, and post-exploitation…
 cyb0r9/androspy
Automated Android backdoor generator with crypter, IP poisoning, and Metasploit payload integration for penetration testing and red team operations.