

 haxorstars/cve-2025-54068
A tool designed to exploit CVE-2025-54068 and Remote Command Execution of the Livewire project.

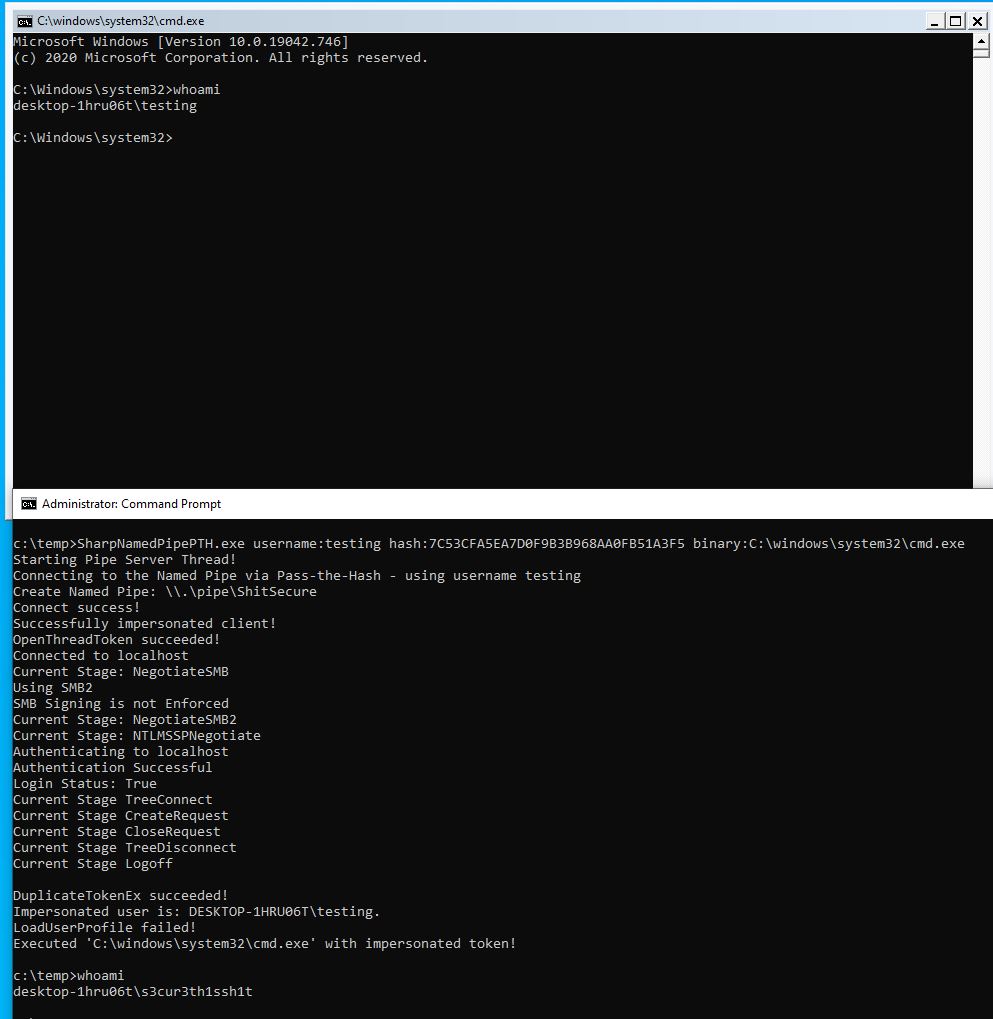 s3cur3th1ssh1t/sharpnamedpipepth
Pass the Hash to a named pipe for token Impersonation
 synacktiv/livepyre
A tool designed to exploit CVE-2025-54068 and Remote Command Execution if the APP_KEY of the Livewire project is known.
 technicalcorp0/cve-2023-38831-exploit
This project contains a Python script that exploits **CVE-2023-38831**, a vulnerability in **WinRAR** versions prior to 6.23. The exploit generates a…
 yora1928/cve-2026-48908-by-yora
Passive security checker for CVE-2026-48908 affecting SP Page Builder.
 cobbr/elite
Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…
 bc-security/ironsharppack
IronSharpPack is a repo of popular C# projects that have been embedded into IronPython scripts that execute an AMSI bypass and then reflective load…
 maldevel/gdog
A fully featured Windows backdoor that uses Gmail as a C&C server
 octoberfest7/xll_phishing
XLL Phishing Tradecraft
 mtaha-sec/bash-apocalypse
Recreating Shellshock (CVE-2014-6271) - the bash vulnerability that endangered millions of servers. Automated exploitation toolkit + Burp Suite…
 frkngksl/shoggoth
Polymorphic encryptor that transforms shellcode, PE, and COFF files into obfuscated, position-independent payloads with RC4 and random block cipher…
 frkngksl/hintinject
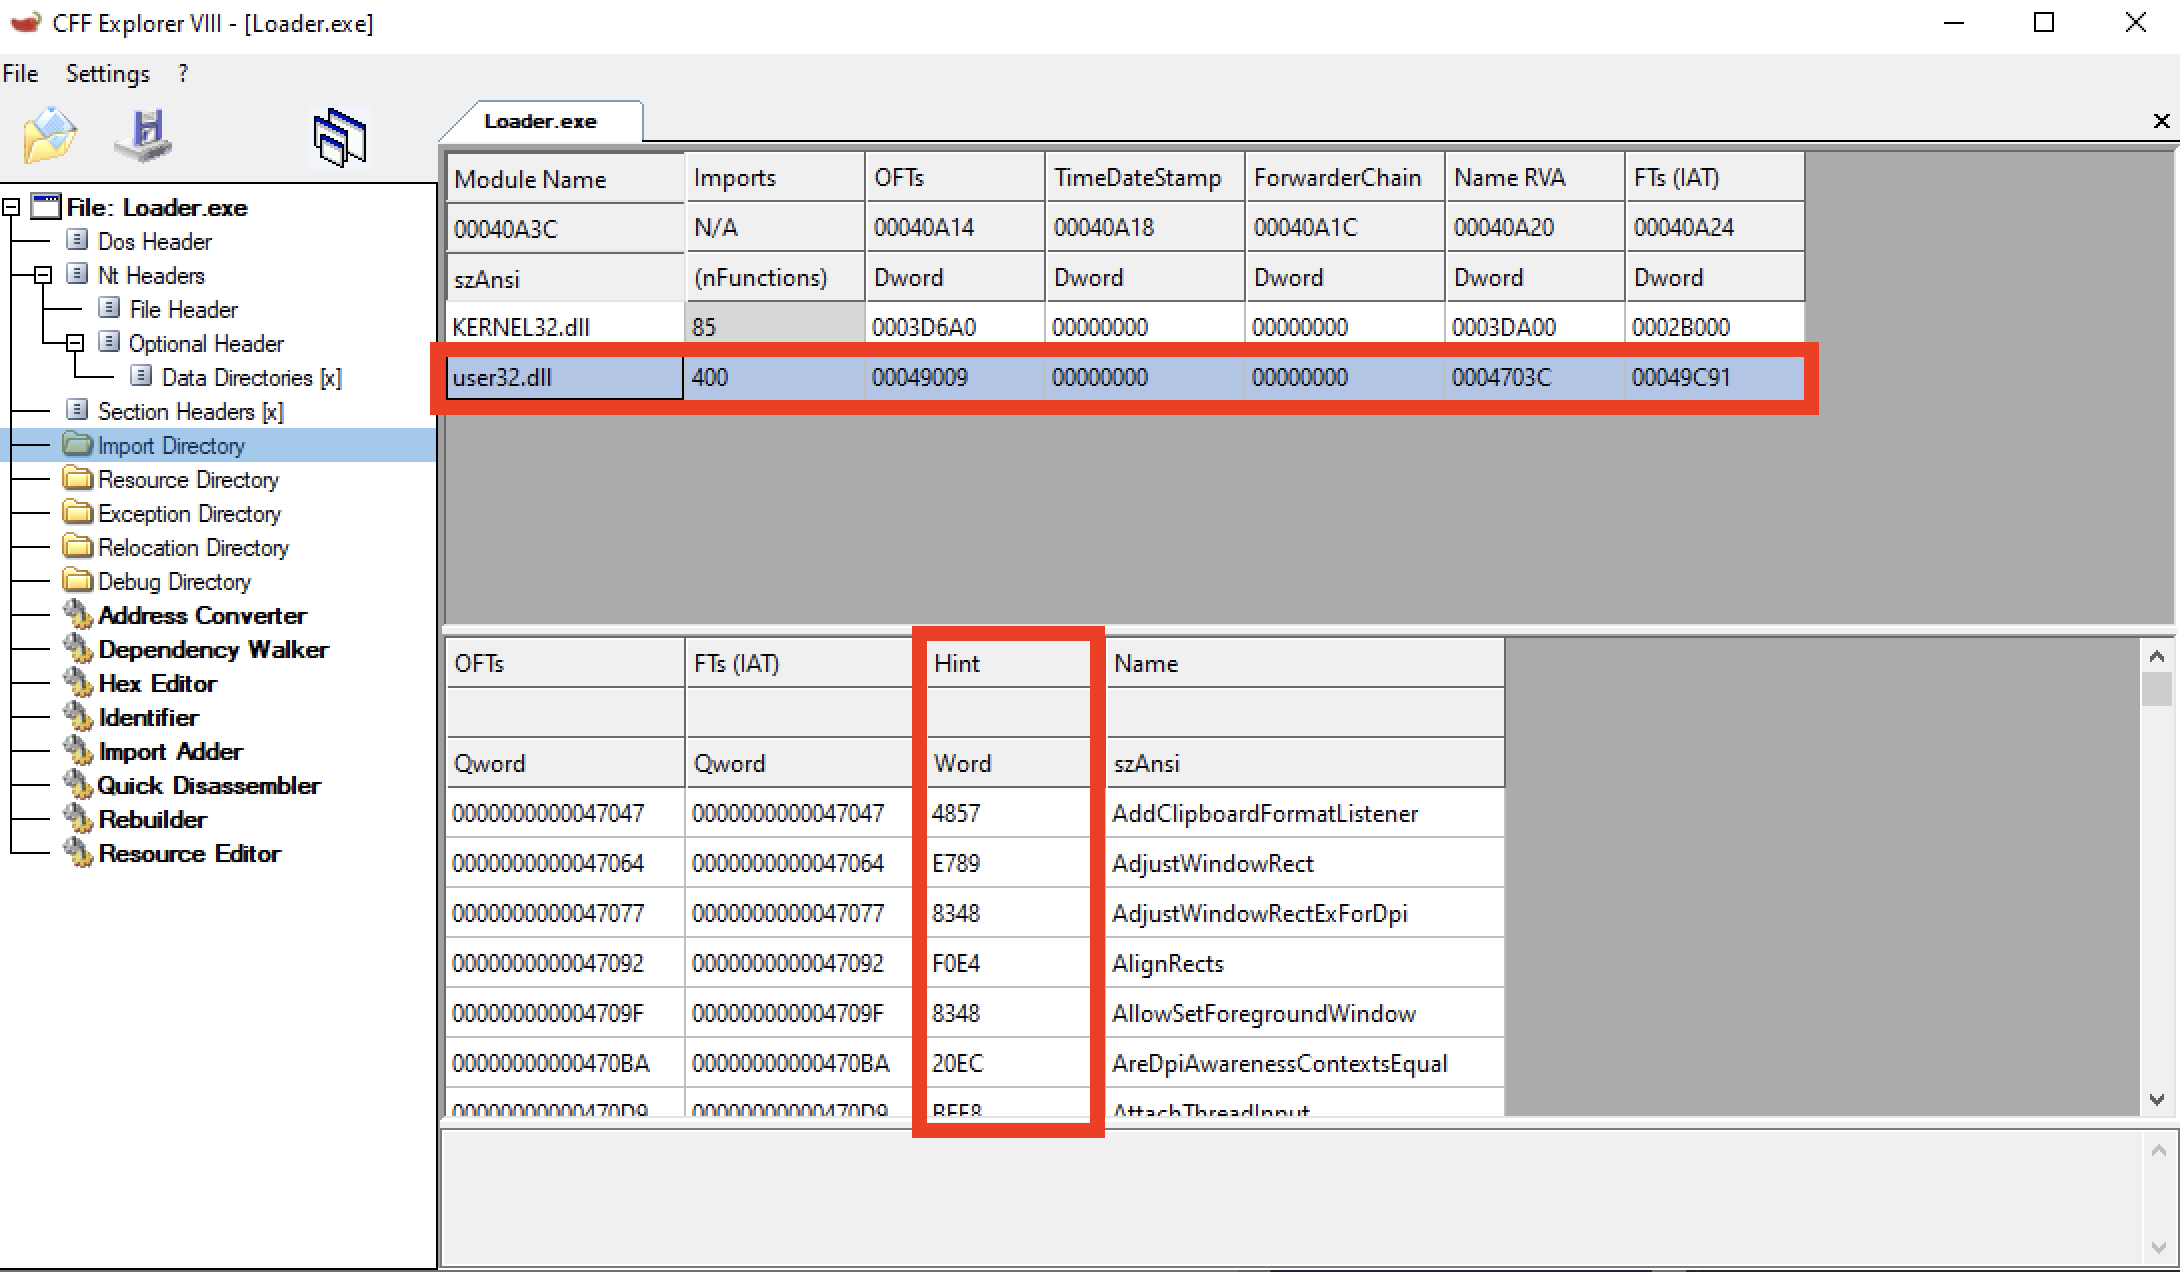
A PoC project for embedding shellcode to Hint/Name Table
 cisc0-gif/kitt-lite
Python-Based Pentesting CLI Tool
 jbooz1/cve-2017-0213
A version of CVE-2017-0213 that I plan to use with an Empire stager
 pwnfo/mapchar
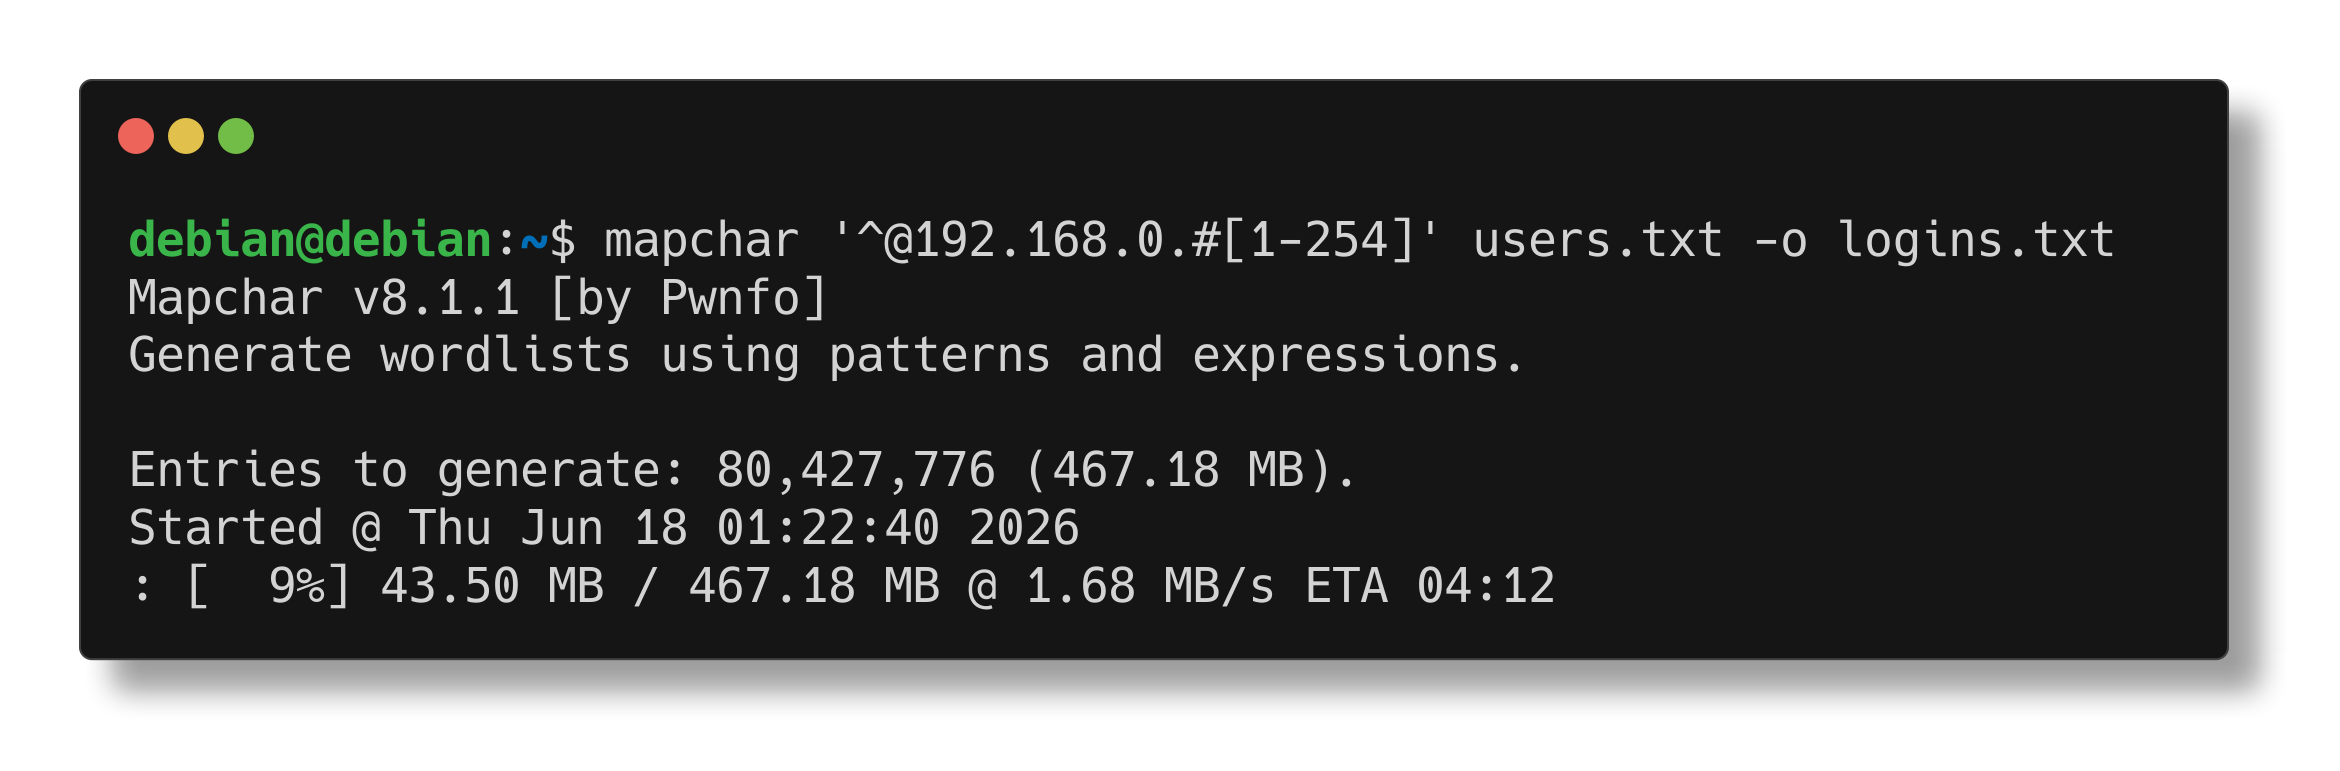
Generate wordlists using pattern logic and expressions.