
CVE-2025-43960
 far00t01/cve-2025-43960
PHP Object Injection exploit for Adminer <4.8.1 via Monolog, causing Denial of Service through crafted serialized payloads. Includes PoC, CVSS…
code-analysisexploitationpayload-generation+2
1
far00t01/cve-2025-43960PHP Object Injection exploit for Adminer <4.8.1 via Monolog, causing Denial of Service through crafted serialized payloads. Includes PoC, CVSS…
 attackgithub/zimbra-rce
Zimbra RCE CVE-2019-9670
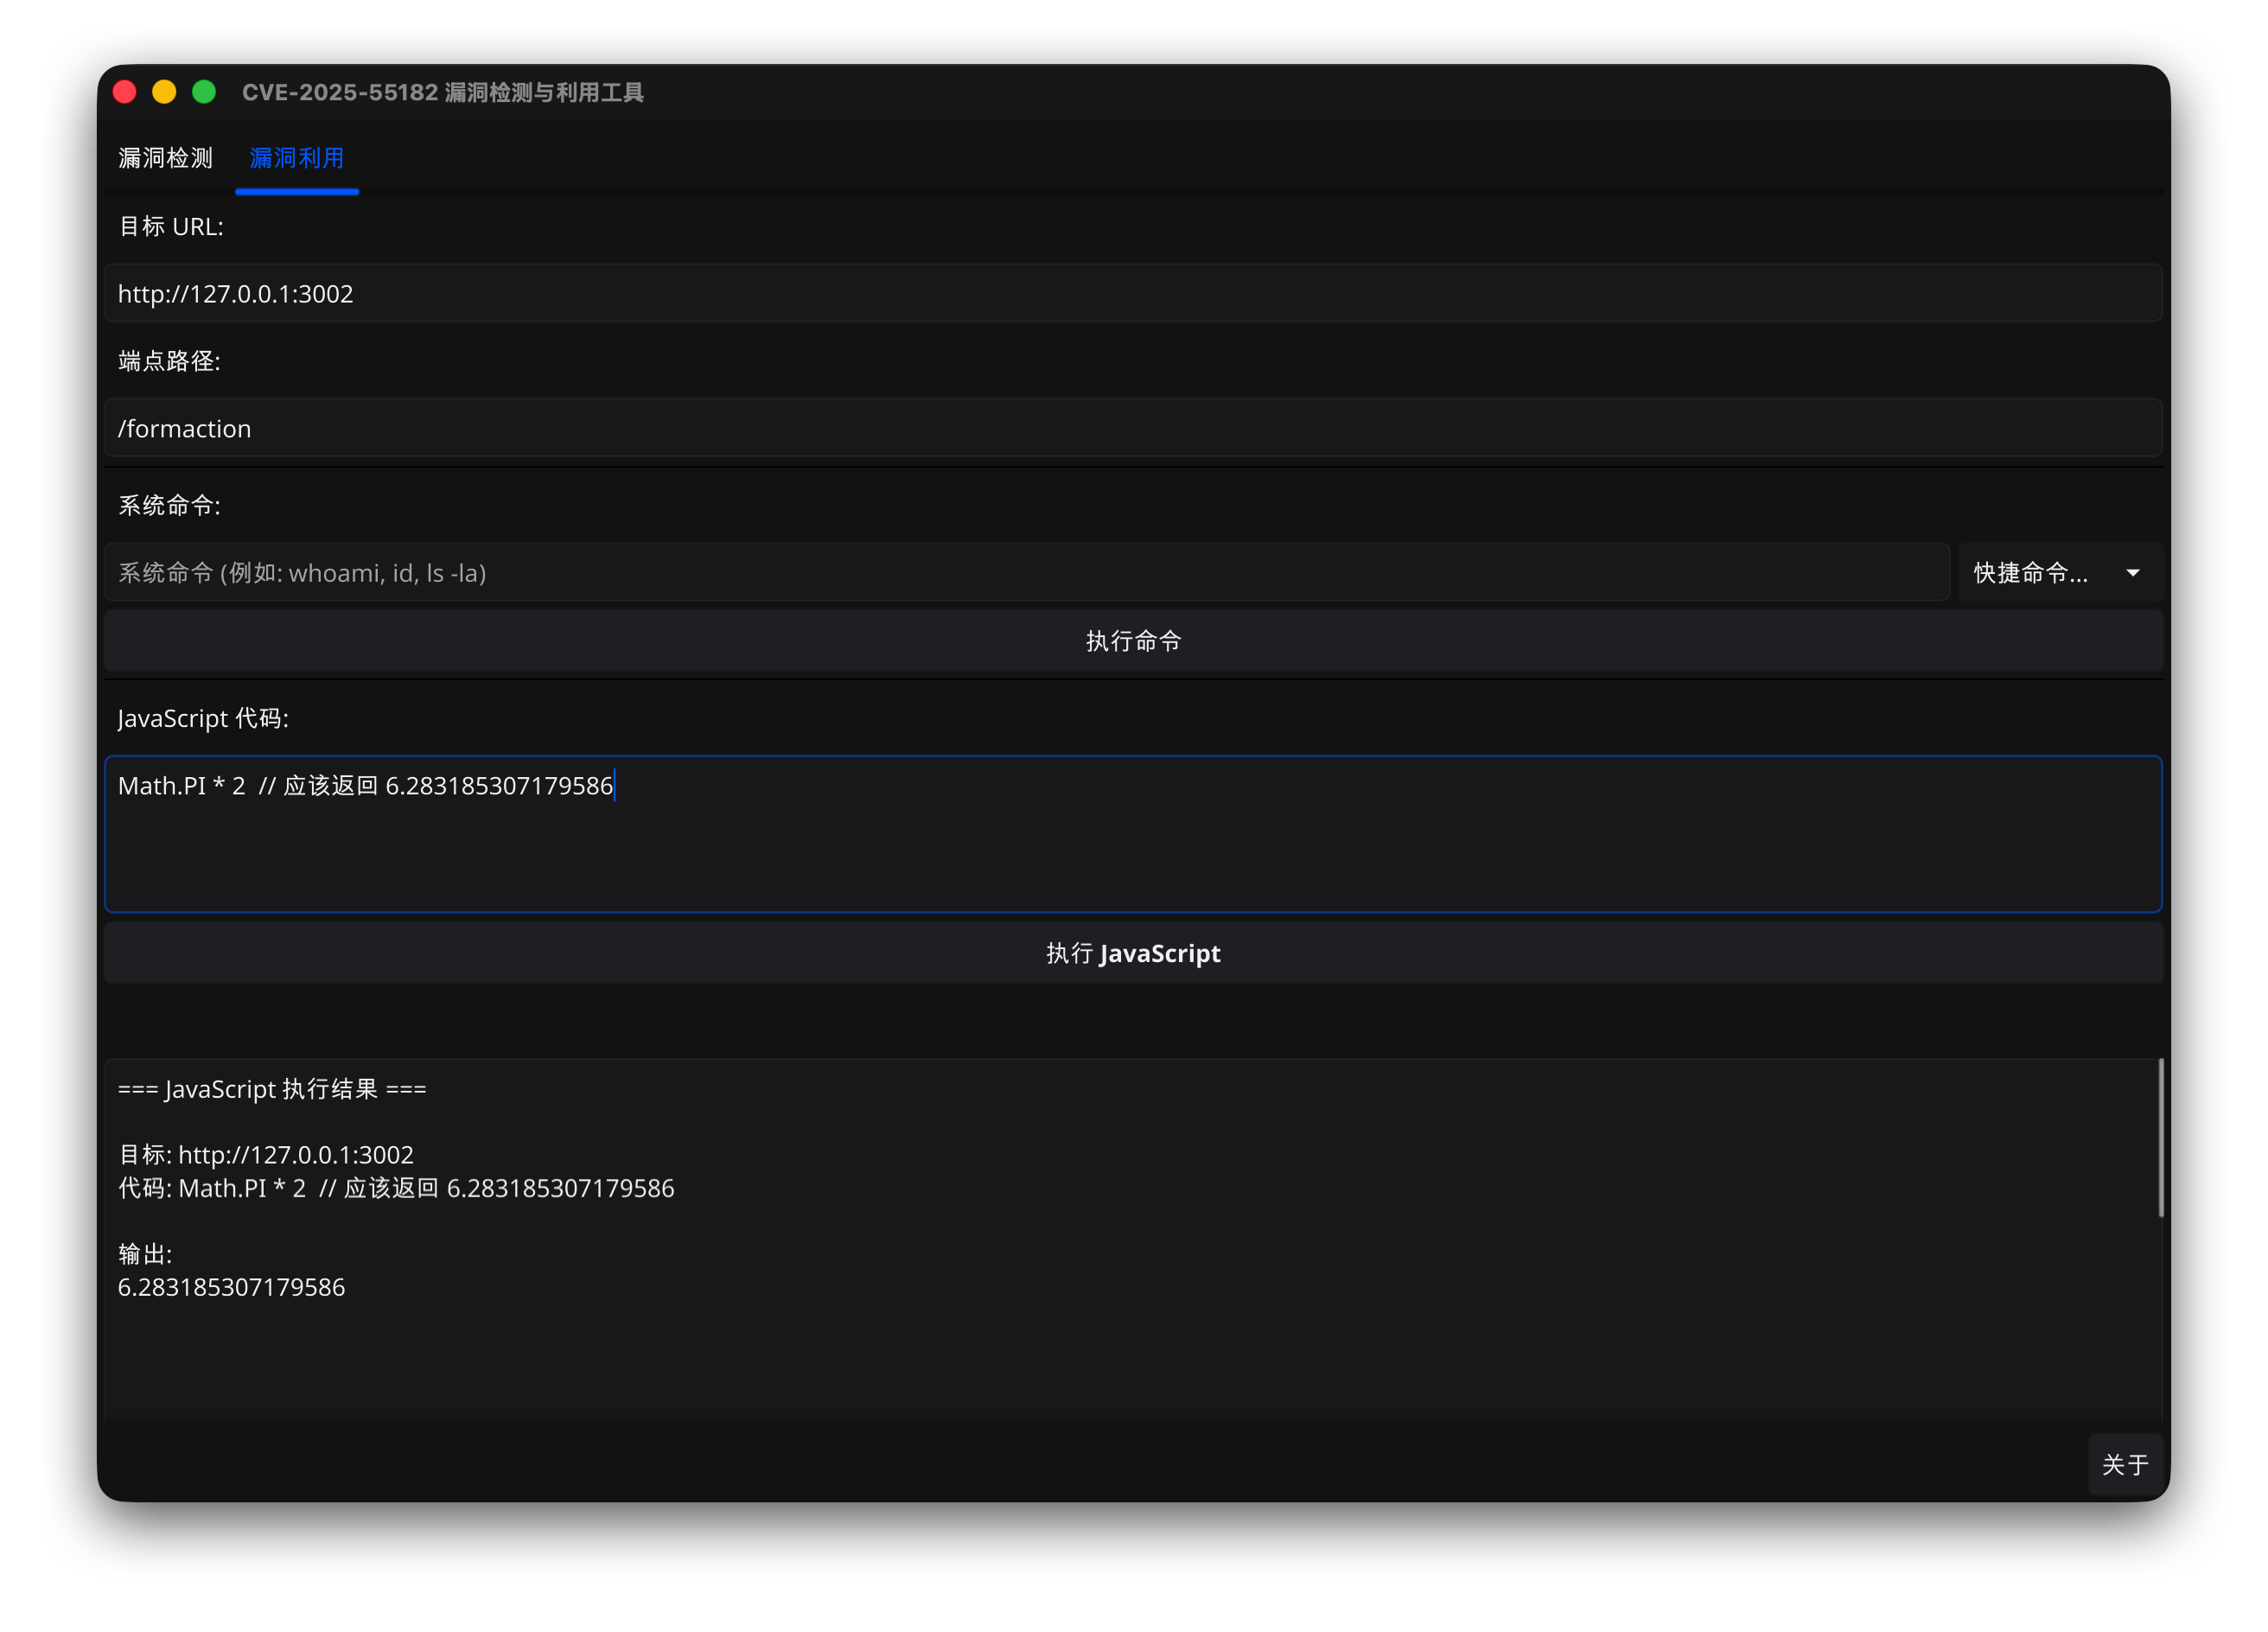 songsanggggg/cve-2025-55182
CVE-2025-55182 漏洞利用GUI,PoC / Exploit for CVE-2025-55182 & CVE-2025-66478
 evkir/phantom-grid
Free Burp Collaborator alternative- OOB interaction capture (HTTP/HTTPS/DNS) with SQLite & exfil reassembly
 ma1dong/activemq_cve-2015-5254
ActiveMQ_CVE-2015-5254
 leerina/cve-2019-2725
Proof-of-concept exploit for CVE-2019-2725 Weblogic deserialization RCE. Executes remote commands by sending a crafted payload to the vulnerable…
 murrez/cve-2026-94132
Python check/exploit PoC for CVE-2026-94132: detects AcyMailing for Joomla versions, probes the media/com_acym/upload directory, and verifies…
 kaizoku73/cve-2026-31857-poc
Proof of Concept for CVE-2026-31857, an authenticated Remote Code Execution vulnerability in Craft CMS caused by unsafe processing of user-controlled…
 java99999/cve-2026-86950-poc
Generates malicious files that trigger a CVE-2026-86950 out-of-bounds write (CWE-787) heap corruption, with reverse shell, command execution, or…
 yym8538/cve-2026-16723
Proof-of-concept exploit for CVE-2026-16723, a Fastjson 1.x @JSONType remote code execution flaw, with a payload JAR builder and reverse-shell…
 gagaltotal/cve-2021-41773-apache
CVE-2021-41773 Apache
 artofwar344/cve-2018-2893
CVE-2018-2893 PoC
 sec13b/cve-2021-44228-poc
exploit CVE-2021-44228
 mkhazamipour/log4j-vulnerable-app-cve-2021-44228-terraform
A Terraform to deploy vulnerable app and a JDNIExploit to work with CVE-2021-44228
 nxploited/cve-2025-8625
Copypress Rest API 1.1 - 1.2 - Missing Configurable JWT Secret and File-Type Validation to Unauthenticated Remote Code Execution
 zitchev/go_follina
Follina (CVE-2022-30190) proof-of-concept
 george0papasotiriou/cve-2026-21013-pdf-javascript-injection-via-embedded-script
Generates a PDF with embedded JavaScript to demonstrate CVE-2026-21013, an OpenAction injection leading to script execution in vulnerable PDF readers.
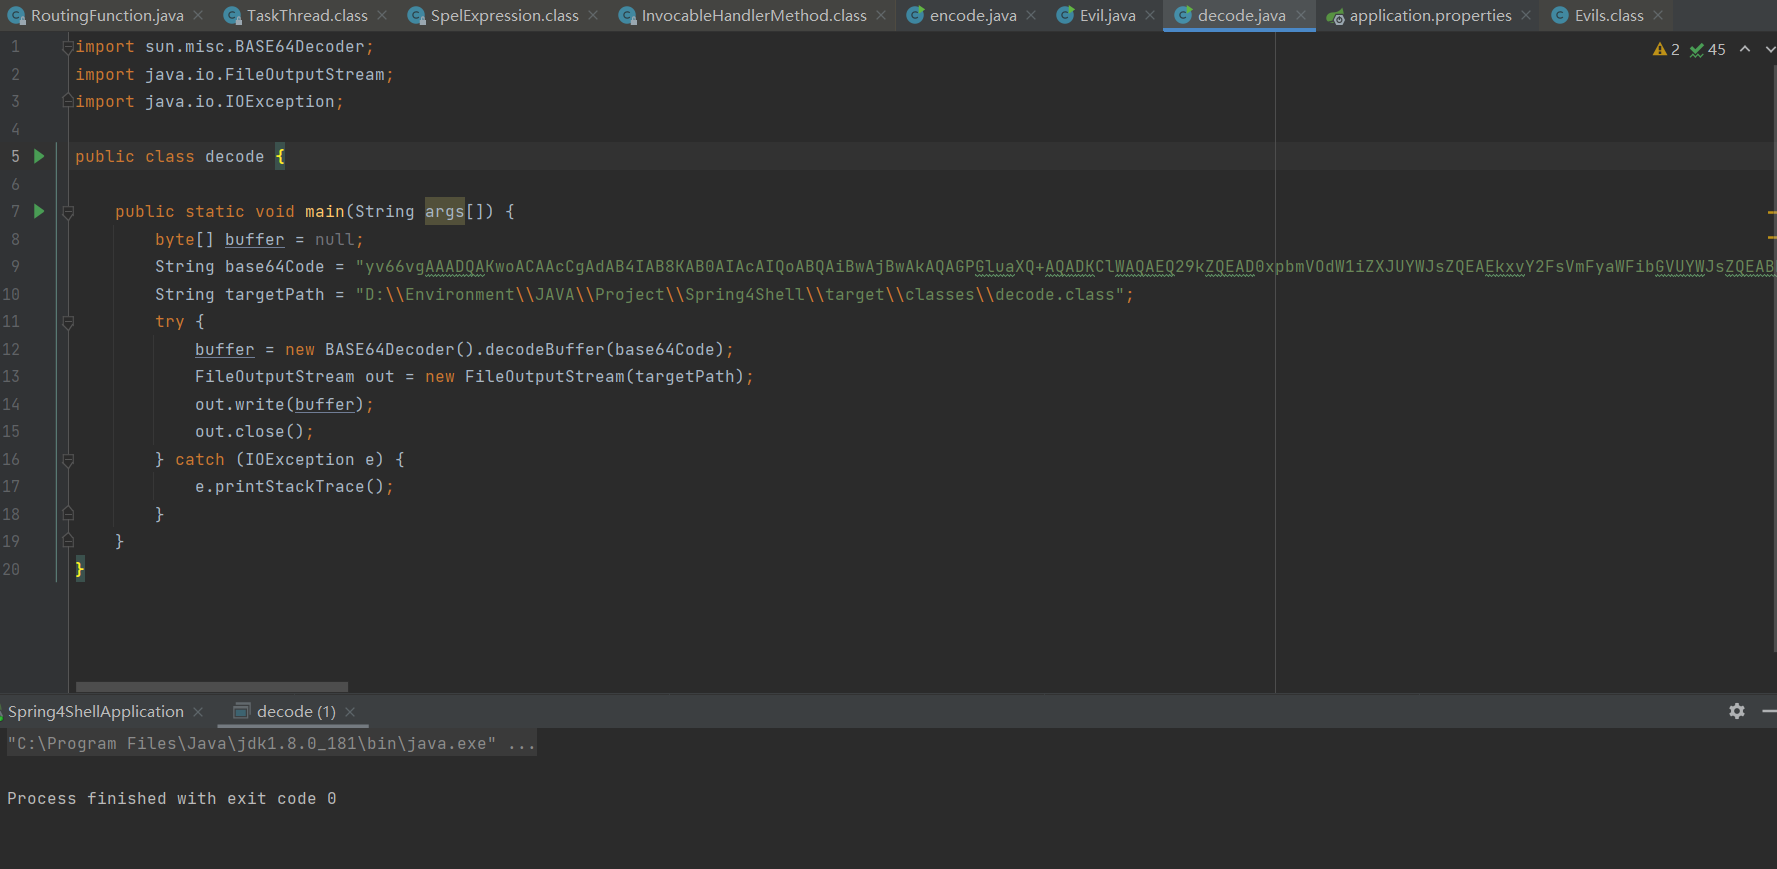 al1ex/javadere
Class to base64 String,base64 String to class