
PowerSharpPack
PowerShell wrapper bundling 50+ C# offensive security tools for post-exploitation, privilege escalation, credential dumping, lateral movement, and…

PowerShell wrapper bundling 50+ C# offensive security tools for post-exploitation, privilege escalation, credential dumping, lateral movement, and…

generate CobaltStrike's cross-platform payload

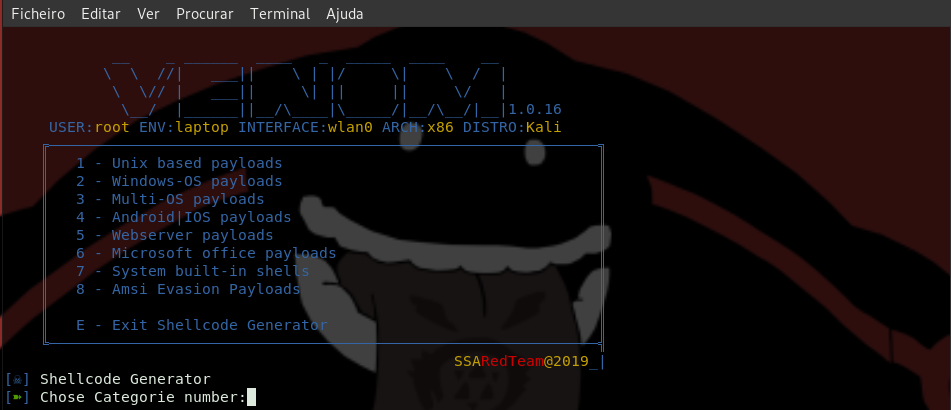
venom - C2 shellcode generator/compiler/handler

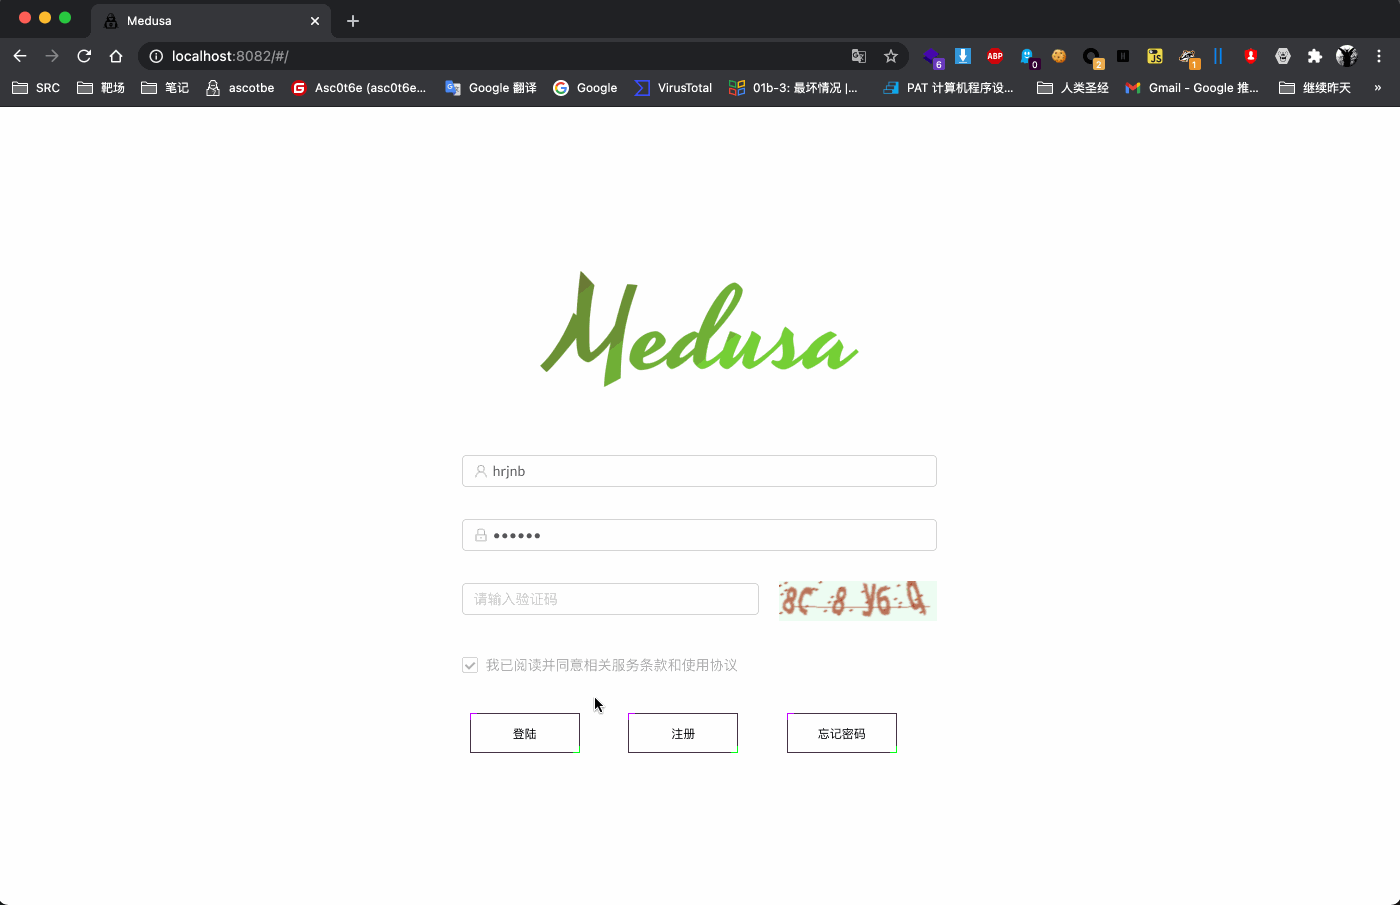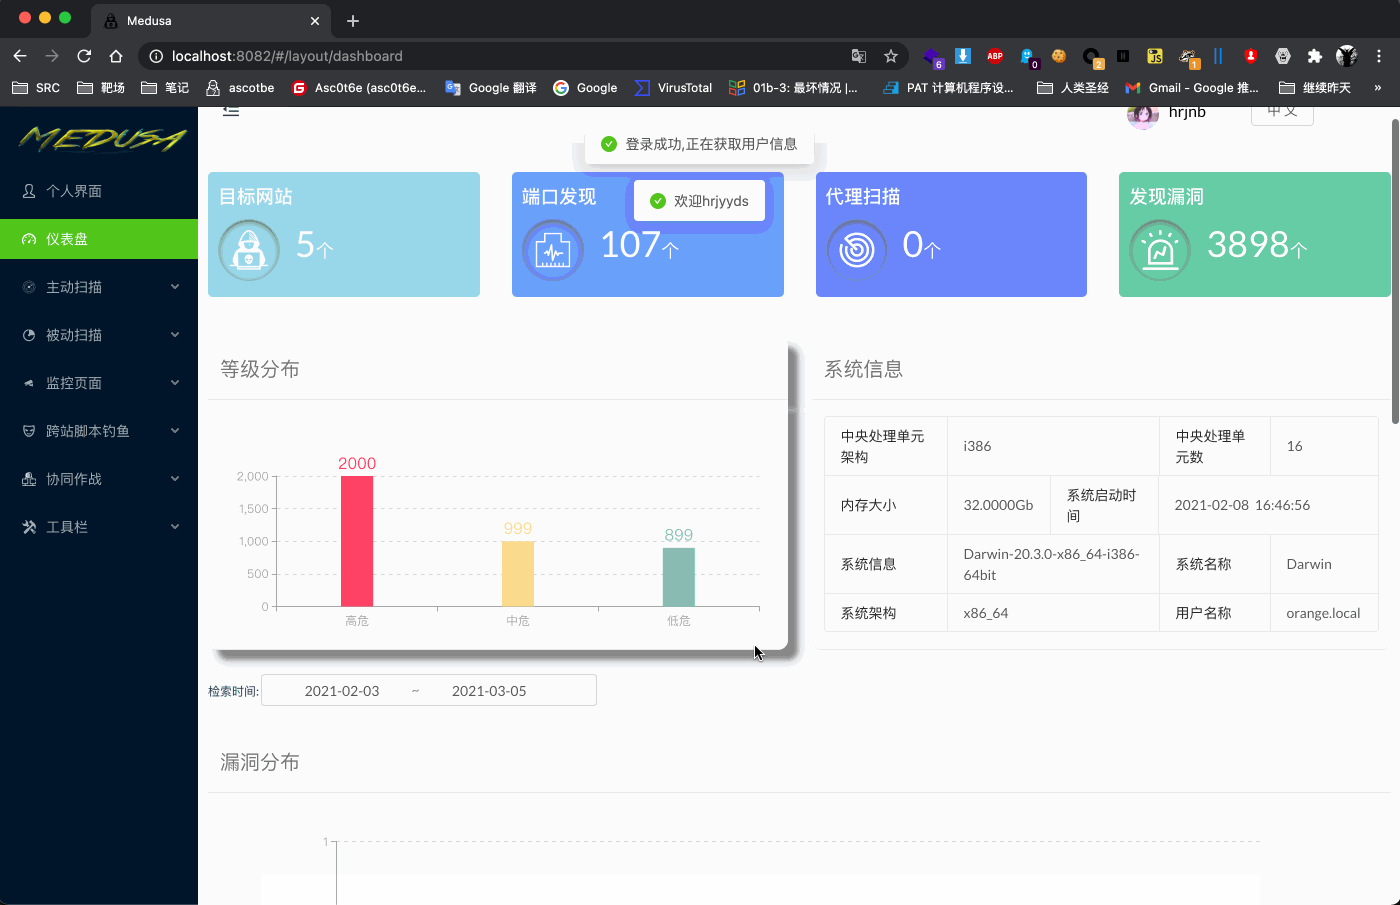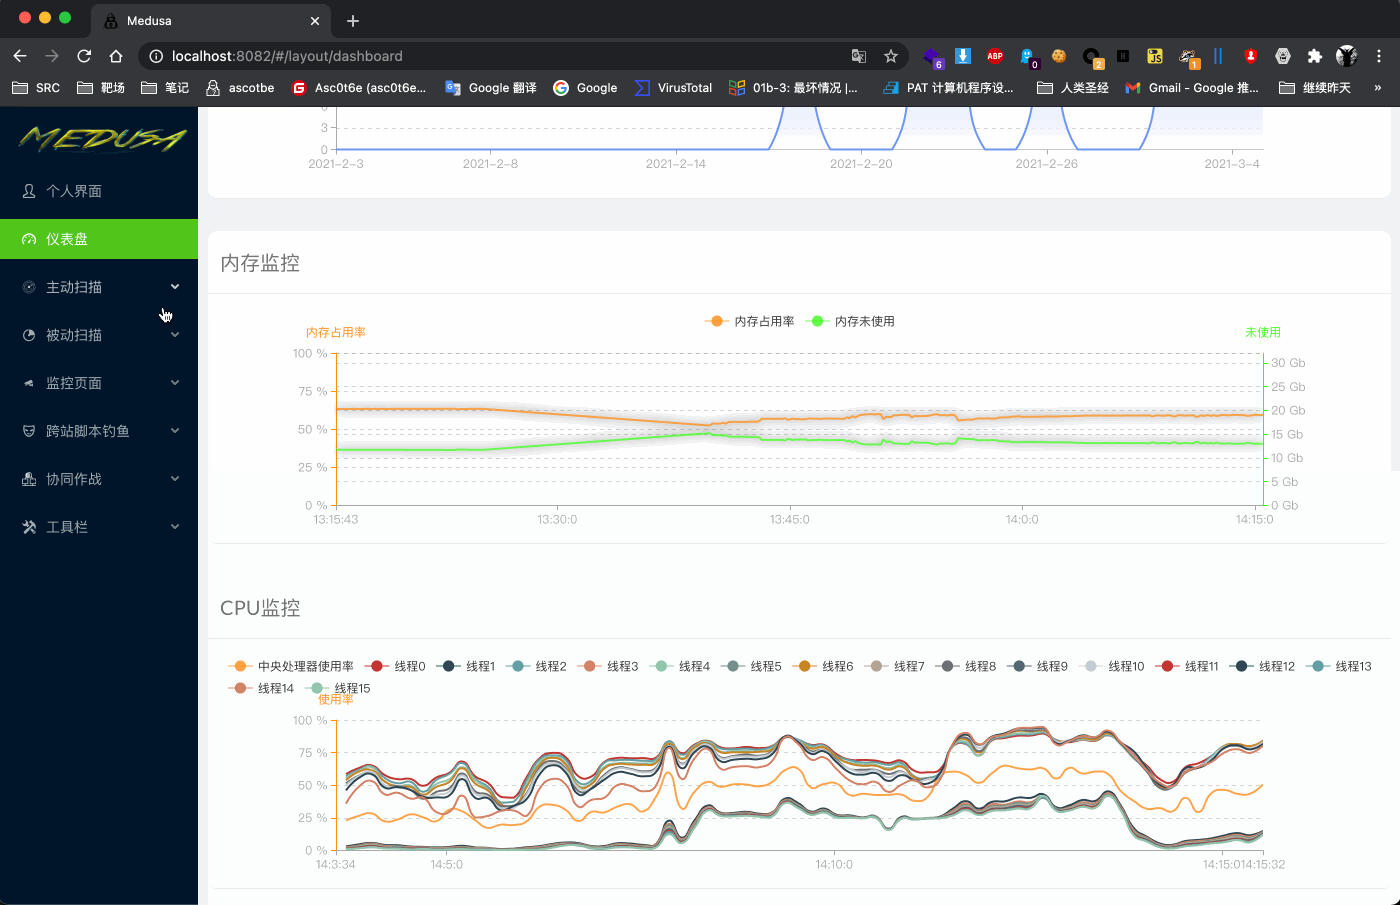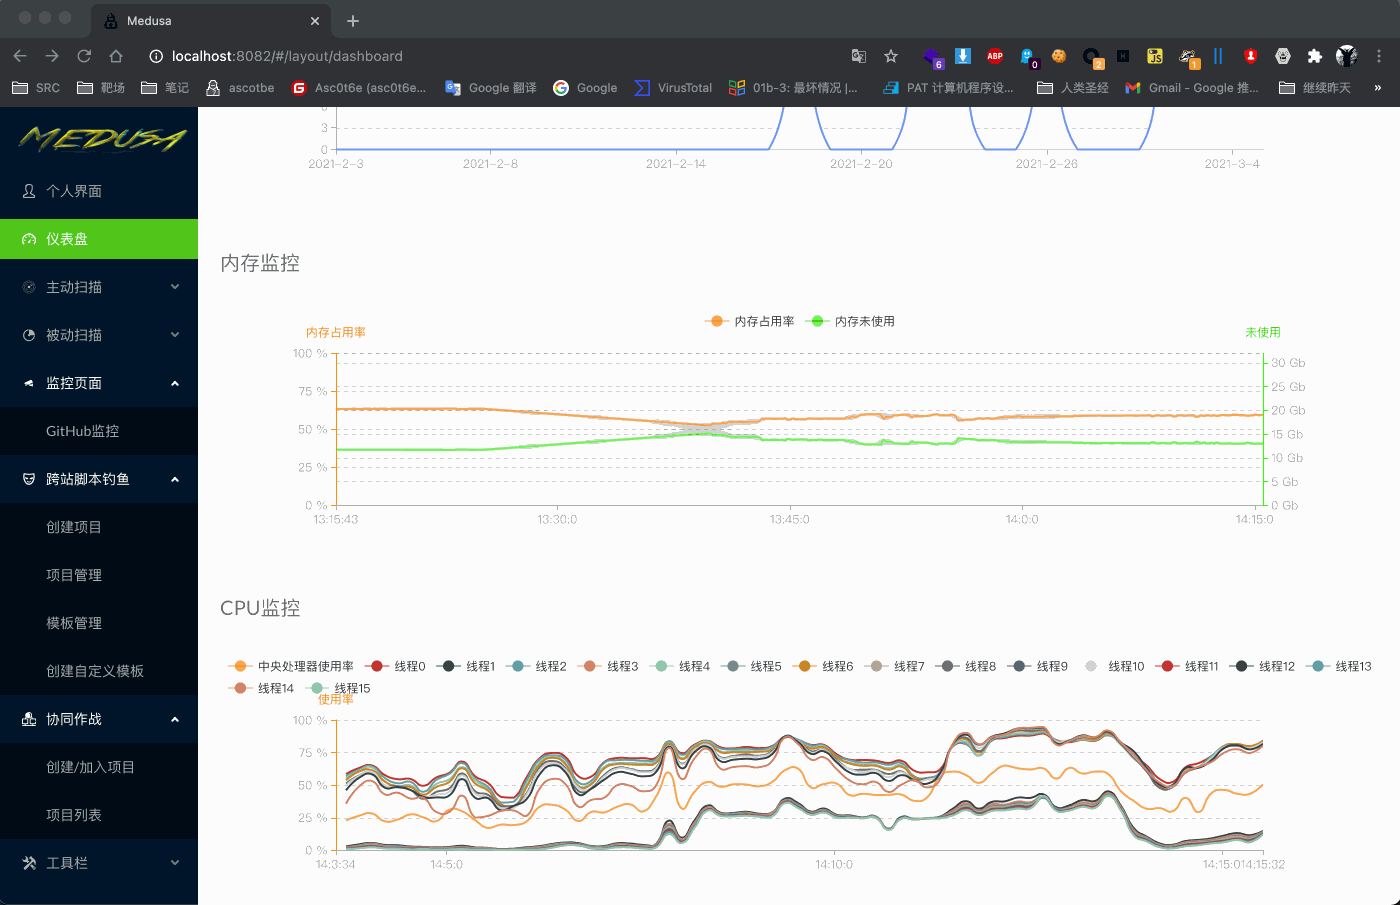
🐈Medusa是一个红队武器库平台,目前包括XSS平台、协同平台、CVE监控、免杀生成、DNSLOG、钓鱼邮件、文件获取等功能,持续开发中

Polymorphic C2 profile generator for Cobalt Strike that automates creation of evasive beacon configurations with randomized options for HTTP, DNS,…

Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…

This tool will setting up your backdoor/rootkits when backdoor already setup it will be hidden your spesisifc process,unlimited your session in…

evasion technique to defeat and divert detection and prevention of security products (AV/EDR/XDR)

Bypass firewall for traffic forwarding using webshell

Polymorphic encryptor that transforms shellcode, PE, and COFF files into obfuscated, position-independent payloads with RC4 and random block cipher…

morphHTA - Morphing Cobalt Strike's evil.HTA

application server attack toolkit

Cooolis-ms是一个包含了Metasploit Payload Loader、Cobalt Strike External C2 Loader、Reflective DLL injection的代码执行工具,它的定位在于能够在静态查杀上规避一些我们将要执行且含有特征的代码,帮助红队人员更方便快…

Anonymously Reverse Shell over Tor Network using Hidden services without Portforwarding.

A script to randomize Cobalt Strike Malleable C2 profiles and reduce the chances of flagging signature-based detection controls

Nim-based assembly packer and shellcode loader for opsec & profit

Cobalt Strike extension for post-exploitation persistence using SharpStay .NET assembly. Provides GUI-driven persistence via Registry keys, Scheduled…

Hacking systems with the automation of PasteJacking attacks.