
PEzor
 phra/pezor
Pack shellcode and PE executables into evasive payloads with anti-debug, unhooking, syscall, and memory fluctuation techniques for red-team…
exploit-frameworksids-ips-evasionpayload-generation+3
2.1k
phra/pezorPack shellcode and PE executables into evasive payloads with anti-debug, unhooking, syscall, and memory fluctuation techniques for red-team…
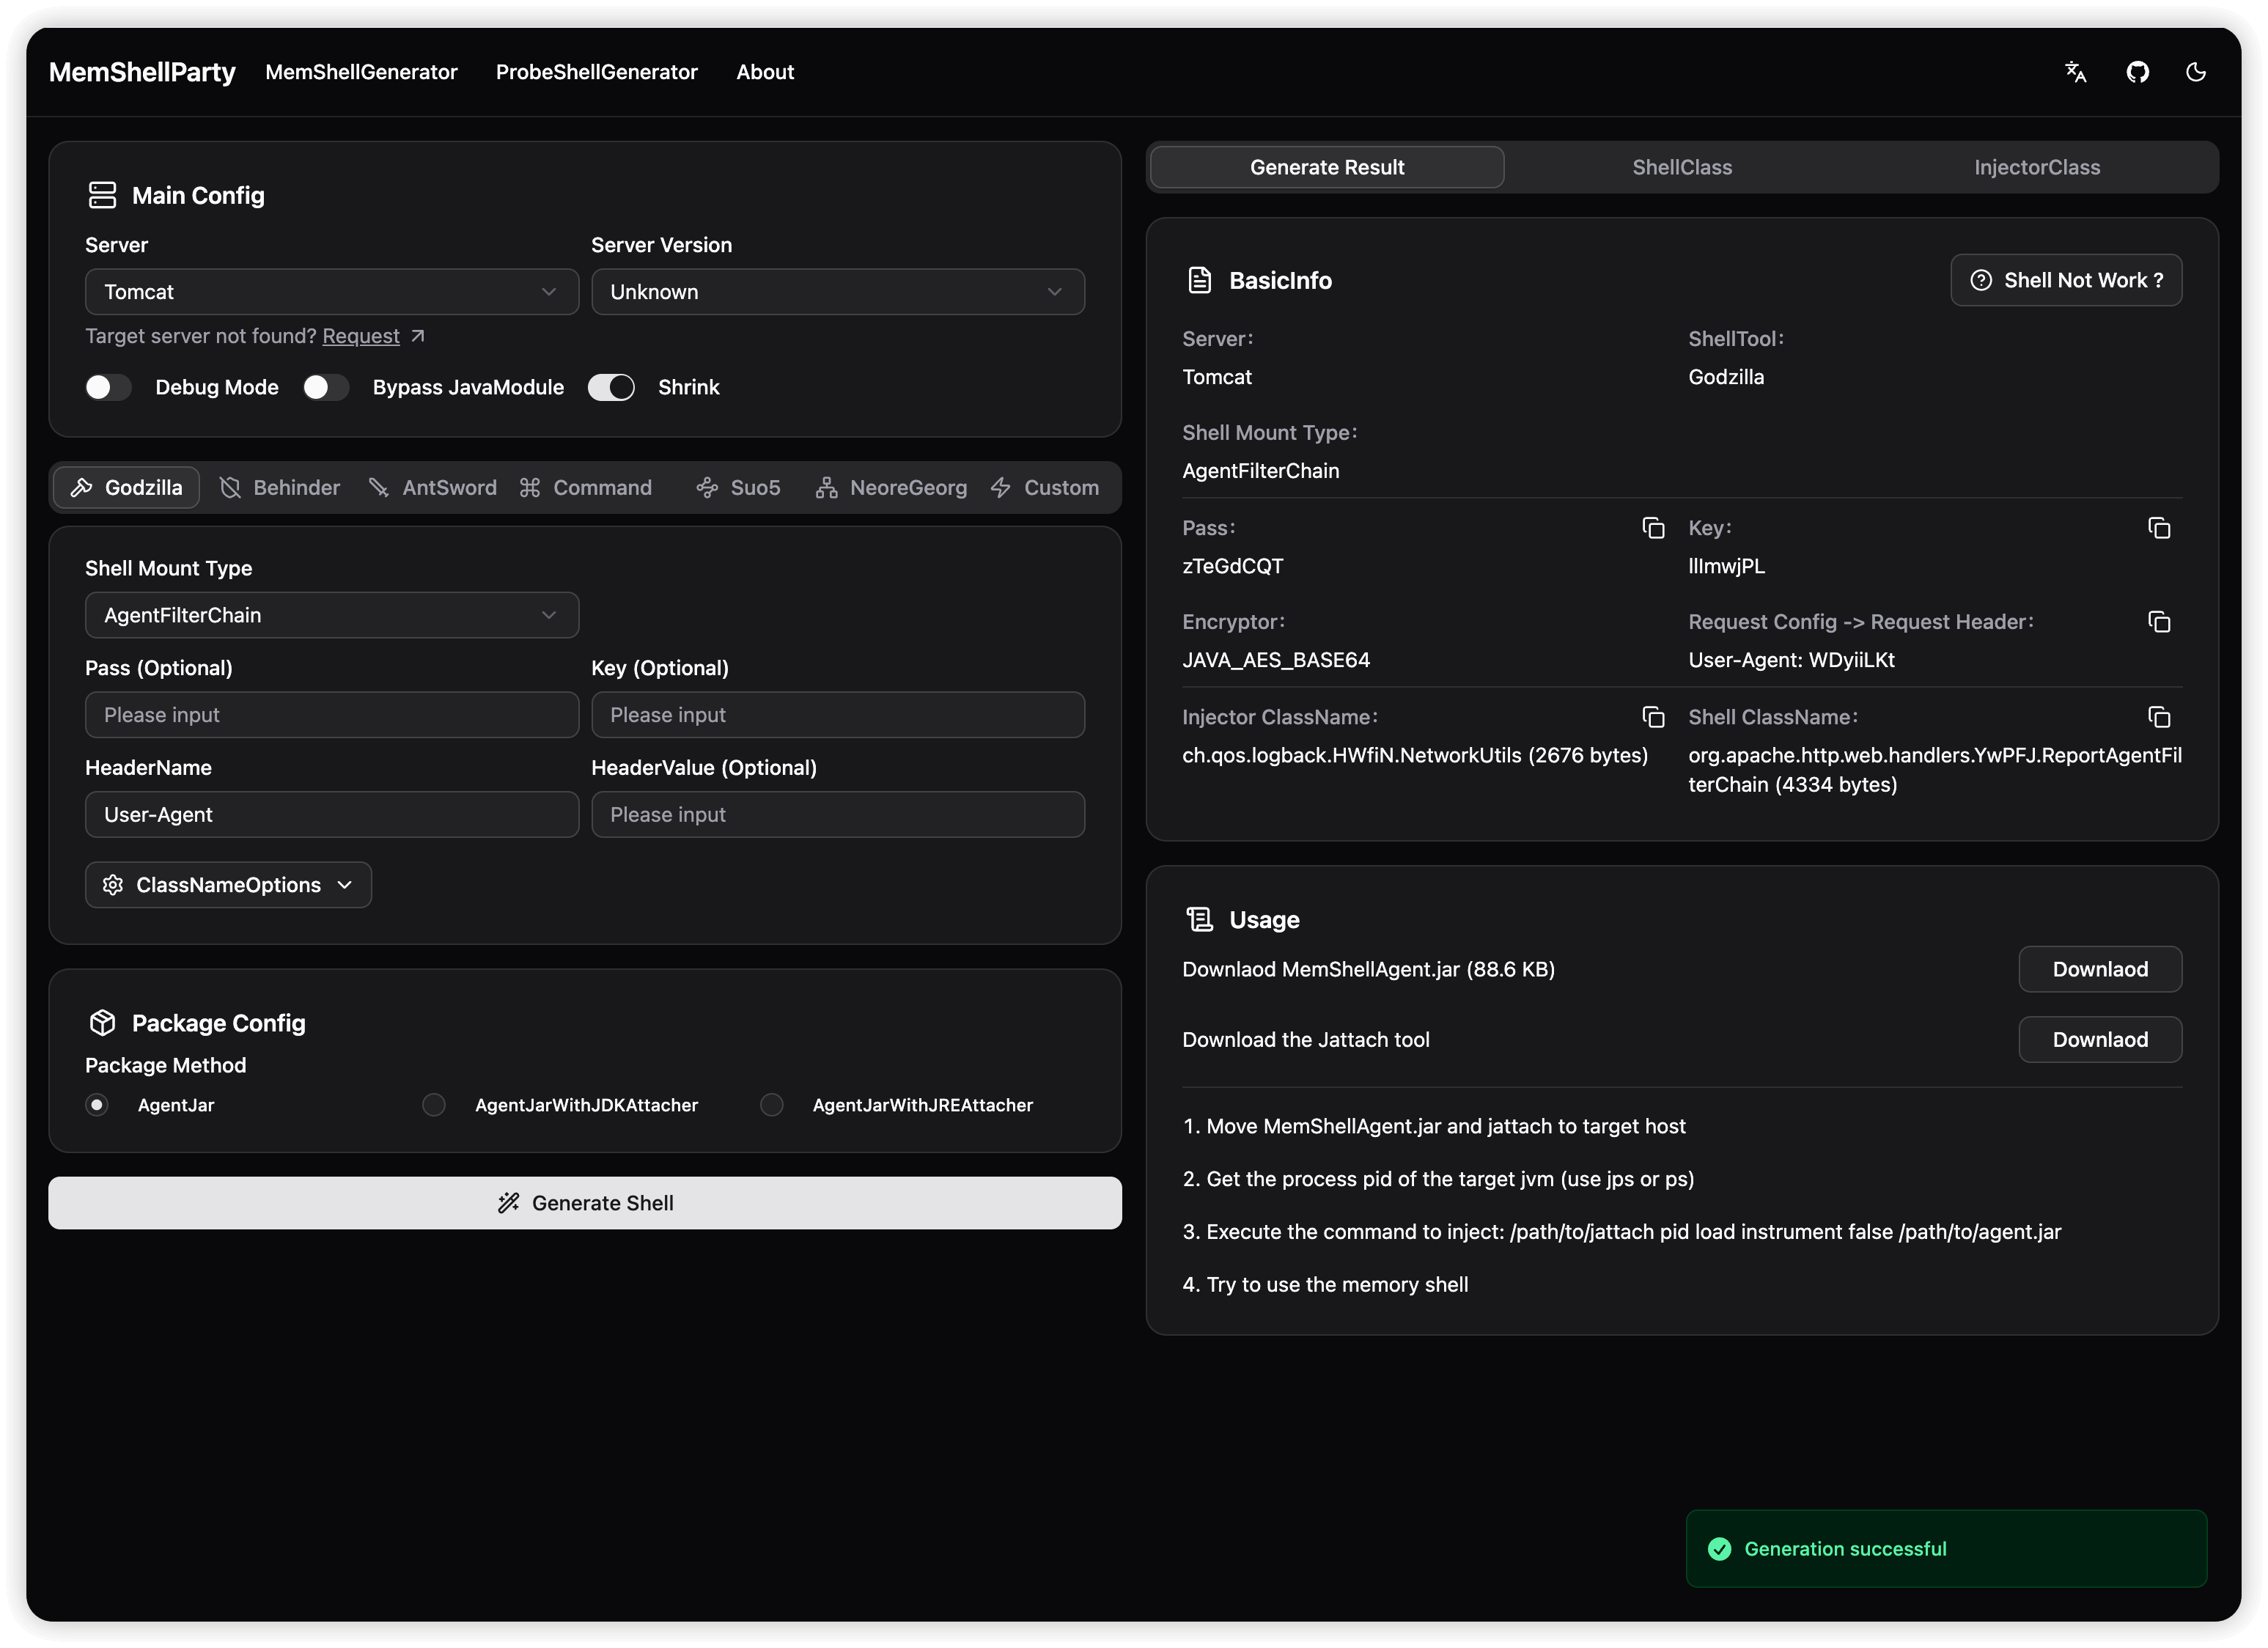 reajason/memshellparty
一款专注于 Java 主流 Web 中间件的内存马快速生成工具,致力于简化安全研究人员和红队成员的工作流程,提升攻防效率
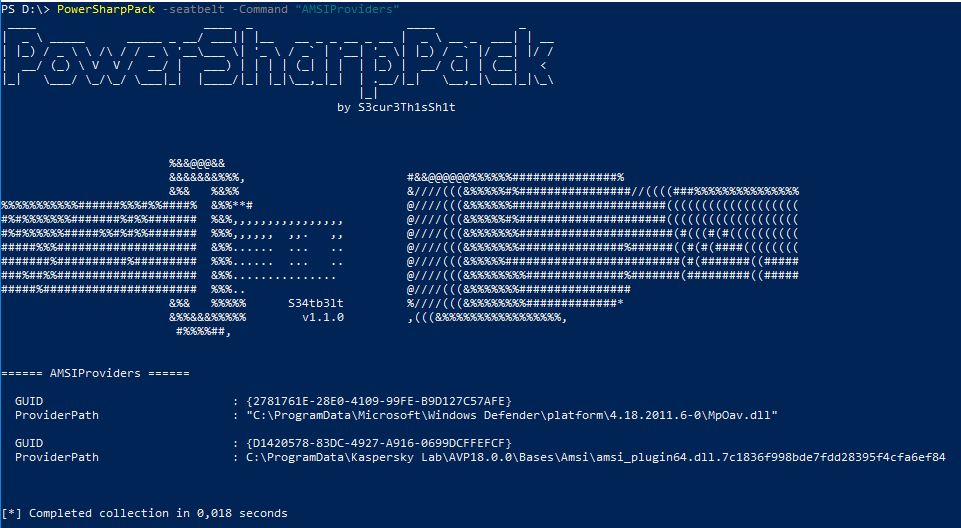 s3cur3th1ssh1t/powersharppack
PowerShell wrapper bundling 50+ C# offensive security tools for post-exploitation, privilege escalation, credential dumping, lateral movement, and…
 screetsec/vegile
This tool will setting up your backdoor/rootkits when backdoor already setup it will be hidden your spesisifc process,unlimited your session in…
 0xsp-srd/mortar
evasion technique to defeat and divert detection and prevention of security products (AV/EDR/XDR)
 0xthirteen/staykit
Cobalt Strike extension for post-exploitation persistence using SharpStay .NET assembly. Provides GUI-driven persistence via Registry keys, Scheduled…
 reverseclabs/wepwnise
WePWNise generates architecture independent VBA code to be used in Office documents or templates and automates bypassing application control and…
 federicodotta/java-deserialization-scanner
All-in-one plugin for Burp Suite for the detection and the exploitation of Java deserialization vulnerabilities
 vysecurity/morphhta
morphHTA - Morphing Cobalt Strike's evil.HTA
 hatriot/clusterd
application server attack toolkit
 d4vinci/pastejacker
Hacking systems with the automation of PasteJacking attacks.
 getrektboy724/betterxencrypt
A better version of Xencrypt.Xencrypt it self is a Powershell runtime crypter designed to evade AVs.
 hktalent/spring-spel-0day-poc
spring-cloud / spring-cloud-function,spring.cloud.function.routing-expression,RCE,0day,0-day,POC,EXP,CVE-2022-22963

 inf0secrabbit/badassmacros
C# tool that generates malicious VBA macros with shellcode injection, VBA purging, and sandbox detection for red team operations.
 kkirsche/cve-2017-10271
Python and Metasploit exploit for Oracle WebLogic WLS-WSAT deserialization vulnerability (CVE-2017-10271) with detection scanning and remote code…
 0x09al/cve-2018-8174-msf
CVE-2018-8174 - VBScript memory corruption exploit.
 mstxq17/cve-2021-1675_rdl_lpe
PrintNightMare LPE提权漏洞的CS 反射加载插件。开箱即用、通过内存加载、混淆加载的驱动名称来ByPass Defender/EDR。