

discover
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
api-security-testingcloud-securitycontainer-security+9
3.9k
leebaird/discoverCustom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 tc4dy/cve-2026-60206-poc-exploit
👾 CVE-2026-60206 - Oracle WebLogic SAML Auth Bypass Exploit Framework ⚡Bash & Python versions. Features: --detect safe check, --exploit…
 keyuraghao/cve-2025-20260
Python-based exploit for CVE-2025-20260 that generates a malicious PDF file and includes core dump analysis capabilities for vulnerability…
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
 tegal1337/pocketpentester
Offline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 miscusi-peek/cheatengine-mcp-bridge
Connect your favorite AI agents directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using natural…
 sacriphanius/zhilly
🛡️ AI-powered portable cybersecurity & pentesting assistant built on ESP32-S3 (LilyGO T-Embed CC1101 & T-Watch S3). Features voice-controlled RF…
 shinthink/cve-2026-61424
DJ-Classifieds Joomla Component Unauthenticated File Upload RCE. 3-string filter bypass via PHP short tags. CVSS 10.0 | CWE-434 | com_djclassifieds <…
 sinfulz/justtryharder
Comprehensive penetration testing cheat sheet for PWK/OSCP exam preparation, covering privilege escalation, password cracking, payload generation,…
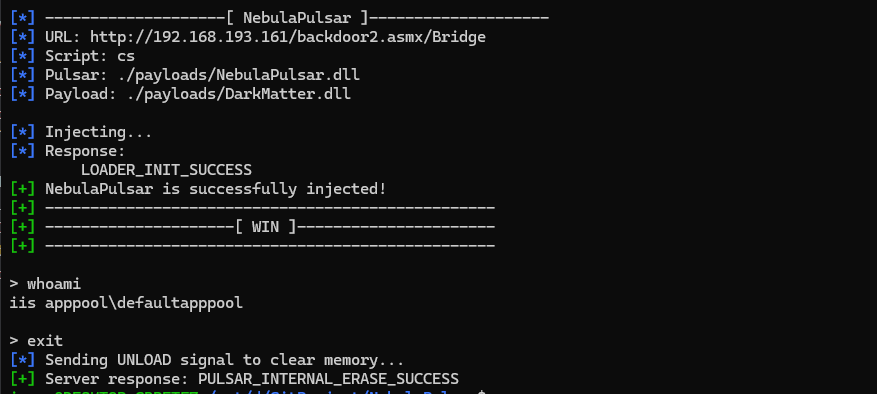 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…
 gh1mau/masta-cve-2026-48907
Single-file Python scanner for CVE-2026-48907 (Joomla JCE Editor RCE). Detects Joomla/JCE, performs intrusive math-verified payload test, supports…
 xxconi/cve-2026-27384
Automated scanner and exploit for CVE-2026-27384, an unauthenticated RCE in W3 Total Cache via mfunc/eval() injection. Features auto-detection, 48…
 xxconi/cve-2026-6271
Automated scanner for CVE-2026-6271, a critical unauthenticated arbitrary file upload leading to RCE in the WordPress Career Section plugin. Supports…
 gouldnicholas/cve-2026-5817-poc
Docker Model Runner container-to-host RCE / Escape: A critical vulnerability that allows for container-to-host code execution in the Docker Model…
 alex-acero-security/cve-2025-20260-poc
Proof-of-concept exploit for CVE-2025-20260, a buffer overflow in ClamAV's PDF scanning. Includes a Python script to generate a malicious PDF and…
 s3rgeym/cve-2020-9006
Exploit for CVE-2020-9006 targeting WordPress Popup-Builder plugin via SQL injection and PHP deserialization, with payload generation and Nmap…
 opsecramdan/react2shell-cve-2025-55182
Automated exploitation framework for CVE-2025-55182 (Next.js RCE) with subdomain enumeration, vulnerability scanning, payload generation, and…