Empire
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
adversarial-attackcommand-and-controldata-exfiltration+16
5.3k
bc-security/empireEmpire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
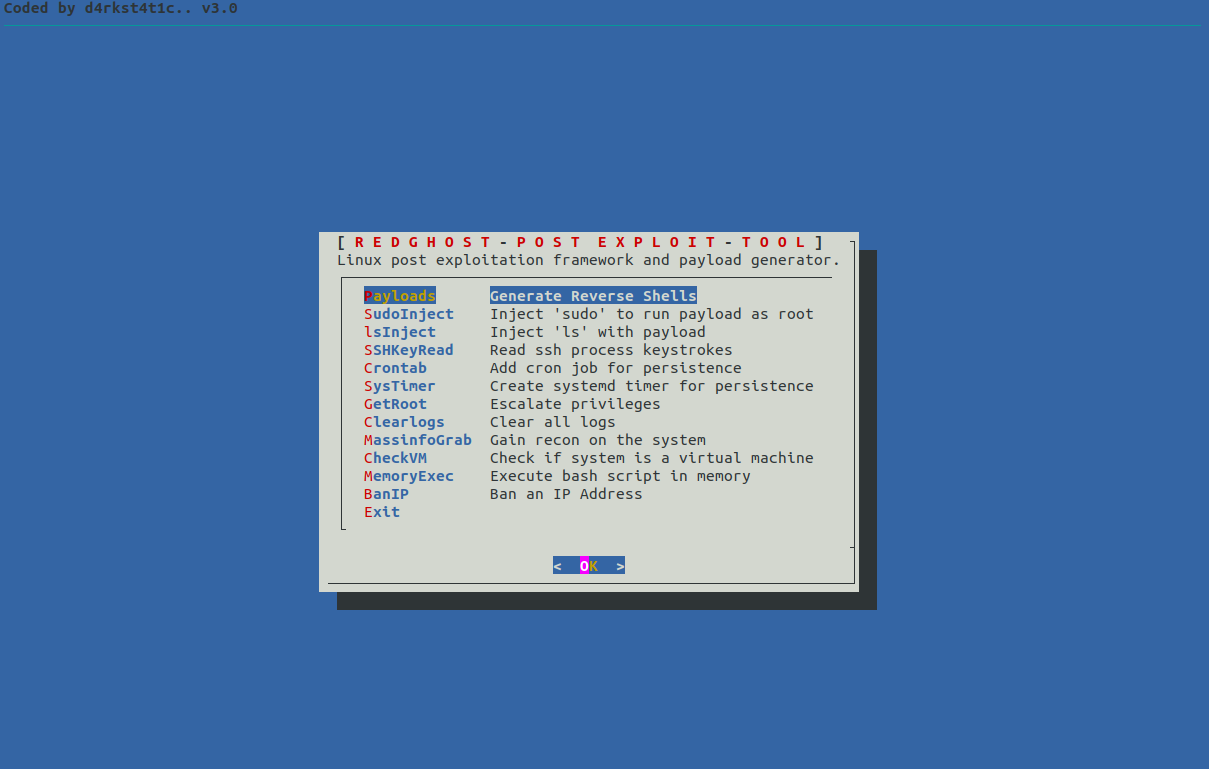 d4rk007/redghost
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
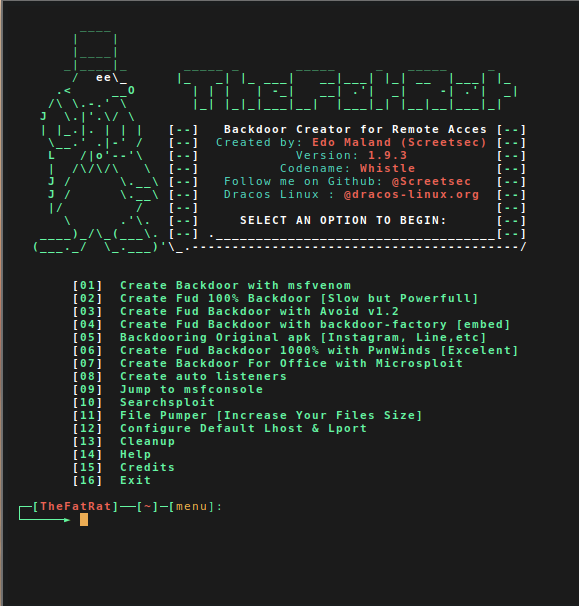 screetsec/thefatrat
Thefatrat a massive exploiting tool : Easy tool to generate backdoor and easy tool to post exploitation attack like browser attack and etc . This…
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
 lucasjacks0n/eggshell
iOS/macOS/Linux Remote Administration Tool
 metarget/k0otkit
k0otkit is a universal post-penetration technique which could be used in penetrations against Kubernetes clusters.
 redcode-labs/gosh
Golang reverse/bind shell generator
 k4nfr3/cve-2024-9474
Python exploit script for CVE-2024-9474 targeting PAN-OS SSL VPN, enabling remote code execution and reverse shell deployment for penetration testing.
 portbuster1337/cve-2026-33137
XWiki Platform - CVE-2026-33137 PoC - Unauthenticated XAR Import via REST /wikis/{wikiName}
 ludy-dev/vbulletin_routestring-rce
PoC exploit for CVE-2019-16759 enabling remote code execution on vBulletin 5.0.0–5.6.2 via malicious POST request due to input validation flaw.
 lp008/cve-2021-25646
Exploit for CVE-2021-25646 Apache Druid RCE via crafted HTTP POST request to the sampler endpoint, with embedded payload delivery and Snort detection…
 havocframework/havoc
The Havoc Framework
 foxglovesec/javaunserializeexploits
Exploit toolkit for Java deserialization vulnerabilities in WebLogic, WebSphere, JBoss, Jenkins, and OpenNMS. Generates crafted serialized payloads…
 joelgmsec/autordpwn
The Shadow Attack Framework
 mananispiwpiw/cve-2025-59528-poc
CVE-2025-59528 Proof of Concept
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 dreadlocked/drupalgeddon2
Exploit for Drupal v7.x + v8.x (Drupalgeddon 2 / CVE-2018-7600 / SA-CORE-2018-002)