
Awesome-CobaltStrike
 zer0yu/awesome-cobaltstrike
List of Awesome CobaltStrike Resources
command-and-controlcurated-resourceseducation+7
zer0yu/awesome-cobaltstrikeList of Awesome CobaltStrike Resources
 fabiobaroni/awesome-exploit-development
A curated list of resources (books, tutorials, courses, tools and vulnerable applications) for learning about Exploit Development
 infosecn1nja/red-teaming-toolkit
This repository contains cutting-edge open-source security tools (OST) for a red teamer and threat hunter.
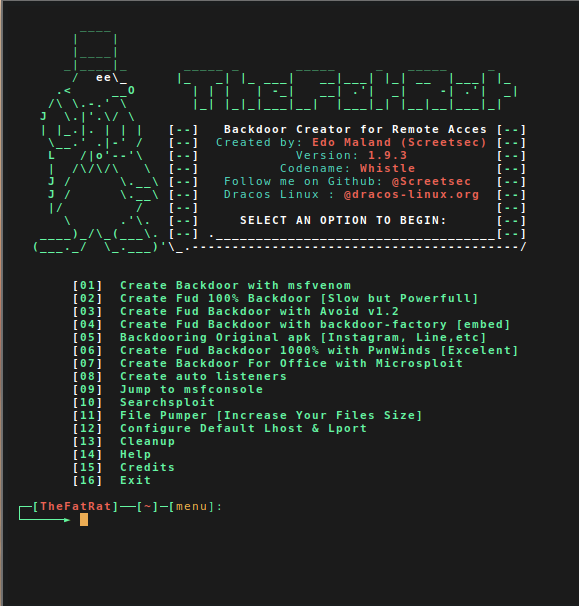 screetsec/thefatrat
Thefatrat a massive exploiting tool : Easy tool to generate backdoor and easy tool to post exploitation attack like browser attack and etc . This…
 stephenfewer/reflectivedllinjection
Reflective DLL injection is a library injection technique in which the concept of reflective programming is employed to perform the loading of a…
 tihanyin/pssw100avb
A list of useful Powershell scripts with 100% AV bypass (At the time of publication).
 blasty/cve-2021-3156
Exploit for CVE-2021-3156 (Baron Samedit), a heap-based buffer overflow in sudo, enabling local privilege escalation. Includes target list and…
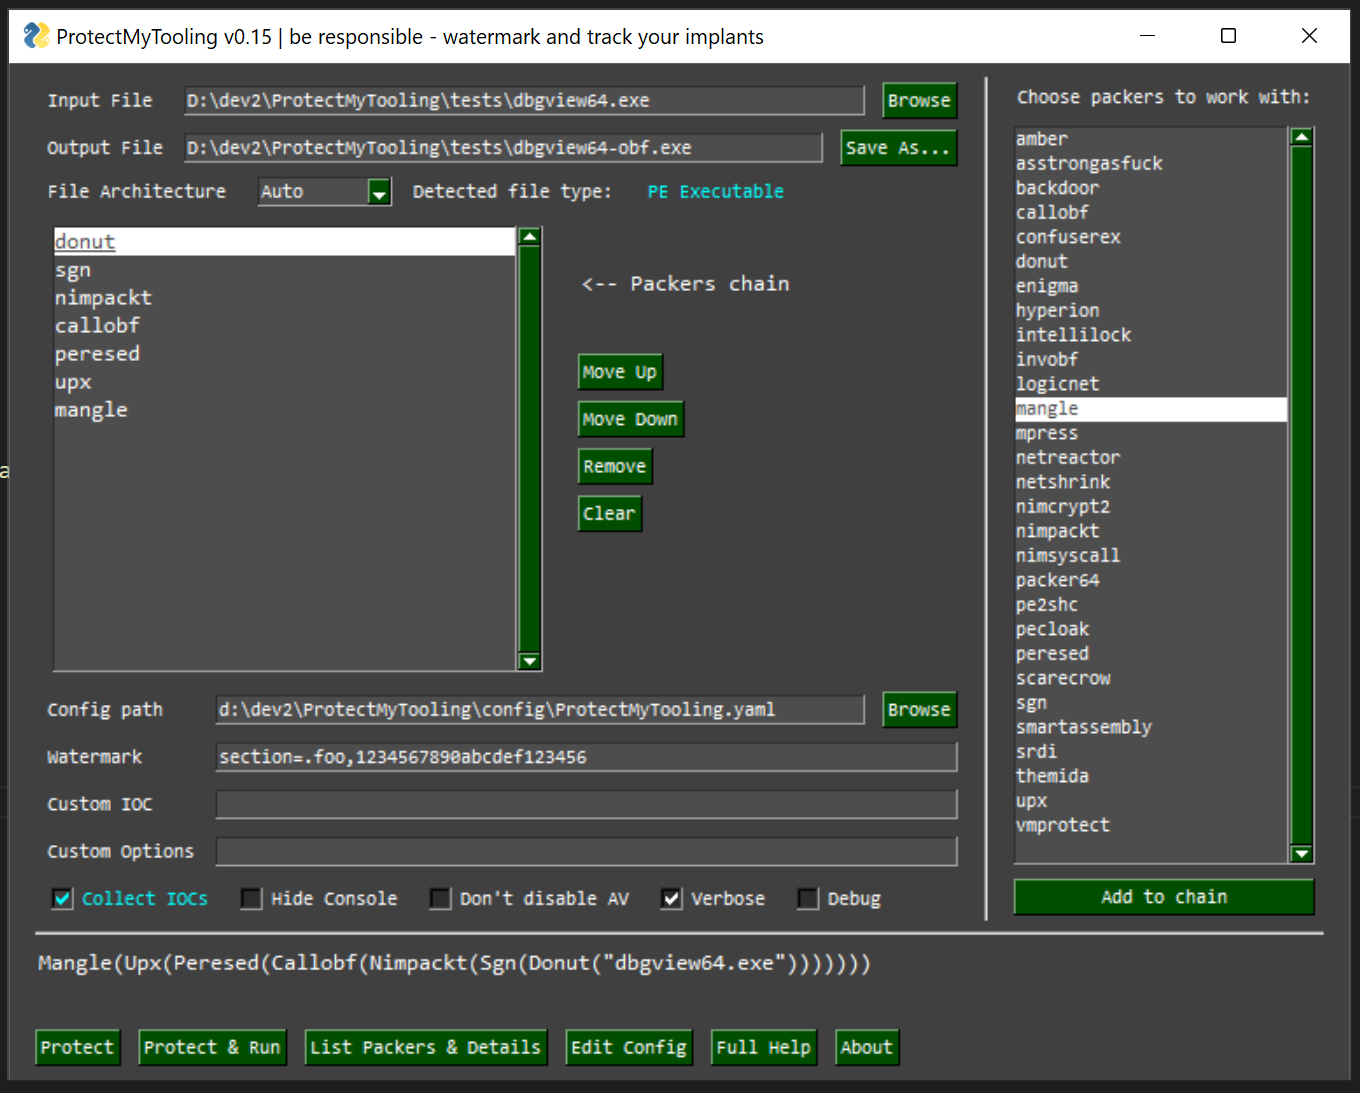 mgeeky/protectmytooling
Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
 khr0x40sh/macroshop
Collection of scripts to aid in delivering payloads via Office Macros. Most are python. See http://khr0x40sh.wordpress.com for details.
 hoodoer/js-tap
JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…
 ivan-sincek/powershell-reverse-tcp
PowerShell scripts for communicating with a remote host.
 kleiton0x00/redditc2
Abusing Reddit API to host the C2 traffic, since most of the blue-team members use Reddit, it might be a great way to make the traffic look legit.
 m4sc3r4n0/avoidz
Avoidz tool to bypass most A.V softwares
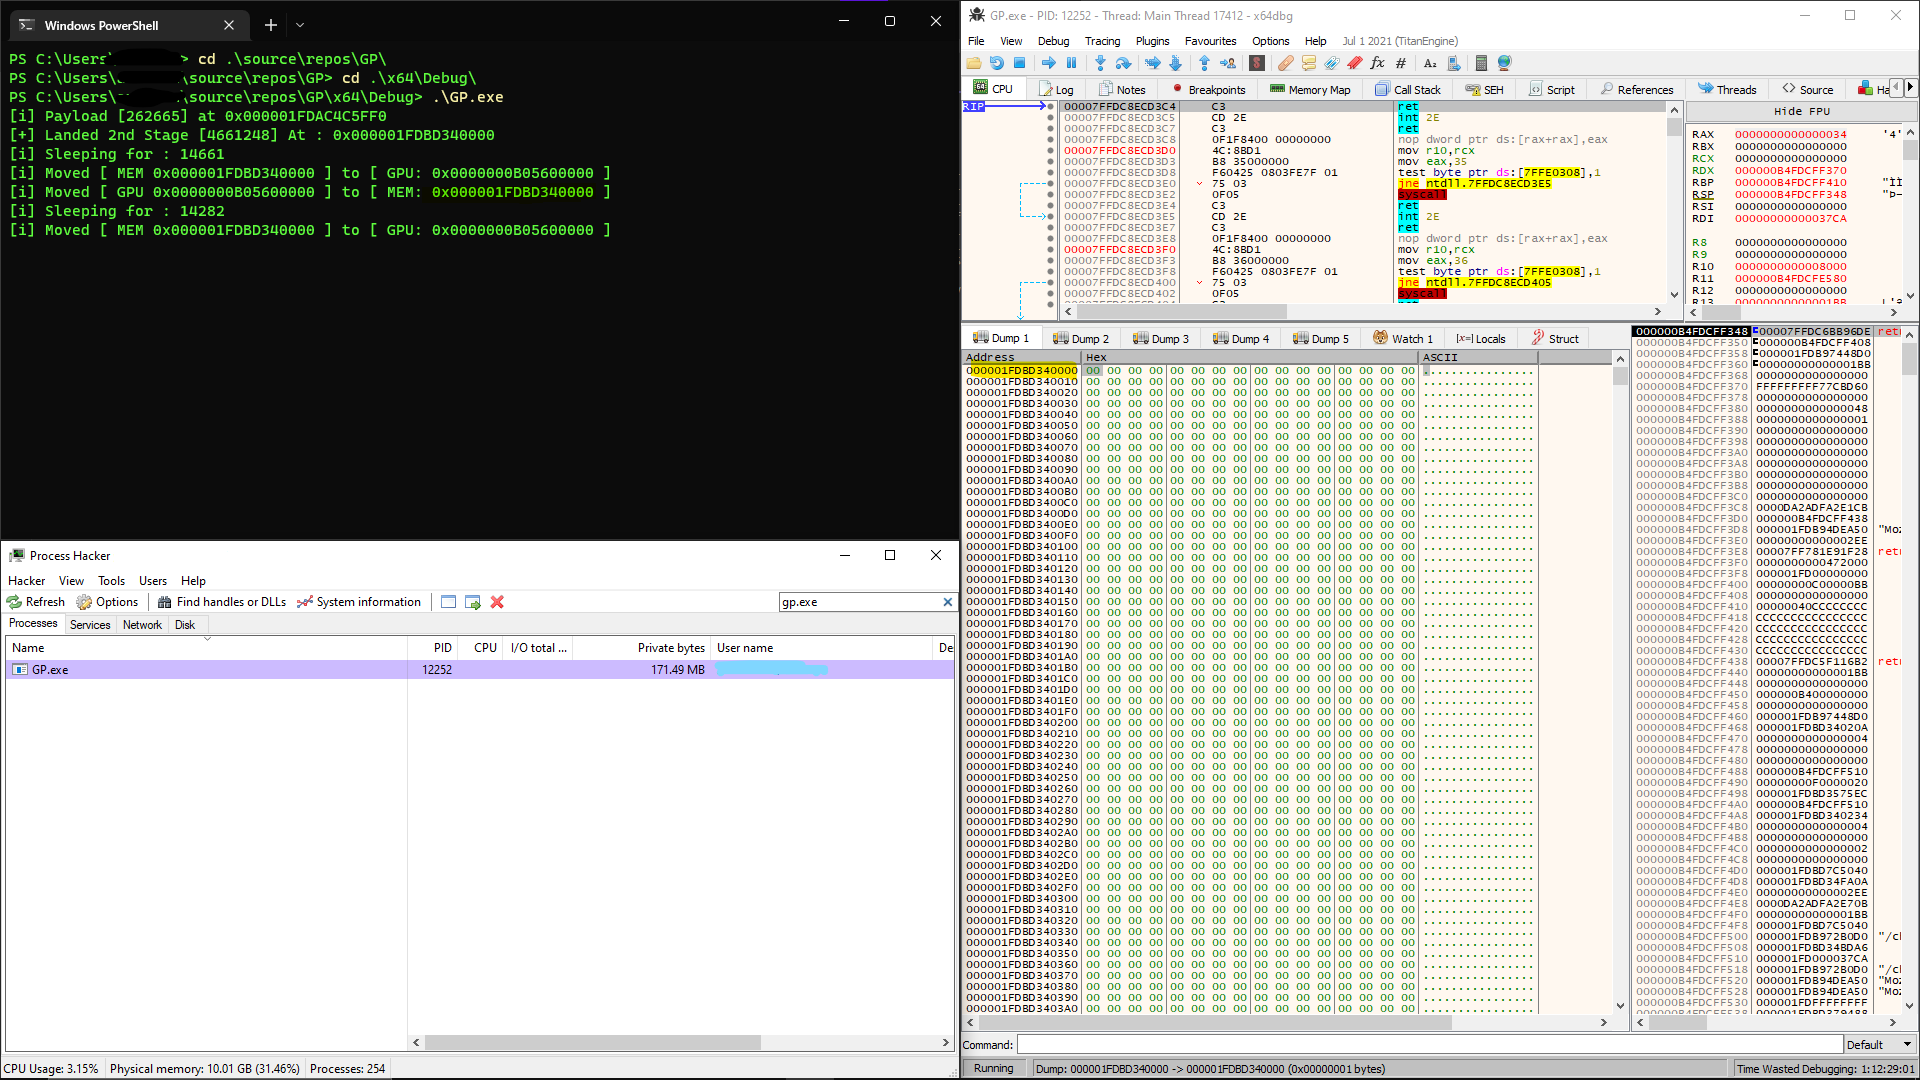 h1d3r/gpu_shellcode
Hides reflective payloads in GPU memory via CUDA APIs, wiping host memory during sleep and using a VEH handler to restore executable memory, evading…
 enelg52/kittystager
KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…
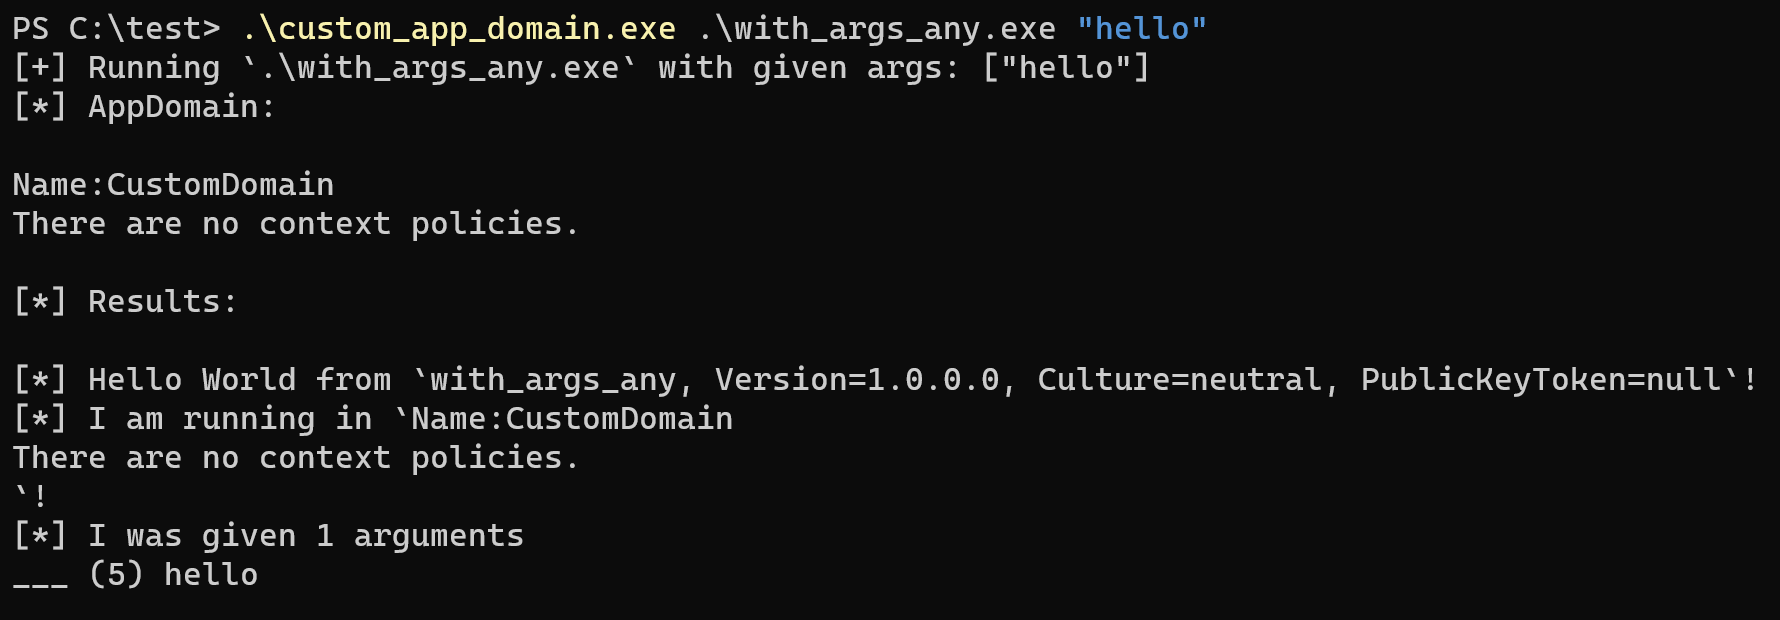 yamakadi/clroxide
A rust library that allows you to host the CLR and execute dotnet binaries.
 h3xduck/umbra
A LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.