
CVE-2021-31166
 mauricelambert/cve-2021-31166
CVE-2021-31166: exploitation with Powershell, Python, Ruby, NMAP and Metasploit.
exploitationexploit-frameworkspayload-development+4
6
mauricelambert/cve-2021-31166CVE-2021-31166: exploitation with Powershell, Python, Ruby, NMAP and Metasploit.
 joshuavanderpoll/cve-2026-44262
Unauthenticated RCE in dedoc/scramble — PoC, Nmap NSE & Nuclei template.
 nulltrace1336/samba-exploit-cve-2007-2447
Step-by-step guide to exploiting Samba 3.0.20 (CVE-2007-2447) using Metasploit, including Nmap scanning, payload setup, and reverse shell execution.
 ethicalhackinglabs/metasploitable2-exploitation-metasploit
Full Metasploit exploitation walkthrough against Metasploitable2 — vsftpd backdoor, Samba CVE-2007-2447, UnrealIRCd backdoor, Netcat exfiltration,…
 showy-headteacher114/cve-2025-66398
Demonstrate exploitation of Signal K Server CVE-2025-66398 allowing unauthenticated attackers to inject backdoor and enable remote code execution.
 joshuavanderpoll/cve-2025-66398
CVE-2025-66398 — Signal K Server ≤ 2.18.0 RCE PoC
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
 infosecn1nja/red-teaming-toolkit
This repository contains cutting-edge open-source security tools (OST) for a red teamer and threat hunter.
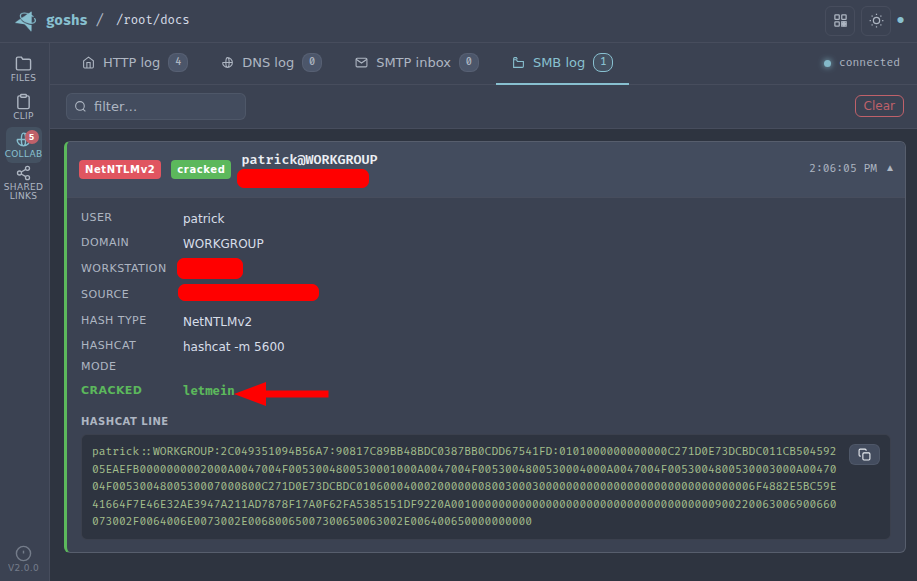 a-poc/redteam-tools
Tools and Techniques for Red Team / Penetration Testing
 brucedevices/firmware
Predatory ESP32 Firmware
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 k8gege/k8tools
K8工具合集(内网渗透/提权工具/远程溢出/漏洞利用/扫描工具/密码破解/免杀工具/Exploit/APT/0day/Shellcode/Payload/priviledge/BypassUAC/OverFlow/WebShell/PenTest) Web GetShell…
 zhzyker/exphub
Exphub[漏洞利用脚本库] 包括Webloigc、Struts2、Tomcat、Nexus、Solr、Jboss、Drupal的漏洞利用脚本,最新添加CVE-2020-14882、CVE-2020-11444、CVE-2020-10204、CVE-2020-10199、CVE-2020-1938…
 hackerschoice/thc-tips-tricks-hacks-cheat-sheet
Various tips & tricks
 samugit83/redamon
Autonomous AI red team framework that chains reconnaissance, exploitation, and post-exploitation into a single pipeline, then triages findings,…
 rogandawes/p4wnp1_aloa
P4wnP1 A.L.O.A. by MaMe82 is a framework which turns a Rapsberry Pi Zero W into a flexible, low-cost platform for pentesting, red teaming and…
 botesjuan/burp-suite-certified-practitioner-exam-study
Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.