
Exploit-Win32.CVE-2017-0147.A
 robertoleonfr-es/exploit-win32.cve-2017-0147.a
the name of virus is the detection of microsoft defender, is the tipic antivirus
exploitationpayload-developmentpenetration-testing+2
robertoleonfr-es/exploit-win32.cve-2017-0147.athe name of virus is the detection of microsoft defender, is the tipic antivirus
 nika0x38/cve-2017-7269
A Rust implementation of the POC for CVE-2017-7269, targeting the WebDAV service in Microsoft Internet Information Services (IIS) 6.0.
 mazx0p/mssqlbof
A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself
 simoesctt/ctt-exchange-rce-v1.0---microsoft-exchange-exploit-cvss-10.0-critical-cve-2021-26855-cve-2021-27065
CTT-enhanced version of the Microsoft Exchange Server SSRF to RCE exploit (ProxyShell/ProxyLogon), another CVSS 10.0 critical vulnerability that…
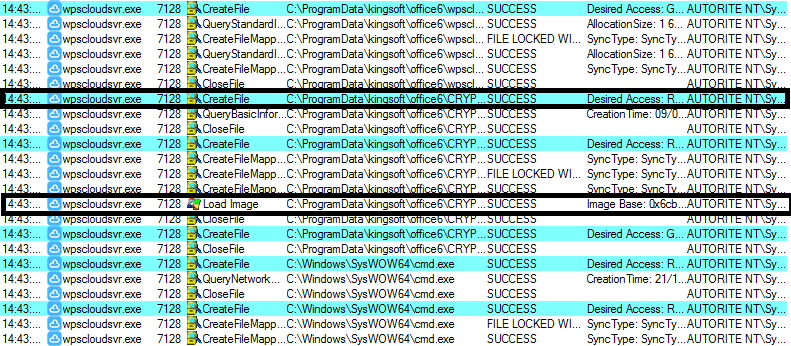 hadimed/kingsoft-wps-office-lpe
CVE-2022-25943
 xm0kht4r/ven0m-ransomware
Fully undetectable and evasive ransomware written in Rust, leveraging a BYOVD technique to disable AV/EDR solutions on the infected systems.
 hv0l/cve-2023-21716_exploit
Proof-of-concept exploit for CVE-2023-21716, a critical remote code execution vulnerability in Microsoft Word. Demonstrates exploitation of the…
 denchief1/cve-2017-7269
C# implementation of CVE-2017-7269 exploit for Microsoft IIS WebDAV remote code execution. Designed for penetration testing and vulnerability…
 d0rb/cve-2024-21388
This Python script exploits a vulnerability (CVE-2024-21388) in Microsoft Edge, allowing silent installation of browser extensions with elevated…
 xaitax/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Microsoft-Outlook-Remote-Code-Execution-Vulnerability
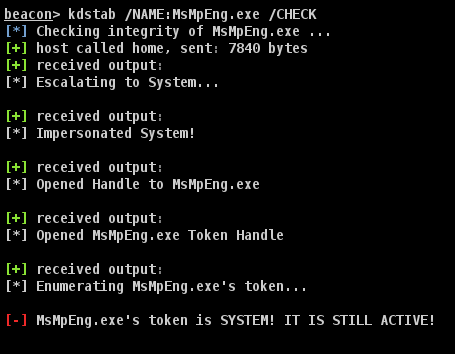 octoberfest7/kdstab
BOF combination of KillDefender and Backstab
 shadowforge-cyber/cve-2026-65660-poc
Malicious Register Directive Code Injection Exploit
 hackfaiz/cve-2026-20841-poc
Proof of concept demonstrating command execution in Microsoft Notepad via crafted files, enabling arbitrary code execution and system compromise.
 nccgroup/cve-2017-8759
NCC Group's analysis and exploitation of CVE-2017-8759 along with further refinements
 mahyarx/cve-2025-47176
Microsoft Outlook Remote Code Execution Vulnerability
 sailay1996/cve-2025-53772
poc for cve-2025-53772
 improvecybersecurityjaro/2022_poc-msdt-follina-cve-2022-30190
Proof of Concept zu MSDT-Follina - CVE-2022-30190. ÜBERPRÜFUNG DER WIRKSAMKEIT VON MICROSOFT DEFNEDER IN DER JEWEILS AKTUELLSTEN WINDOWS 10 VERSION.
 symbolexe/cve-2023-23397
CVE-2023-23397: Remote Code Execution Vulnerability in Microsoft Outlook