

Silverseal
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
binary-exploitationexploitationmalware-analysis+4
170
idov31/silversealLinux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 xtr4nge/fruityc2
FruityC2 is a post-exploitation (and open source) framework based on the deployment of agents on compromised machines. Agents are managed from a web…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 bishopfox/sliver
Adversary Emulation Framework
 hackernese/sneakyexe
Automatic UAC-Bypassing for custom payloads during privilege escalation testing
 infodox/tsh-sctp
TinySHell port to SCTP
 theandersmadsen/humane-aipin-ghostlock
Guarded, source-only Humane AI Pin root PoC for CVE-2026-43499
 nu11secur1ty/metasploit-framework-nu11secur1ty
Extending of metasploit-framework
 keraattin/cve-2026-35031
Critical path traversal to RCE vulnerability in Jellyfin Media Server (CVSS 9.9). Includes proof-of-concept exploit, technical analysis, and…
 error-inside/cve-2026-47670
Authenticated Remote Code Execution via loadReader functionName code injection in DbGate
 0x00pf/0x00sec_code
Educational repository of offensive security source code: remote shells, ELF injectors, crypters, memory injection, and droppers for Linux,…
 padsalatushal/cve-2011-2523
Python exploit for vsftpd 2.3.4 - Backdoor Command Execution
 rushikesh-a-bhujbal/cve-2011-2523
From-scratch exploit development in Python. No Metasploit. No frameworks. Raw socket-level implementation of real CVEs against authorized lab targets.
 lynk4/cve-2011-2523
Python exploit for vsftpd 2.3.4 - Backdoor Command Execution
 neargle/go-get-rce-cve-2018-6574-poc
CVE-2018-6574 POC : golang 'go get' remote command execution during source code build
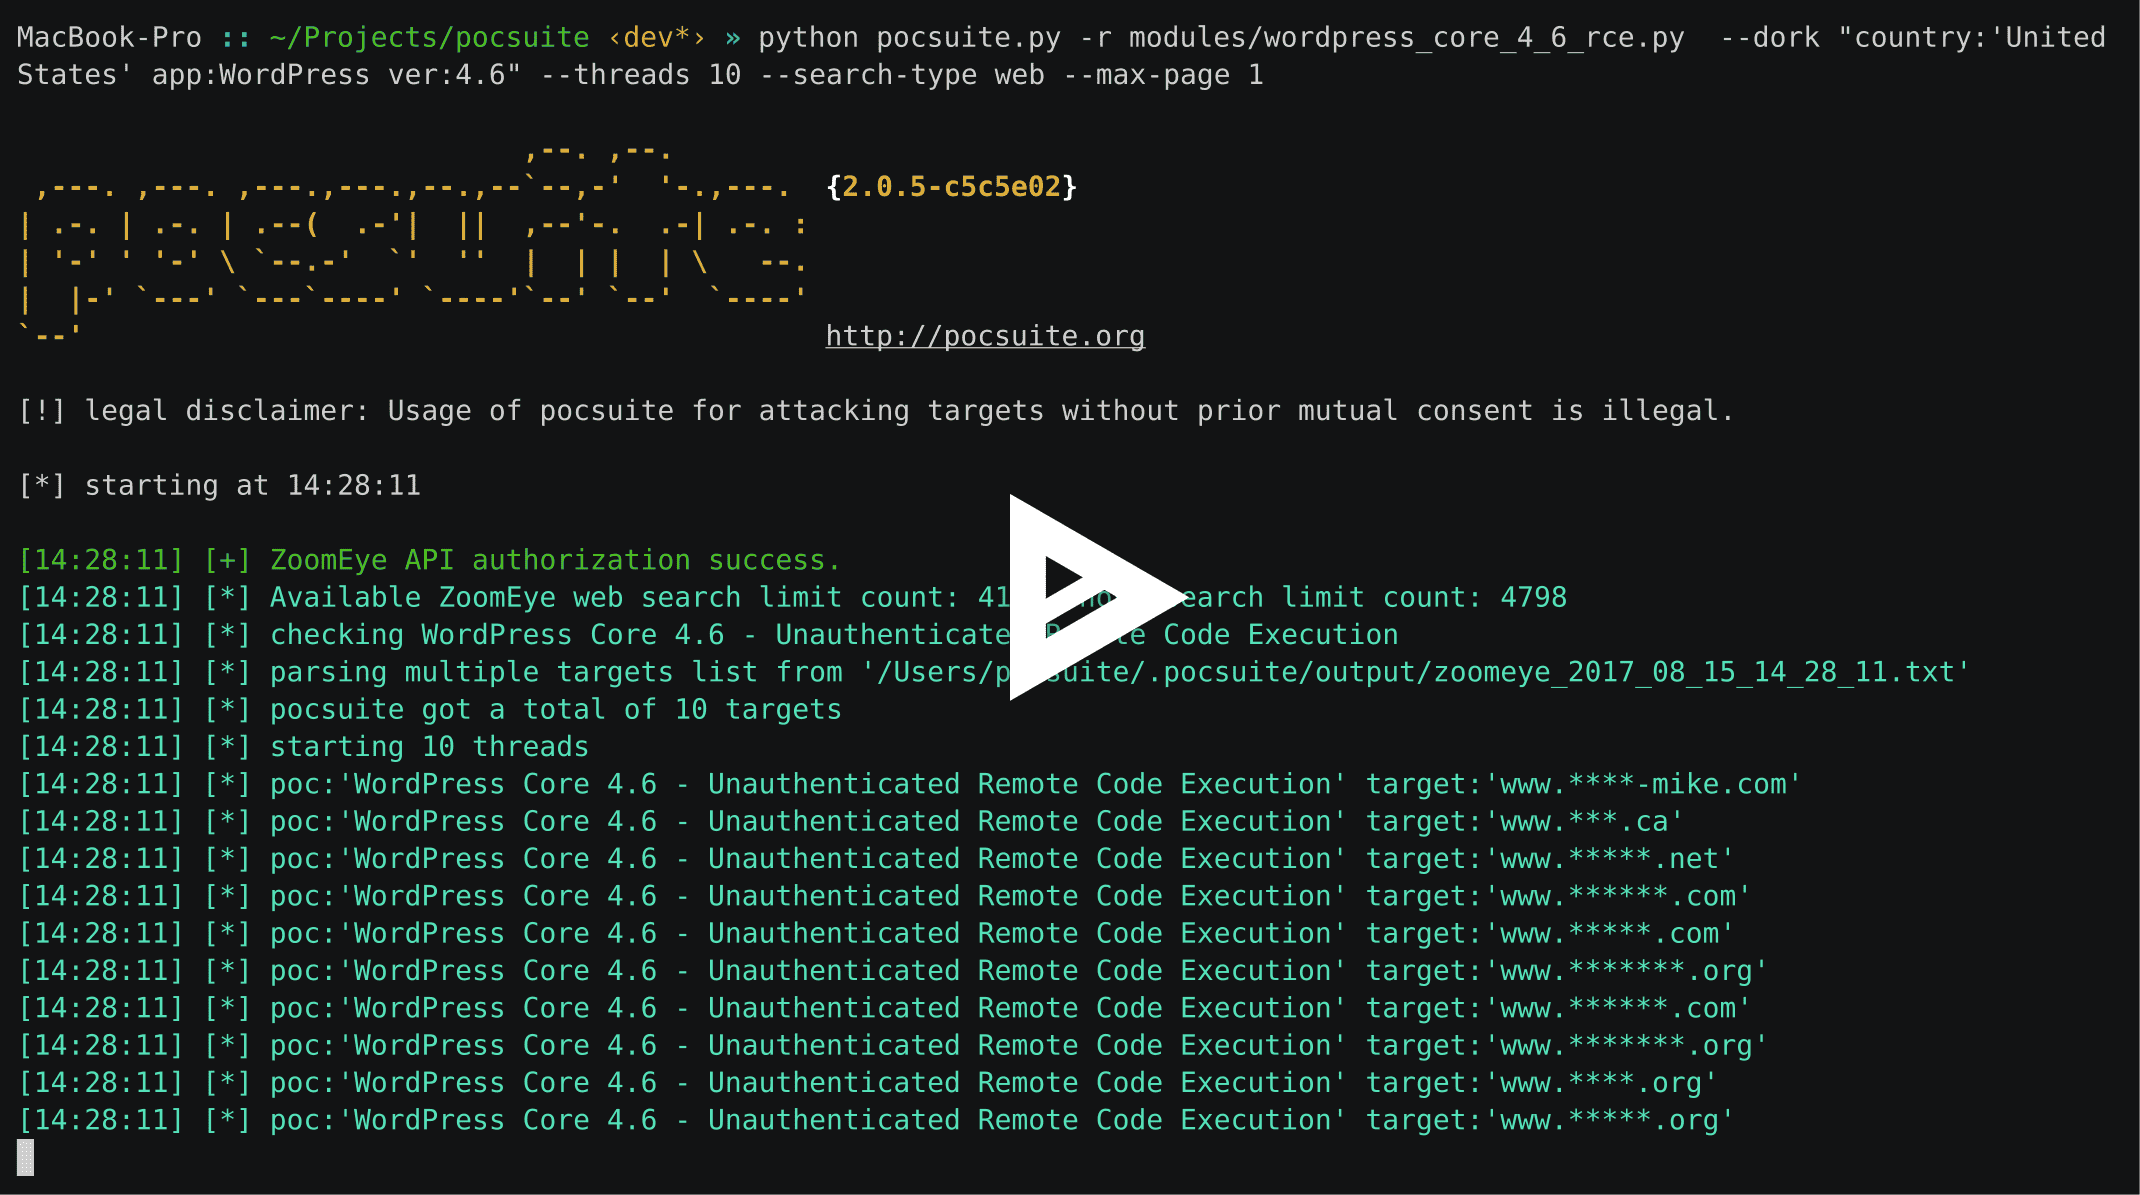 knownsec/pocsuite
This project has stopped to maintenance, please to https://github.com/knownsec/pocsuite3 project.
 lesnuages/hershell
Multiplatform reverse shell generator
 tarlogicsecurity/chankro
Herramienta para evadir disable_functions y open_basedir