
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Pocsuite — This project has stopped to maintenance, please to https://github.com/knownsec/pocsuite3 project. | Kitploit
Tools/GitHubGitHub/knownsec/pocsuite
Penetration Testing FrameworksExploit FrameworksVulnerability AnalysisPayload Development
GitHubknownsec/pocsuite

Pocsuite

This project has stopped to maintenance, please to https://github.com/knownsec/pocsuite3 project.

View Repository
1.8k591537 years agoReviewed by Kitploit
Website
Share

This project has stopped to maintenance, please to https://github.com/knownsec/pocsuite3 project.

Pocsuite

Python 2.6|2.7 License Twitter build

Overview

Pocsuite is an open-sourced remote vulnerability testing and proof-of-concept development framework developed by the Knownsec 404 Team. It comes with a powerful proof-of-concept engine, many niche features for the ultimate penetration testers and security researchers.
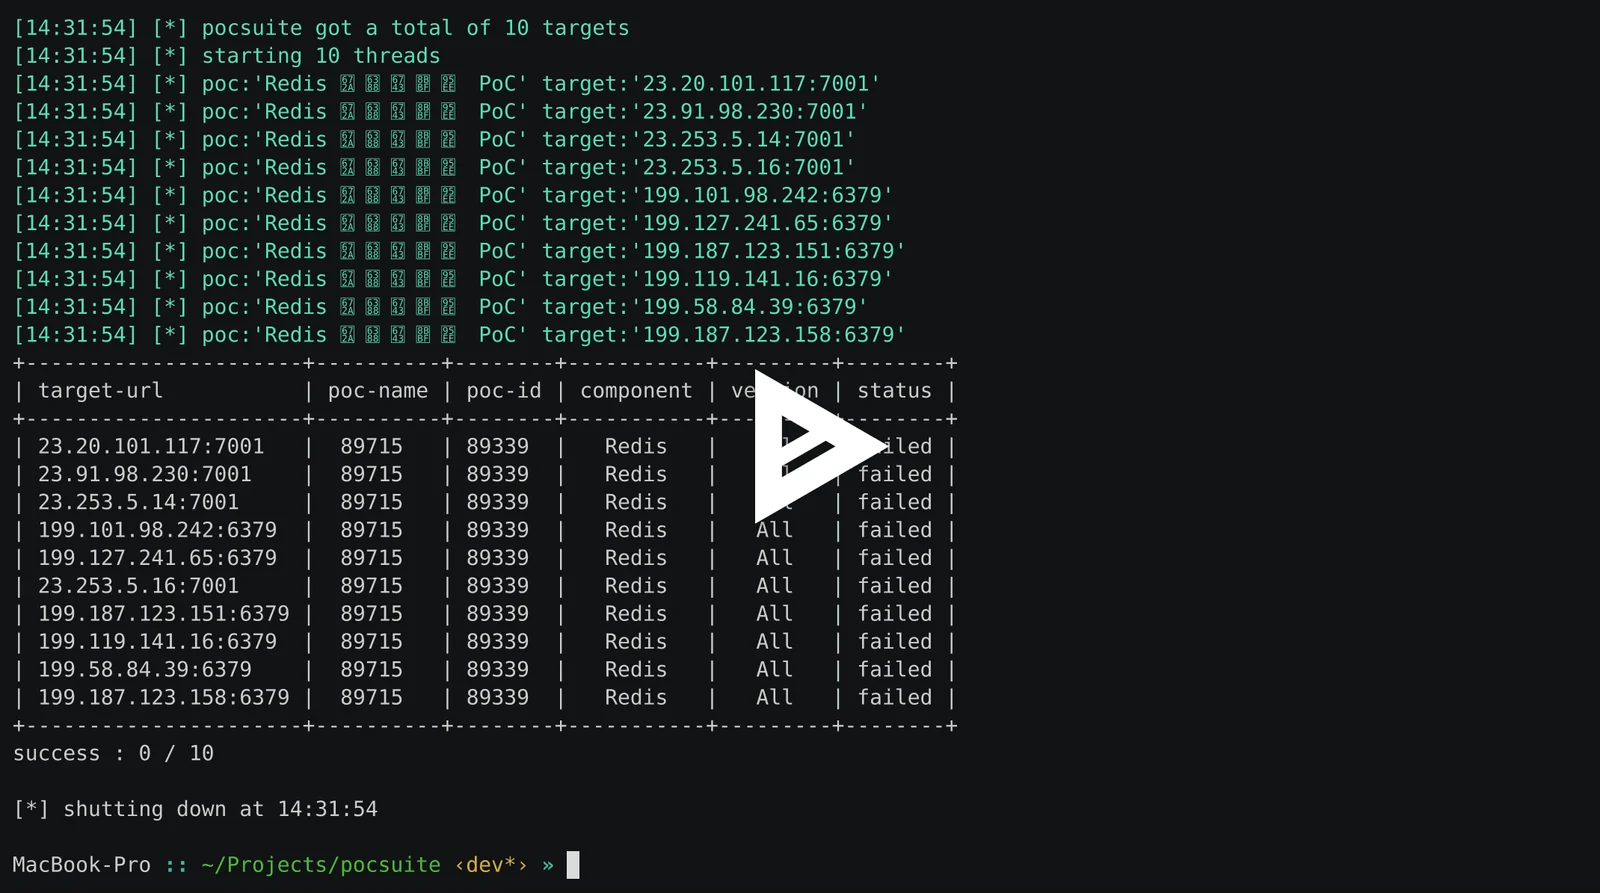
How to use

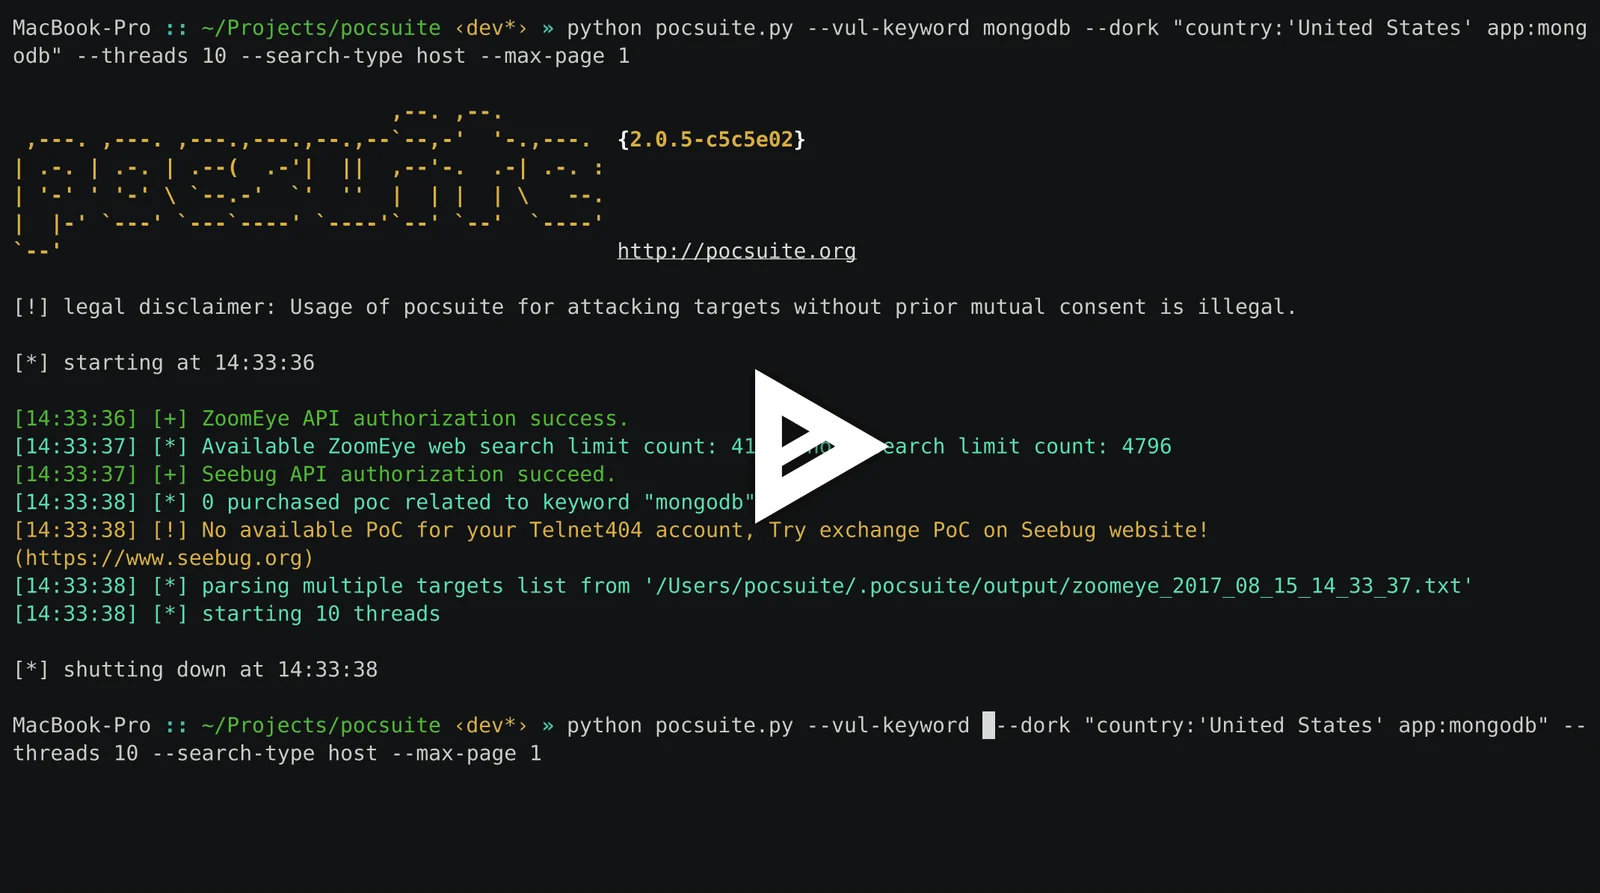
Pocsuite with seebug PoC search and zoomeye dork

asciicast

Pocsuite with seebug PoC and zoomeye dork

asciicast

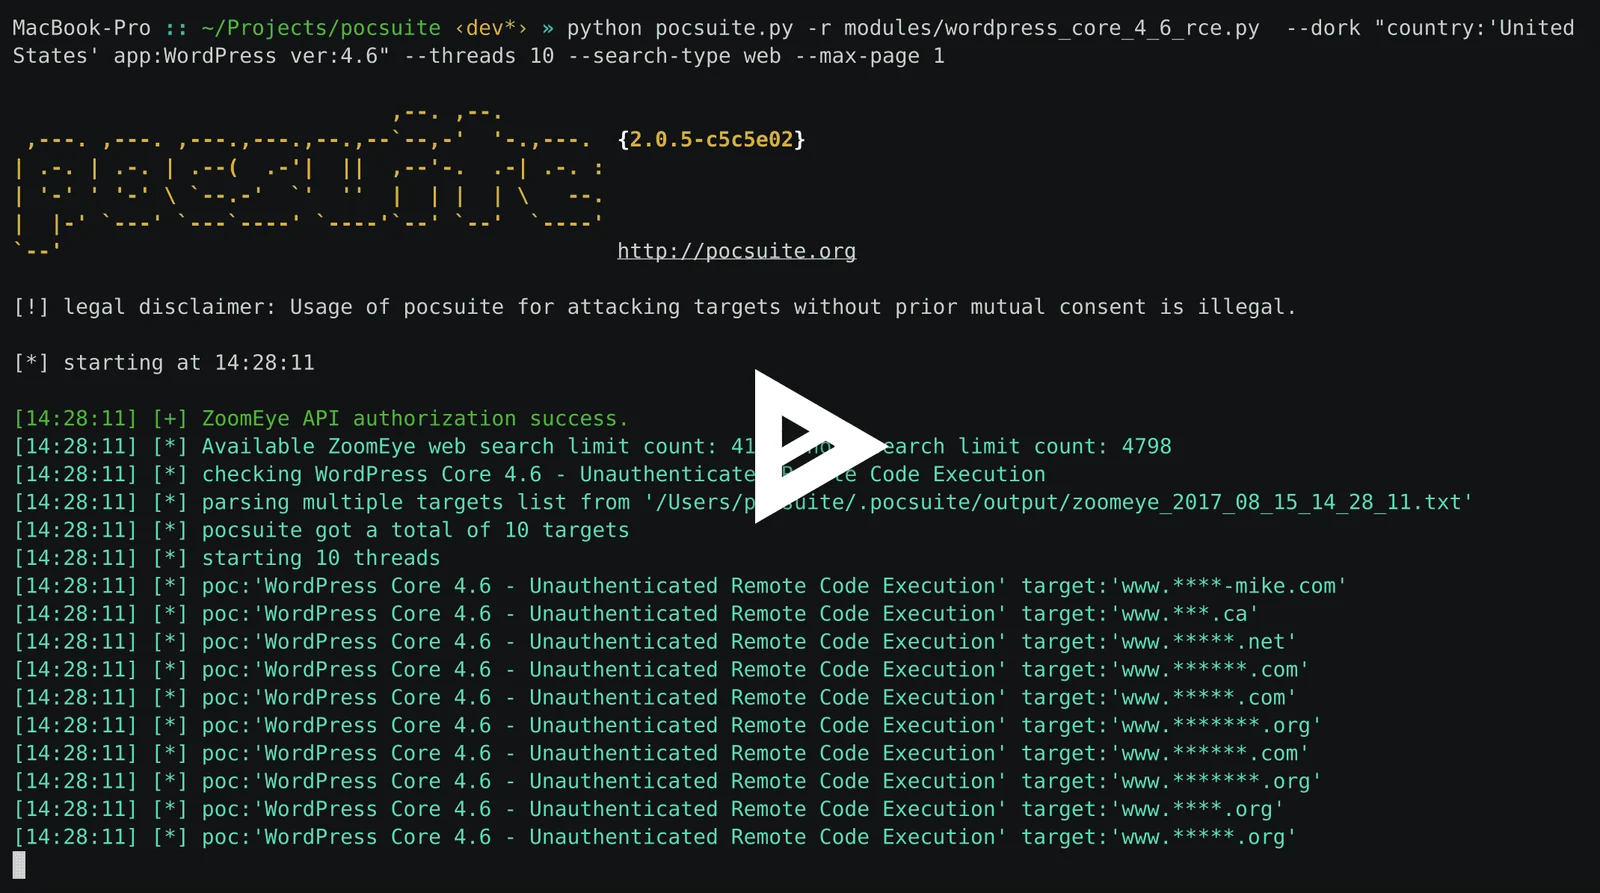
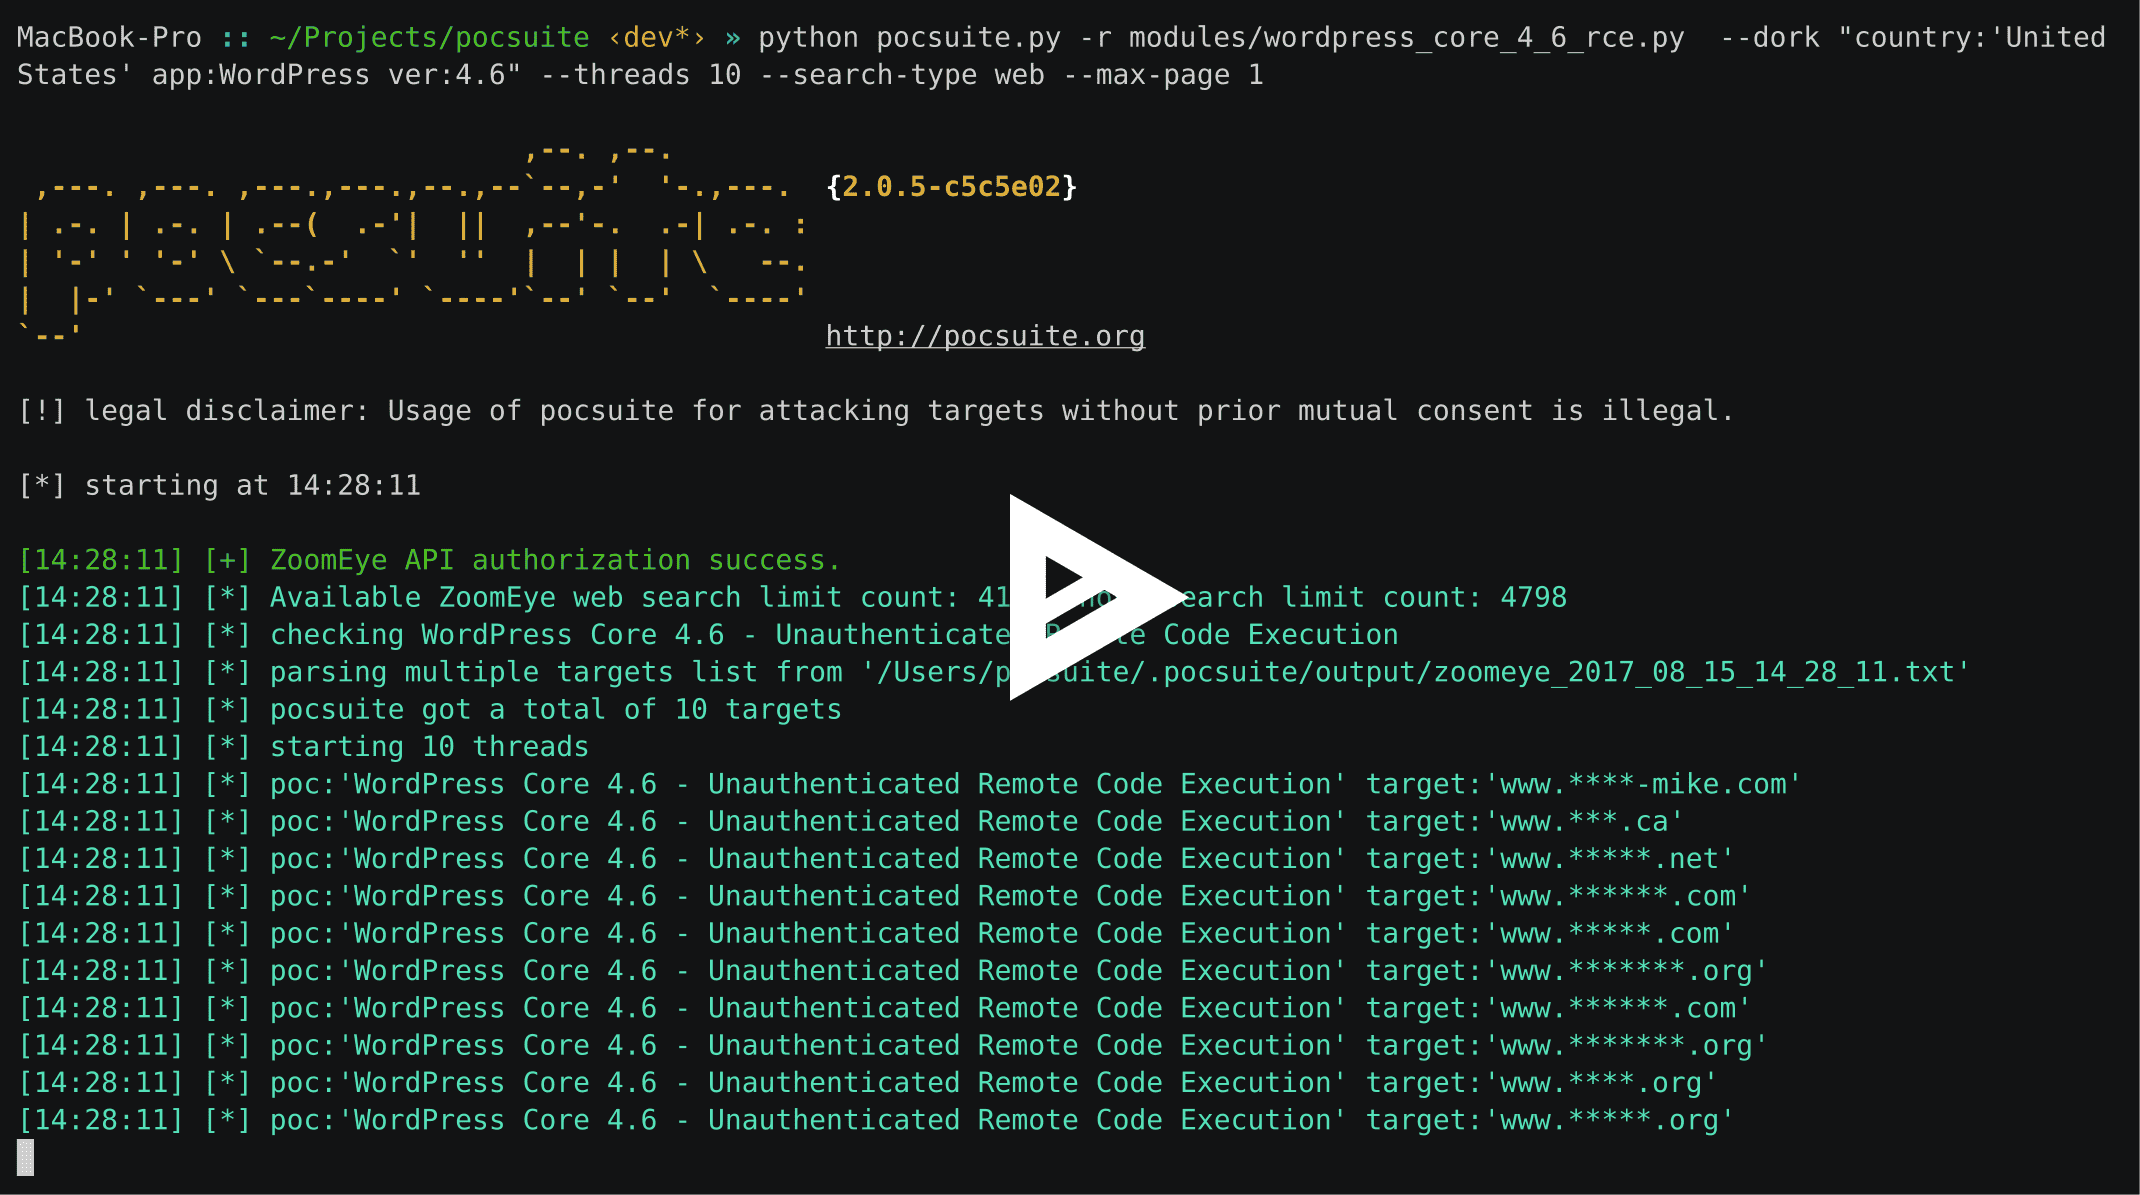
Pocsuite with zoomeye API

asciicast

Pocsuite with seebug PoC API online

asciicast

Requirements

  • Python 2.6+
  • Works on Linux, Windows, Mac OSX, BSD

Installation

The quick way:

$ pip install pocsuite

Or click here to download the latest source zip package and extract

$ wget https://github.com/knownsec/Pocsuite/archive/master.zip
$ unzip master.zip

The latest version of this software is available from: http://pocsuite.org

Documentation

Documentation is available in the english docs / chinese docs directory.

How to Contribute

  1. Check for open issues or open a fresh issue to start a discussion around a feature idea or a bug.
  2. Fork the repository on GitHub to start making your changes to the dev branch (or branch off of it).
  3. Write a test which shows that the bug was fixed or that the feature works as expected.
  4. Send a pull request and bug the maintainer until it gets merged and published. Make sure to add yourself to THANKS.

Links

  • Thanks List
  • Change Log
  • Bug tracking
  • Copyright
  • Pocsuite
  • Seebug
  • ZoomEye
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    795
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    520
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    439
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    267
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    264

Explore all tools

Browse our collection of tools

View all tools →