
SneakyEXE
 hackernese/sneakyexe
Automatic UAC-Bypassing for custom payloads during privilege escalation testing
exploitationpayload-developmentprivilege-escalation+1
974 years ago
hackernese/sneakyexeAutomatic UAC-Bypassing for custom payloads during privilege escalation testing
 beefproject/beef
The Browser Exploitation Framework Project
 tennc/webshell
This is a webshell open source project
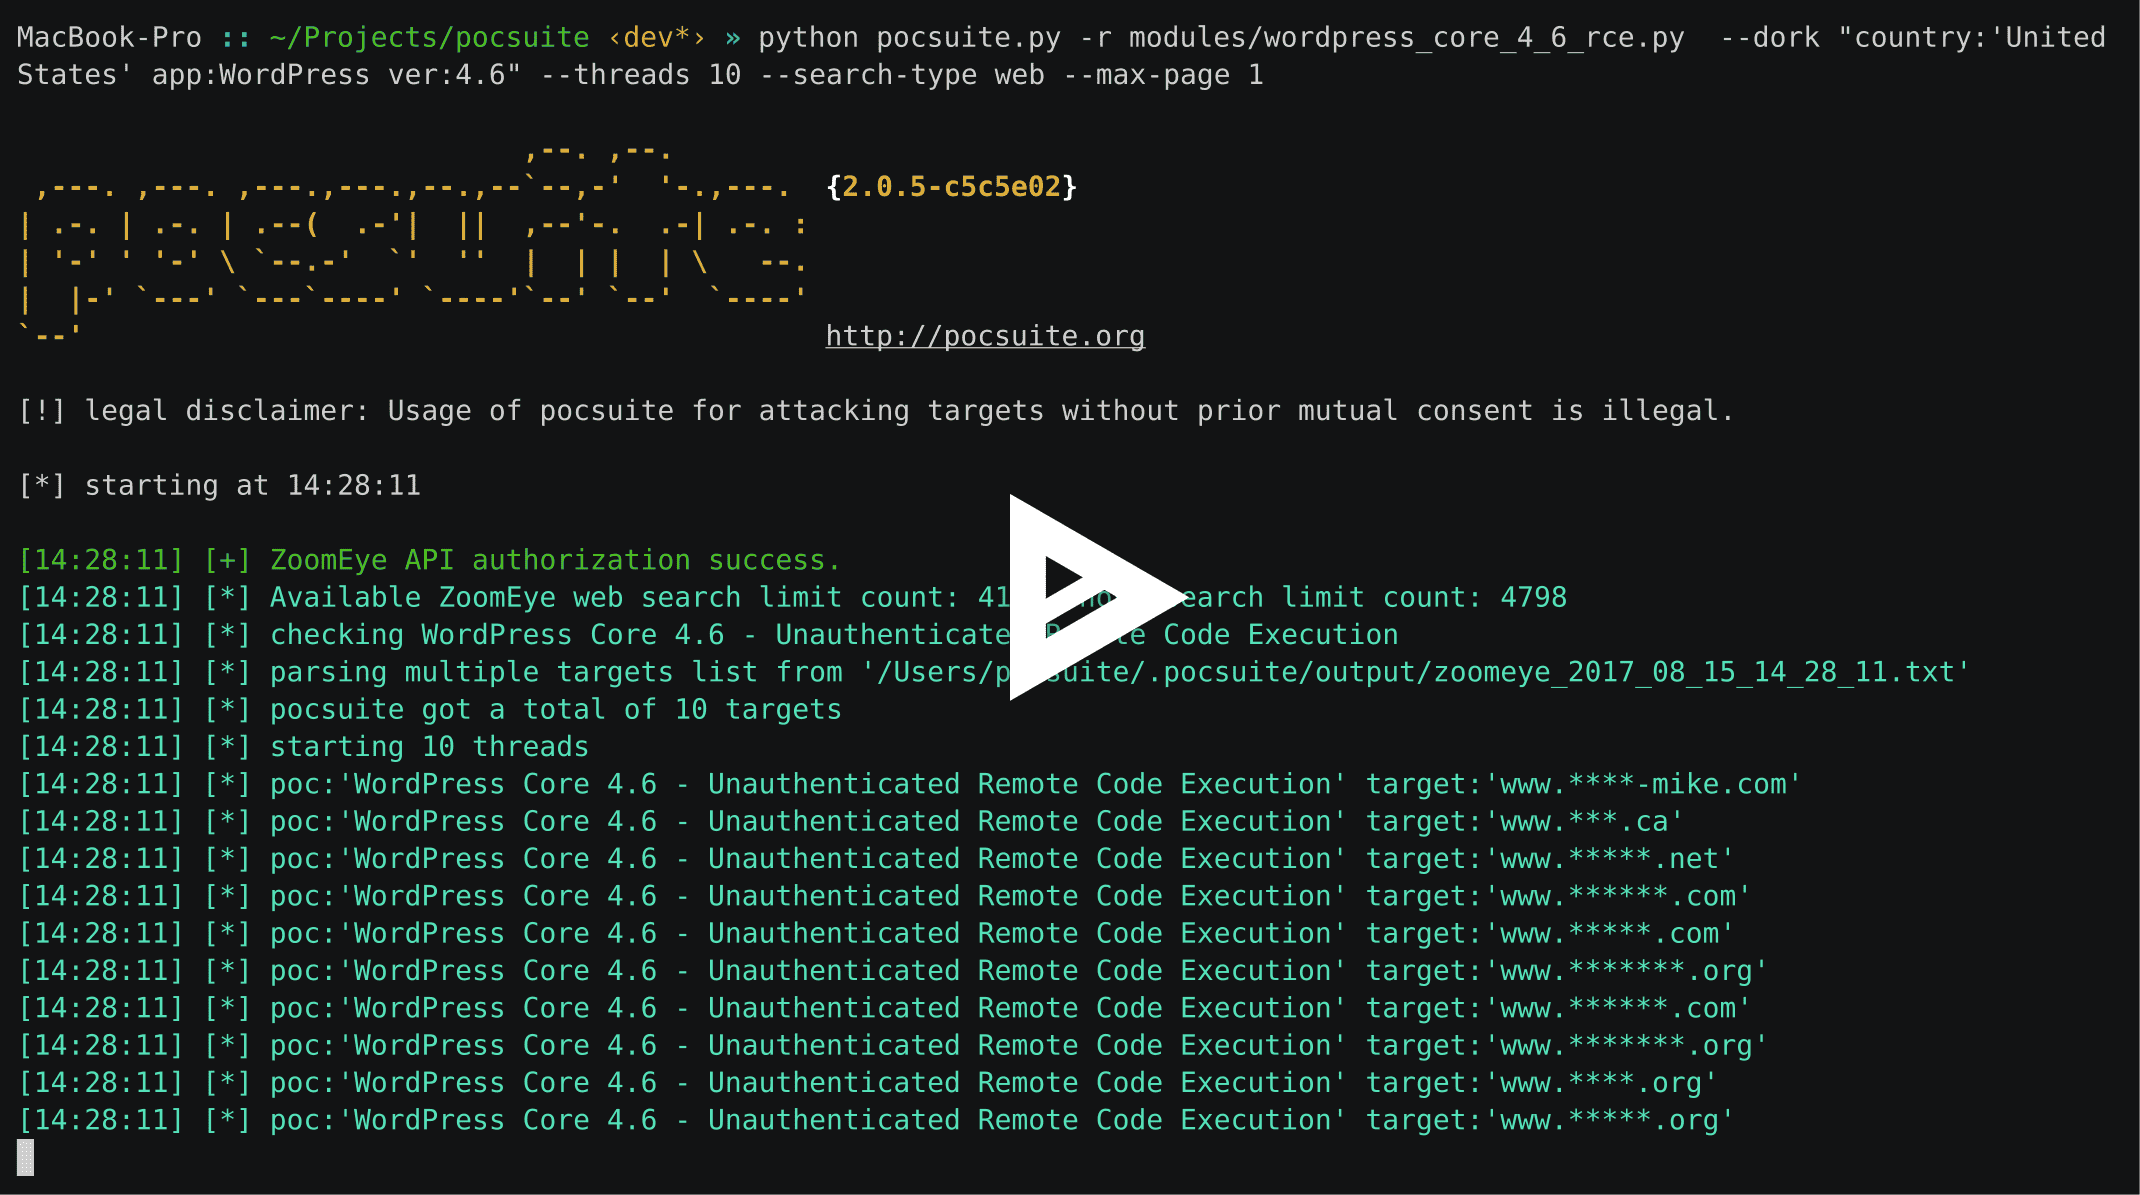 knownsec/pocsuite
This project has stopped to maintenance, please to https://github.com/knownsec/pocsuite3 project.
 secrary/injectproc
InjectProc - Process Injection Techniques [This project is not maintained anymore]
 r3nhat/grat2
We developed GRAT2 Command & Control (C2) project for learning purpose.
 cerbersec/ares
Project Ares is a Proof of Concept (PoC) loader written in C/C++ based on the Transacted Hollowing technique
 enelg52/kittystager
KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…
 s3n4t0r-0x0/pixelcode-attack
Malicious PixelCode is a security research project that demonstrates a covert technique for encoding executable files into pixel data and storing…
 cobalt-strike/sleep_python_bridge
This project is 'bridge' between the sleep and python language. It allows the control of a Cobalt Strike teamserver through python without the need…
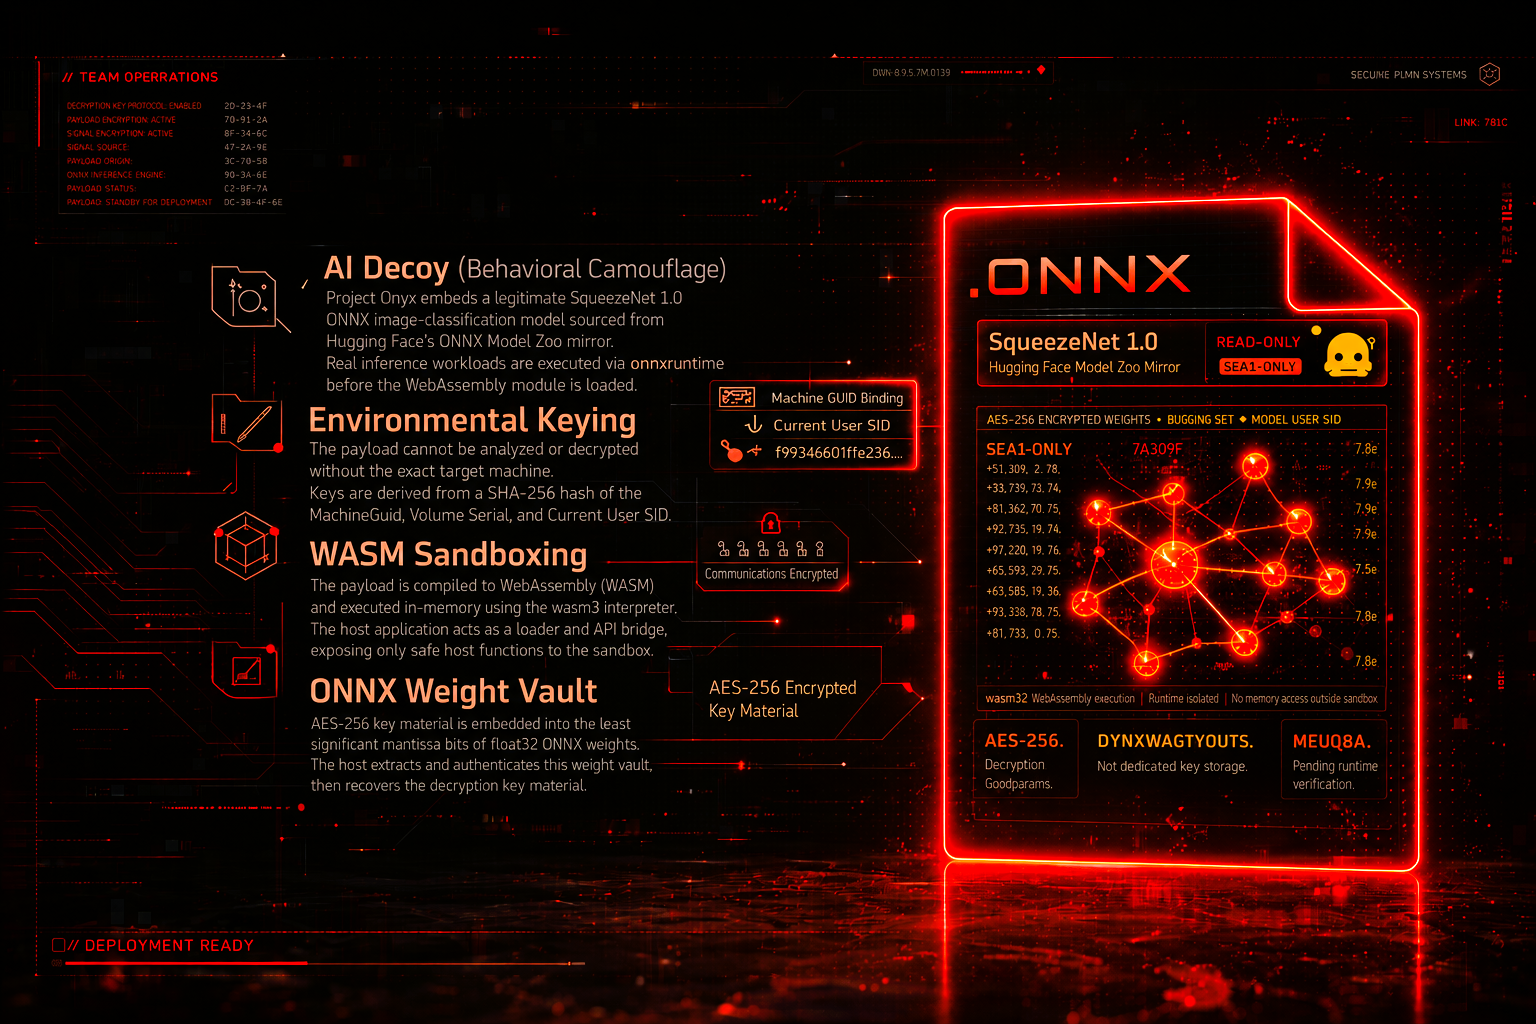 x-3306/project-onyx
Advanced EDR Evasion via AI Telemetry Spoofing & WASM Sandboxing. Project Onyx is a PoC Red Team pipeline designed to demonstrate advanced evasion…
 rasta-mouse/cswhispers
Source generator to add D/Invoke and indirect syscall methods to a C# project.
 bishopfox/asminject
Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…
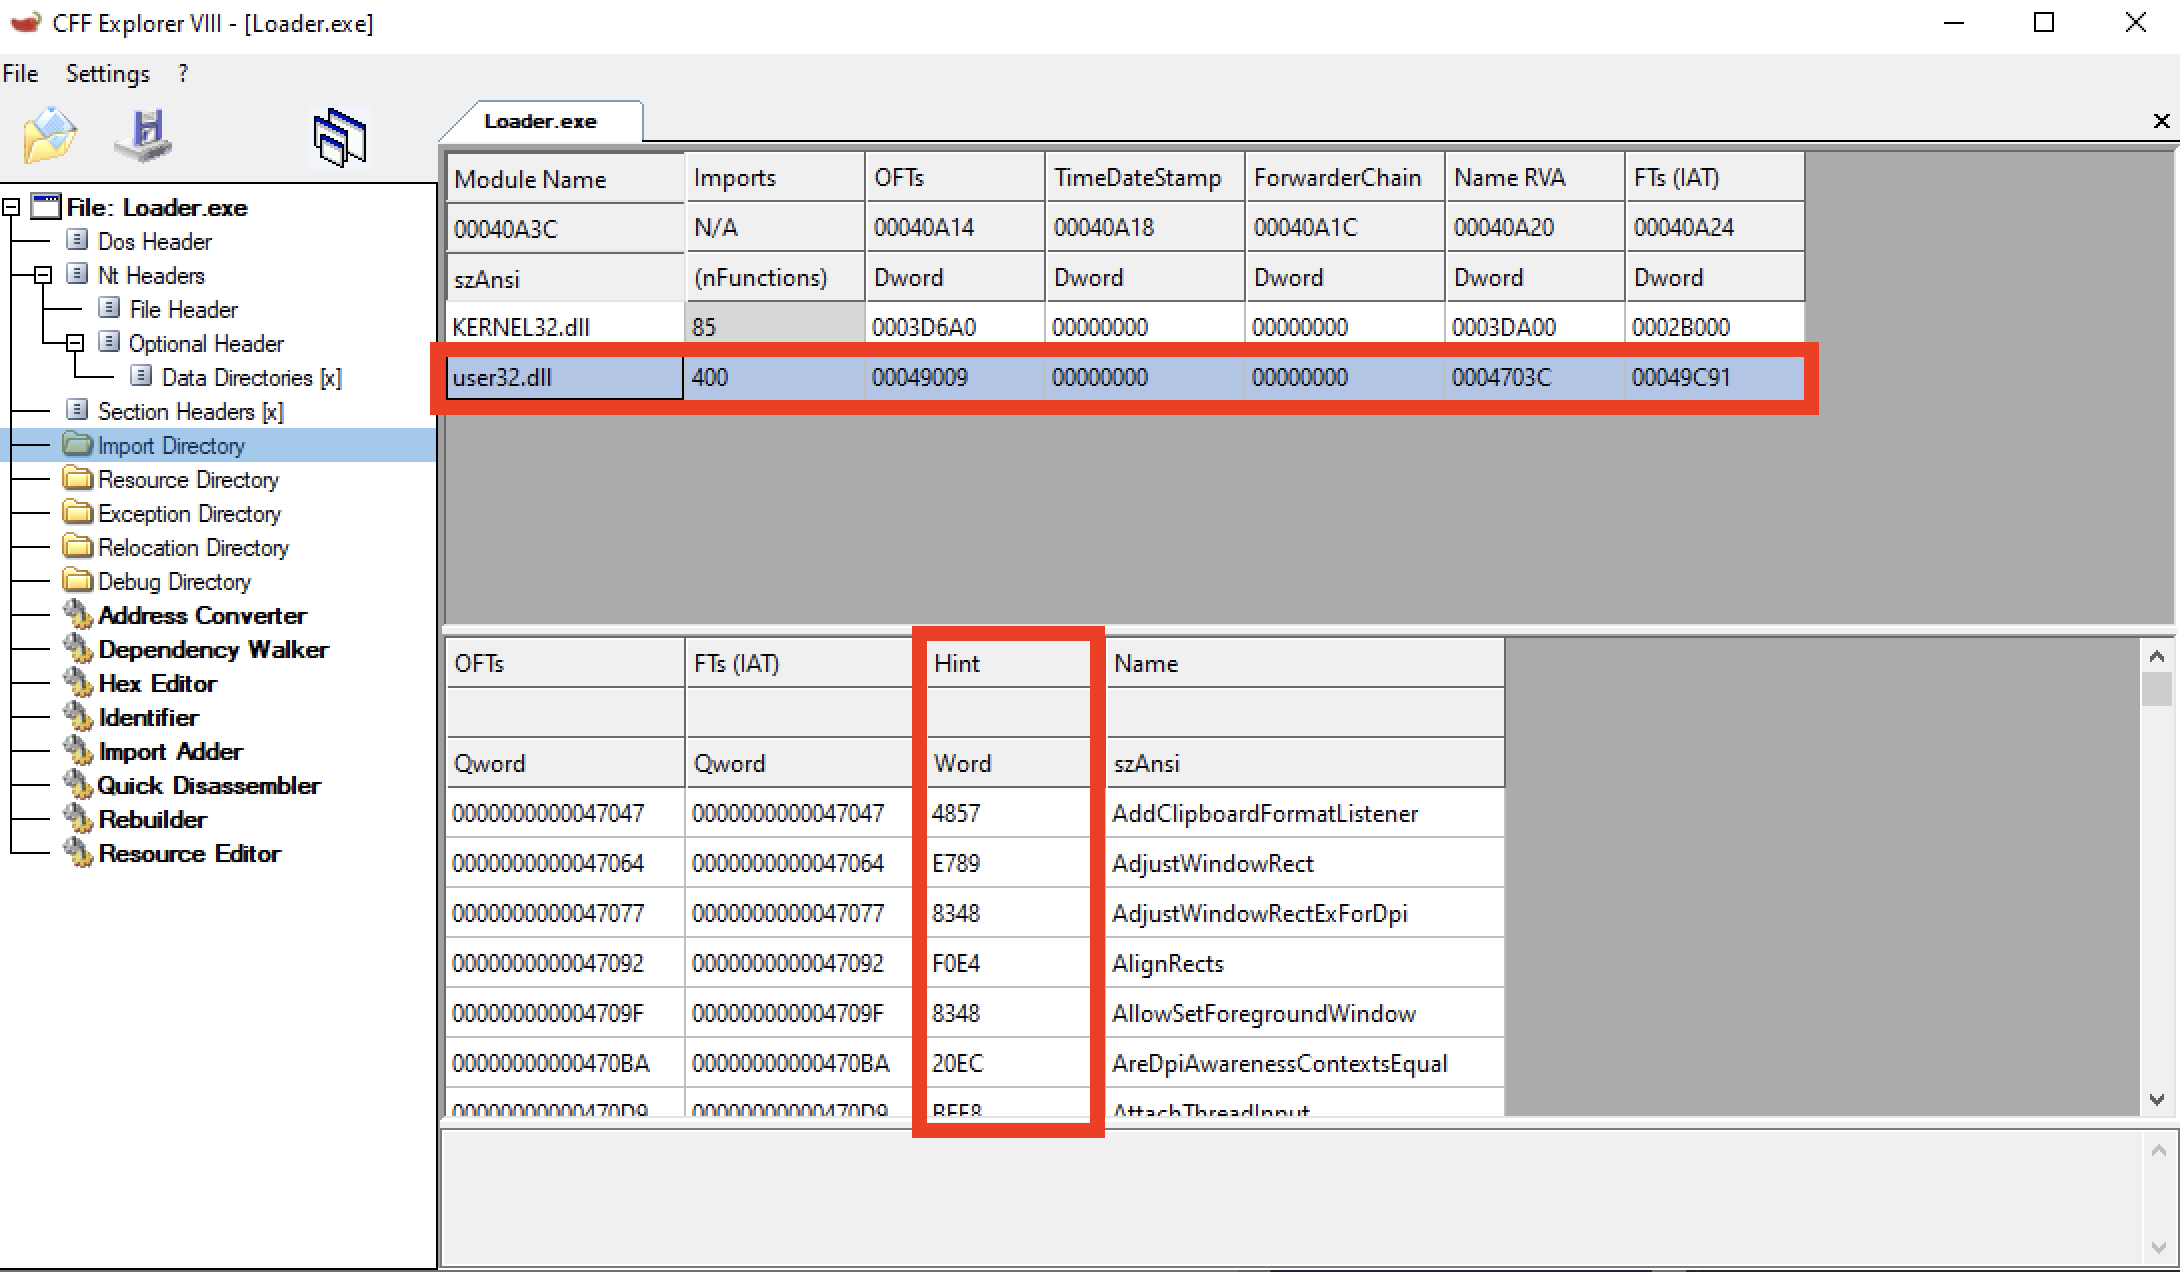 frkngksl/hintinject
A PoC project for embedding shellcode to Hint/Name Table
 bc-security/ironsharppack
IronSharpPack is a repo of popular C# projects that have been embedded into IronPython scripts that execute an AMSI bypass and then reflective load…
 octoberfest7/dscourier_bof
BOF POC of the DSCourier project / invoking WinGet via COM
 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…
 traitimtrongvag/android-imgui-template
A complete Android ImGui menu template project.