
CVE-2026-58424
A flaw in Gitea Open Source Git Server’s approval‑gate logic allows a pull request that originates from a permanent fork to merge without satisfying…

A flaw in Gitea Open Source Git Server’s approval‑gate logic allows a pull request that originates from a permanent fork to merge without satisfying…

Extended kernel lazy importer for Windows drivers that resolves APIs at runtime with encrypted, cached import names to hide kernel function usage…

PoC exploit for CVE-2025-47917: Use-After-Free in mbedTLS leading to remote code execution.

CVE-2023-51518: Preauthenticated Java Deserialization via JMX in Apache James

CVE-2026-50343 InstallService StaticPluginMap EoP - standard user to SYSTEM

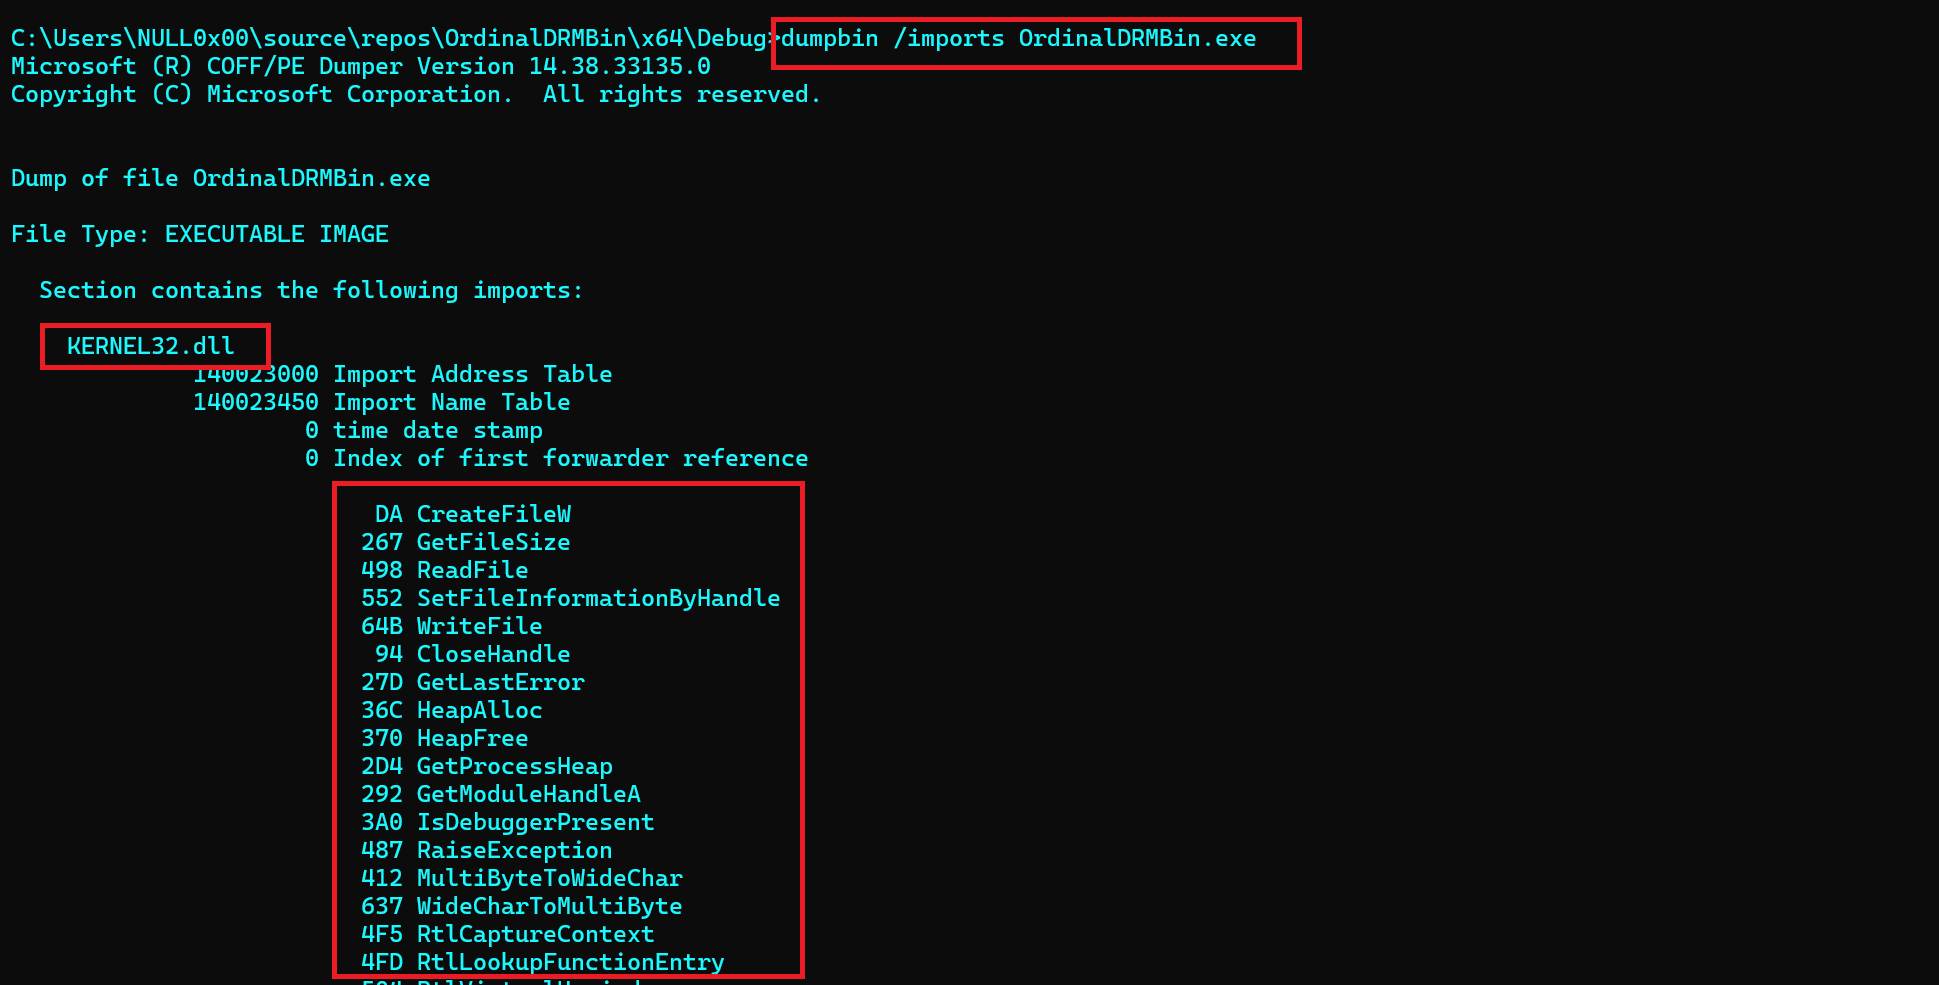
Create Anti-Copy DRM Malware

PoC for persisting .NET payloads in Windows Notification Facility (WNF) state names using low-level Windows Kernel API calls.

Generates initial access payloads abusing AddInProcess.exe via .NET deserialization, supporting HTA, VBA, JS, and CHM templates for in-memory code…

PoC Java exploit based on http://www.contextis.com/research/blog/java-pwn2own/

Automating the exploitation of CVE-2026-7299 - Stored XSS via Database Table/Column Names in SQL Autocomplete within Appsmith =>1.99. Initial…

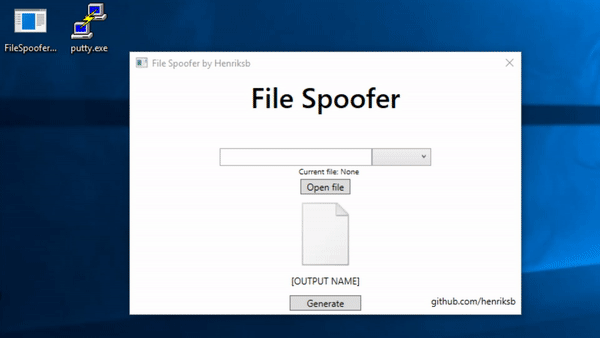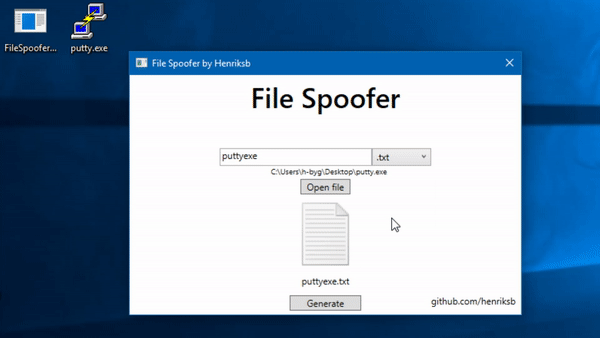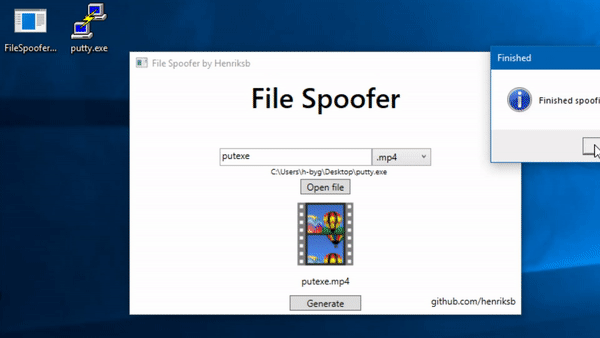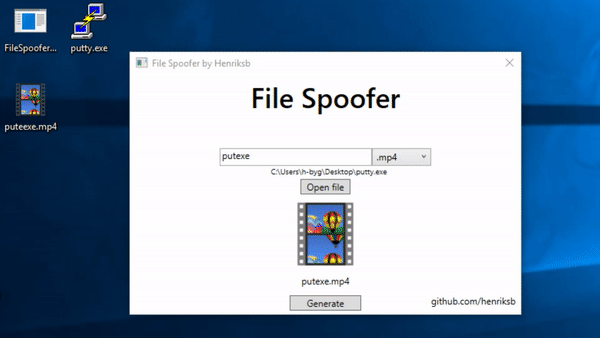
Spoof file icons and extensions in Windows

Documentation and proof of concept code for CVE-2022-24125 and CVE-2022-24126.